
 #2
Tools for observing malware behavior in isolated environments to understand its actions and impact.
Kitploit recommended

 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
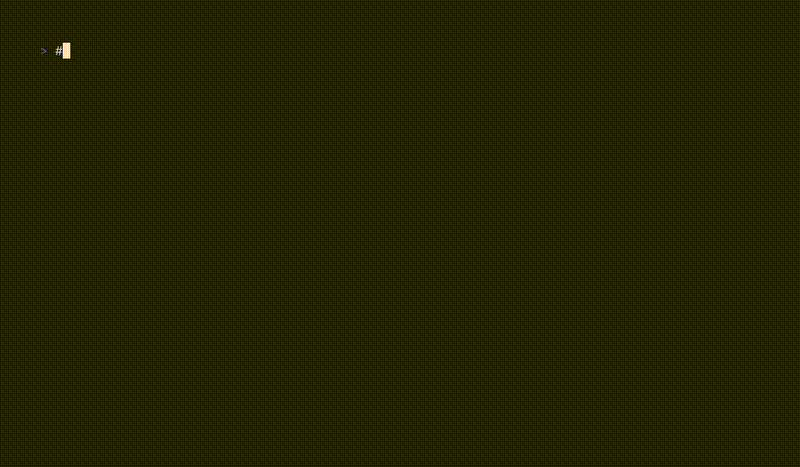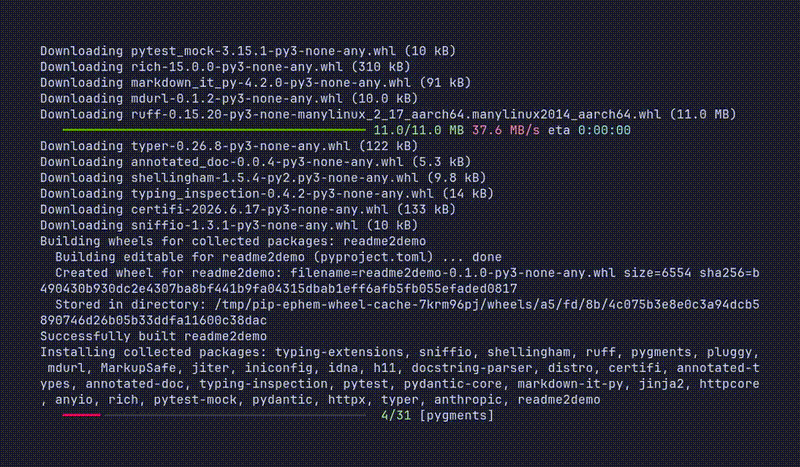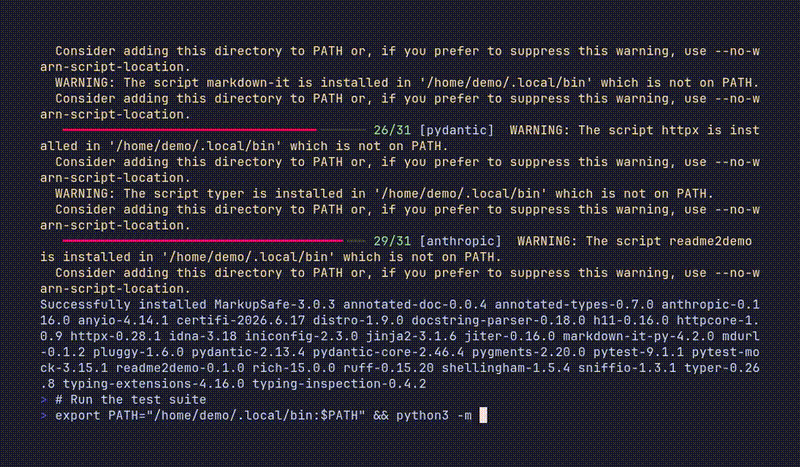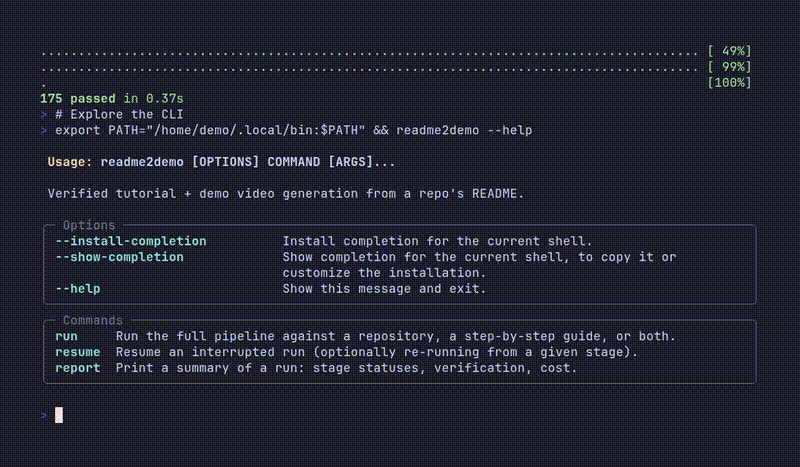 alphacrack/readme2demo
Verified tutorials and demo videos from your README. An AI agent runs it in a hardened Docker sandbox and replays it in a fresh container before…
 bcoles/rootkit-signal-hunter
Detect Linux rootkits which use signals to elevate process privileges.

 purpleteam-labs/purpleteam-s2-containers
Stage two containers
 abraxas/cve-2026-19445-sni-uaf
Proof-of-concept lab for CVE-2026-19445, a CPython ssl SNI SSLContext use-after-free where a remote TLS client frees the server's dispatch context…
 mandiant/flare-ida
IDA Pro utilities from FLARE team
 nccgroup/house
A runtime mobile application analysis toolkit with a Web GUI, powered by Frida, written in Python.
 fcavallarin/domdig
DOM XSS scanner for Single Page Applications
 alexmyg/andropytool
A framework for automated extraction of static and dynamic features from Android applications
 capsulerun/capsule
Secure runtime to sandbox AI agent tasks. Run untrusted code in isolated WebAssembly environments.
 mfthomps/resim
Reverse engineering software using a full system simulator
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 whoisqwerz/pocket_disasm
Multi-session IDALib MCP router for coding agents. Analyze multiple binaries in parallel with IDA-compatible reverse engineering tools.
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 renweimeng/vlun-agent-x
VulnAgent-X: A Layered Agentic Framework for Repository-Level Vulnerability Detection
 0xgalz/virtuailor
IDAPython tool for creating automatic C++ virtual tables in IDA Pro
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS








