
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Digital Forensics — Page 3 | Kitploit
Categories

Digital Forensics

Tools for acquiring, preserving, and analyzing digital evidence for legal or investigative purposes.

Kitploit recommended

Top tools

10 selected
autopsy preview#1

autopsy

GitHubsleuthkit/autopsy
3.3k5 months ago
sleuthkit preview#2

sleuthkit

GitHubsleuthkit/sleuthkit
3.2k20h 16m ago
volatility3 preview#3

volatility3

GitHubvolatilityfoundation/volatility3
4.3k16 days ago
plaso preview#4

plaso

GitHublog2timeline/plaso
2.2k1 day ago
bulk_extractor preview#5

bulk_extractor

GitHubsimsong/bulk_extractor
1.4k16 days ago
velociraptor preview#6

velociraptor

GitHubvelocidex/velociraptor
4.2k9h 2m ago
timesketch preview#7

timesketch

GitHubgoogle/timesketch
3.4k2 days ago
mvt preview#8

mvt

GitHubmvt-project/mvt
15.6k1 day ago
androidqf preview#9

androidqf

GitHubmvt-project/androidqf
2308 days ago
avml preview#10

avml

GitHubmicrosoft/avml
1.1k4 days ago
NewestRelevanceMost popularRecently updated
1342 results
CAPEv2 preview

CAPEv2

GitHubkevoreilly/capev2

Malware Configuration And Payload Extraction
dynamic-analysis-sandboxingmemory-forensicsvulnerability-analysis+6
3.4k0 days ago
pcileech preview

pcileech

GitHubufrisk/pcileech

Direct Memory Access (DMA) Attack Software

privilege-escalationmemory-forensicsexploitation+7
7.9k22 days ago
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

ioc-managementstatic-analysisdynamic-analysis-sandboxing+10
6.1k7 days ago
androguard preview

androguard

GitHubandroguard/androguard

Reverse engineering and pentesting for Android applications
android-securitystatic-analysisdynamic-analysis-sandboxing+6
6.2k3 days ago
grr preview

grr

GitHubgoogle/grr

Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…

disk-forensicsmemory-forensicsnetwork-forensics+4
5.1k26 days ago
digital-forensics-lab preview

digital-forensics-lab

GitHubfrankwxu/digital-forensics-lab

Free hands-on digital forensics labs for students and faculty

disk-forensicspassword-crackingmemory-forensics+9
2.9k15h 34m ago
Blackbone preview

Blackbone

GitHubdarthton/blackbone

Windows memory hacking library
privilege-escalationdynamic-analysis-sandboxingmemory-forensics+9
5.5k4 years ago
BlueTeam-Tools preview

BlueTeam-Tools

GitHuba-poc/blueteam-tools

Tools and Techniques for Blue Team / Incident Response
defensive-toolsvulnerability-scannersnetwork-mapping+8
4.4k2 months ago
unredacter preview

unredacter

GitHubbishopfox/unredacter

Never ever ever use pixelation as a redaction technique

vulnerability-analysisinformation-gatheringdigital-forensics+4
8.4k4 years ago
LaZagne preview

LaZagne

GitHubalessandroz/lazagne

Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…

password-crackingencryption-decryption-toolsmemory-forensics+8
11.0k1 year ago
DidierStevensSuite preview

DidierStevensSuite

GitHubdidierstevens/didierstevenssuite

Collection of Python scripts for malware analysis, file format parsing, hashing, and forensic triage, including PDF, OLE, and XOR analysis utilities.

static-analysishash-analysisreverse-engineering+6
2.6k14 days ago
gef preview

gef

GitHubhugsy/gef

GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
static-analysisdynamic-analysis-sandboxingmemory-forensics+10
8.3k2 months ago
pyWhat preview

pyWhat

GitHubbee-san/pywhat

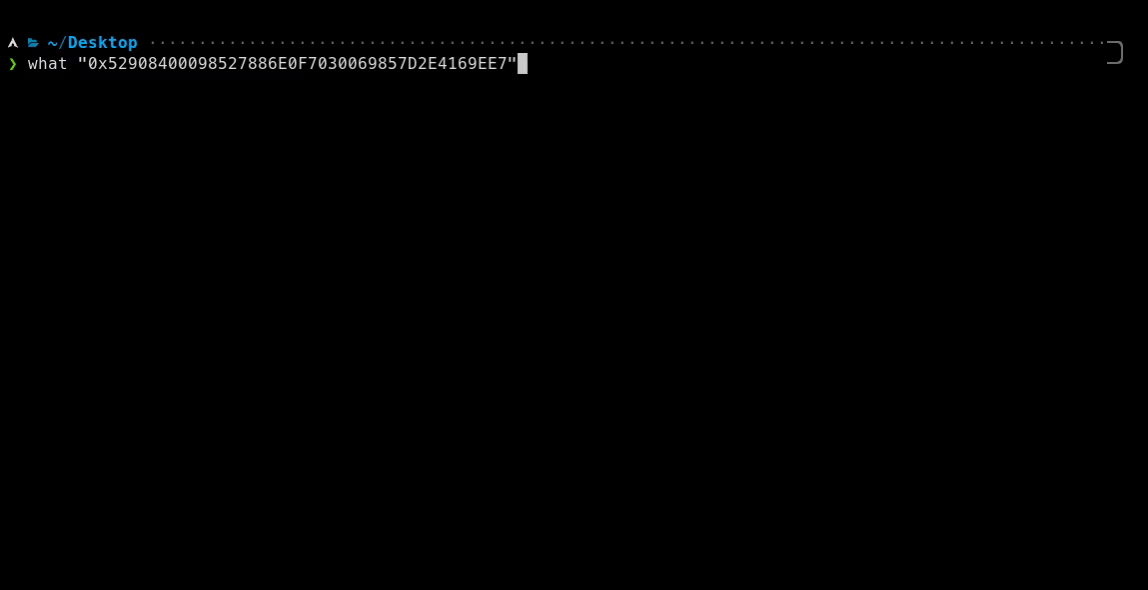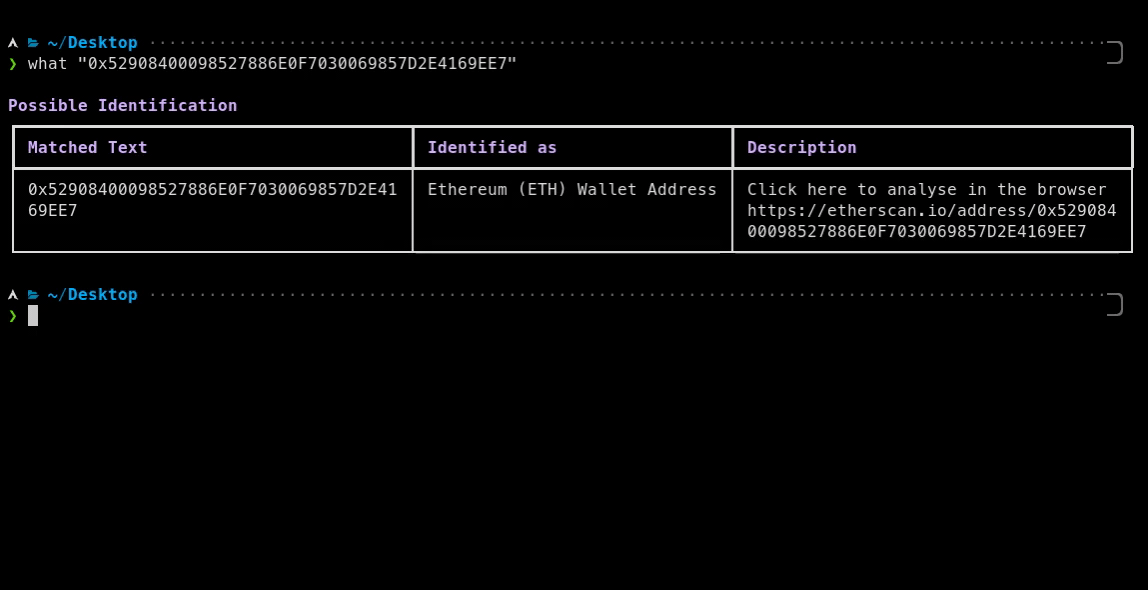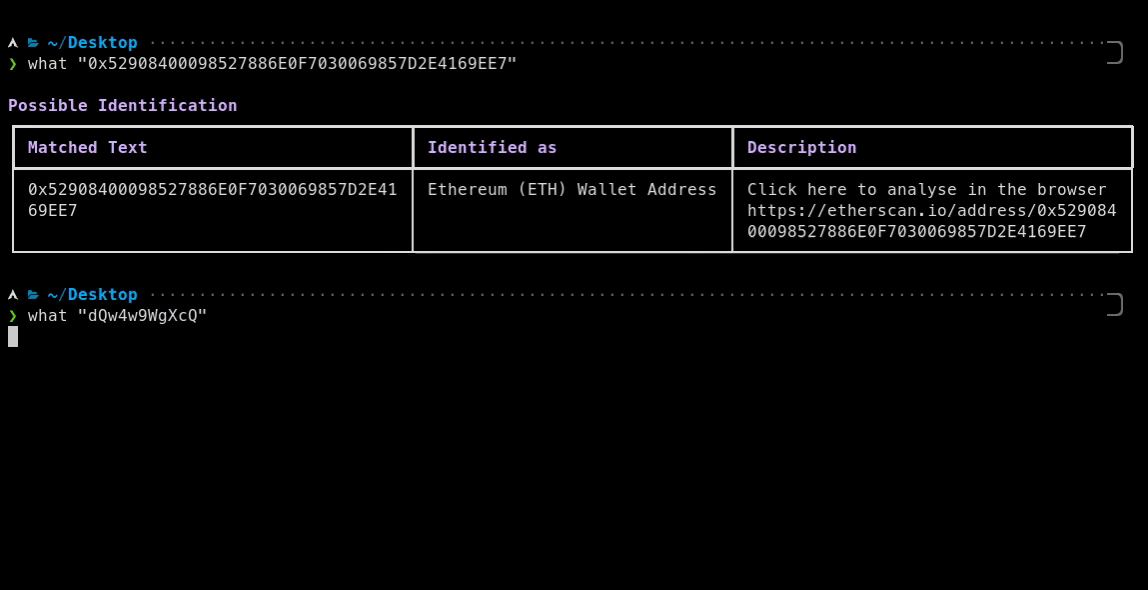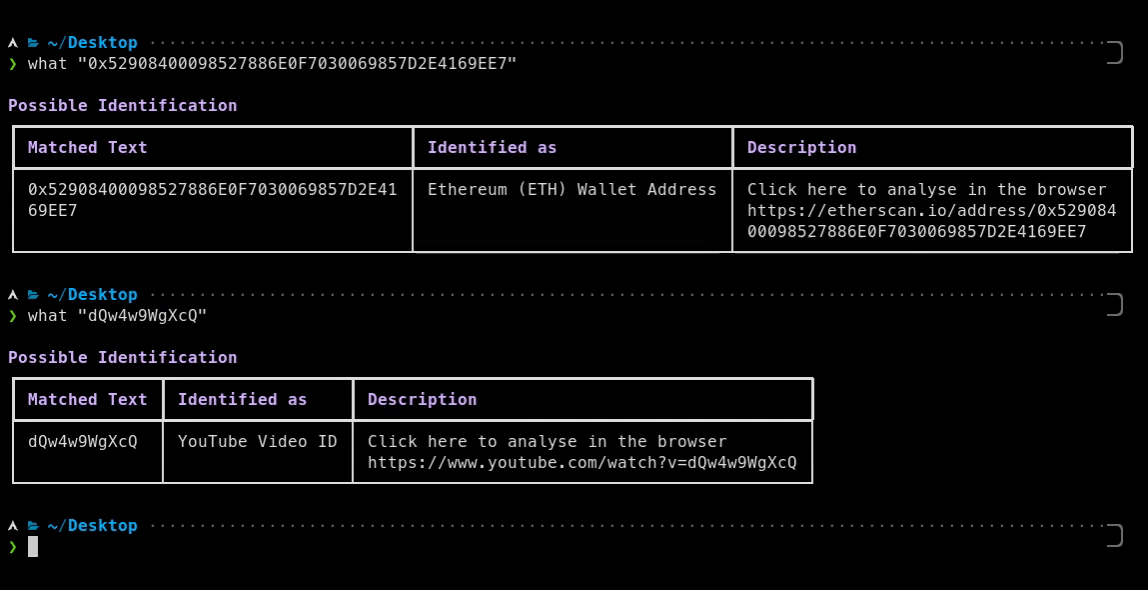
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…

osintreconnaissancevulnerability-analysis+7
7.3k26 days ago
volatility3 preview

volatility3

GitHubvolatilityfoundation/volatility3

Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
memory-forensicsforensicsmalware-analysis+2
4.3k16 days ago
DetectionLab preview

DetectionLab

GitHubclong/detectionlab

Automate the creation of a lab environment complete with security tooling and logging best practices


defensive-toolsconfiguration-auditingsecurity-virtualization+5
5.0k3 years ago
velociraptor preview

velociraptor

GitHubvelocidex/velociraptor

Digging Deeper....

defensive-toolsdisk-forensicsmemory-forensics+8
4.2k9h 2m ago
rizin preview

rizin

GitHubrizinorg/rizin

UNIX-like reverse engineering framework and command-line toolset.

embedded-systems-securitystatic-analysisexploitation+7
4.1k1 day ago
flare-floss preview

flare-floss

GitHubmandiant/flare-floss

FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.

disk-forensicsstatic-analysisdynamic-analysis-sandboxing+8
4.1k6 days ago
Previous1234…75Next






