
 #1
Tools for acquiring, preserving, and analyzing digital evidence for legal or investigative purposes.
Kitploit recommended

 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

 wiltodelta/remove-ai-watermarks
Remove visible and invisible AI watermarks from images and video, and AI provenance metadata from images, video, and audio. Python library, CLI, and…
 rawfilejson/awesome-osint-arsenal
OSINT & recon toolkit // 100+ tools, one-command installer, SOCMINT, GEOINT, network recon, dark web, forensics & more.
 the-tcpdump-group/tcpdump
the TCPdump network dissector
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 olafhartong/sysmon-modular
A repository of sysmon configuration modules
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 neo23x0/signature-base
YARA signature and IOC database for my scanners and tools
 hephaest0s/usbkill
« usbkill » is an anti-forensic kill-switch that waits for a change on your USB ports and then immediately shuts down your computer.
 ssrajadh/sentrysearch
Semantic search over videos using Gemini Embedding 2 or Qwen3-VL.
 zer0yu/awesome-cobaltstrike
List of Awesome CobaltStrike Resources
 blacktop/ipsw
iOS/macOS Research Swiss Army Knife
 stephenfewer/reflectivedllinjection
Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…
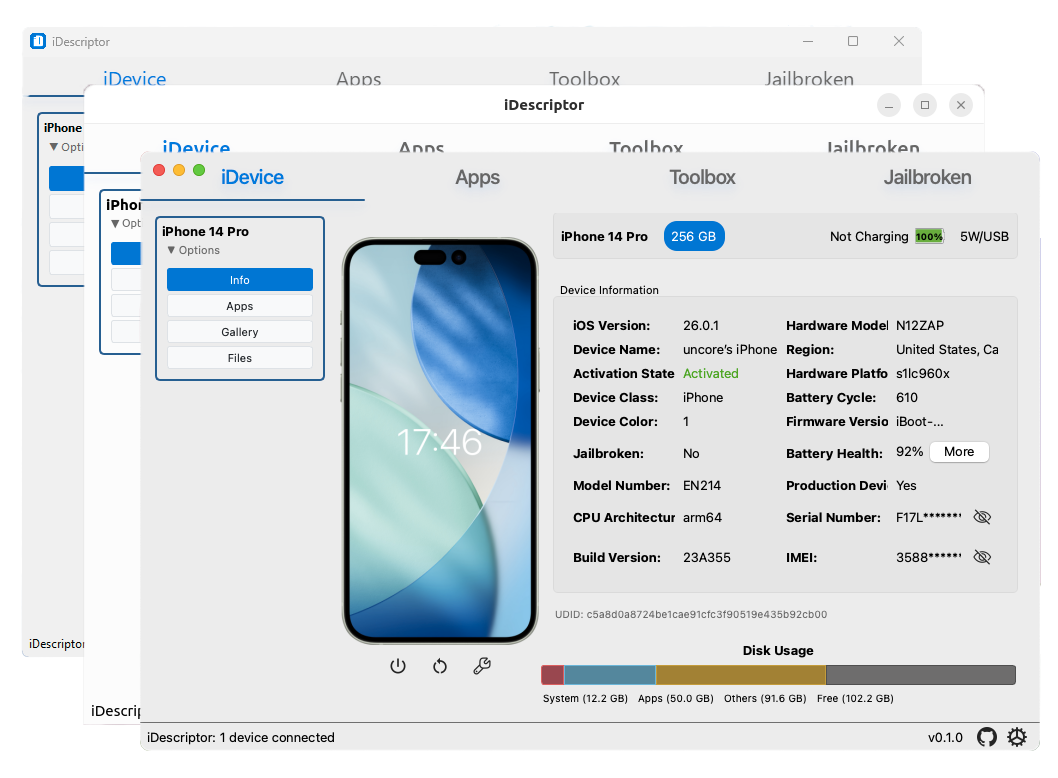 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt






