
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
hammer — Dow Jones Hammer : Protect the cloud with the power of the cloud(AWS) | Kitploit

Tools/GitHubGitHub/dowjones/hammer
Cloud Infrastructure SecurityVulnerability ScannersConfiguration AuditingCloud SecurityDevSecOpsMisconfiguration
GitHubdowjones/hammer

hammer

Dow Jones Hammer : Protect the cloud with the power of the cloud(AWS)

View Repository
45059417 years agoReviewed by Kitploit
Share

HammerLogo

Overview

Dow Jones Hammer is a multi-account cloud security tool for AWS. It identifies misconfigurations and insecure data exposures within most popular AWS resources, across all regions and accounts. It has near real-time reporting capabilities (e.g. JIRA, Slack) to provide quick feedback to engineers and can perform auto-remediation of some misconfigurations. This helps to protect products deployed on cloud by creating secure guardrails.
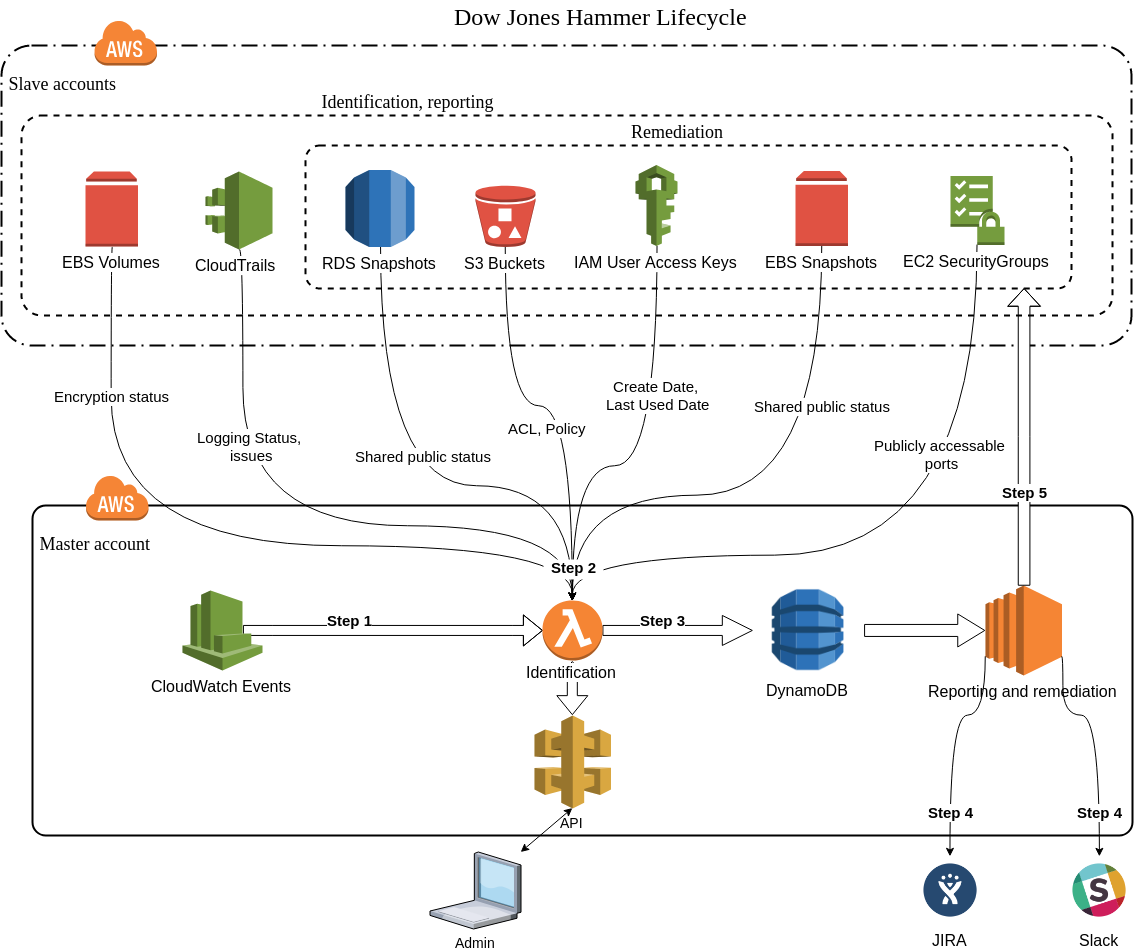
HammerLifecycleDiagram

Documentation

Dow Jones Hammer documentation is available via GitHub Pages at https://dowjones.github.io/hammer/.

Security features

  • Insecure Services
  • S3 ACL Public Access
  • S3 Policy Public Access
  • IAM User Inactive Keys
  • IAM User Keys Rotation
  • CloudTrail Logging Issues
  • EBS Unencrypted Volumes
  • EBS Public Snapshots
  • RDS Public Snapshots
  • SQS Public Policy Access
  • S3 Unencrypted Buckets
  • RDS Unencrypted Instances
  • AMIs Public Access

Technologies

  • Python 3.6
  • AWS (Lambda, Dynamodb, EC2, SNS, CloudWatch, CloudFormation)
  • Terraform
  • JIRA
  • Slack

Contributing

You are welcome to contribute!

Issues:

You can use GitHub Issues to report issues. Describe what is going on wrong and what you expect to be correct behaviour.

Patches:

We currently use dev branch for ongoing development. Please open PRs to this branch.

Run tests:

Run tests with this command:

tox

Contact Us

Feel free to create issue report, pull request or just email us at [email protected] with any other questions or concerns you have.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →





