
 #1
Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.
Kitploit recommended

 shoucheng3/wildfly__wildfly_cve-2018-1047_11-0-0-final
Java EE 7 application server with modular design, unified configuration, and management. Supports standalone and domain modes with built-in testing…
 shoucheng3/jenkinsci__perfecto-plugin_cve-2020-2261_1-17
Jenkins plugin for automated mobile app testing via Perfecto cloud, managing secure tunnel connections and app uploads within CI/CD pipelines.
 shoucheng3/eclipse__hawkbit_cve-2020-27219_0-3-0m6
Domain-independent back end for rolling out software updates to constrained edge devices, controllers, and gateways over IP-based infrastructure,…
 shoucheng3/whitesource__curekit_cve-2022-23082_1-1-3
Java security library providing contextual encoders and sanitizers to automatically remediate vulnerabilities like XSS, path traversal, and command…
 shoucheng3/payara__payara_cve-2022-37422_5-2022-2
Jakarta EE and MicroProfile application server runtime for development and containerized deployments, supporting cloud-native middleware with…
 shoucheng3/jenkinsci__git-client-plugin_cve-2019-10392_2-8-4
Jenkins plugin providing Git APIs for automated repository operations including fetch, checkout, merge, and tag, with support for credential-based…
 chen-keinan/kube-beacon
Open Source runtime scanner for k8s cluster and perform security audit checks based on CIS Kubernetes Benchmark specification
 luftwaffe66/gobfuscator
Obfuscates Go source code via AES-256 string encryption with runtime decryption, identifier renaming, and comment removal to hinder reverse…
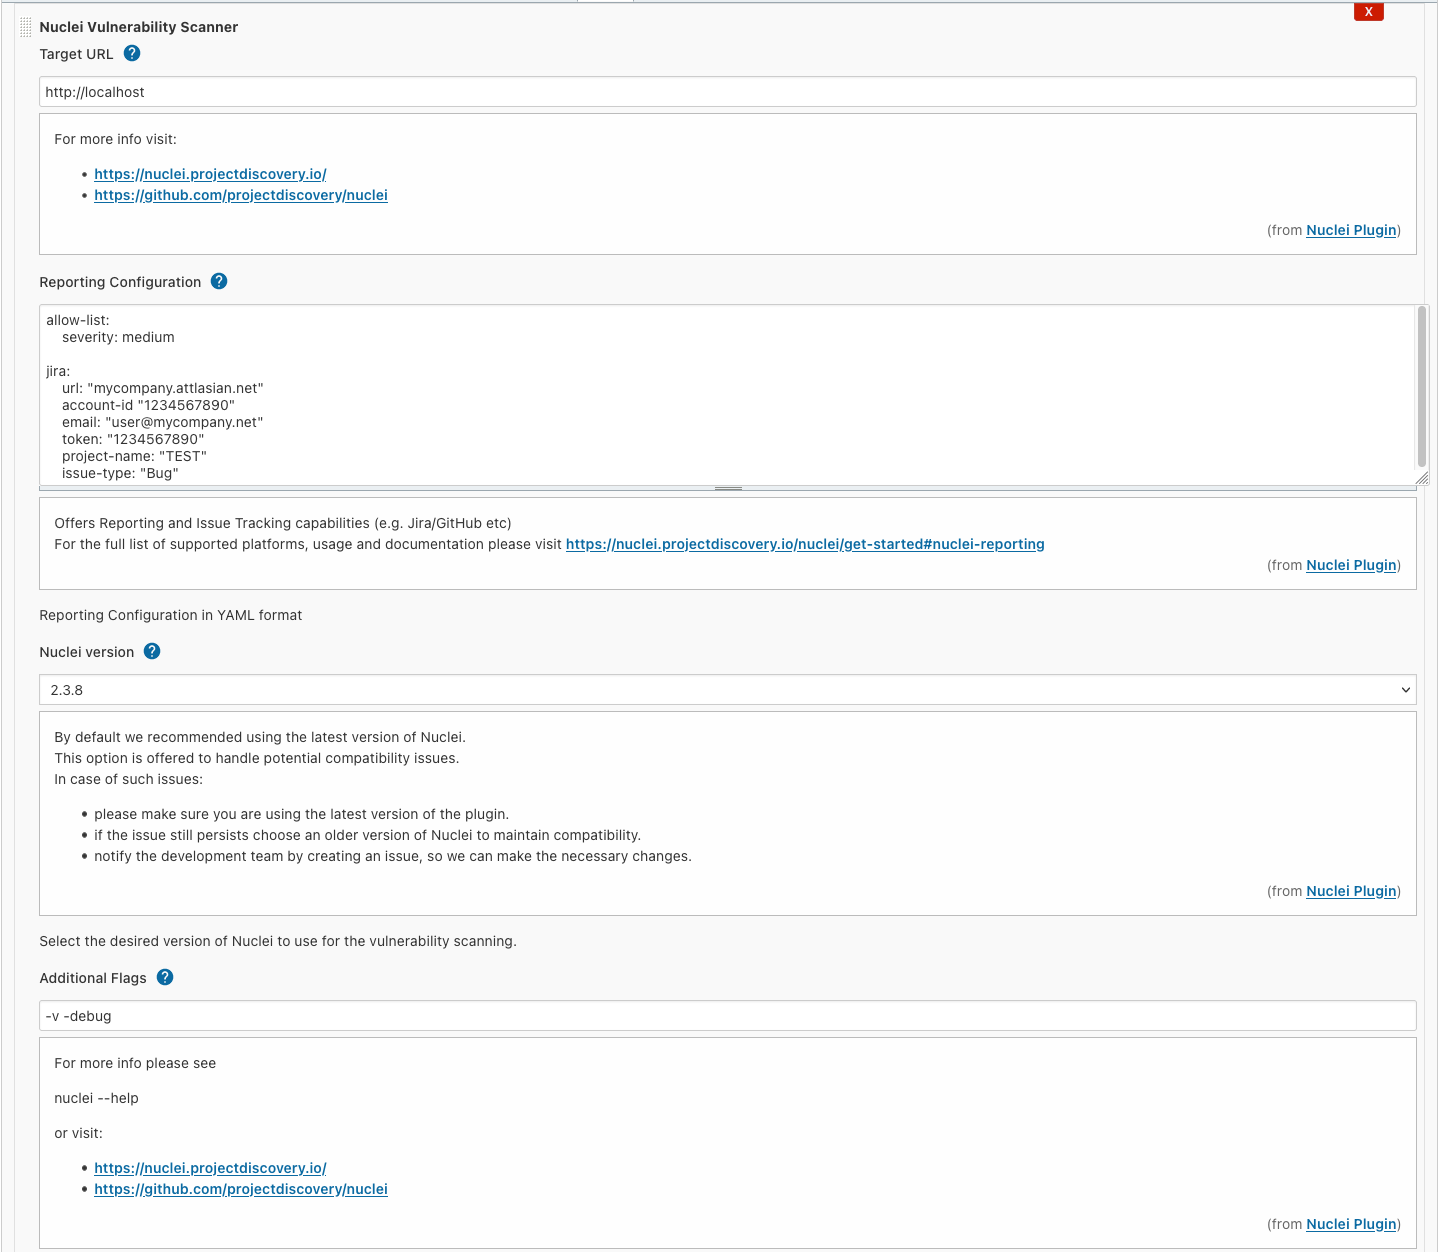 jenkinsci/nuclei-plugin
Nuclei is a fast tool for configurable targeted vulnerability scanning based on templates offering massive extensibility and ease of use.
 projectdiscovery/nuclei-templates-labs
Vulnerable environments paired with ready-to-use Nuclei templates for security testing and learning! 🚀
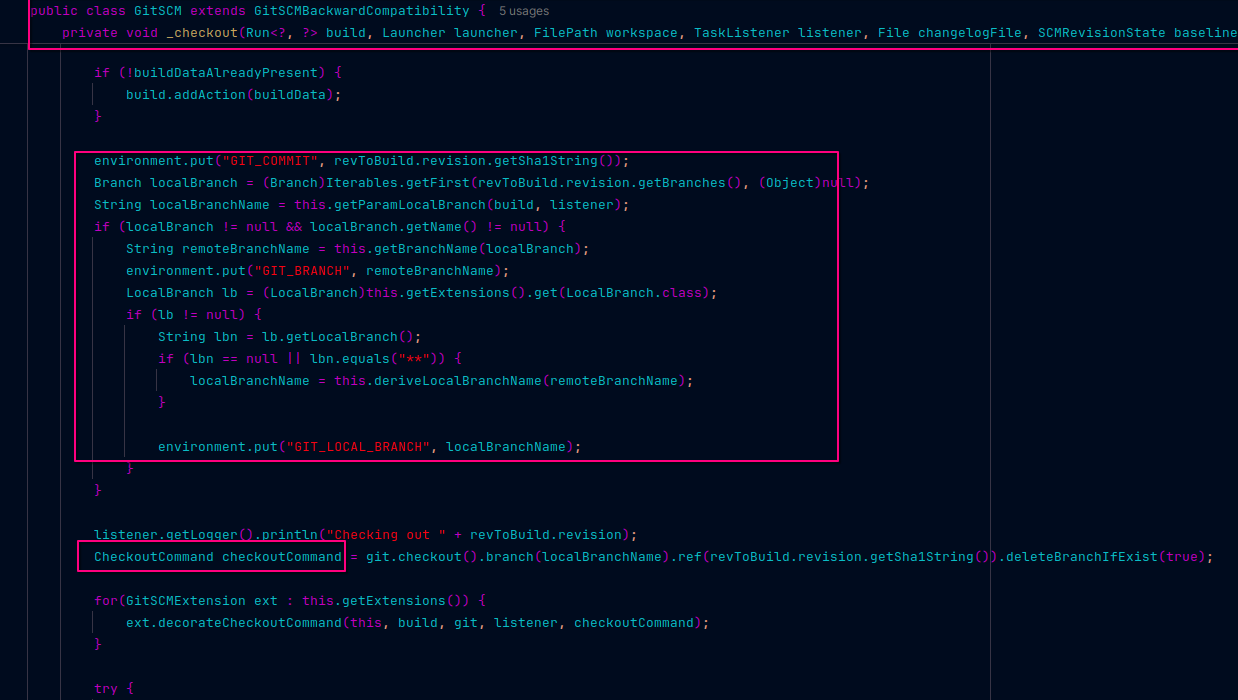 pl4tyz/cve-2025-53652-jenkins-git-parameter-analysis
CVE-2025-53652: Jenkins Git Parameter Analysis
 joshlarsen/aws-recon
Multi-threaded AWS inventory collection tool with a focus on security-relevant resources and metadata.
 securityuniversalorg/secusphere
Centralized DevSecOps platform for vulnerability management, CI/CD security integration, automated security assessment aggregation, and fostering…
 mindpatch/vulfy
🐺 Vulfy – Fast Rust based package version scanner
 gmh5225/llm-guard-service
A service to provide protection against prompt injection, jailbreak attacks, and harmful content when interacting with AI services..

 atlassian/git-secrets-scan
Scans Git repositories for hardcoded secrets, keys, and passwords using Gitleaks, integrating security into Bitbucket Pipelines with Code Insights…
 brunoh6/web-threat-mitigation
Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…
 kvesta/vesta
A static analysis of vulnerabilities, Docker and Kubernetes cluster configuration detect toolkit based on the real penetration of cloud computing








