
 #1
Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.
Kitploit recommended

 kriskimmerle/wheelaudit
Python Wheel File Security Scanner — scan .whl files for security issues before installation. Detects path traversal (CVE-2026-24049), RECORD…
 barrersoftware/opencode-secure
Security-hardened fork of OpenCode - Fixes CVE-2026-22812 (CVSS 8.8 RCE) that upstream refuses to patch
 deepfence/threatmapper
Open Source Cloud Native Application Protection Platform (CNAPP)
 thoughtworks/talisman
Git hook-based secret scanner that detects tokens, passwords, and private keys in outgoing changesets, preventing sensitive data from being committed…
 rustsec/rustsec
RustSec API & Tooling
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…
 novoda/gradle-static-analysis-plugin
Easy setup of static analysis tools for Android and Java projects.
 rcarmo/agentbox
Docker-based sandbox for coding agents with isolated environments, preinstalled agent tooling, service control, and workspace bootstrap for secure…
 eth0izzle/security-skills
A collection of Claude Code skills that help security teams stay secure
 morpheuslord/cloudg
Map, graph and audit AWS, Azure and GCP from one CLI. Builds a topology graph, runs Prowler/Checkov/Trivy, tags findings against 28 compliance…
 xiaoqimikko/tomcat85-check
CVE-2025-55752:Tomcat 8.5 已 EOL,终版 8.5.100。Apache 逐条声明「8.5 也受影响」的 2025 CVE 有 14 条,其中 10 条在 NVD 按 8.5.100 查不到。离线单 jar,读 conf/ 判断你到底中了哪几条。
 tencent/codeanalysis
Enterprise-grade static code analysis platform with multi-language support, security vulnerability detection, code quality metrics, and DevOps…
 lirantal/npq
safely install npm packages by auditing them pre-install stage
 dev-sec/linux-baseline
InSpec-based compliance profile for auditing Linux system hardening against security baselines, ensuring consistent configuration across…
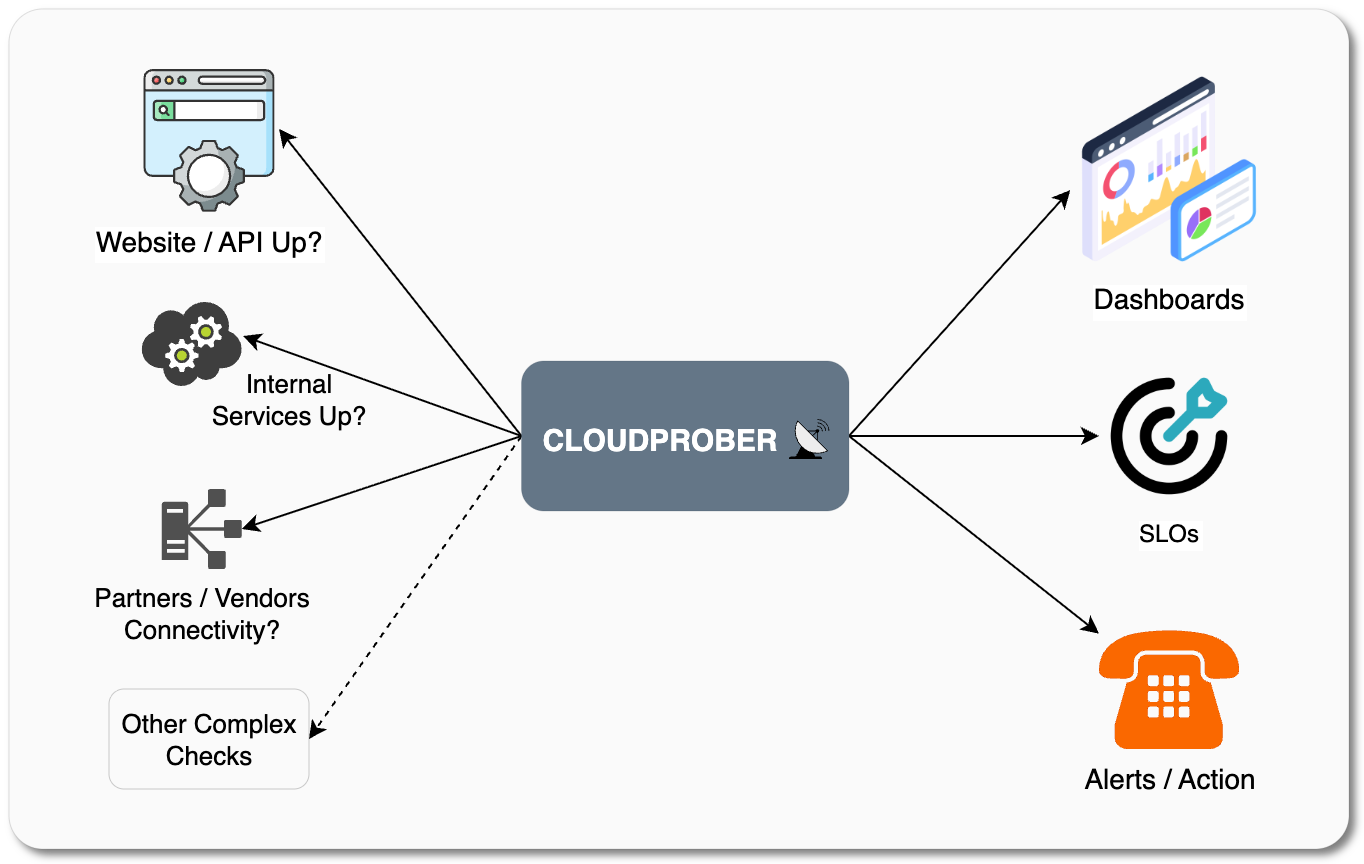 cloudprober/cloudprober
An active monitoring software to detect failures before your customers do.
 0x4d31/burpa
Burp-Automator: A Burp Suite Automation Tool with Slack Integration. It can be used with Jenkins and Selenium to automate Dynamic Application…
 momenbasel/vulnhawk
AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.
 shubhamshubhankar/autosource
Automated static code analysis framework integrated with SonarQube for early vulnerability detection in source code by scanning Git repositories…








