
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Categories

Debuggers

Debugging tools specifically for analyzing malware execution flow and identifying vulnerabilities.

Kitploit recommended
Top tools

10 selected
x64dbg preview#1

x64dbg

GitHubx64dbg/x64dbg
49.1k6 days ago
pwndbg preview#2

pwndbg

GitHubpwndbg/pwndbg
10.8k1 day ago
gef preview#3

gef

GitHubhugsy/gef
8.3k2 months ago
delve preview#4

delve

GitHubgo-delve/delve
25.0k12h 47m ago
rr preview#5

rr

GitHubrr-debugger/rr
10.7k7 days ago
cutter preview#6

cutter

GitHubrizinorg/cutter
19.4k13h 47m ago
radare2 preview#7

radare2

GitHubradareorg/radare2
24.5k9h 3m ago
ghidra preview#8

ghidra

GitHubnationalsecurityagency/ghidra
71.1k9h 55m ago
dnSpy preview#9

dnSpy

GitHubdnspyex/dnspy
10.9k2 days ago
dynamorio preview#10

dynamorio

GitHubdynamorio/dynamorio
3.2k11h 25m ago
NewestRelevanceMost popularRecently updated
564 results
binja_dynamics preview

binja_dynamics

GitHubnccgroup/binja_dynamics

A PyQt5 frontend to the binjatron plugin for Binary Ninja that includes highlighting features aimed at making it easier for beginners to learn about…
dynamic-analysis-sandboxingreverse-engineeringdebuggers+2
259 years ago
stackflow preview

stackflow

GitHubd4rkcat/stackflow

Universal stack-based buffer overfow exploitation tool
payload-generationvulnerability-analysisexploitation+5
2312 years ago
Ghidra-Rare preview

Ghidra-Rare

GitHubaleph-void/ghidra-rare

A repository of SLEIGH support for rare processor ISAs
embedded-systems-securitystatic-analysisreverse-engineering+4
191 day ago
archivo-syxe05-snat preview

archivo-syxe05-snat

GitHubshow0ne/archivo-syxe05-snat

Historical archive of reverse engineering and unpacking tutorials covering commercial protectors (Armadillo, ASProtect, Themida) with classic tools…
reverse-engineeringdebuggersmalware-analysis+3
297 months ago
dapr preview

dapr

GitHubnccgroup/dapr

Driver Attack Platform for Linux
android-securityembedded-systems-securityexploit-frameworks+5
187 years ago
AIDebug preview

AIDebug

GitHubanpa1200/aidebug

Evidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging
static-analysisdynamic-analysis-sandboxingreverse-engineering+7
1526 days ago
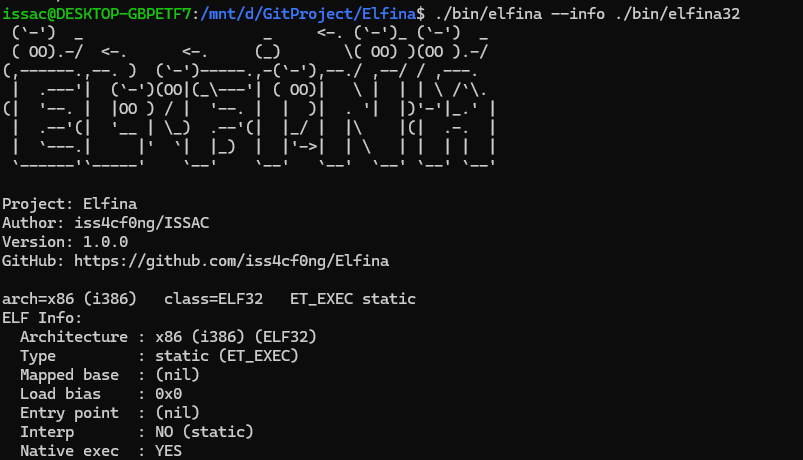
Elfina preview

Elfina

GitHubiss4cf0ng/elfina

Multi-architecture ELF loader and analysis toolkit with probing, disassembly, hexdump, entropy calculation, and mmap/memfd execution for x86 and…
reverse-engineeringdebuggersmalware-analysis+3
527 months ago
WHFB-PinCapture preview

WHFB-PinCapture

GitHubivancabrera02/whfb-pincapture

Captures Windows Hello PINs at entry by injecting a DLL into LogonUI.exe that sets a CPU hardware breakpoint on NgcSerializeConvenienceCredential,…

privilege-escalationmemory-forensicspassword-attacks+5
1018 days ago
apiscope preview

apiscope

GitHubkaisonox/apiscope

An API hooking framework for intercepting and monitoring Windows applications

dynamic-analysis-sandboxingdynamic-code-analysisreverse-engineering+4
204 months ago
sylvia preview

sylvia

GitHubstolevchristian/sylvia

iOS Syscall Explorer for IDA 9.X

static-analysisios-securityvulnerability-analysis+5
155 months ago
KEPaboo preview

KEPaboo

GitHub0vercl0k/kepaboo

Neutralize KEPServerEX anti-debugging techniques

dynamic-analysis-sandboxingreverse-engineeringscada-ics-security+5
333 years ago
ltm preview

ltm

GitHubagent-hellboy/ltm

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…

disk-forensicsosintdynamic-analysis-sandboxing+7
233 months ago
PrologWinDbg preview

PrologWinDbg

GitHubdumpanalysis/prologwindbg

Use Prolog to analyze memory dumps and stopped live processes in WinDbg.
memory-forensicsreverse-engineeringscripting-automation+4
1514 days ago
elfpeek preview

elfpeek

GitHuboblivionsage/elfpeek

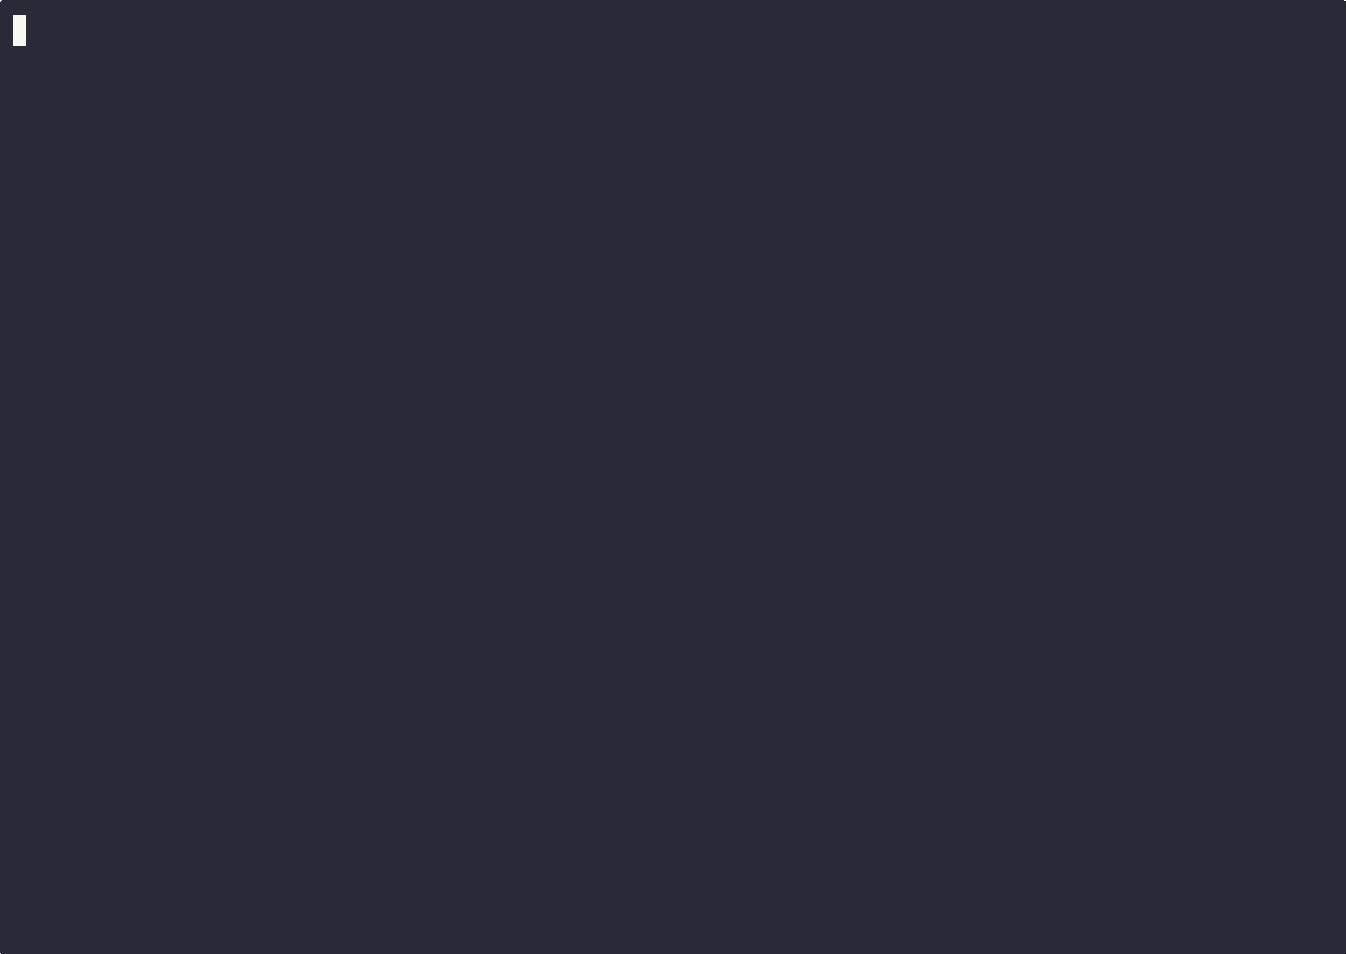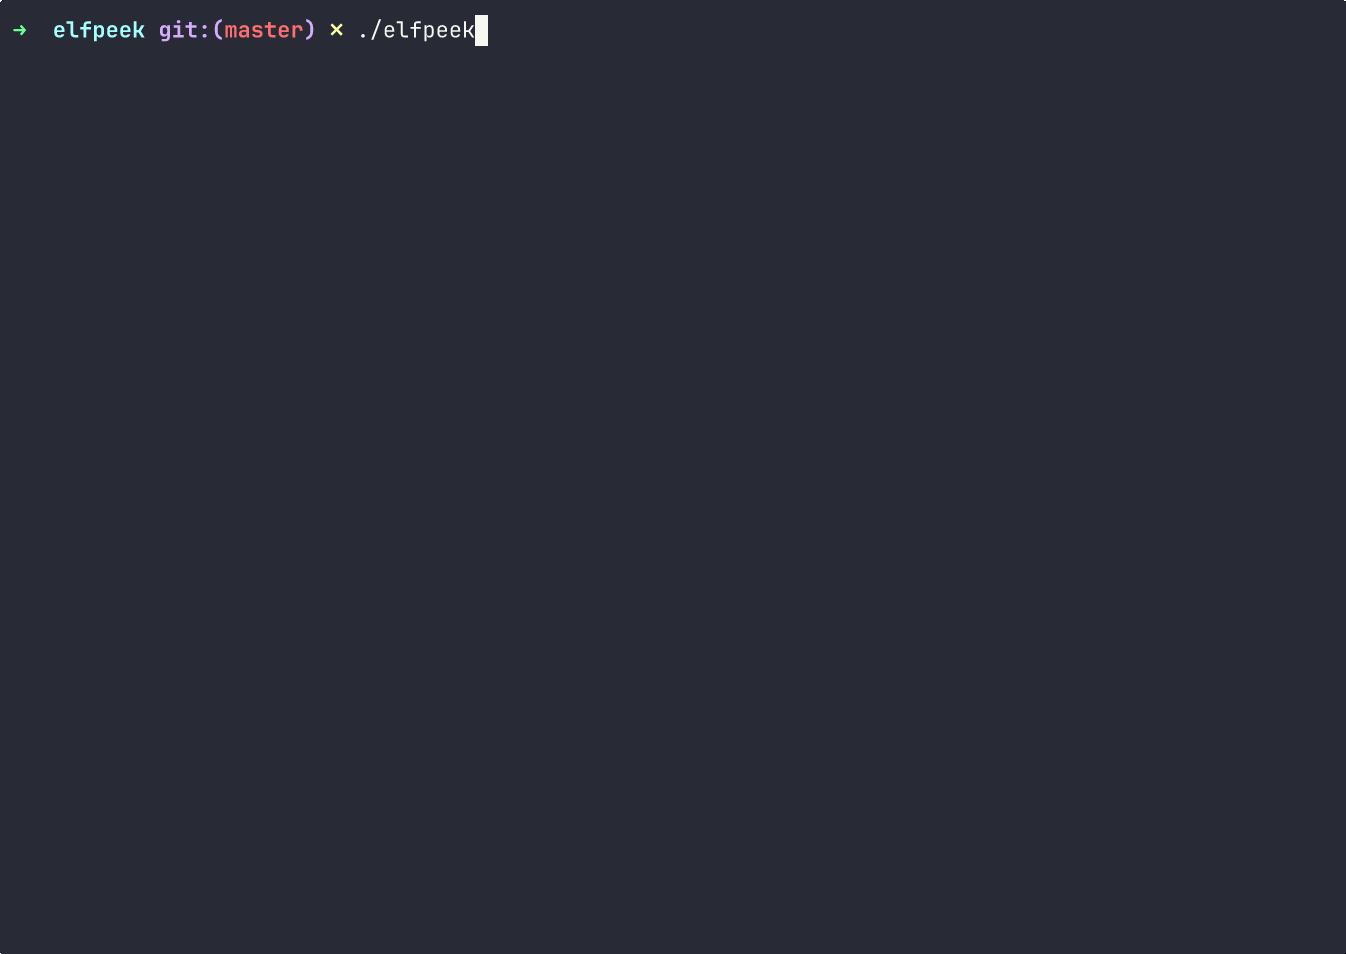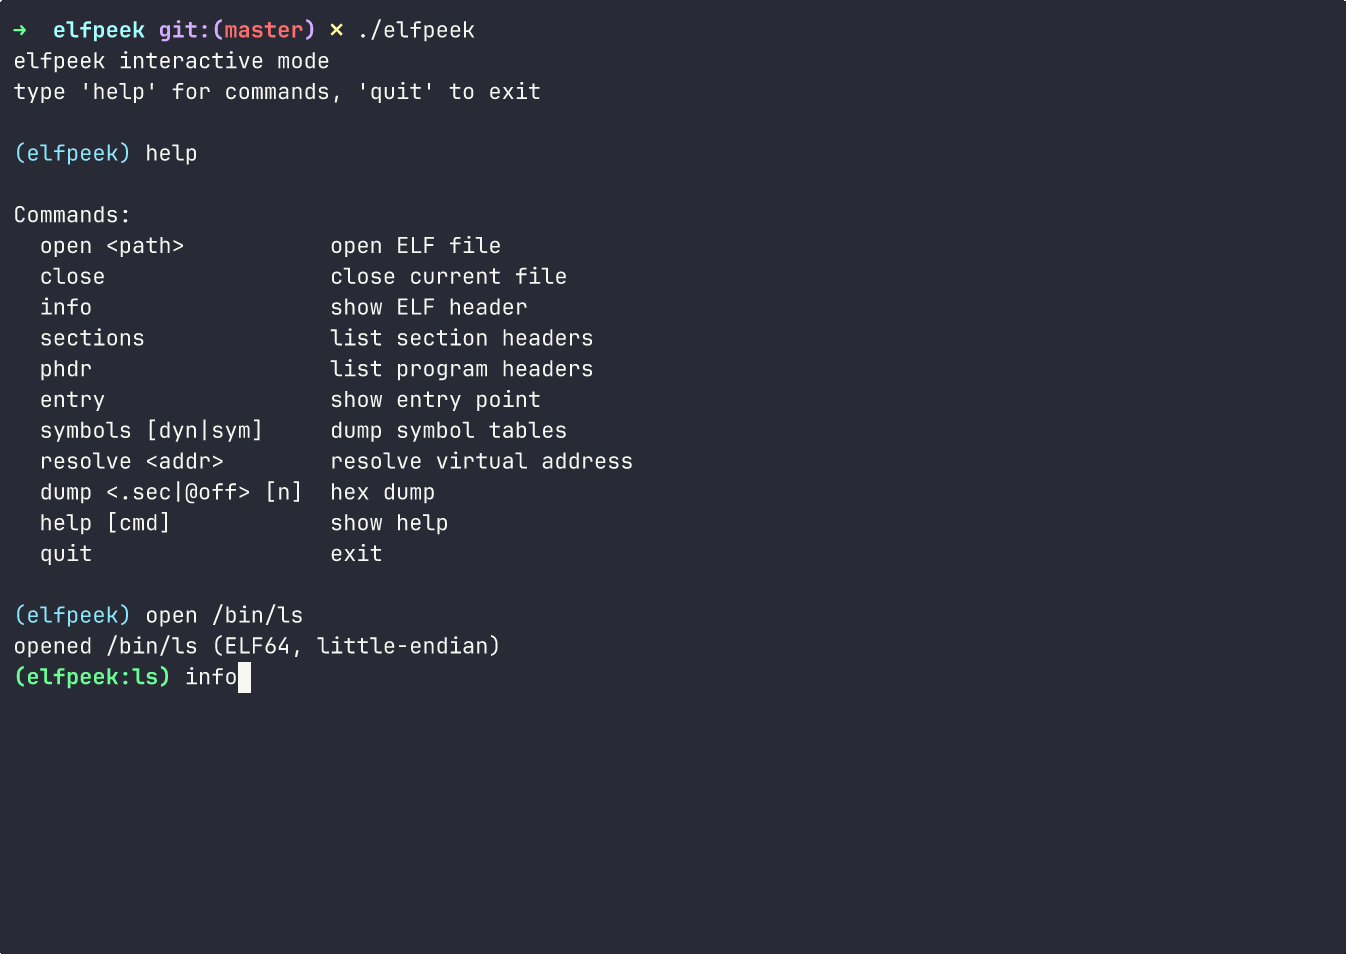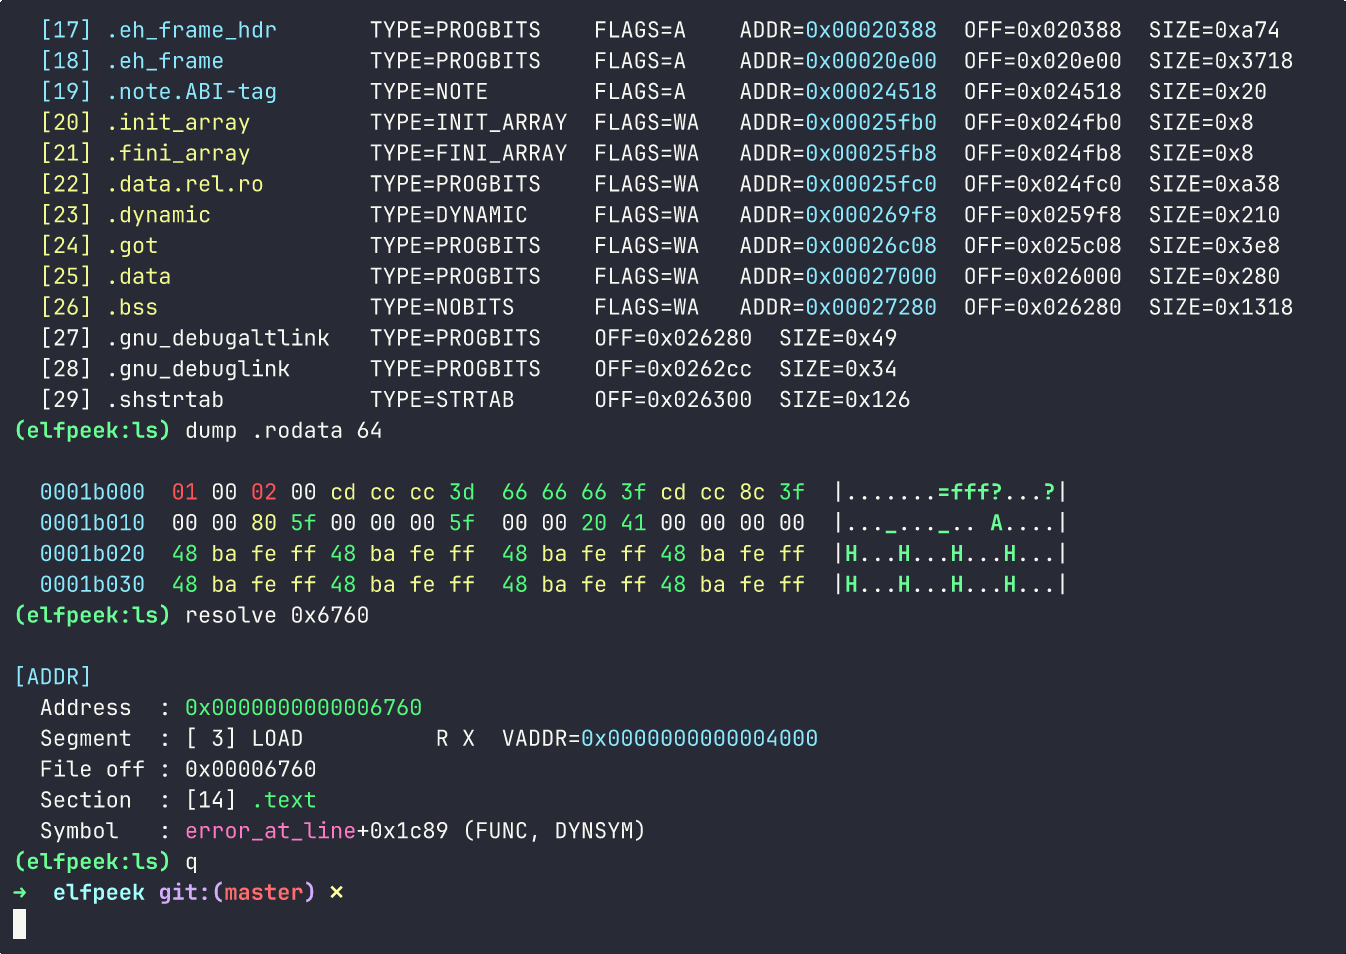
Minimal ELF inspector written in C for quick binary layout inspection
static-analysisreverse-engineeringdebuggers+2
299 months ago
ollydbg-binary-execution-visualizer preview

ollydbg-binary-execution-visualizer

GitHubehabhussein/ollydbg-binary-execution-visualizer

reverse engineering, visual binary analysis

static-analysisdynamic-analysis-sandboxingreverse-engineering+3
249 years ago
pycdc preview

pycdc

GitHubejfkdev/pycdc

Decompile and disassemble Python bytecode (.pyc/.pyo) back to readable source. Supports Python 2.0 - 3.15 (CPython, PyPy and other implementations).…
static-analysiscode-analysisreverse-engineering+4
103 days ago
CVE-2023-6241-Pixel7_Adaptation preview

CVE-2023-6241-Pixel7_Adaptation

GitHubilgobbo00/cve-2023-6241-pixel7_adaptation

Adaptation of CVE-2023-6241 for Google Pixel 7 from Google Pixel 8 taken from securitylab/SecurityExploits/Android/Mali/CVE_2023_6241

android-securityvulnerability-analysisexploitation+5
141 year ago
xtride preview

xtride

GitHubpr0me/xtride

N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…


static-analysisreverse-engineeringdebuggers+5
264 months ago
Previous1…202122…32Next







