
 #1
Debugging tools specifically for analyzing malware execution flow and identifying vulnerabilities.
Kitploit recommended
 synacktiv/thats_no_pipe
Windows named pipe hooking toolkit
 saint0x/fzy
a systems programming language prioritizing verifiable correctness, determinism, and performance
 encrypter15/cve-2025-29824
Proof-of-concept exploit for CVE-2025-29824, a use-after-free vulnerability in the Windows CLFS kernel driver, demonstrating privilege escalation to…
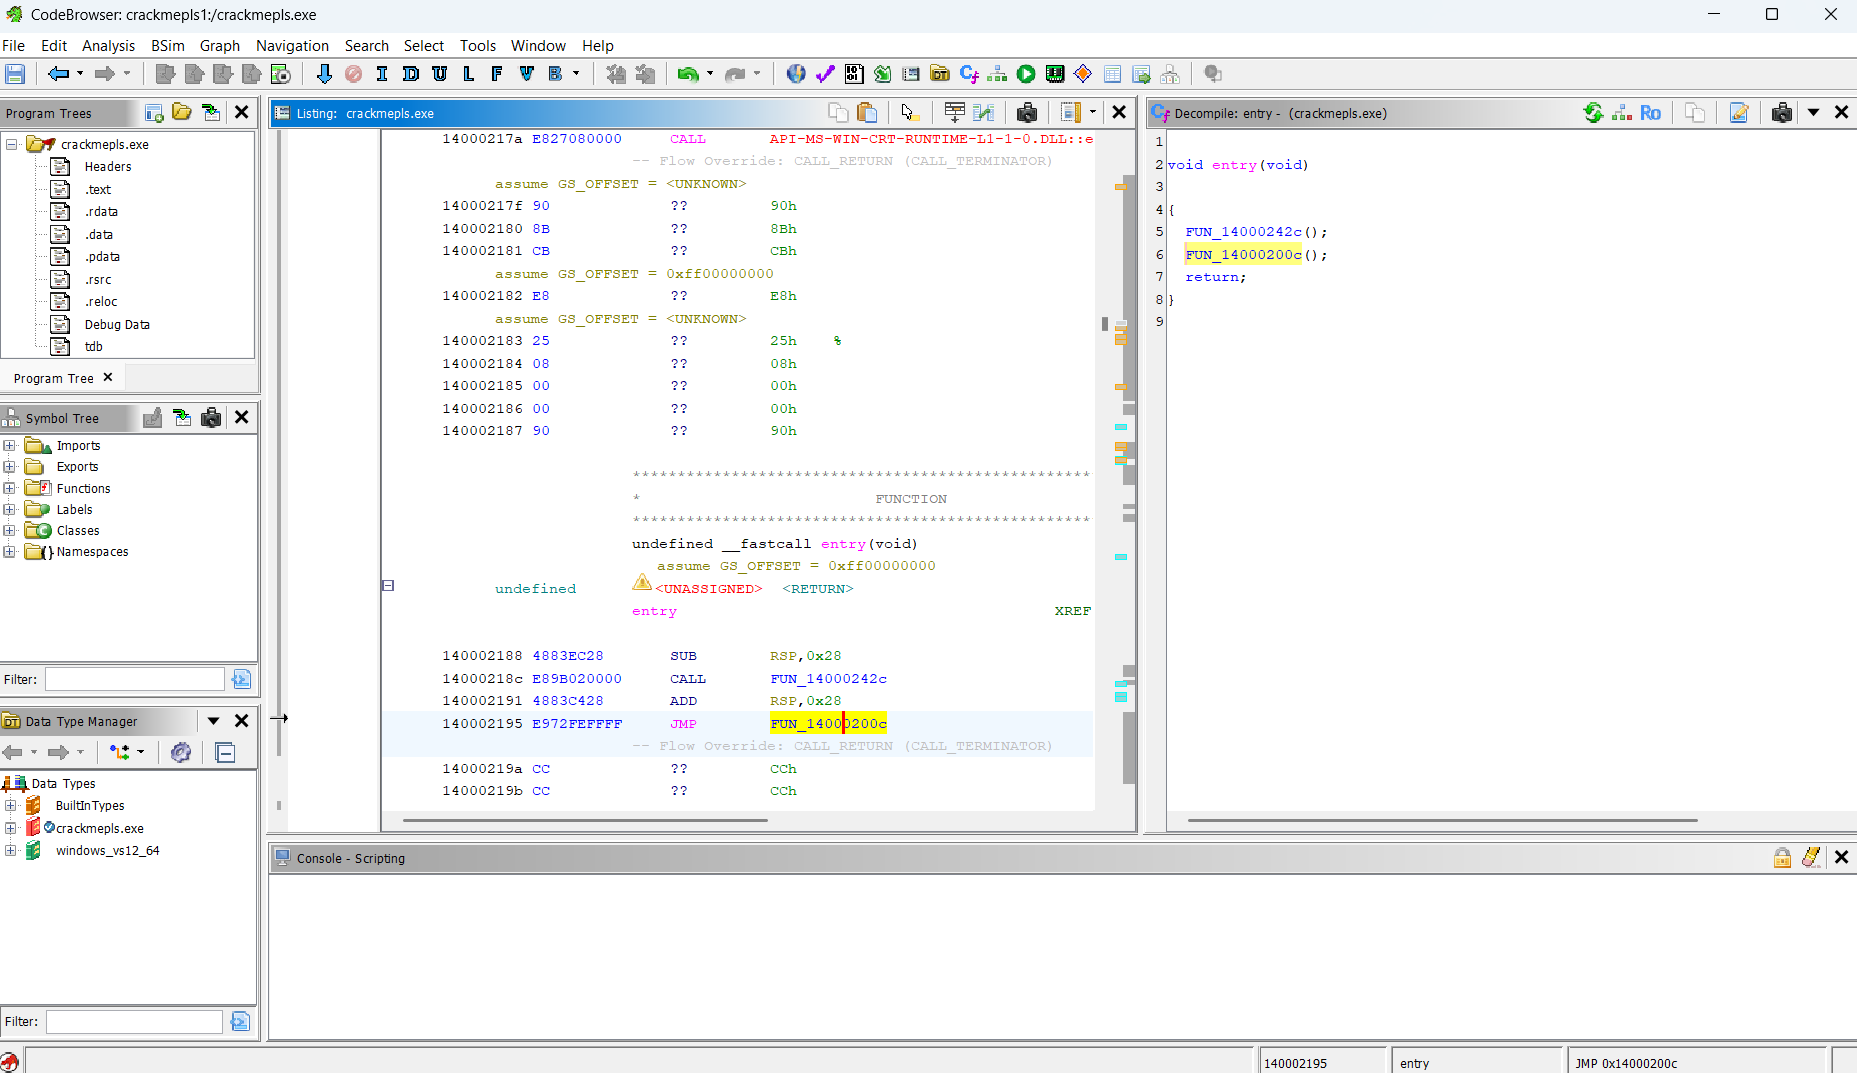 markoglasgow/gemma_crackme_tutorial
Step-by-step tutorial on using Google's Gemma 4 E4B local AI model to reverse engineer a Windows crackme with Ghidra, including setup for local…
 nccgroup/libdlmalloc
Heap analysis tooling for dlmalloc
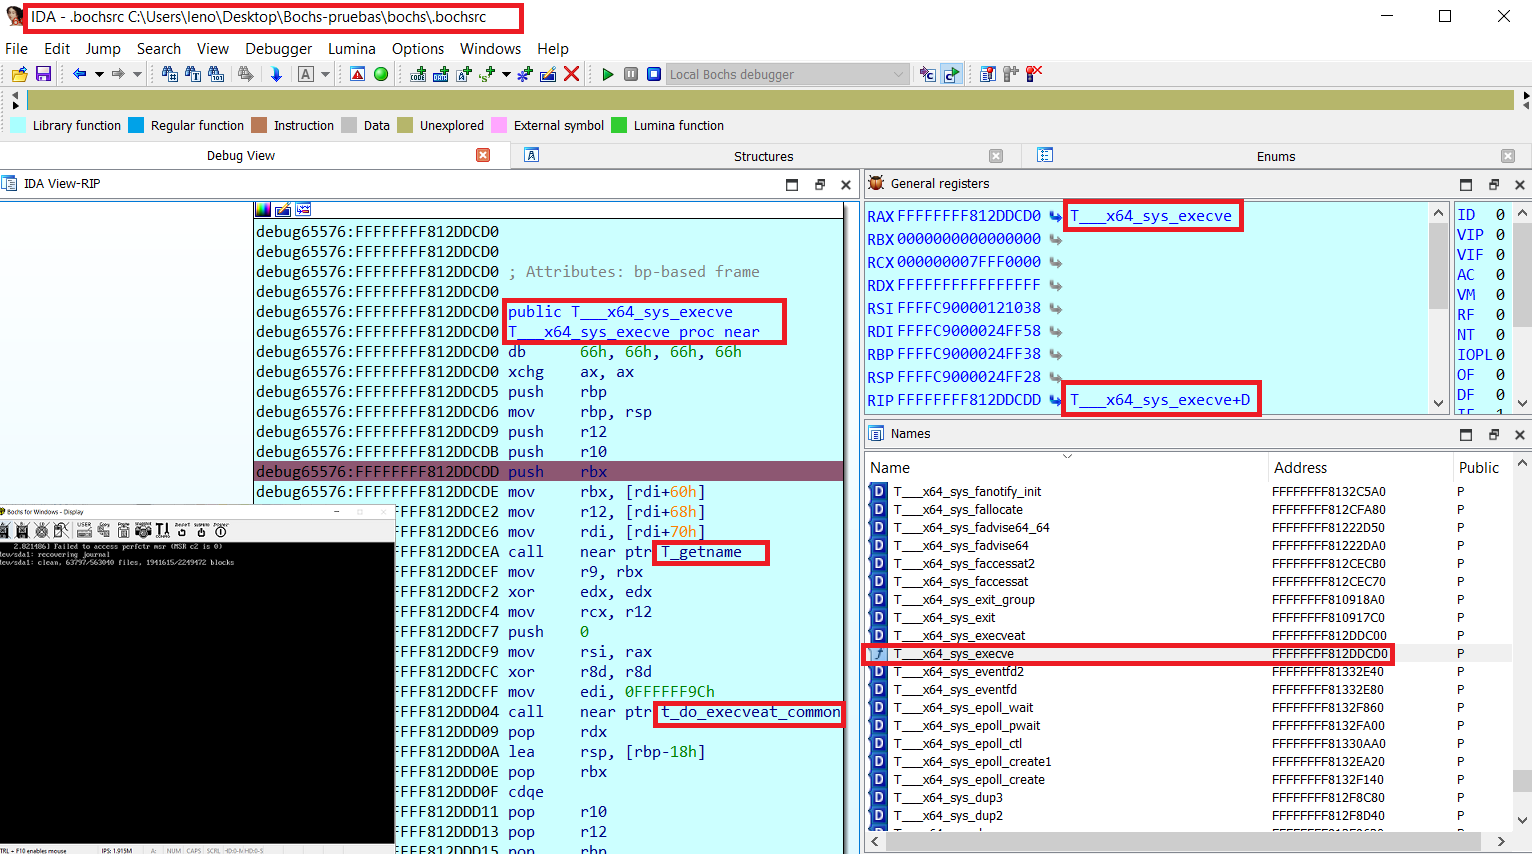 therealdreg/bochs_linux_kernel_debugging
Tools for Linux kernel debugging on Bochs (including symbols, native Bochs debugger and IDA PRO)
 c0mposer/c-game-modding-utility
A game modding utility that makes injecting C/C++ code easier.
 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect
 jordan9001/vsock_poc
Investigating the bug behind CVE-2021-26708
 bicurico/vaxd
Lightweight Windows disassembler, PE inspection and patch-assistance tool for native EXE/DLL files.
 euva-project/euva
A lightweight hex editor and decompiler to solve your binary file analysis problems.
 ignacioj/whacamole
Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
 bitstream93/shellcode-test-harness
A lightweight test harness designed to speed up shellcode development by providing an execution environment with integrated crash diagnostics and…
 eversinc33/drvtrace
WinDbg plugin to trace module transitions from a debugged driver.
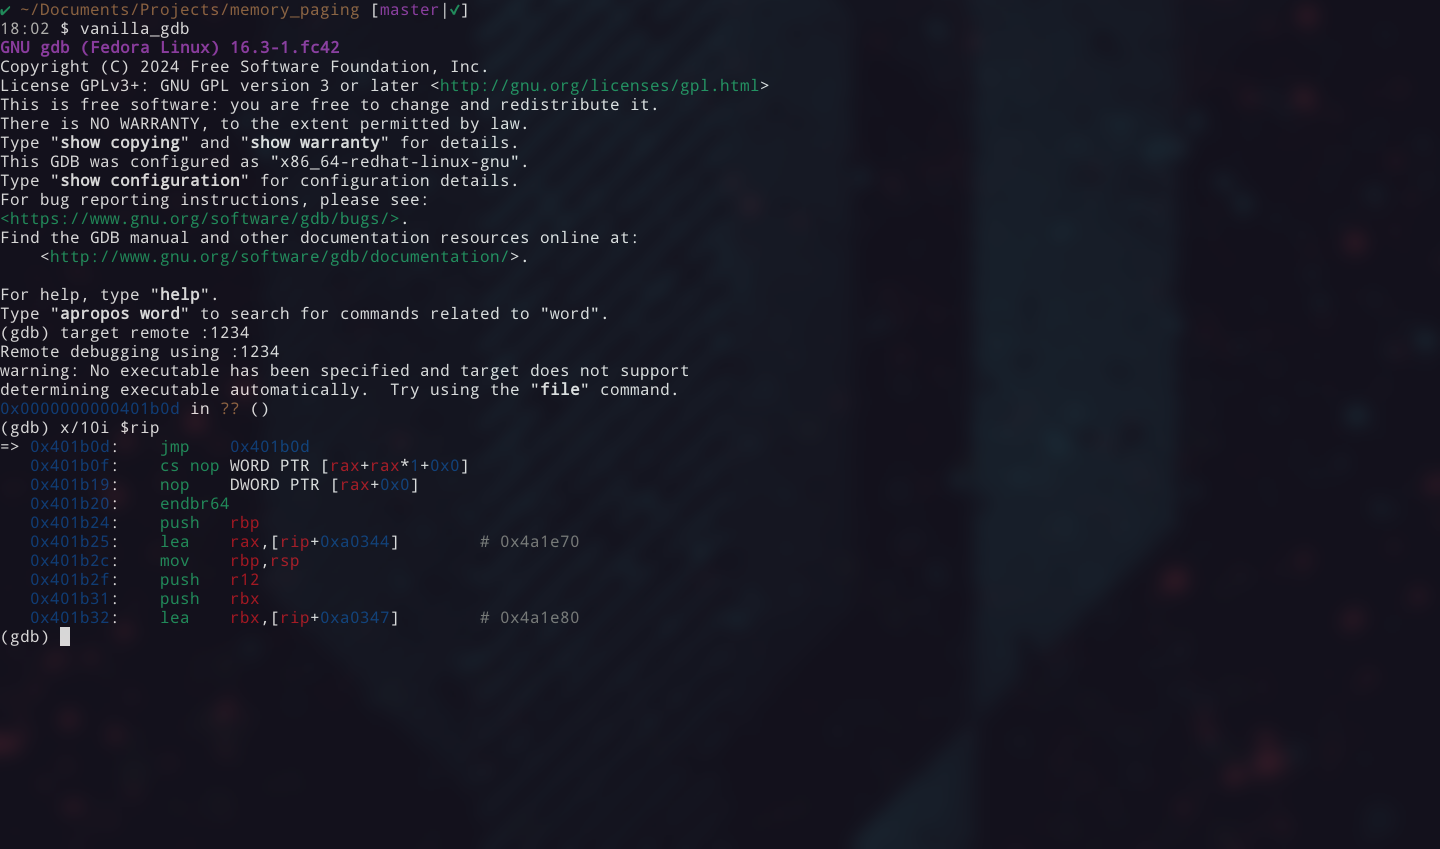 jazho76/page_table_walk
Walk x86-64 page tables by hand in qemu and gdb. Decompose a virtual address, follow cr3 through all levels of physical memory, and extract a flag…
 grecandrei/ida-pro-mcp
Local-first, deterministic MCP server for IDA Pro/Home: 109 strict-schema reverse-engineering operations, evidence-backed findings, and policy-gated…
 deepquantum/dconstruct
A disassembler & experimental decompiler for TLOU2 DC Scripts.
 malwaretech/msdia-x64
Enable Microsoft PDB support in Ghidra without installing Visual Studio








