
 #1
Debugging tools specifically for analyzing malware execution flow and identifying vulnerabilities.
Kitploit recommended

 kernelzeroday/cve-2021-3156-baron-samedit
1day research effort
 velteyn/unbattletech
BattleTech: The Crescent Hawk's Inception reverse engeneering
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 nccgroup/libtalloc
libtalloc is a python script for use with GDB that can be used to analyse the "trivial allocator" (talloc)
 synacktiv/pike-agent
Experimental Linux strace LLM agent
 ejfkdev/dae
Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…
 martinclauss/exim-rce-cve-2018-6789
This repository provides a learning environment to understand how an Exim RCE exploit for CVE-2018-6789 works.
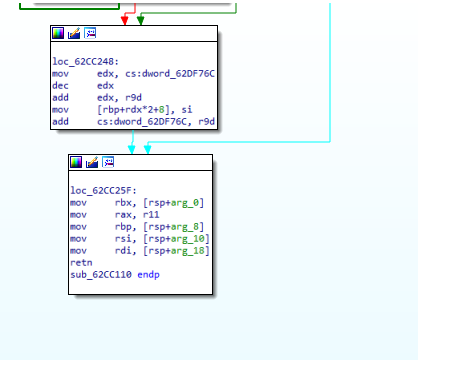 spiralbl0ck/blacklotus-analysis-stage2-bootkit-rootkit-stage
Z2A-BlackLotus Challenge stage 2 bootkit-rootkit analysis
 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 nccgroup/libmempool
Heap analysis tooling for mempool
 asherdll/r2gopclntabparser
A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.
 gmh5225/letmegg
Windows kernel proof-of-concept demonstrating an anti-debugging technique that prevents WinDbg from breaking by manipulating the kernel exception…
 webraybtl/cve-2023-40031
notepad++堆缓冲区溢出漏洞CVE-2023-40031 分析与复现
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
 mr-wolf-is-me/ida-processor-modules
IDA Pro processor modules adding disassembly support for uncommon CPU, DSP, and GPU architectures including XMOS xCORE, TI C7x/PRU, MicroBlaze, and…








