
 #1
Debugging tools specifically for analyzing malware execution flow and identifying vulnerabilities.
Kitploit recommended

 rasetsuu/vmp-devirt
Trace-assisted VMProtect devirtualization research platform: version front-ends feed a shared Remill/LLVM backend to lift handlers, recover dataflow,…
 ricardoquesada/regenerator2000
An interactive disassembler for the CPU 6502, focused on Commodore 8-bit computers. Features a TUI with modern features like x-ref, undo/redo, flow…
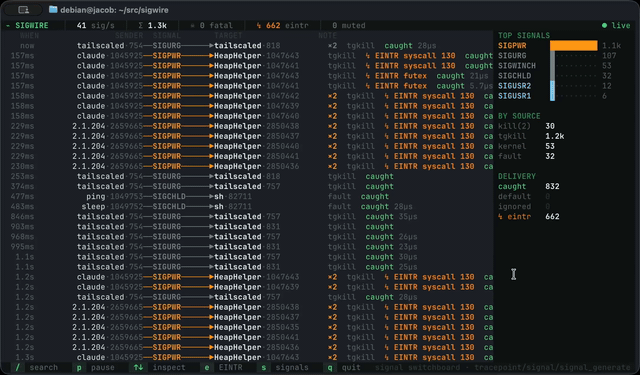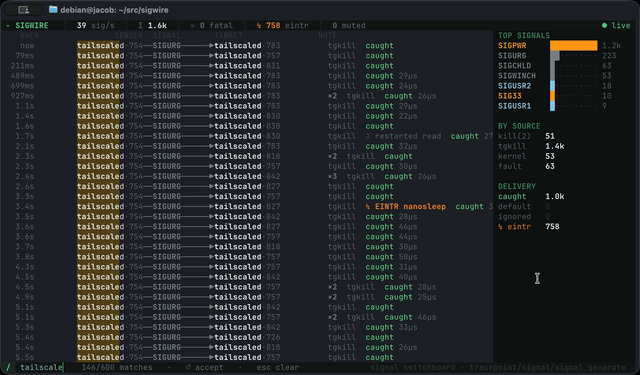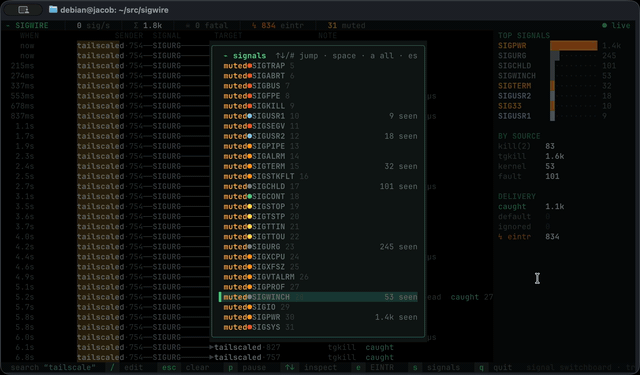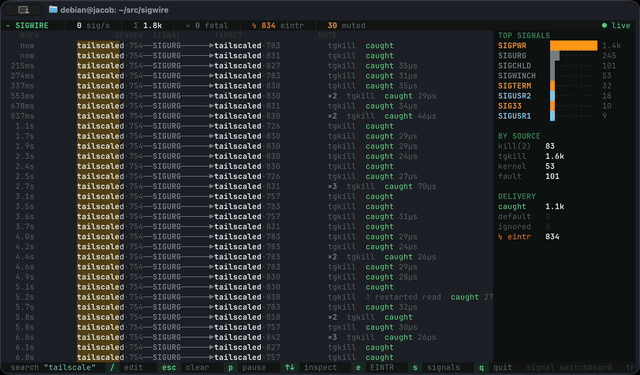 yeet-src/sigwire
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
 malwaretech/basichook
x86 Inline hooking engine (using trampolines)
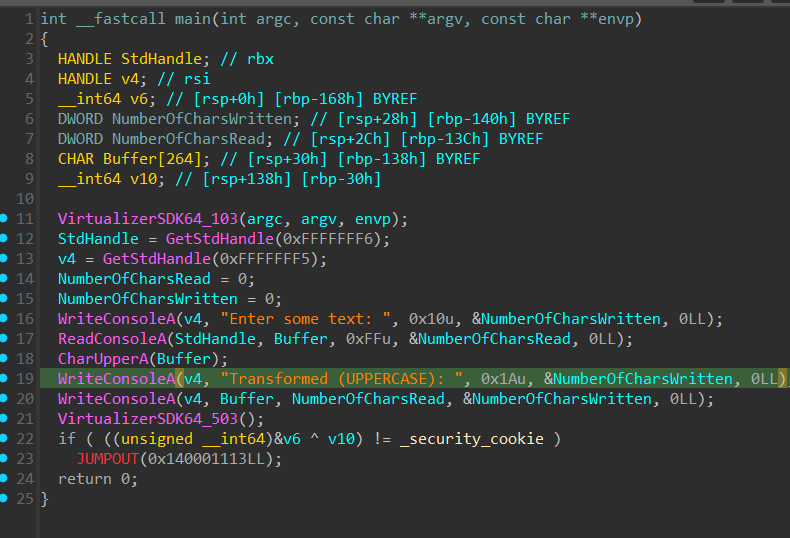 backengineering/themida-devirt
Themida Devirt Results
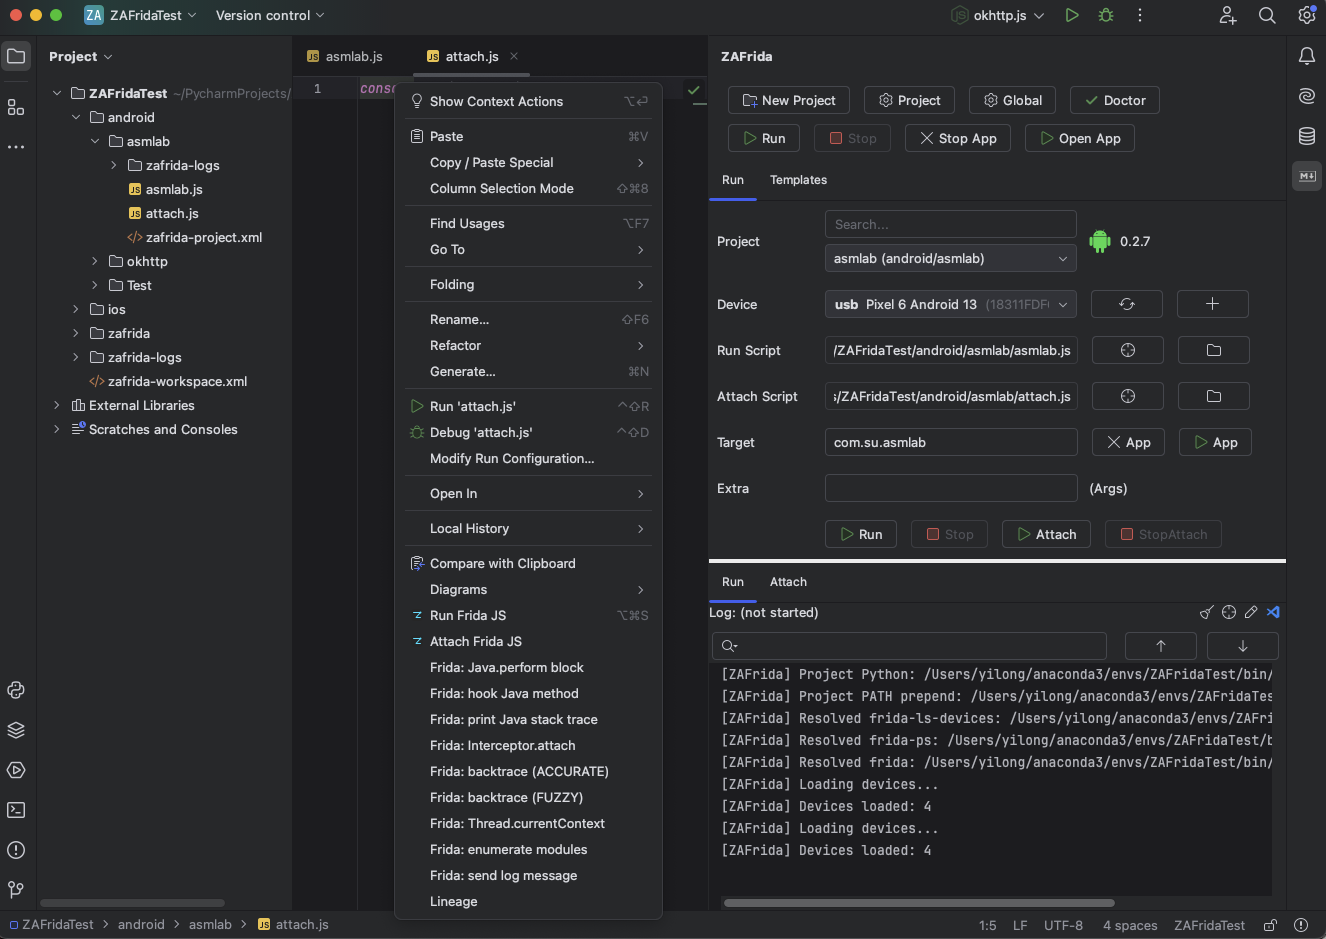 yilongmd/zafrida-ui
A Frida UI tool window inside PyCharm / JetBrains IDEs.
 controlplaneio/truffleproc
truffleproc — hunt secrets in process memory (TruffleHog & gdb mashup)
 nccgroup/iodide
The Cisco IOS Debugger and Integrated Disassembler Environment
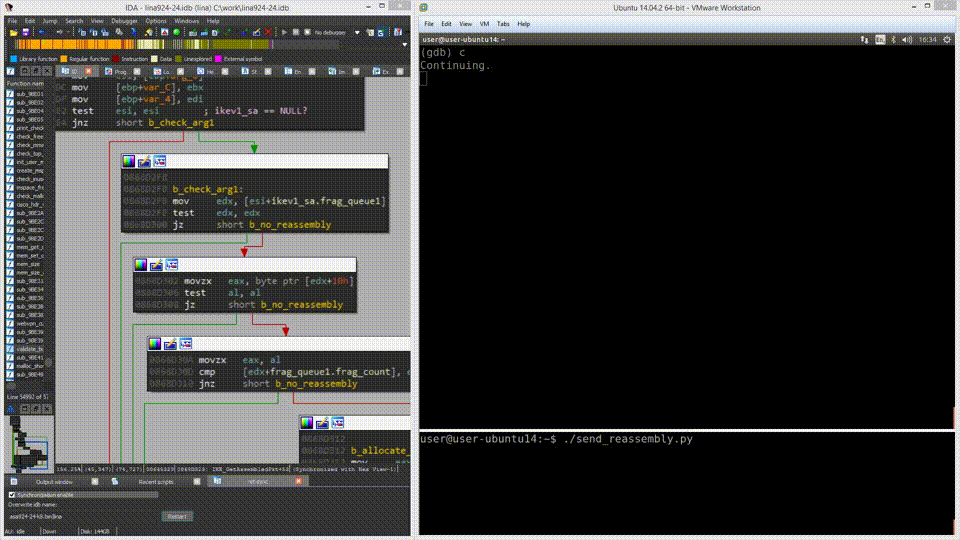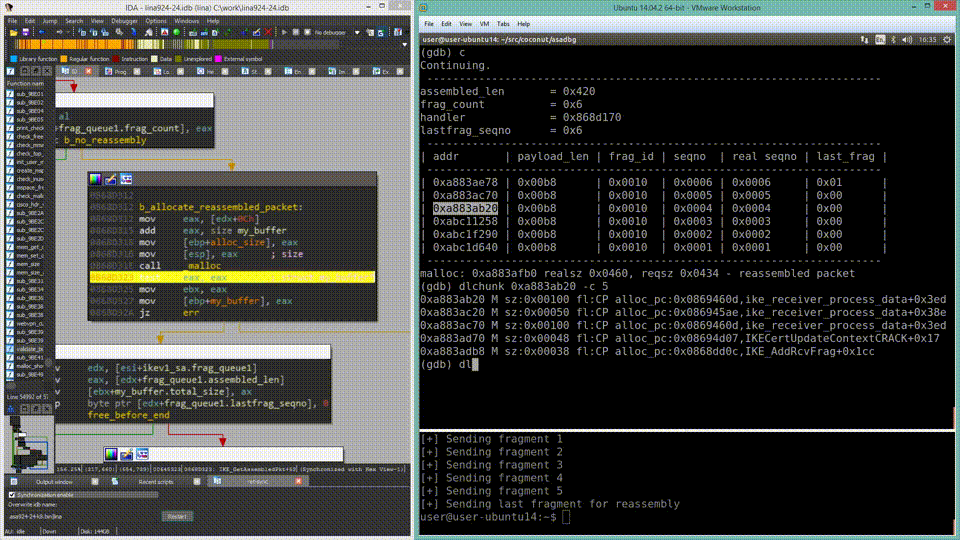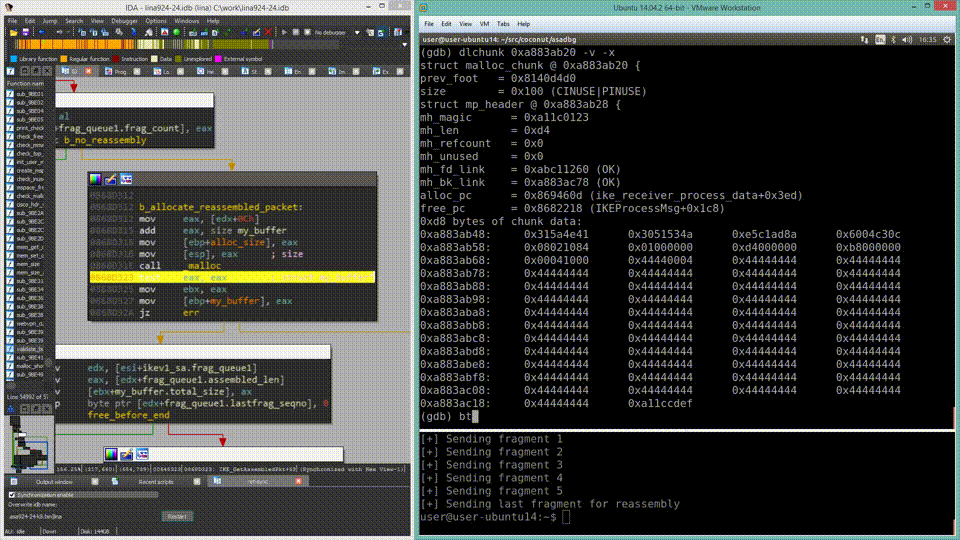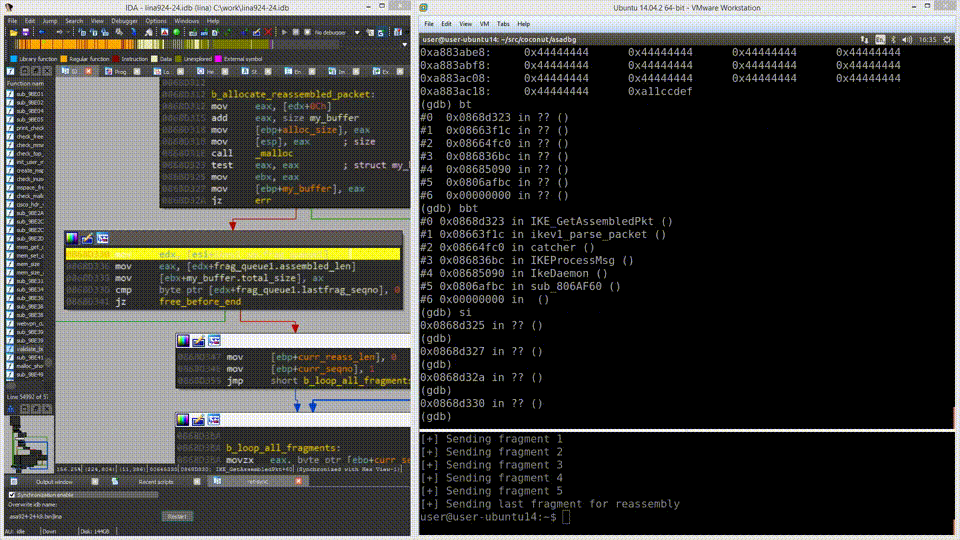 nccgroup/asadbg
asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices
 rbmm/ntdetours
Detours implementation (x64/x86) which used only ntdll import
 immunityinc/libptrace
An event driven multi-core process debugging, tracing, and manipulation framework.
 malienist/lupo
WinDbg plugin for automated malware dynamic analysis and IOC extraction. Executes within the debugger to collect predefined indicators and writes…
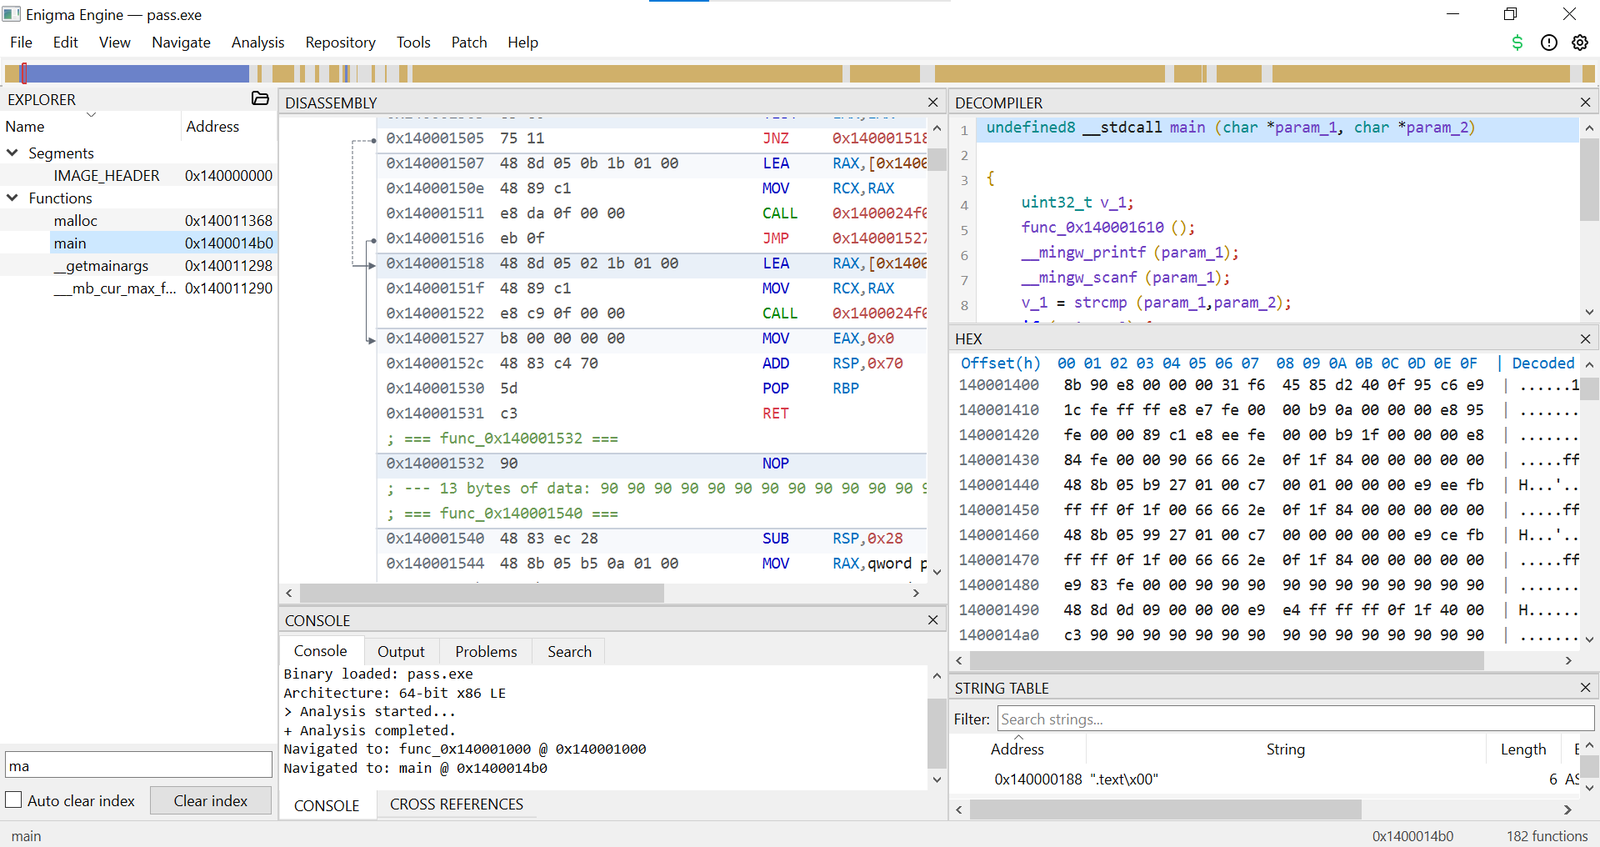 bunnybuzz/enigma
Native C++ reverse-engineering engine with disassembly, decompilation, and analysis pipeline for PE/ELF binaries, featuring interactive GUI and…
 madmin3r/unconfuserex
Deobfuscator for ConfuserEx 2.
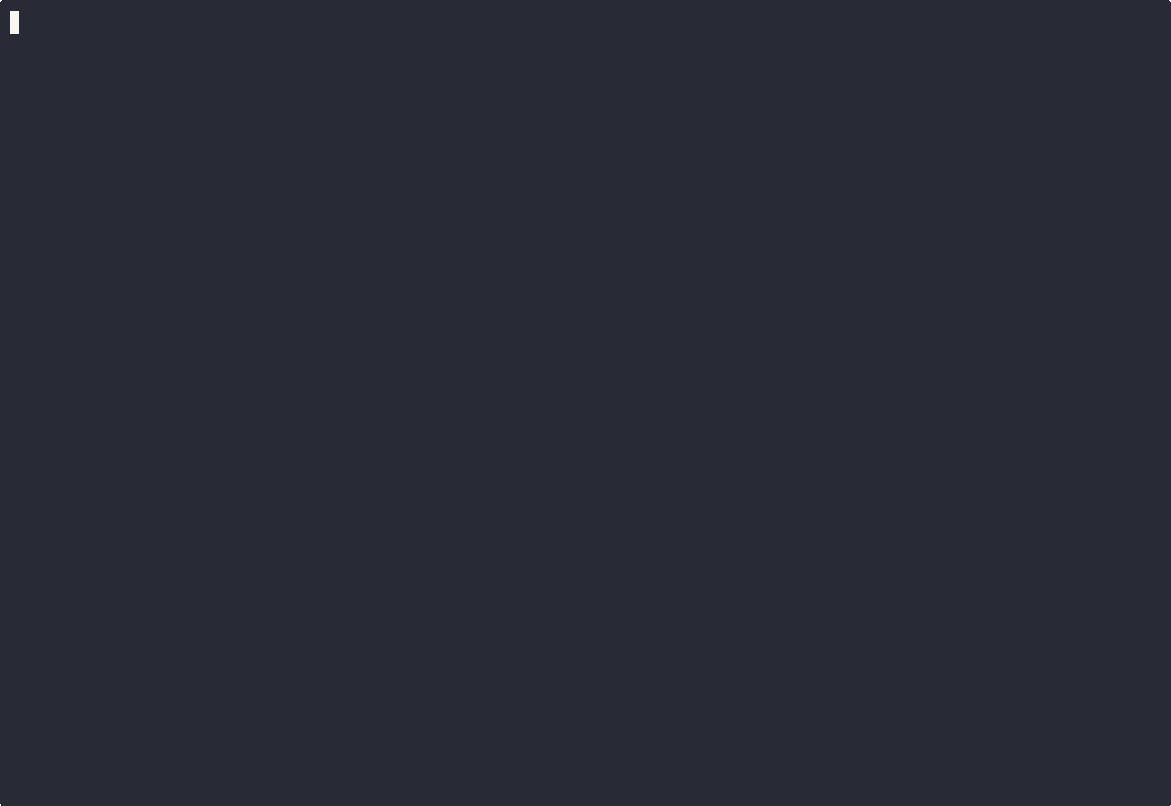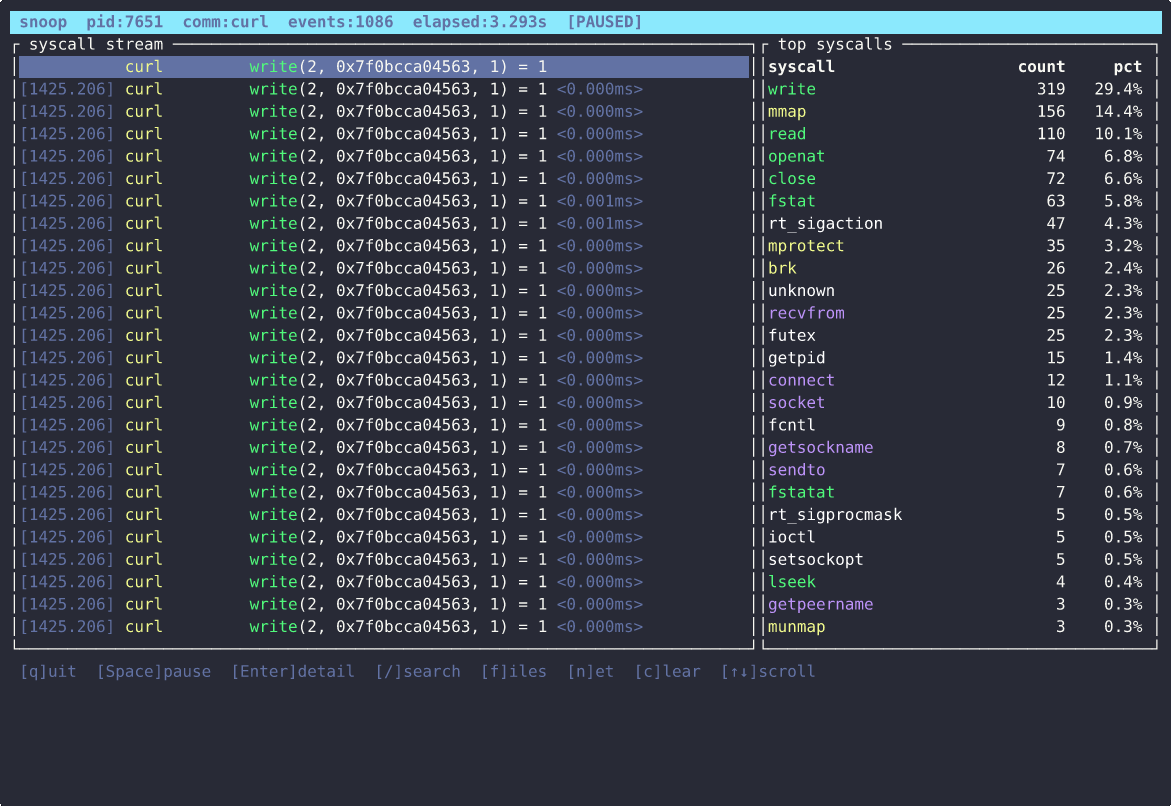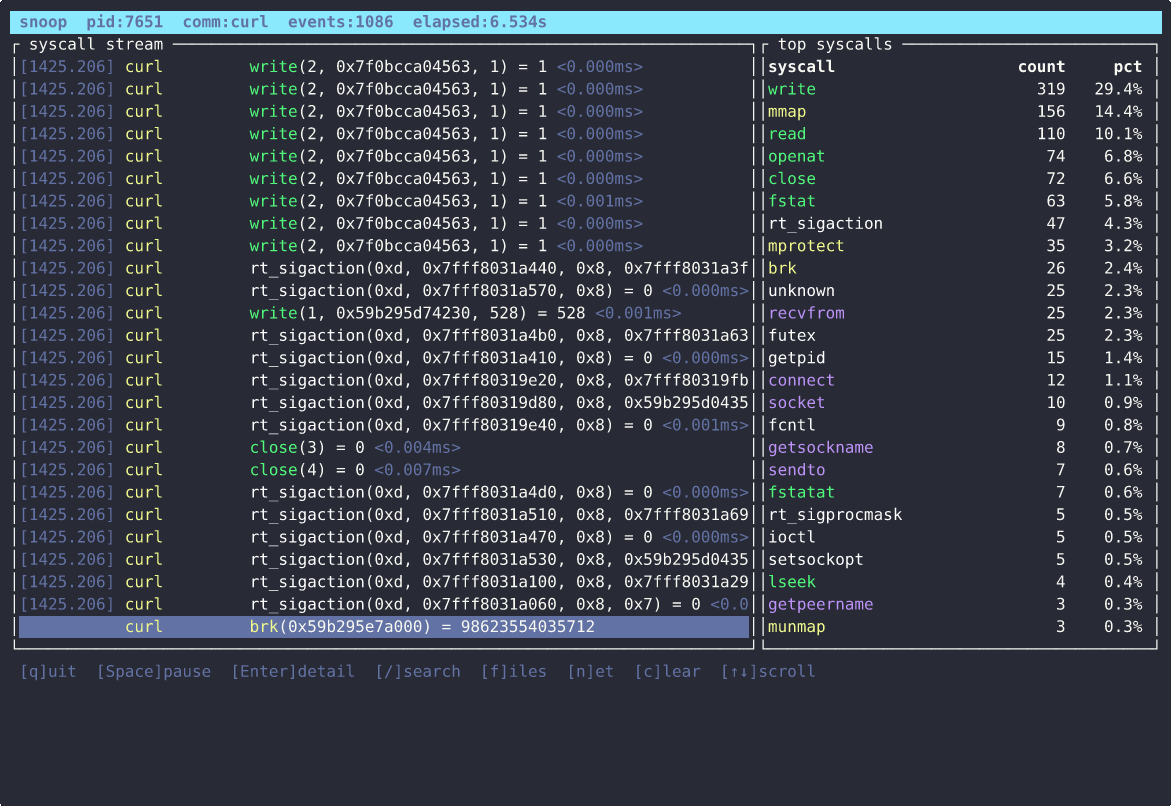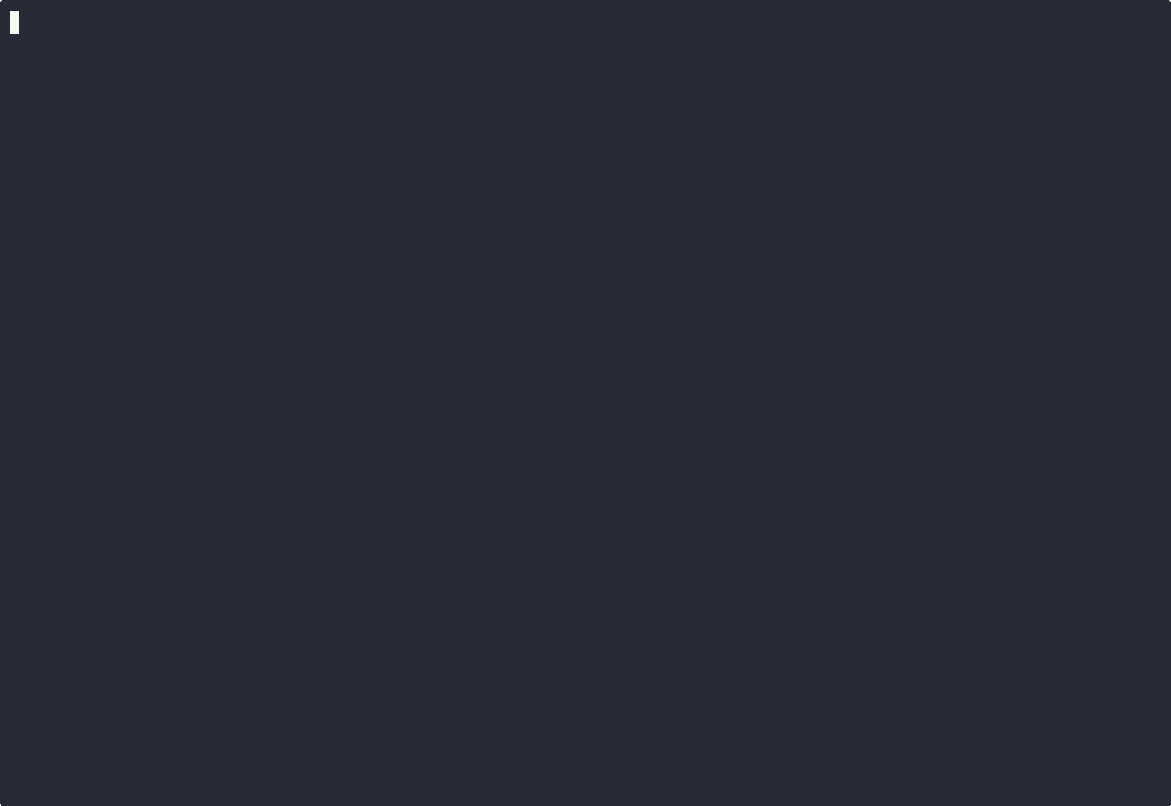 pandaadir05/snoop
A modern syscall tracer built on eBPF. Think strace, but with a real TUI, smart filters, TLS decryption, and output that's actually readable.
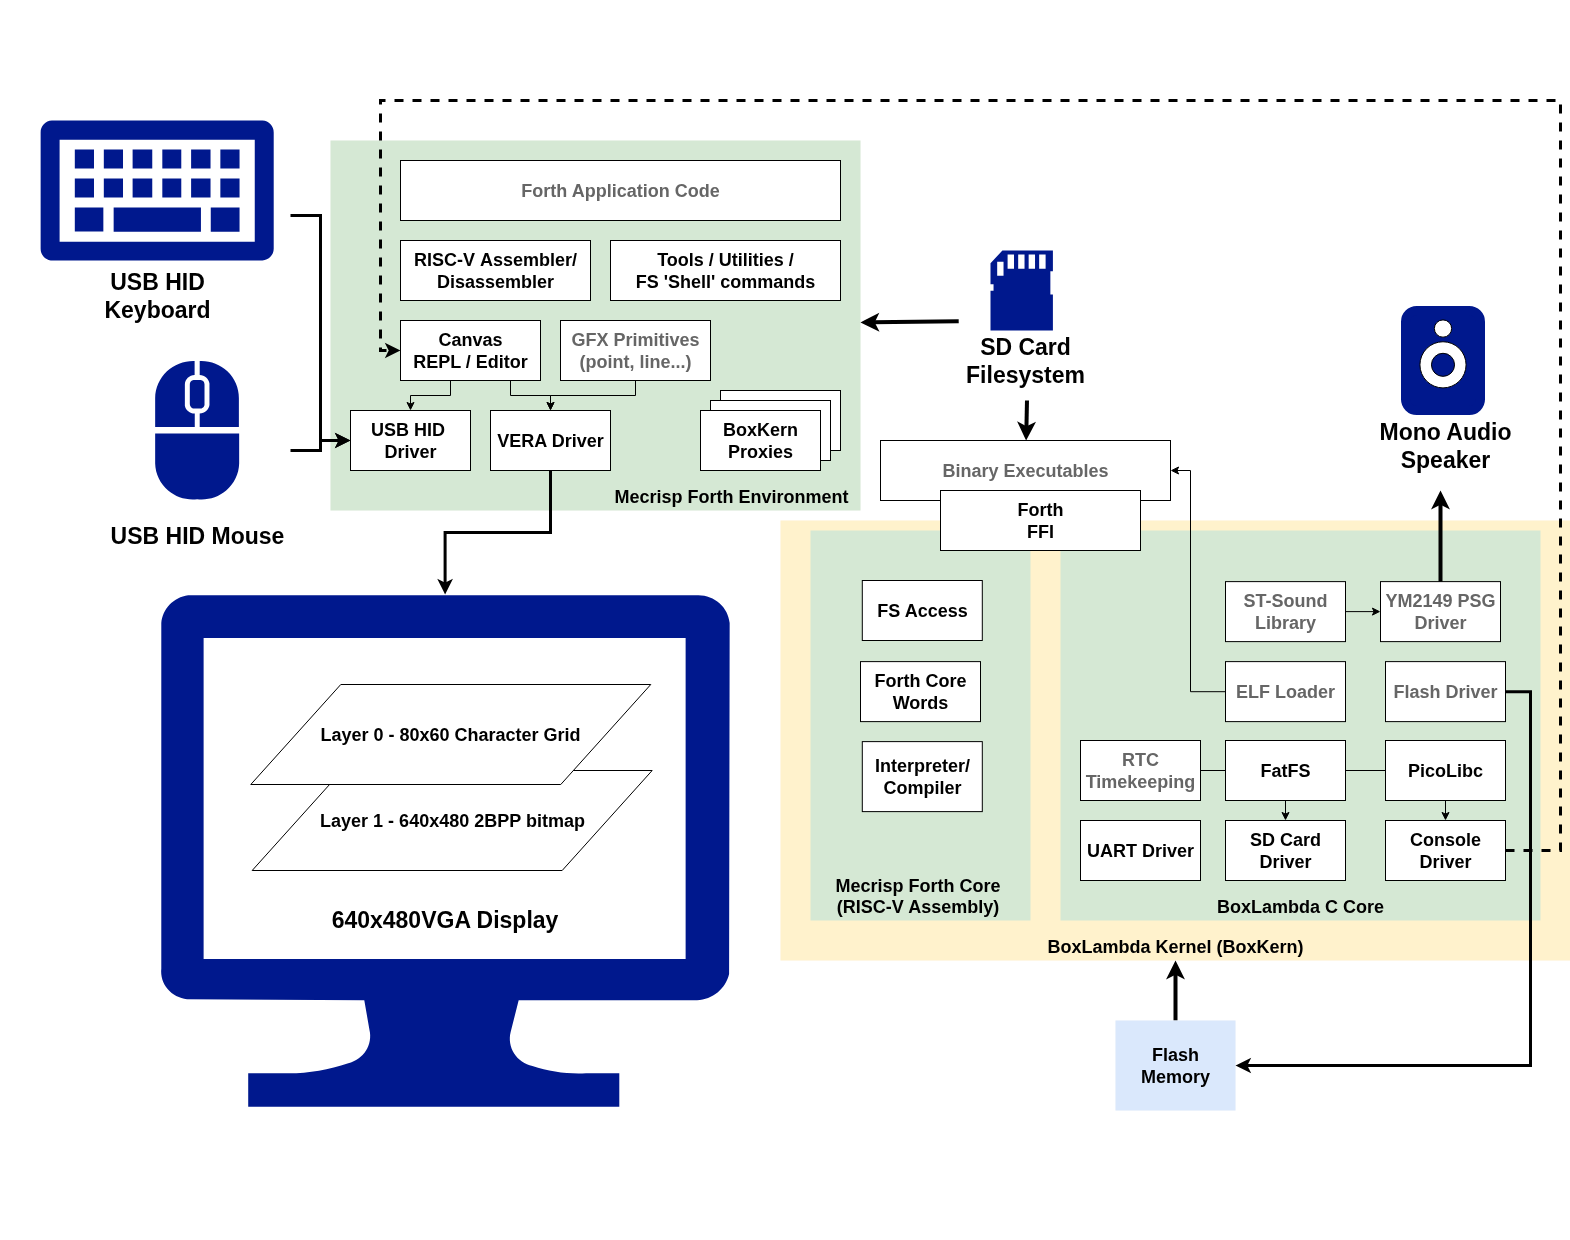 epsilon537/boxlambda
FPGA based microcomputer sandbox for software and RTL experimentation
 c0ntextomy/c0ntextomy
CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…








