
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Debuggers — Page 14 | Kitploit
Categories

Debuggers

Debugging tools specifically for analyzing malware execution flow and identifying vulnerabilities.

Kitploit recommended
Top tools

10 selected
x64dbg preview#1

x64dbg

GitHubx64dbg/x64dbg
49.1k16h 2m ago
pwndbg preview#2

pwndbg

GitHubpwndbg/pwndbg
10.8k7h 12m ago
gef preview#3

gef

GitHubhugsy/gef
8.3k2 months ago
delve preview#4

delve

GitHubgo-delve/delve
25.0k8 days ago
rr preview#5

rr

GitHubrr-debugger/rr
10.7k4 days ago
cutter preview#6

cutter

GitHubrizinorg/cutter
19.4k1 month ago
radare2 preview#7

radare2

GitHubradareorg/radare2
24.5k8h 44m ago
ghidra preview#8

ghidra

GitHubnationalsecurityagency/ghidra
71.1k1 day ago
dnSpy preview#9

dnSpy

GitHubdnspyex/dnspy
10.9k10 days ago
dynamorio preview#10

dynamorio

GitHubdynamorio/dynamorio
3.2k13h 43m ago
NewestRelevanceMost popularRecently updated
558 results
libslub preview

libslub

GitHubnccgroup/libslub

Python library for examining Linux kernel SLUB heap allocations and structures within GDB, enabling deeper understanding of kernel heap internals for…
exploitationreverse-engineeringdebuggers+1
1881 year ago
Squalr preview

Squalr

GitHubsqualr/squalr

A generic game/software hacking tool written from the ground up in Rust.

dynamic-analysis-sandboxingmemory-forensicsexploitation+5
1514 months ago
dezlock-dump preview

dezlock-dump

GitHubdougwithseismic/dezlock-dump

Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
reconnaissancememory-forensicsdynamic-code-analysis+6
829 days ago
EVENSTAR preview

EVENSTAR

GitHubwinterknife/evenstar

Intel 64/Windows low-level experiments

memory-forensicsexploitationreverse-engineering+5
1081 month ago
shellex preview

shellex

GitHubtherealdreg/shellex

C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
exploitationreverse-engineeringshellcode+5
1123 years ago
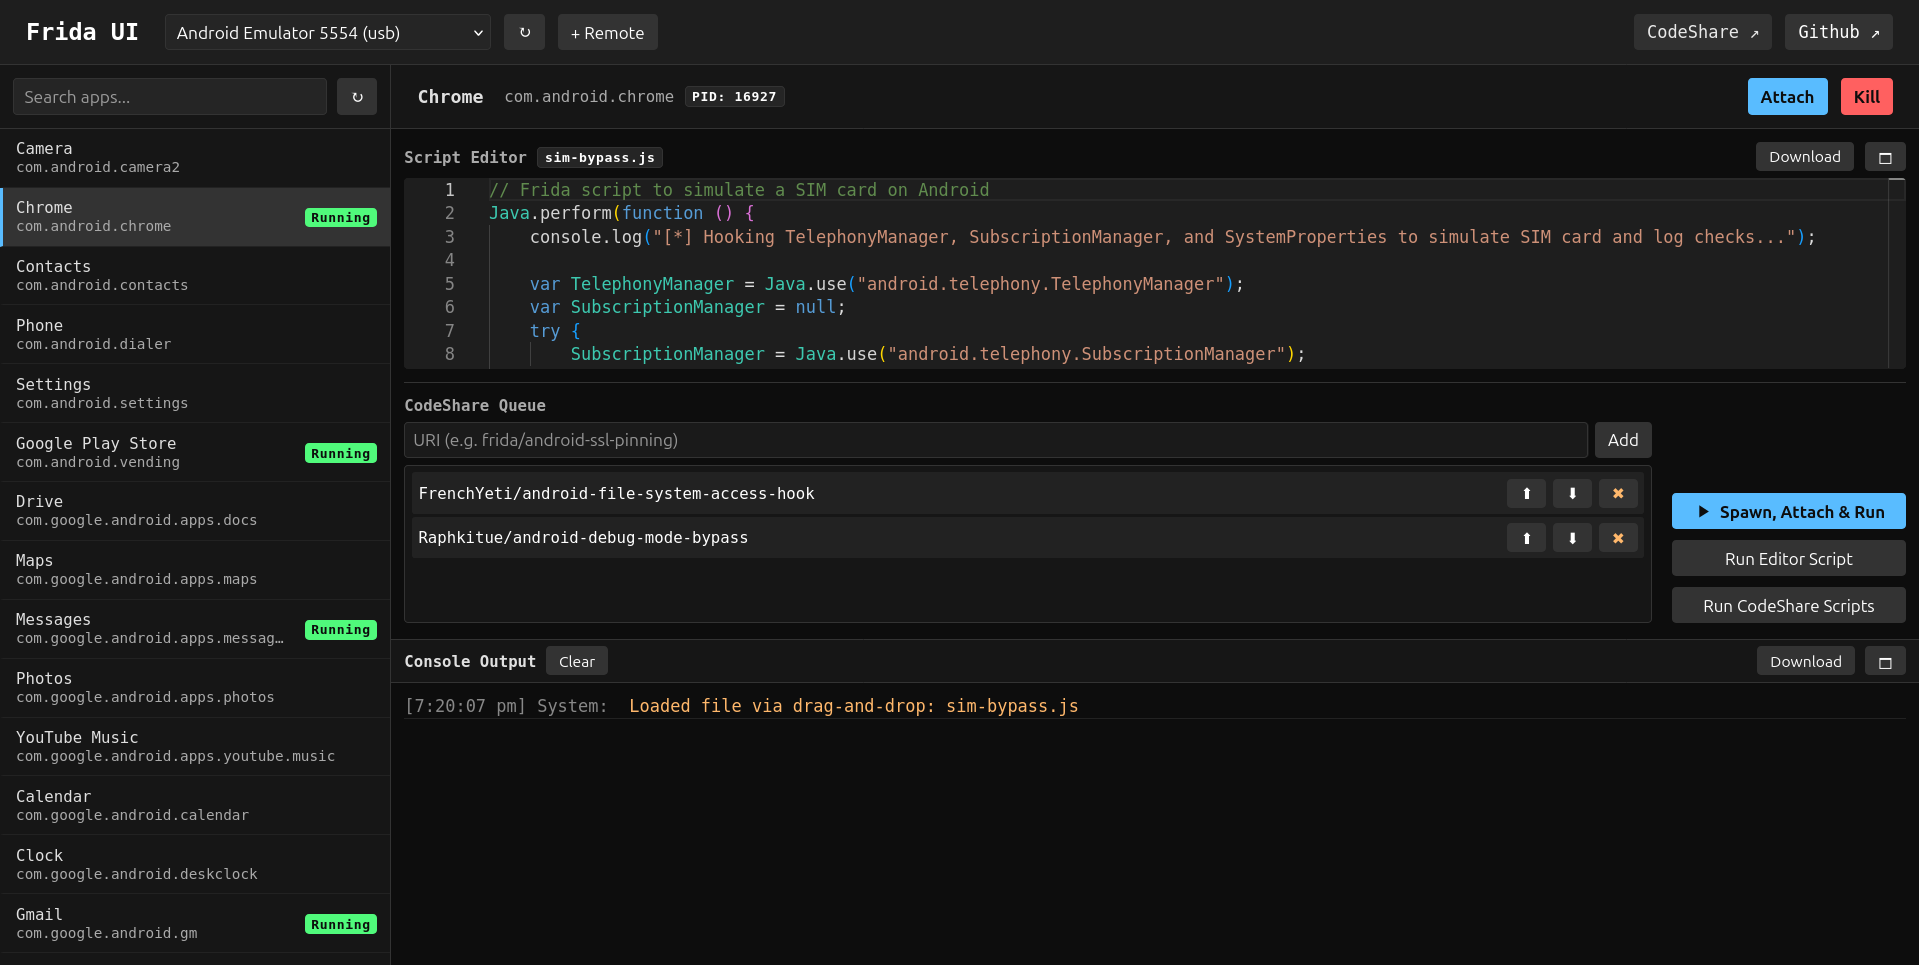
frida-ui preview

frida-ui

GitHubadityatelange/frida-ui

Interact with Frida devices, processes, and scripts directly from your browser.
android-securitydynamic-analysis-sandboxingweb-proxies-interception+5
2387 months ago
salt preview

salt

GitHubpaolomonti42/salt

SALT - SLUB ALlocator Tracer for the Linux kernel
memory-forensicsreverse-engineeringdebuggers+2
1578 years ago
PsyloDbg preview

PsyloDbg

GitHubdarkcodersc/psylodbg

User-friendly Microsoft Windows Debugger for Malware Analysts.
reverse-engineeringdebuggersmalware-analysis+1
2063 years ago
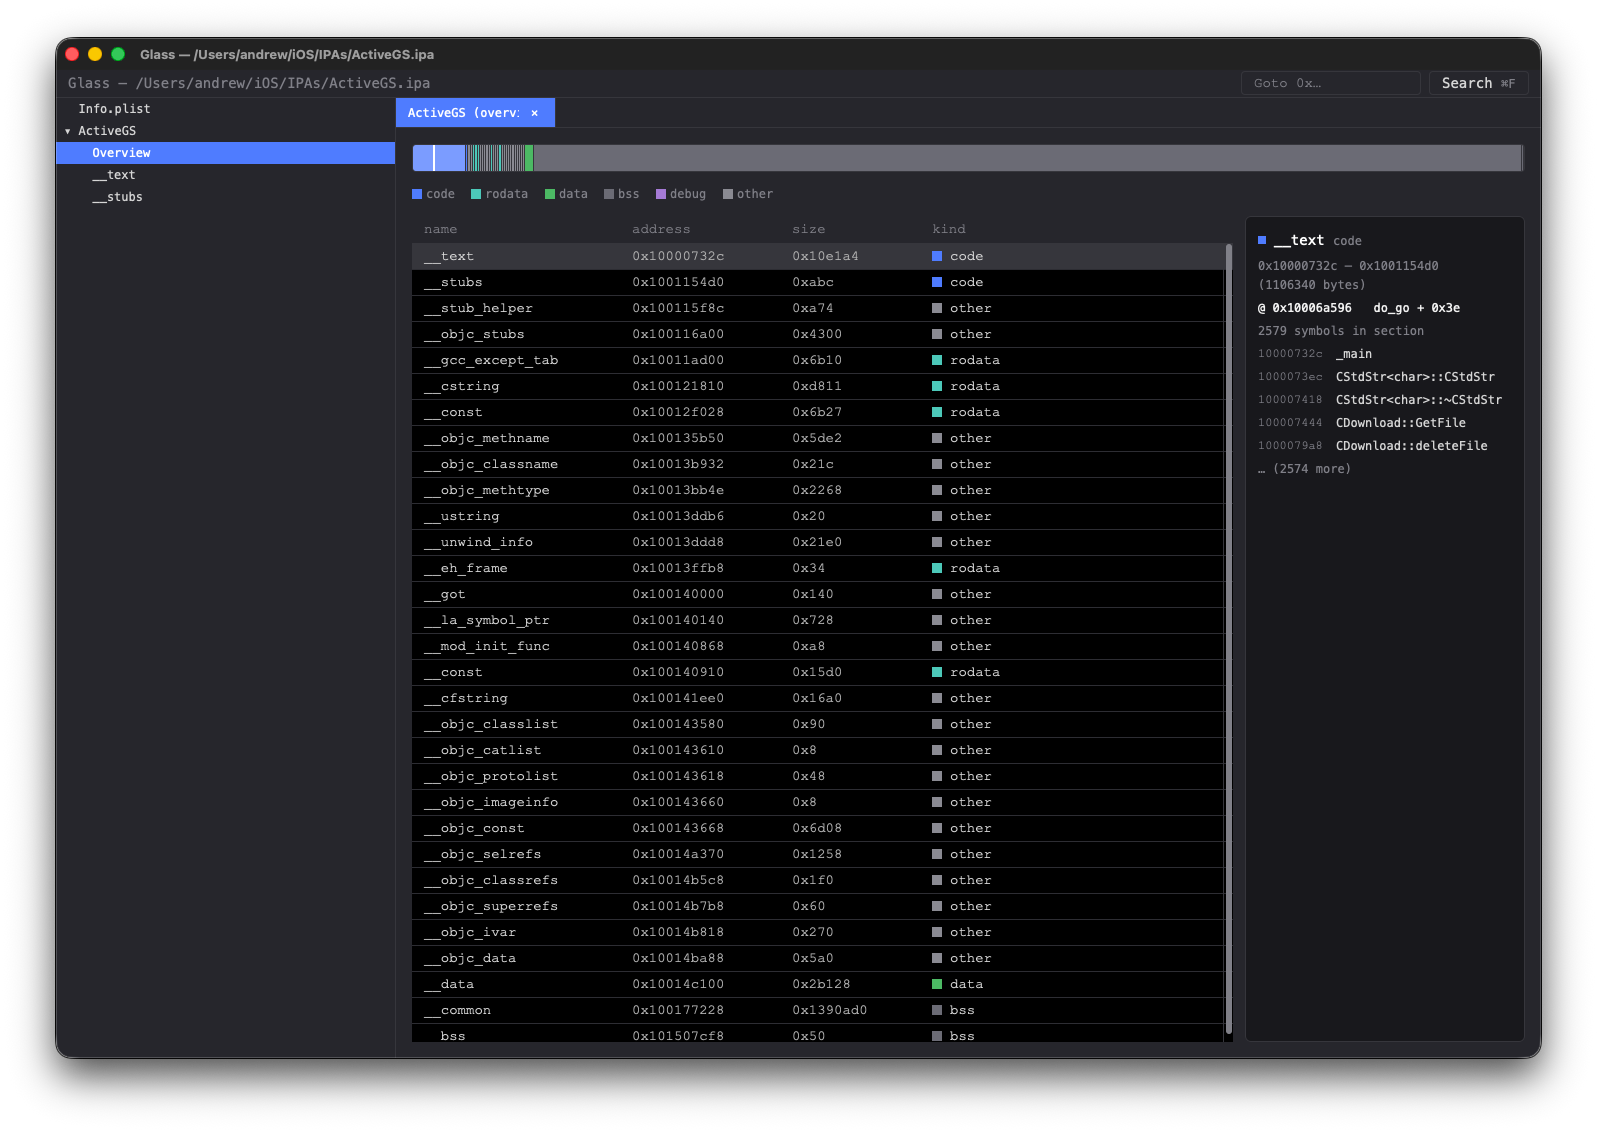
Glass preview

Glass

GitHubazw413/glass

Glass - a fast and free IDA Pro alternative
android-securityembedded-systems-securitystatic-analysis+7
1912 months ago
Learning-Linux-Binary-Analysis preview

Learning-Linux-Binary-Analysis

GitHubpacktpublishing/learning-linux-binary-analysis

Learning Linux Binary Analysis, published by Packt
memory-forensicsexploitationreverse-engineering+7
893 years ago
r0ak preview

r0ak

GitHubharryanon/r0ak

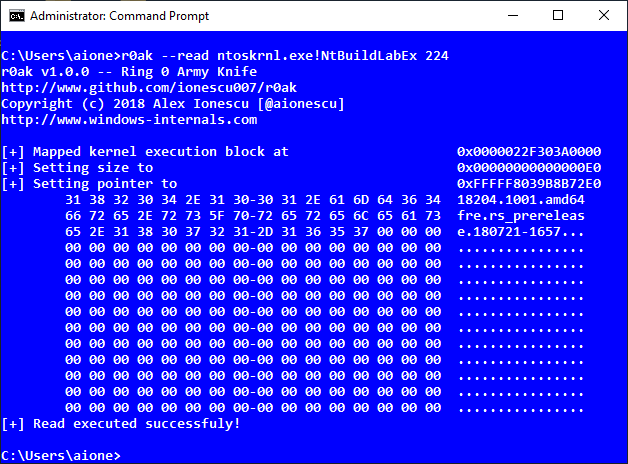
Windows command-line utility for reading, writing, and executing kernel-mode code from Administrator context using a font validation execution…
privilege-escalationmemory-forensicsvulnerability-analysis+5
1088 years ago
showstopper preview

showstopper

GitHubcheckpointsw/showstopper

ShowStopper is a tool for helping malware researchers explore and test anti-debug techniques or verify debugger plugins or other solutions that clash…
reverse-engineeringdebuggersmalware-analysis+1
2244 years ago
instrumentation_callbacks preview

instrumentation_callbacks

GitHubdeputation/instrumentation_callbacks

A proof of concept demonstrating instrumentation callbacks on Windows 10 21h1 with a TLS variable to ensure all syscalls are caught.
dynamic-analysis-sandboxingreverse-engineeringdebuggers+1
1604 years ago
asafw preview

asafw

GitHubnccgroup/asafw

Set of scripts to deal with Cisco ASA firmware [pack/unpack etc.]
embedded-systems-securityexploitationreverse-engineering+4
1074 years ago
AFLTriage preview

AFLTriage

GitHubqualcomm/afltriage

Portable debugger-based crash triage tool for fuzzing outputs. Supports parallel triage, crash deduplication, sanitizer report parsing, and multiple…
vulnerability-analysisdebuggersfuzzing
1456 months ago
grap preview

grap

GitHubquosecgmbh/grap

Define and match user-defined graph patterns against binary control flow graphs using a Capstone-based disassembler, with CLI, Python bindings, and…
static-analysisreverse-engineeringdebuggers+2
1554 years ago
gftrace preview

gftrace

GitHubleandrofroes/gftrace

A command line Windows API tracing tool for Golang binaries.
dynamic-analysis-sandboxingreverse-engineeringdebuggers+2
1592 years ago
r2web preview

r2web

GitHubradareorg/r2web

Access radare2 from anywhere, anytime.

static-analysisdynamic-analysis-sandboxingreverse-engineering+2
5122 days ago
Previous1…131415…31Next








