
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended
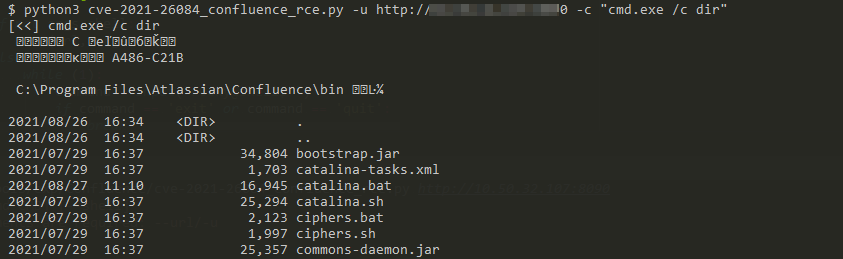
 prettyrecon/cve-2021-26084_confluence
CVE-2021-26084 - Confluence Pre-Auth RCE OGNL injection 回显
 xwpdx0/poc-2025-9074
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…
 dakotanelson/multicat
PoC RAT using the sneaky-creeper data exfiltration library
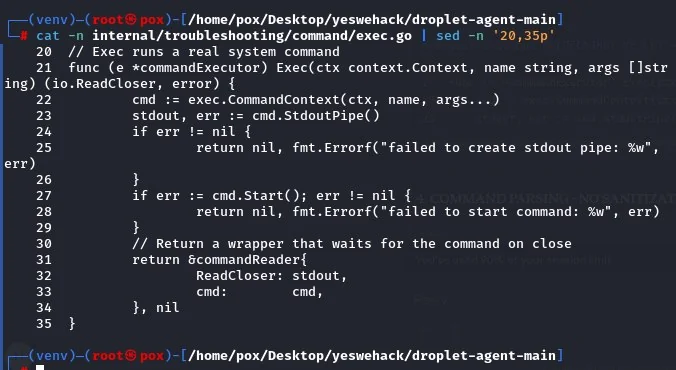 poxsky/cve-2026-24516-digitalocean-rce
Critical Pre-Auth Root RCE (CVSS 10.0) in DigitalOcean Droplet Agent up to v1.3.2 via Command Injection.
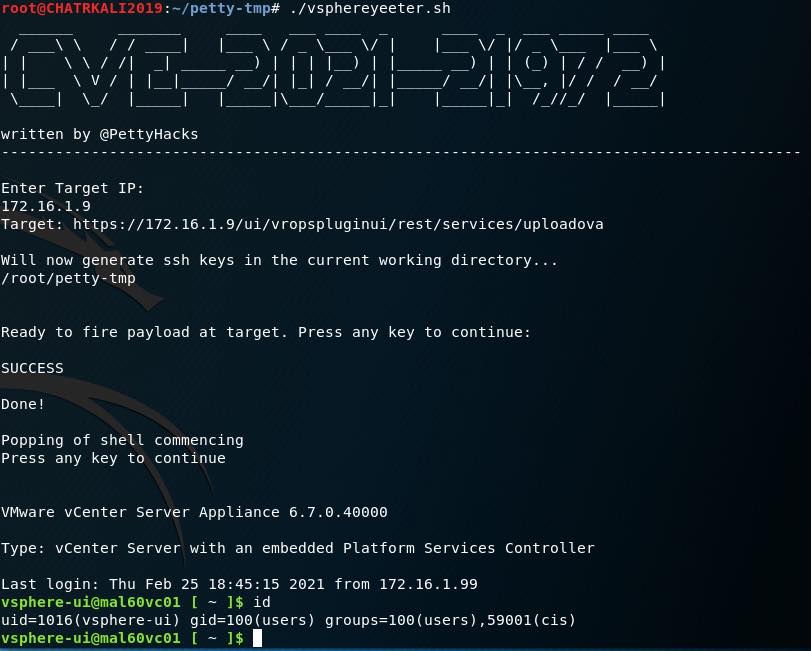 pettyhacks/vsphereyeeter
POC exploit for CVE-2021-21972
 likekabin/cve-2018-2628
Python exploit for CVE-2018-2628 targeting WebLogic servers, providing remote command execution via a JSP webshell with interactive cmd interface.
 falcon-lnhg/strutsshell
Interactive command-line shell for exploiting Apache Struts CVE-2017-5638. Automates HTTP/HTTPS exploitation with real-time shell interaction on…
 badb33f/apache-log4j-poc
Proof of Concept of apache log4j LDAP lookup vulnerability. CVE-2021-44228
 vulnmachines/bitbucket-cve-2022-36804
CVE-2022-36804 Atlassian Bitbucket Command Injection Vulnerability
 noshadi-sec/cve-2026-97229
Python exploit for CVE-2026-97229, a GitLab CI lint regex RCE. Creates a project, pushes a malicious CI config, triggers the lint endpoint, and…
 0xblackash/cve-2026-24061
CVE-2026-24061
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
 t54r/cve-2026-10795_poc
AI amended PoC for CVE-2026-10795 - for educational purposes only - use at your own risk on labs you own ;)
 ridpath/cve-2021-26828-ultimate
ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR
 emirpolatt/cve-2022-36446
CVE-2022-36446 - Webmin 1.996 Remote Code Execution
 ieee0824/cve-2017-1000117
Proof-of-concept exploit for CVE-2017-1000117, a Git remote code execution vulnerability that executes ifconfig on successful exploitation.
 hybryx/cve-2020-8165
Python exploit for CVE-2020-8165 targeting Rails MemCacheStore and RedisCacheStore. Enables remote command execution via user-provided object…
 dsibilio/follina-spring
Server to host/activate Follina payloads & generator of malicious Word documents exploiting the MS-MSDT protocol. (CVE-2022-30190)








