
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended
 yifanzhg/cve-2023-45158
Proof-of-concept exploit for CVE-2023-45158, a command injection vulnerability in web2py. Demonstrates remote code execution via crafted HTTP…
 4m3rr0r/cve-2011-2523-poc
Python exploit for CVE-2011-2523 (VSFTPD 2.3.4 Backdoor Command Execution)
 hex00-0x4/cve-2025-24893-xwiki-rce
This vulnerability could allow a malicious user to execute remote code by sending appropriately crafted requests to the default search engine…
 nanowraith/cve-2024-23692
Proof-of-concept exploit for CVE-2024-23692, demonstrating command injection in HFS via crafted HTTP requests to execute system commands and retrieve…
 skynoxk/cve-2025-48703
Remote Code execution in CentOS web panel
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 0xblackash/cve-2026-24061
CVE-2026-24061
 saidbenaissa/cve-2025-11953-vulnerability-demo
CVE-2025-11953 demonstration: Critical RCE vulnerability in React Native CLI (CVSS 9.8). Educational security research with proof-of-concept exploits…
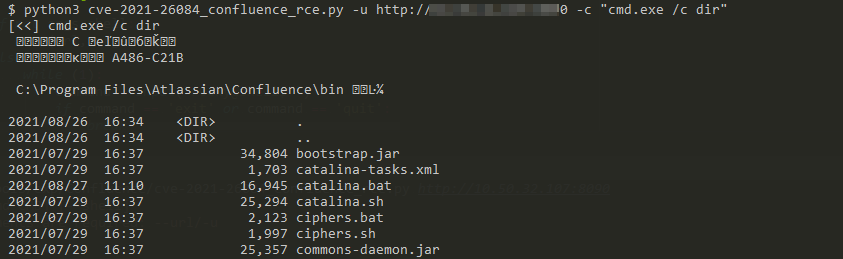 prettyrecon/cve-2021-26084_confluence
CVE-2021-26084 - Confluence Pre-Auth RCE OGNL injection 回显
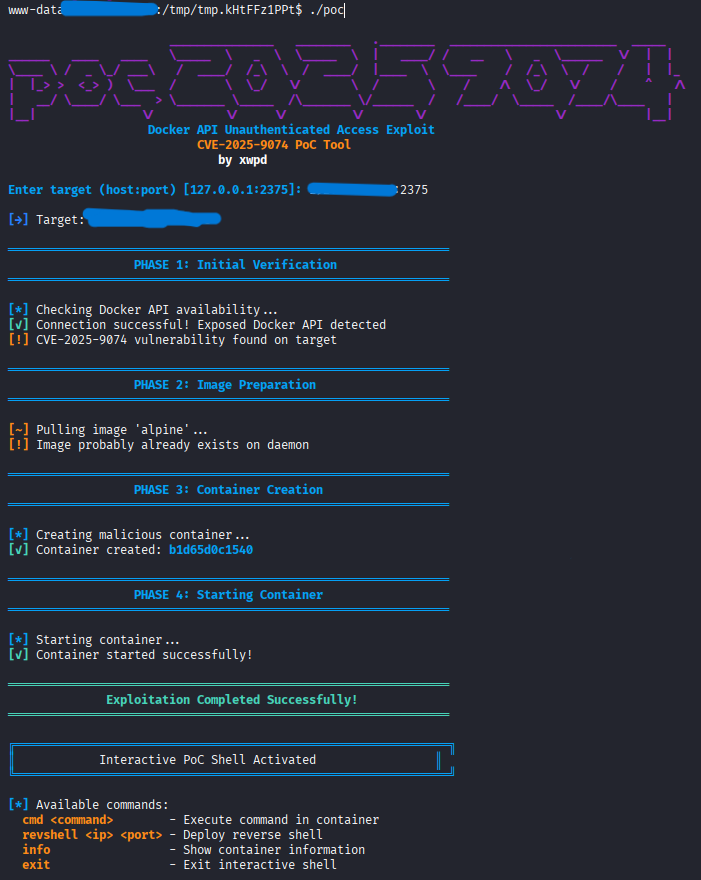 xwpdx0/poc-2025-9074
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…
 dakotanelson/multicat
PoC RAT using the sneaky-creeper data exfiltration library
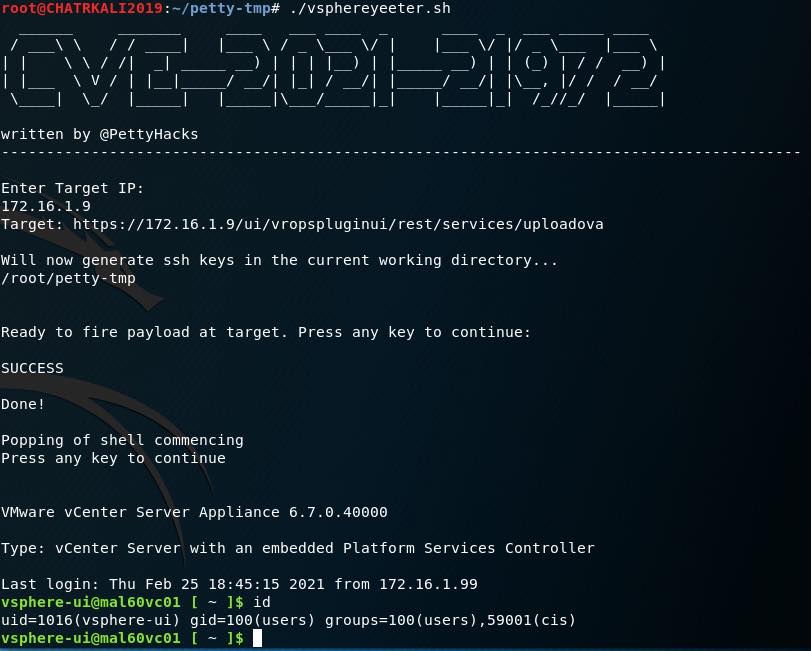 pettyhacks/vsphereyeeter
POC exploit for CVE-2021-21972
 likekabin/cve-2018-2628
Python exploit for CVE-2018-2628 targeting WebLogic servers, providing remote command execution via a JSP webshell with interactive cmd interface.
 falcon-lnhg/strutsshell
Interactive command-line shell for exploiting Apache Struts CVE-2017-5638. Automates HTTP/HTTPS exploitation with real-time shell interaction on…
 badb33f/apache-log4j-poc
Proof of Concept of apache log4j LDAP lookup vulnerability. CVE-2021-44228
 vulnmachines/bitbucket-cve-2022-36804
CVE-2022-36804 Atlassian Bitbucket Command Injection Vulnerability
 ridpath/cve-2021-26828-ultimate
ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR
 emirpolatt/cve-2022-36446
CVE-2022-36446 - Webmin 1.996 Remote Code Execution








