
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended

 synacktiv/cve-2025-47227_cve-2025-47228
ScriptCase Pre-Authenticated Remote Command Execution exploitation script (CVE-2025-47227, CVE-2025-47228).
 johanneslks/cve-2025-14558
FreeBSD rtsold DNSSL Command Injection (RCE)
 gh-ost00/cve-2024-7120
Proof-of-concept exploit for CVE-2024-7120 command injection vulnerability in RAISECOM gateway devices. Provides exploitation details, affected…
 cybersecurityworks553/log4j-shell-csw
A Proof-Of-Concept Exploit for CVE-2021-44228 vulnerability.
 richard-tang/sscms-pluginshell
CVE-2022-28118
 mattimustang/firepwner
Exploit for CVE-2015-6357 Cisco FireSIGHT Management Center Certificate Validation Vulnerability
 machine1337/smtpshell
A simple Reverse Shell that can communicate through Gmail SMTP or any other SMTP to evade network restrictions
 dntaskmehow/neo-defender
This framework has been **RE-WEAPONIZED** & exploits CVE-2026-33825, a local privilege escalation (LPE) vulnerability in Microsoft Defender caused by…
 p0dalirius/cve-2020-8813-cacti-rce-in-graph_realtime
CVE-2020-8813 - RCE through graph_realtime.php in Cacti 1.2.8
 b4sh2/cve-2025-57819-poc
CVE-2025-57819 -> rce
 avento/cve-2023-0669
GoAnywhere MFT CVE-2023-0669 LicenseResponseServlet Deserialization Vulnerabilities Python RCE PoC(Proof of Concept)
 rmhowe425/poc-cve-2026-93674
Python proof-of-concept exploit for CVE-2026-93674, an authenticated blind command injection in Langflow, enabling remote shell command execution via…
 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
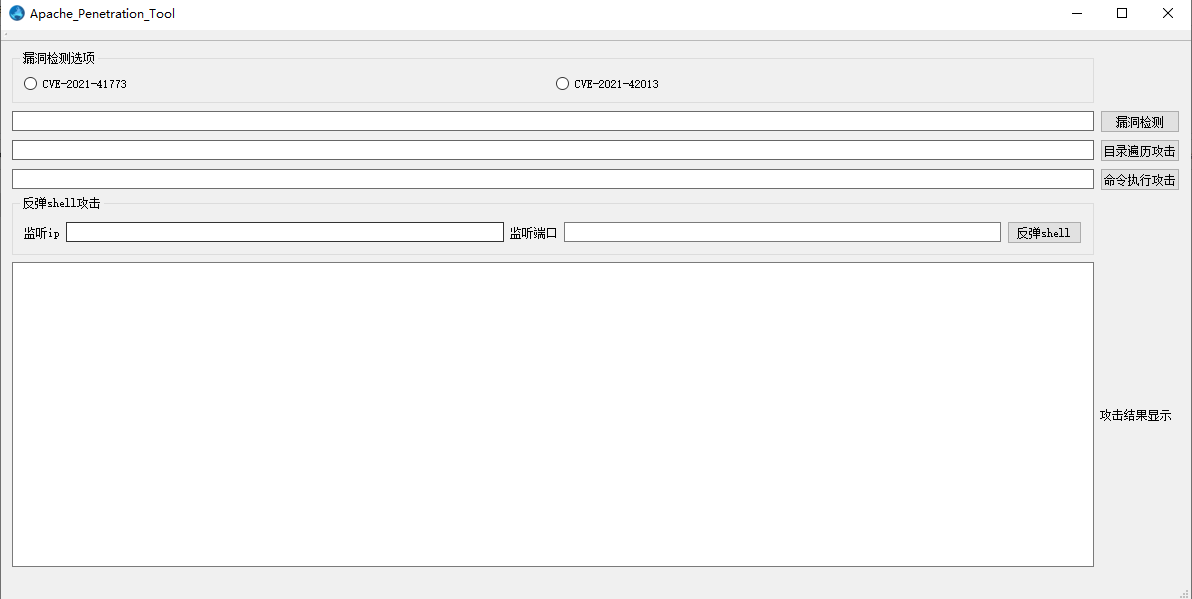 wangfly-me/apache_penetration_tool
CVE-2021-41773&CVE-2021-42013图形化漏洞检测利用工具
 seep1959/njutils
A client and chat program for njrat 0.6.4, 0.7d, and 0.7d golden edition.
 kagura-maru/cve-2021-40444-poc
An attempt to reproduce Microsoft MSHTML Remote Code Execution (RCE) Vulnerability and using Metasploit Framework.
 exploit-install/cve-2017-0199
Exploit toolkit CVE-2017-0199 - v2.0 is a handy python script which provides a quick and effective way to exploit Microsoft RTF RCE. It could…
 killswitch-gui/flask_heroku_redirector
flask heroku C2 redirector template








