
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended

 blazeinfosec/bt2
Blaze Telegram Backdoor Toolkit is a post-exploitation tool that leverages the infrastructure of Telegram as a C&C
 kcarretto/paragon
Red Team engagement platform with the goal of unifying offensive tools behind a simple UI
 ivan-sincek/powershell-reverse-tcp
PowerShell scripts for communicating with a remote host.
 nccgroup/pybeacon
A collection of scripts for dealing with Cobalt Strike beacons in Python
 twosevenonet/injectsetconsole
Proof of Concept for Process Code Injection Without Using WriteProcessMemory
 shadow-workers/shadow-workers
Shadow Workers is a free and open source C2 and proxy designed for penetration testers to help in the exploitation of XSS and malicious Service…
 zcgonvh/cve-2020-17144
weaponized tool for CVE-2020-17144
 ruped24/killchain
A unified console to perform the "kill chain" stages of attacks.
 noahoksuz/osripper
AV evading cross platform Backdoor and Crypter Framework with a integrated lightweight webUI
 0x09al/dns-persist
DNS-Persist is a post-exploitation agent which uses DNS for command and control.
 redsiege/persistassist
Fully modular persistence framework
 dazzyddos/lsawhisper-bof
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…
 devzero-security/redstackpro
Compose red team infrastructure and Active Directory ranges on a canvas, then compile to a complete Terraform and Ansible working directory you run…
 syss-research/outis
outis is a custom Remote Administration Tool (RAT) or something like that. It was build to support various transport methods (like DNS) and platforms…
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 brav0hax/smbexec
Rapid psexec-style attack tool using Samba for remote command execution, credential dumping, and lateral movement across Windows networks with hash…
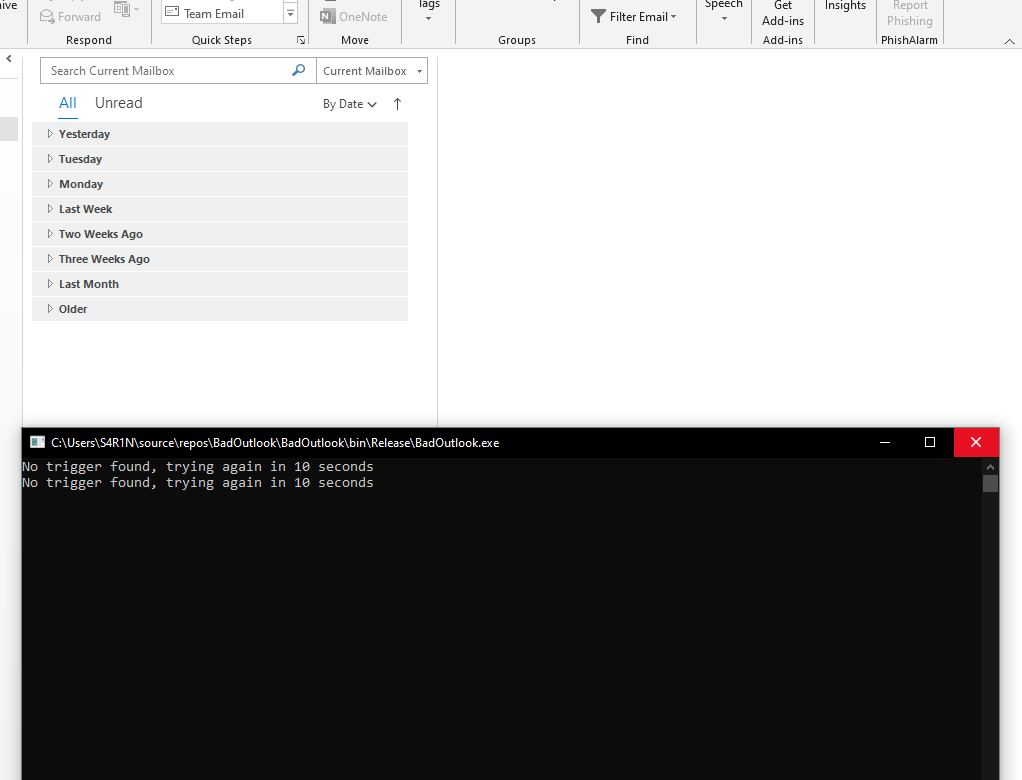 aahmad097/badoutlook
Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
 byt3bl33d3r/pymalleablec2
Python interpreter for Cobalt Strike Malleable C2 Profiles. Allows you to parse, build and modify them programmatically.








