
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended
 outflanknl/findobjects-bof
A Cobalt Strike Beacon Object File (BOF) project which uses direct system calls to enumerate processes for specific loaded modules or process handles.
 mythicagents/xenon
A Mythic agent for Windows written in C
 capt-meelo/beaconator
A beacon generator using Cobalt Strike and a variety of tools.
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
 maherazzouzi/cve-2022-37706-lpe-exploit
A reliable exploit + write-up to elevate privileges to root. (Tested on Ubuntu 22.04)
 reveng007/sharpgmailc2
Our Friendly Gmail will act as Server and implant will exfiltrate data via smtp and will read commands from C2 (Gmail) via imap protocol
 kraken-ng/kraken
Modular multi-language webshell for web post-exploitation with PHP, JSP, and ASPX agents. Features defense evasion, C2 mode, and Python-based core…
 a-d-team/sharpmemshell
.NET in-memory webshell (memshell) payloads implemented via HttpListener and VirtualPath, compatible with the Godzilla 4.01 post-exploitation…
 scorpioneslabs/dvs
D(COM) V(ulnerability) S(canner) AKA Devious swiss army knife - Lateral movement using DCOM Objects
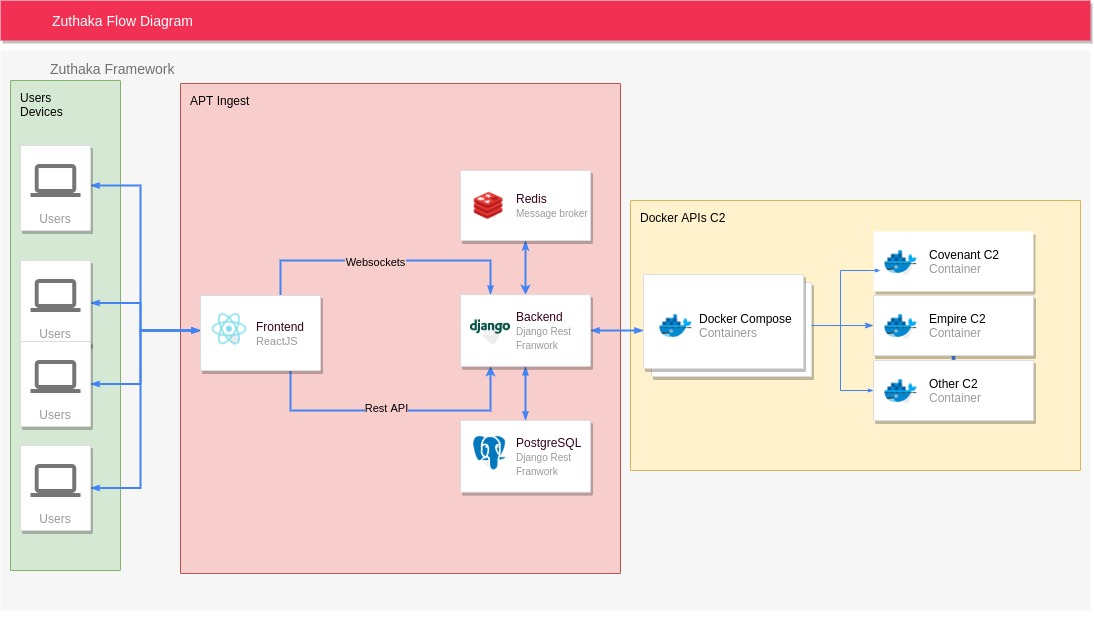 pucarasec/zuthaka
Open-source C2 integration framework providing a unified web interface for managing multiple command-and-control instances, listeners, agents, and…
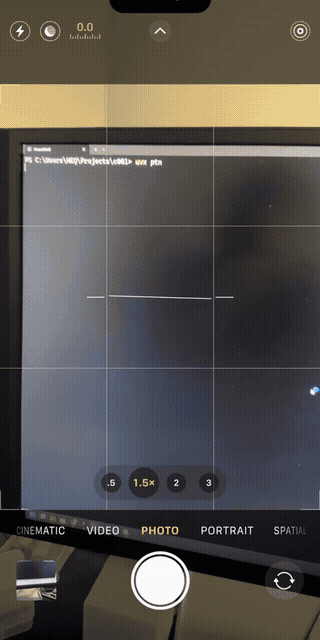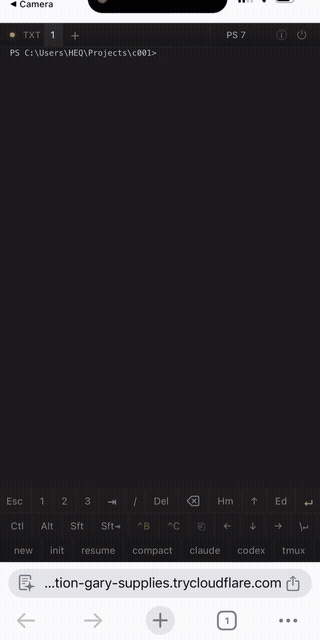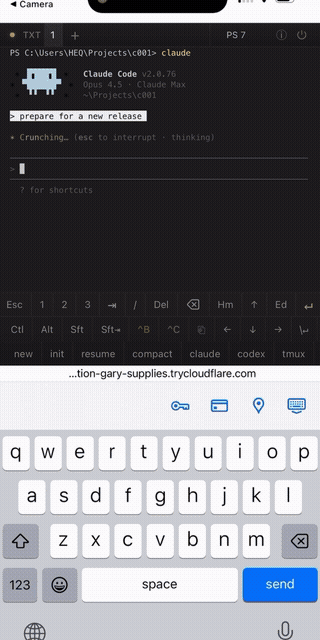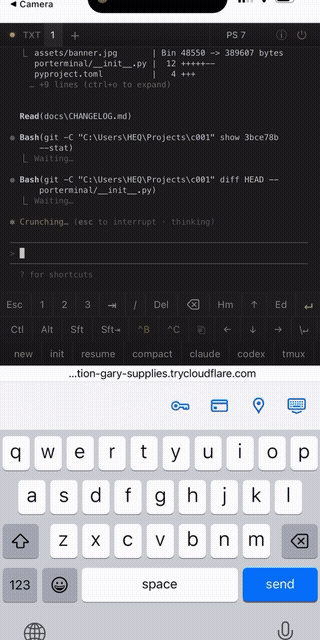 lyehe/porterminal
Quick n' dirty web/mcp terminal tunneling your phone & pc
 skelsec/evilrdp
RDP client with extended control for automated mouse, keyboard, and clipboard manipulation, file transfer, SOCKS proxy, and remote command execution…
 kleiton0x00/redditc2
Abusing Reddit API to host the C2 traffic.
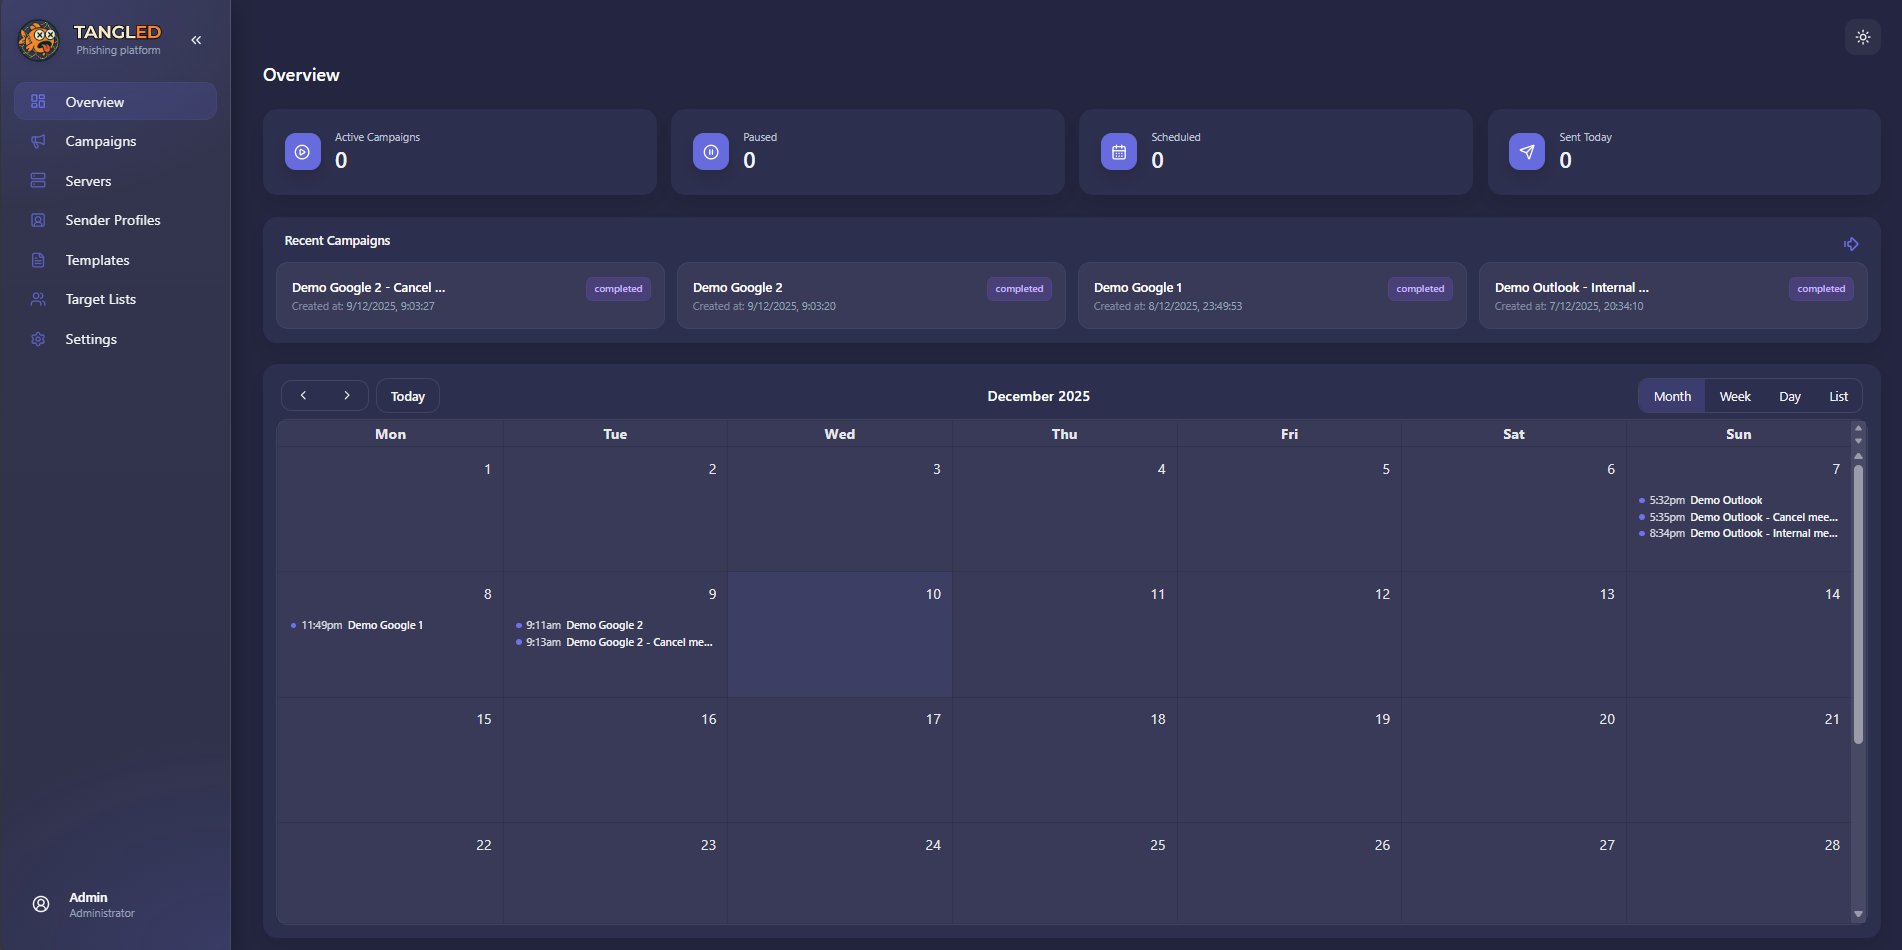 ineesdv/tangled
Open-source offensive security platform for conducting phishing campaigns that weaponizes iCalendar automatic event processing.
 paranoidninja/brute-ratel-c4-community-kit
This repository contains scripts, configurations and deprecated payload loaders for Brute Ratel C4 (https://bruteratel.com/)
 geeoon/dns-tunnel-keylogger
Keylogging server and client that uses DNS tunneling/exfiltration to transmit keystrokes through firewalls.
 thatcherclough/betterbackdoor
A backdoor with a multitude of features.
 m8sec/activereign
A Network Enumeration and Attack Toolset for Windows Active Directory Environments.








