
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended
 jas502n/cve-2020-14882
Weblogic CVE-2020-14882 unauthorized RCE exploit with patch bypass, command execution, and webshell deployment for penetration testing.
 jymcheong/autottp
Automated Tactics Techniques & Procedures
 metarget/k0otkit
k0otkit is a universal post-penetration technique which could be used in penetrations against Kubernetes clusters.
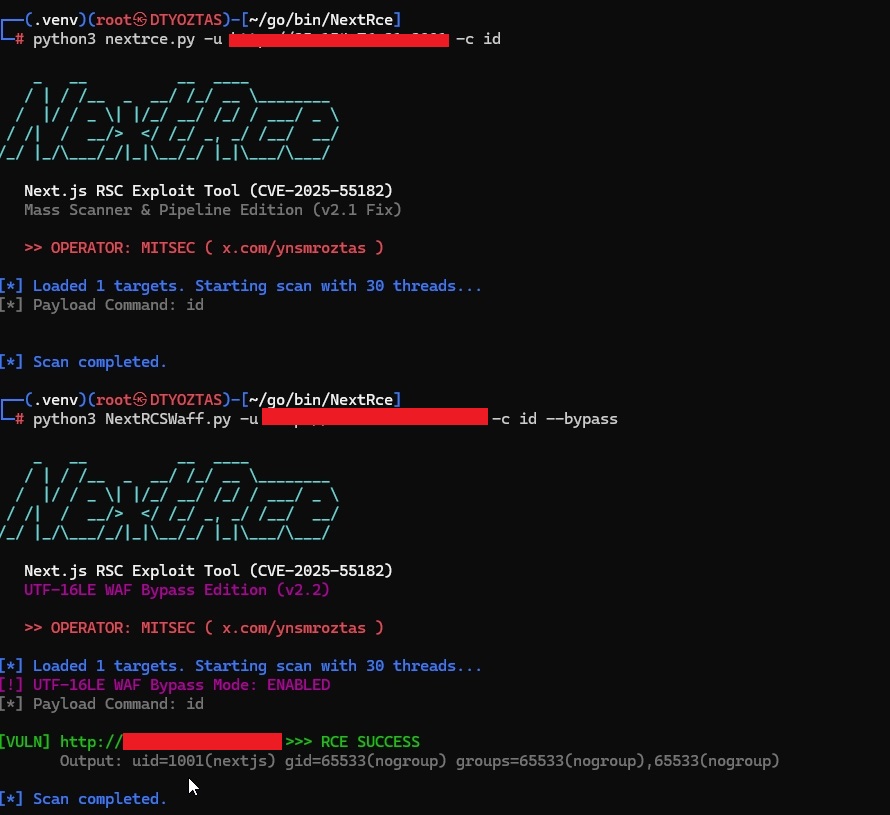 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
 safebreach-labs/sireprat
Remote Command Execution as SYSTEM on Windows IoT Core (releases available for Python2.7 & Python3)
 xm0kht4r/av-edr-killer
AV/EDR processes termination by exploiting a vulnerable driver (BYOVD)
 mr-in4inci3le/sliver-gui
A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…
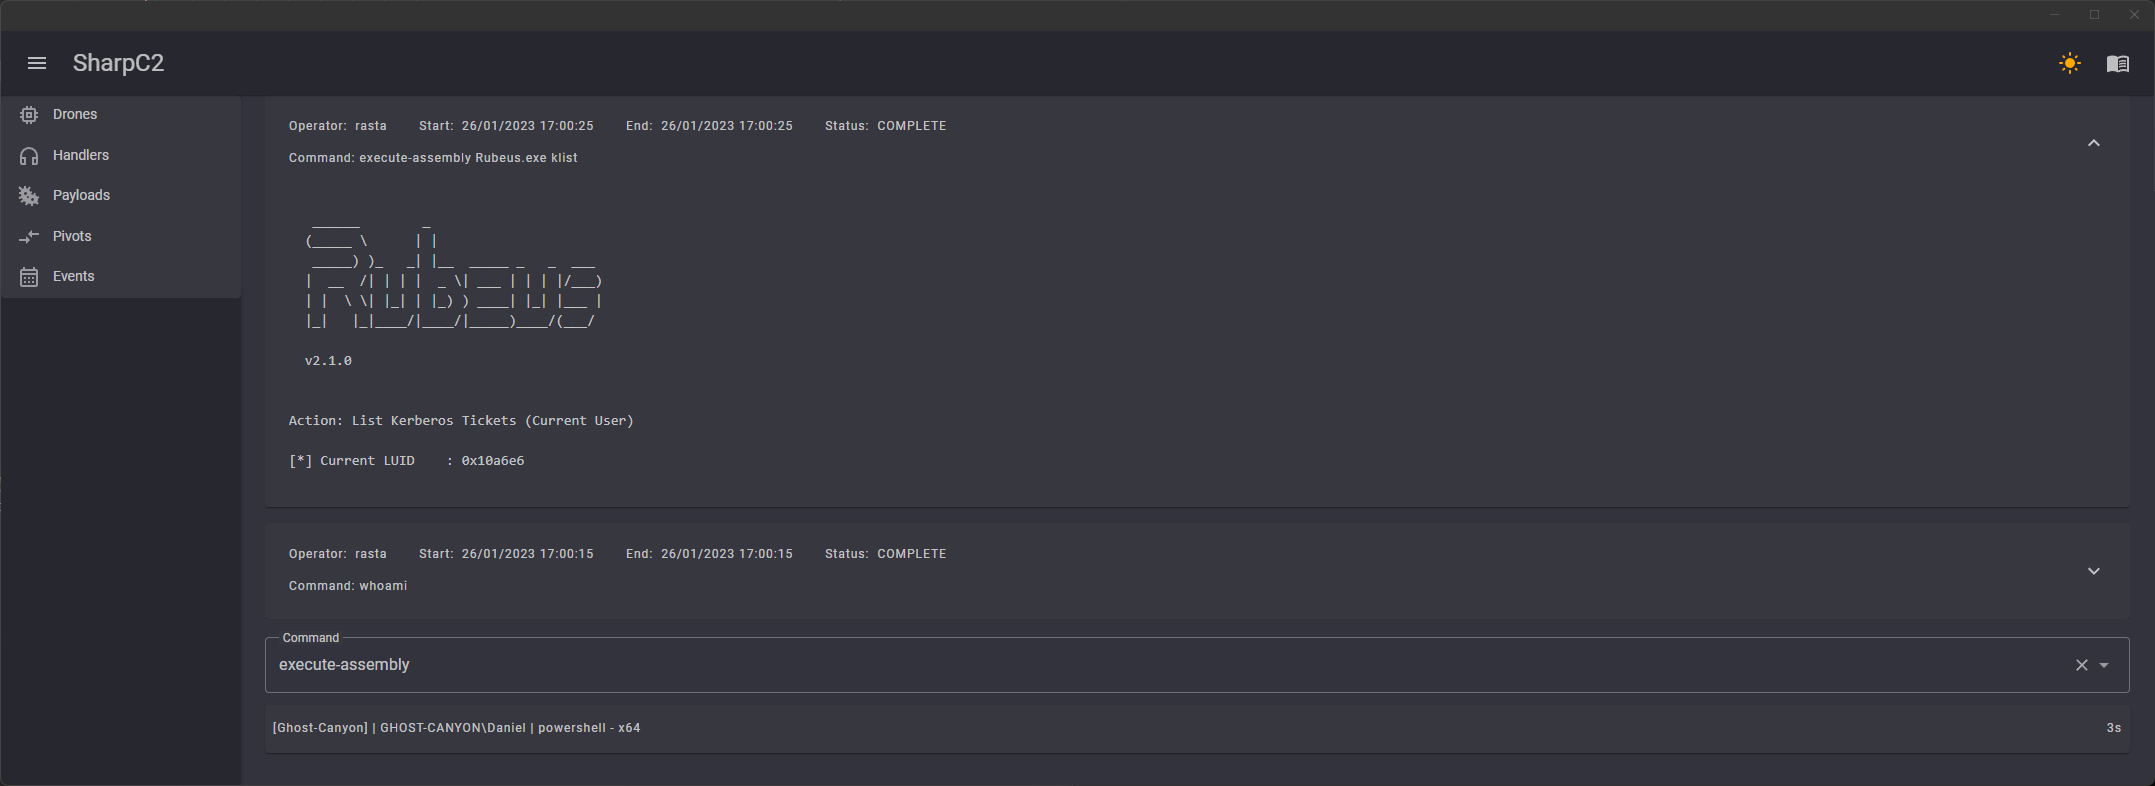 rasta-mouse/sharpc2
Command and Control Framework written in C#
 ryhanson/externalc2
A library for integrating communication channels with the Cobalt Strike External C2 server
 yt1g3r/cve-2020-0688_exp
CVE-2020-0688_EXP Auto trigger payload & encrypt method
 xorrior/raven
CobaltStrike External C2 for Websockets
 xtr4nge/fruityc2
FruityC2 is a post-exploitation (and open source) framework based on the deployment of agents on compromised machines. Agents are managed from a web…
 rasta-mouse/misctools
Miscellaneous Tools
 abelche/evil_minio
EXP for CVE-2023-28434 MinIO unauthorized to RCE
 loosehose/silentbutdeadly
SilentButDeadly is a network communication blocker specifically designed to neutralize EDR/AV software by preventing their cloud connectivity using…
 seastorm/puttyrider
Hijack Putty sessions in order to sniff conversation and inject Linux commands.
 zibility/remote
参考Gh0st源码,实现的一款PC远程协助软件,拥有远程Shell、文件管理、桌面管理、消息发送等功能。
 matheuzsecurity/furtex
Post-exploitation and evasion research toolkit for Linux.








