
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended
 frkngksl/nimexec
Fileless Command Execution for Lateral Movement in Nim
 voulnet/cve-2017-8759-exploit-sample
Running CVE-2017-8759 exploit sample.
 al1ex/cve-2021-22205
CVE-2021-22205& GitLab CE/EE RCE
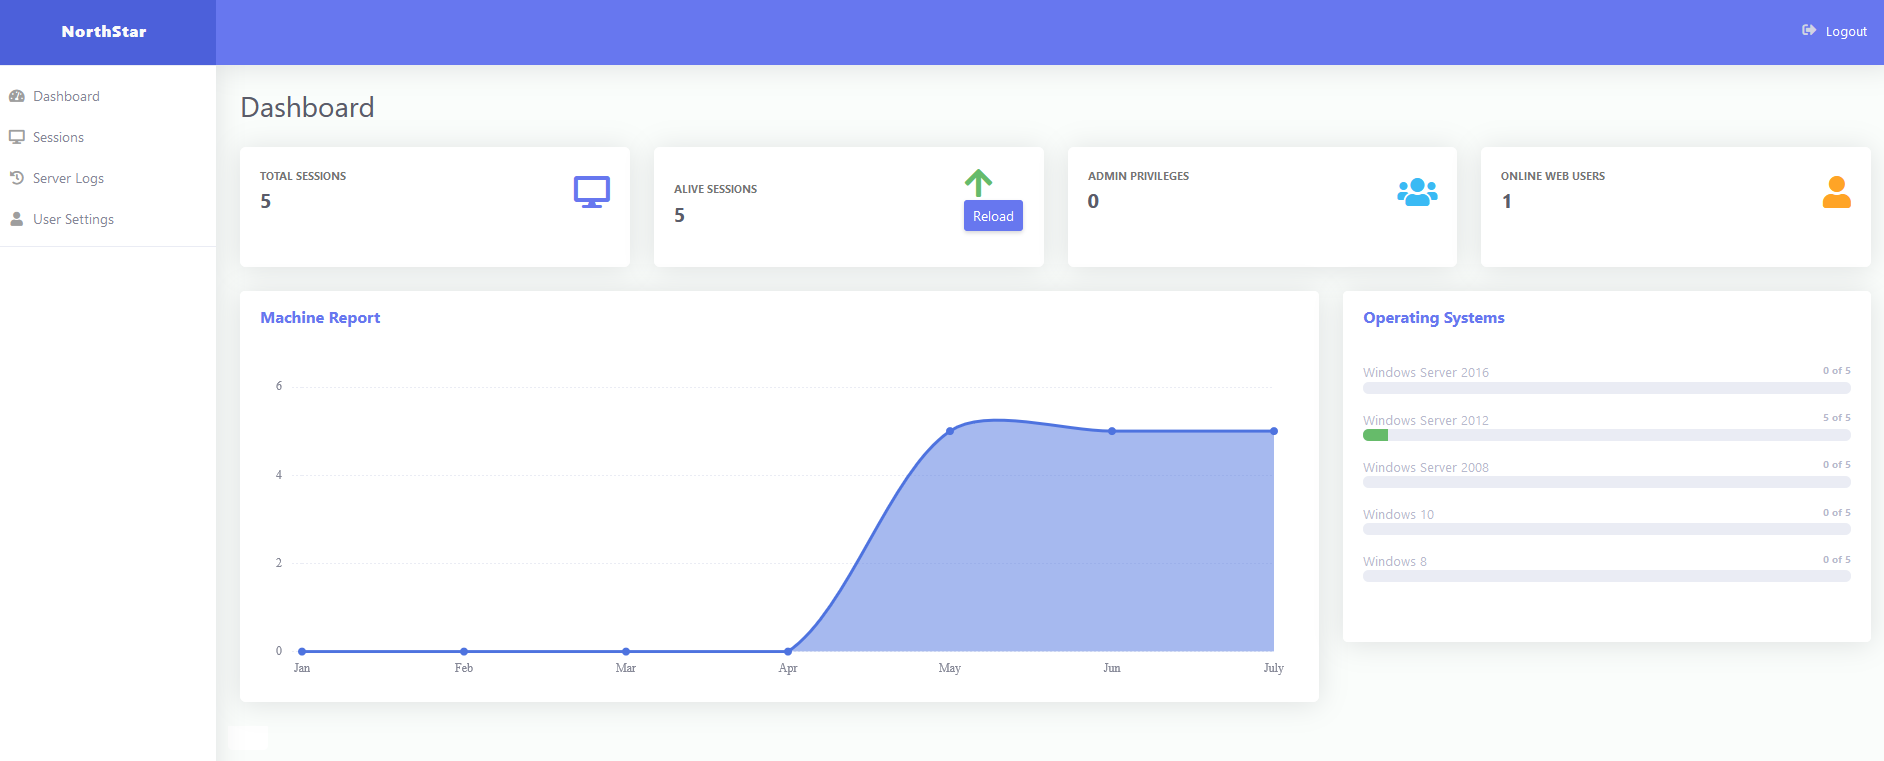 eng1ndes/northstarc2
Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…
 imcpwn/browser-backdoor
BrowserBackdoor is an Electron Application with a JavaScript WebSocket Backdoor and a Ruby Command-Line Listener
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 leo4j/amnesiac
PowerShell-based post-exploitation framework for lateral movement in Active Directory environments. Executes in-memory with named-pipe command…
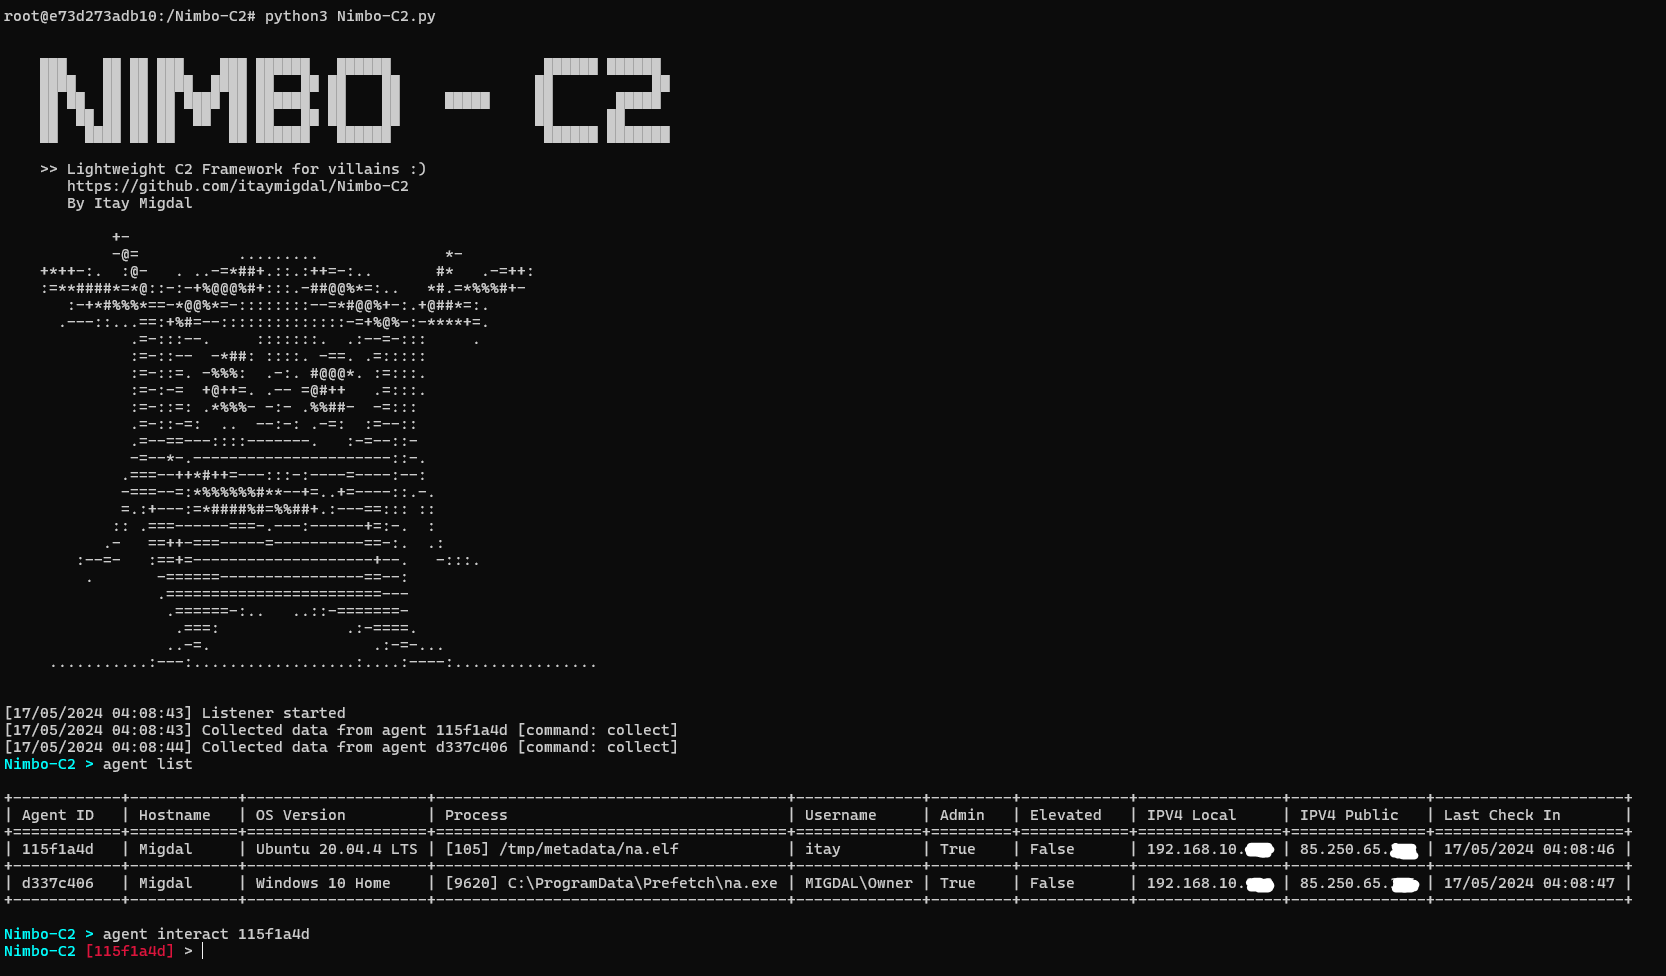 itaymigdal/nimbo-c2
Nimbo-C2 is yet another (simple and lightweight) C2 framework
 d00mfist/mystikal
macOS Initial Access Payload Generator
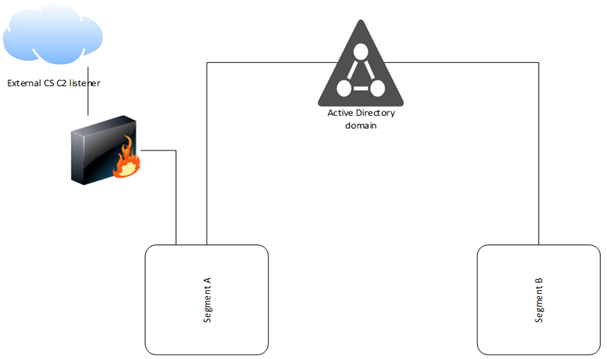 fox-it/ldapfragger
C2 tool routing Cobalt Strike beacon data over LDAP user attributes for stealthy command-and-control in segmented networks.
 jas502n/cve-2020-14882
Weblogic CVE-2020-14882 unauthorized RCE exploit with patch bypass, command execution, and webshell deployment for penetration testing.
 jymcheong/autottp
Automated Tactics Techniques & Procedures
 metarget/k0otkit
k0otkit is a universal post-penetration technique which could be used in penetrations against Kubernetes clusters.
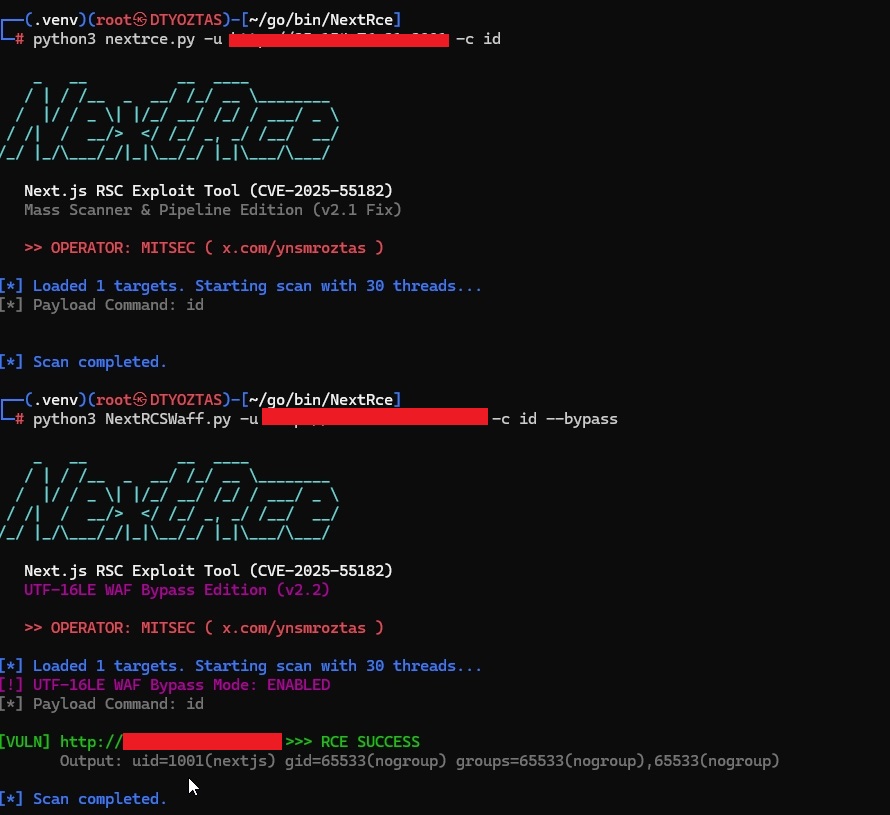 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
 safebreach-labs/sireprat
Remote Command Execution as SYSTEM on Windows IoT Core (releases available for Python2.7 & Python3)
 xm0kht4r/av-edr-killer
AV/EDR processes termination by exploiting a vulnerable driver (BYOVD)
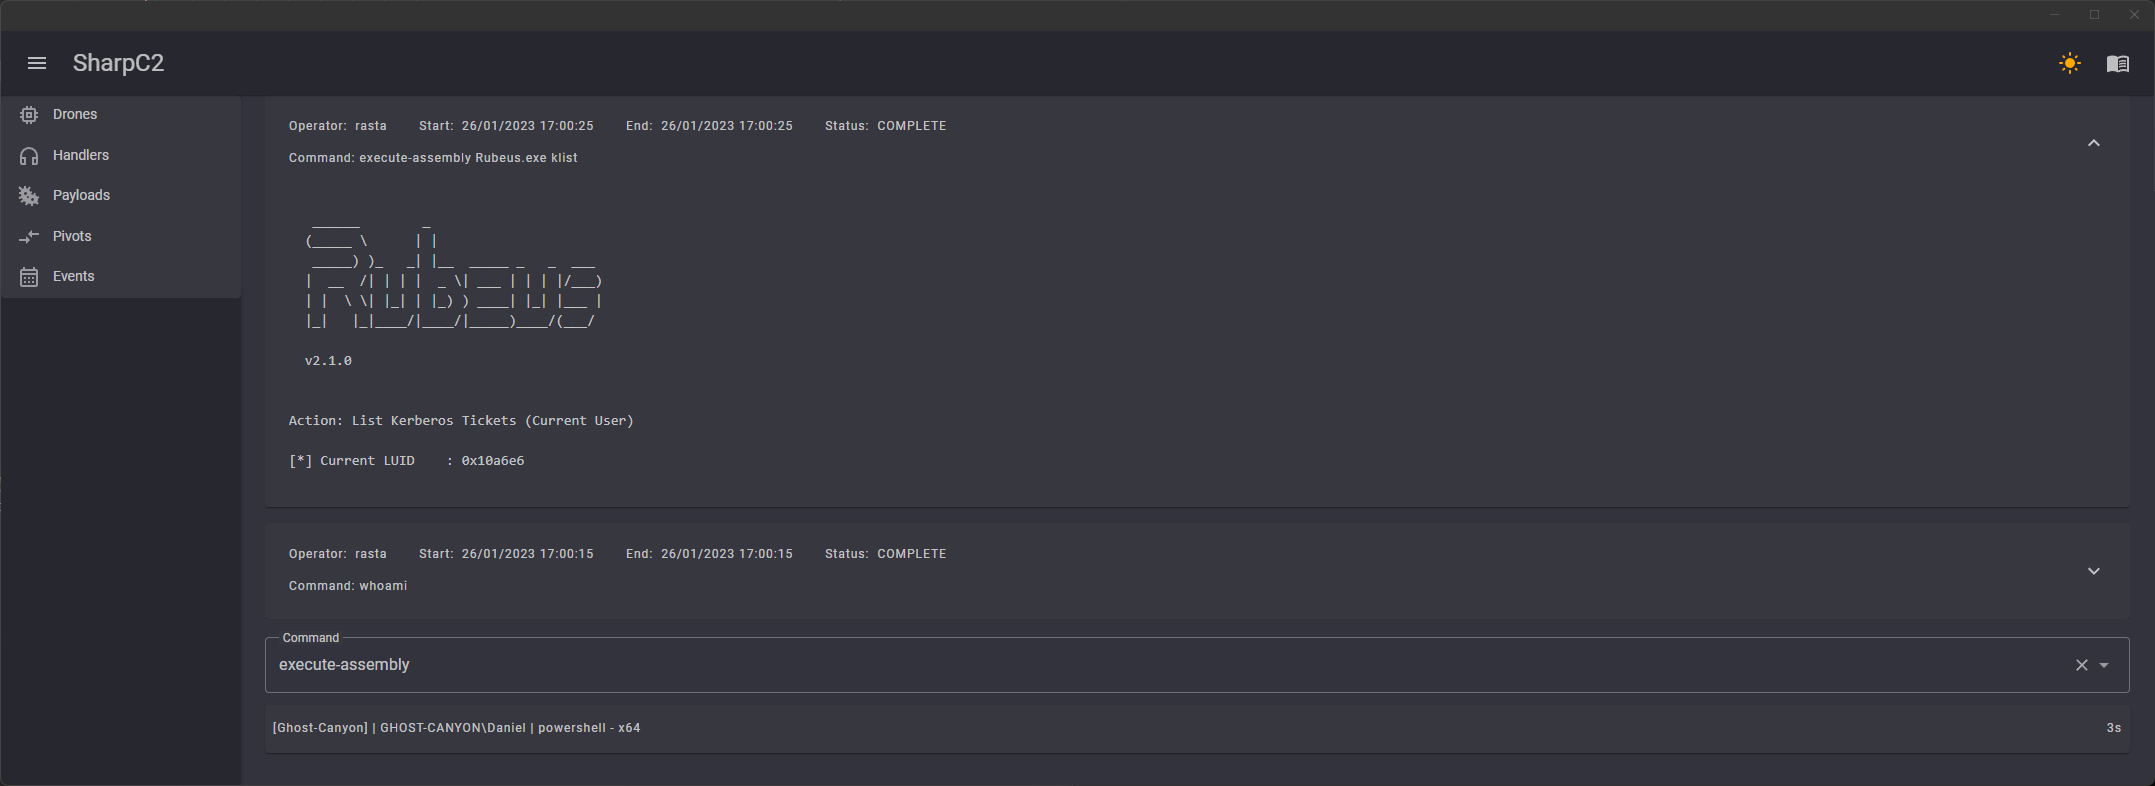 rasta-mouse/sharpc2
Command and Control Framework written in C#
 ryhanson/externalc2
A library for integrating communication channels with the Cobalt Strike External C2 server








