#1
 d0n601/cve-2025-13374
Kalrav AI Agent <= 2.3.3 - Unauthenticated Arbitrary File Upload via kalrav_upload_file AJAX Action
 l4f2s4/cve-2025-49113_exploit_cookies
Authenticated remote code execution exploit for Roundcube Webmail (CVE-2025-49113) via insecure deserialization. Includes session injection, gadget…
 mbanyamer/cve-2026-25546-godot-mcp-0.1.1-os-command-injection
Proof-of-concept exploit for CVE-2026-25546, demonstrating OS command injection in godot-mcp via malicious projectPath parameter, with Python PoC and…
 lukasz-rybak/cve-2026-22692
CVE-2026-22692 - Critical Twig Sandbox Bypass via collect()->mapInto() allowing RCE/LFI/XXE in October CMS
 open-flaw/cve-2025-23061
CVE-2025-23061 - Mongoose Command Injection
 sudotom/rcno-reviews
Recencio Book Reviews - WordPress plugin for managing book reviews. Originally created by Kemory Grubb. Security-patched fork resolving…
 before-rain/cve-2025-50472
Proof-of-concept exploit for CVE-2025-50472, a deserialization RCE vulnerability in ModelScope ms-swift's ModelFileSystemCache via malicious .mdl…
 sudo-wp/sudowp-clickfunnels-zurich
A security-patched fork of the legacy ClickFunnels Classic WordPress plugin. Fixes critical Stored XSS vulnerabilities (CVE-2022-4782) while…
 khoatran107/cve-2025-38001
C-based proof-of-concept exploit for CVE-2025-38001, demonstrating vulnerability exploitation and code analysis for security research.
 sahiloj/cve-2025-5352
Demonstrates a stored XSS vulnerability in lunary-ai/lunary's Analytics component, where unsanitized NEXT_PUBLIC_CUSTOM_SCRIPT injection leads to…
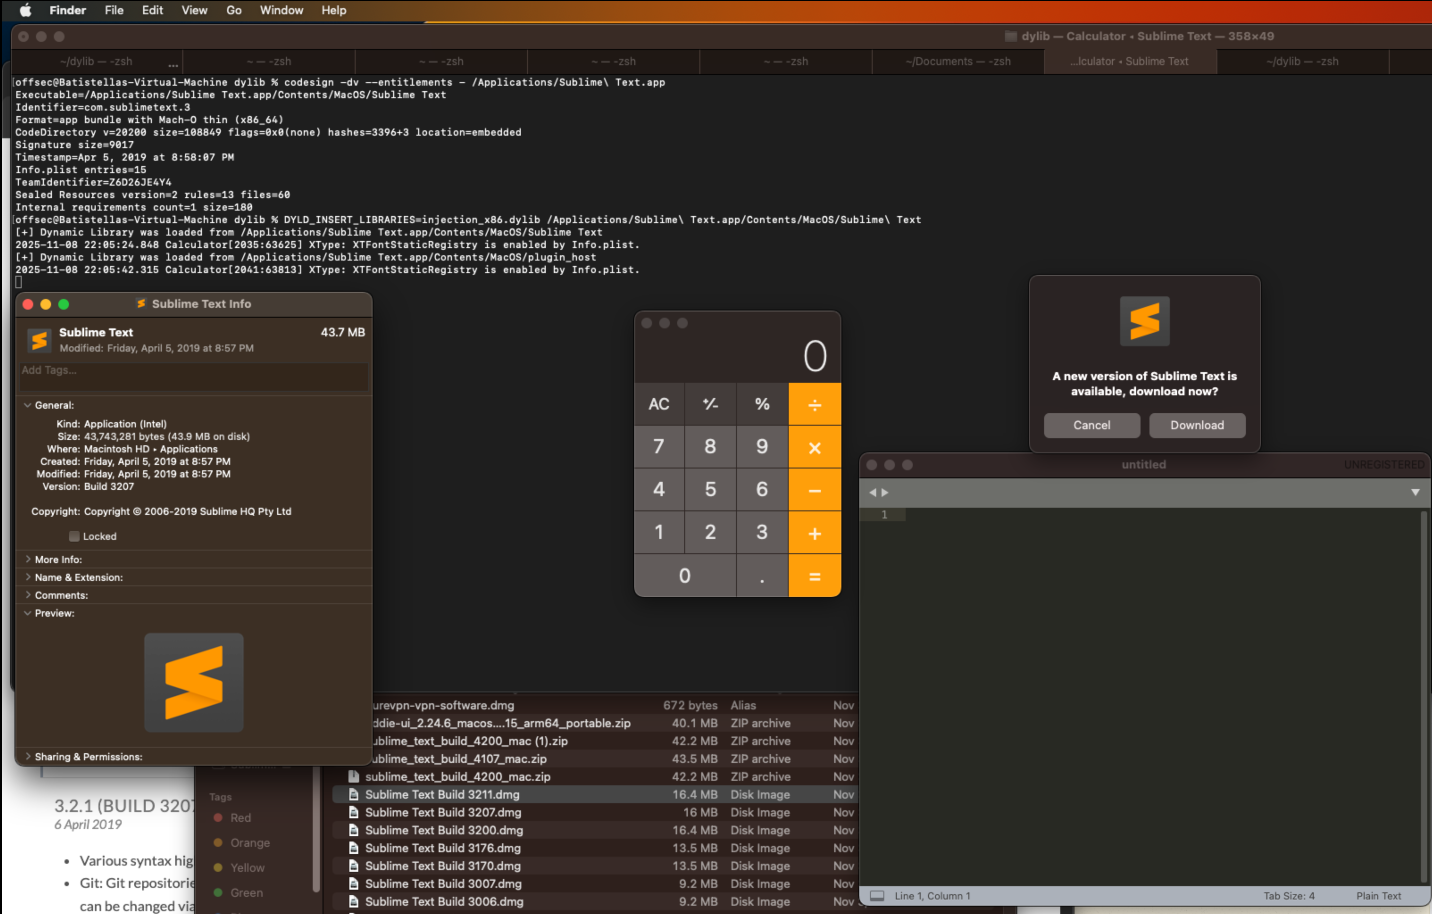 vinicius-batistella/cve-2025-65741
Proof-of-concept for CVE-2025-65741 demonstrating dylib injection in Sublime Text 3 on macOS via unsigned code, with a compiled .dylib payload and…
 gmh5225/evmbench-certora-agent-harness
Iterative agent harness that uses LLMs and Certora Prover to generate and refine smart-contract CVL specs, feeding verifier output back until success…
 garethmsheldon/react2shell-cve-2025-55182-detector
Multi-language detection scripts for CVE-2025-55182 (React2Shell) that scan package.json files to identify vulnerable React dependency versions and…
 bitt0n/cve-2026-0766
Proof-of-concept exploit for CVE-2026-0766, a remote code execution vulnerability in OpenWebUI via tool code injection. Includes command execution,…
 thekamran/cve-2025-55182-proof-of-concept
Proof-of-Concept exploit for CVE-2025-55182, demonstrating prototype pollution leading to remote code execution in server-side rendering…
 ducducuc111/cve-2025-55182-poc
Proof-of-concept exploit for CVE-2025-55182, demonstrating remote code execution via prototype chain vulnerability in React Server Components.…
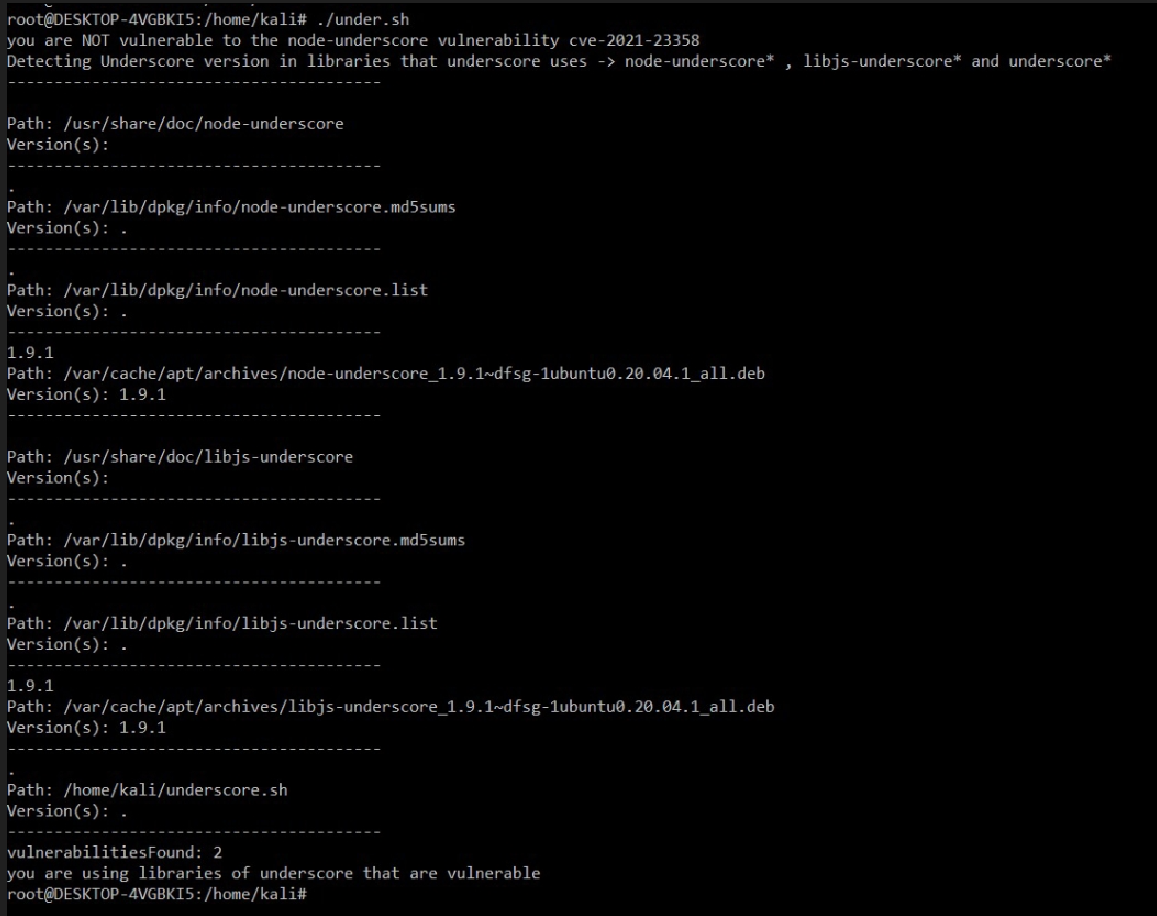 ekamsinghwalia/detection-script-for-cve-2021-23358
Detection script for cve-2021-23358