
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended
 sassoftware/jackson
This repository provides a comprehensive security remediation of denial-of-service and allocation of resources without limits or throttling security…
 kang8/cve-2021-43503
Proof-of-concept exploit for CVE-2021-43503, a Laravel deserialization RCE vulnerability. Includes PHP POP chain generation and HTTP-based payload…
 timtimxs/cve-2026-51947-advisory
Pivotal CRM's patch for an initial deserialization vulnerability was incomplete. The fix switched from BinaryFormatter to JSON.NET but left…
 shadowsock5/shardingsphere_cve-2020-1947
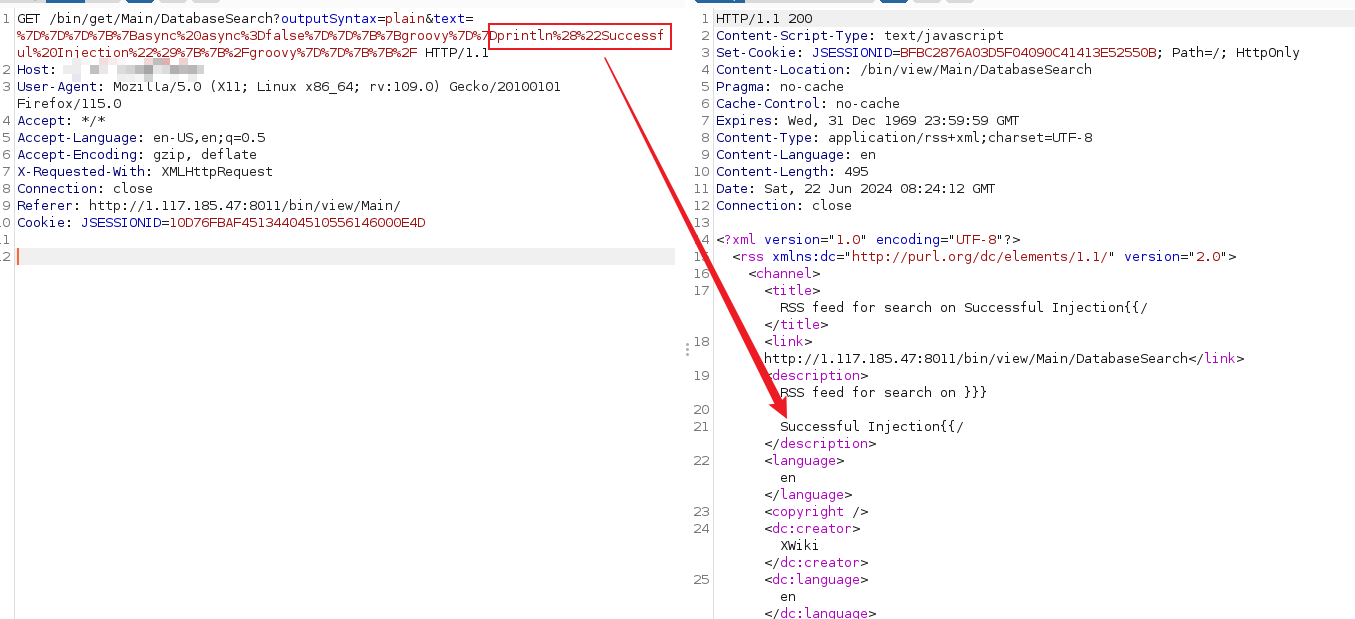 nanowraith/cve-2024-31982
Proof-of-concept exploit for CVE-2024-31982: Java Server-Side Template Injection (SSTI) leading to remote code execution via Groovy payload injection.
 vm2mv/tinyxml
TinyXML 2.6.2 with fixes for CVE-2021-42260 and CVE-2023-34194
 ahmedreda38/cve-2025-47273-poc
CVE-2025-47273 is a high-severity path traversal vulnerability in the setuptools library ,specifically version 78.1.0 .
 y0s9/cve-2021-3129
CVE-2021-3129-Laravel Debug mode 远程代码执行漏洞
 zhixiangyao/cve-2025-66478-exploit-poc
Proof-of-concept exploit demo for CVE-2025-66478 using Node.js
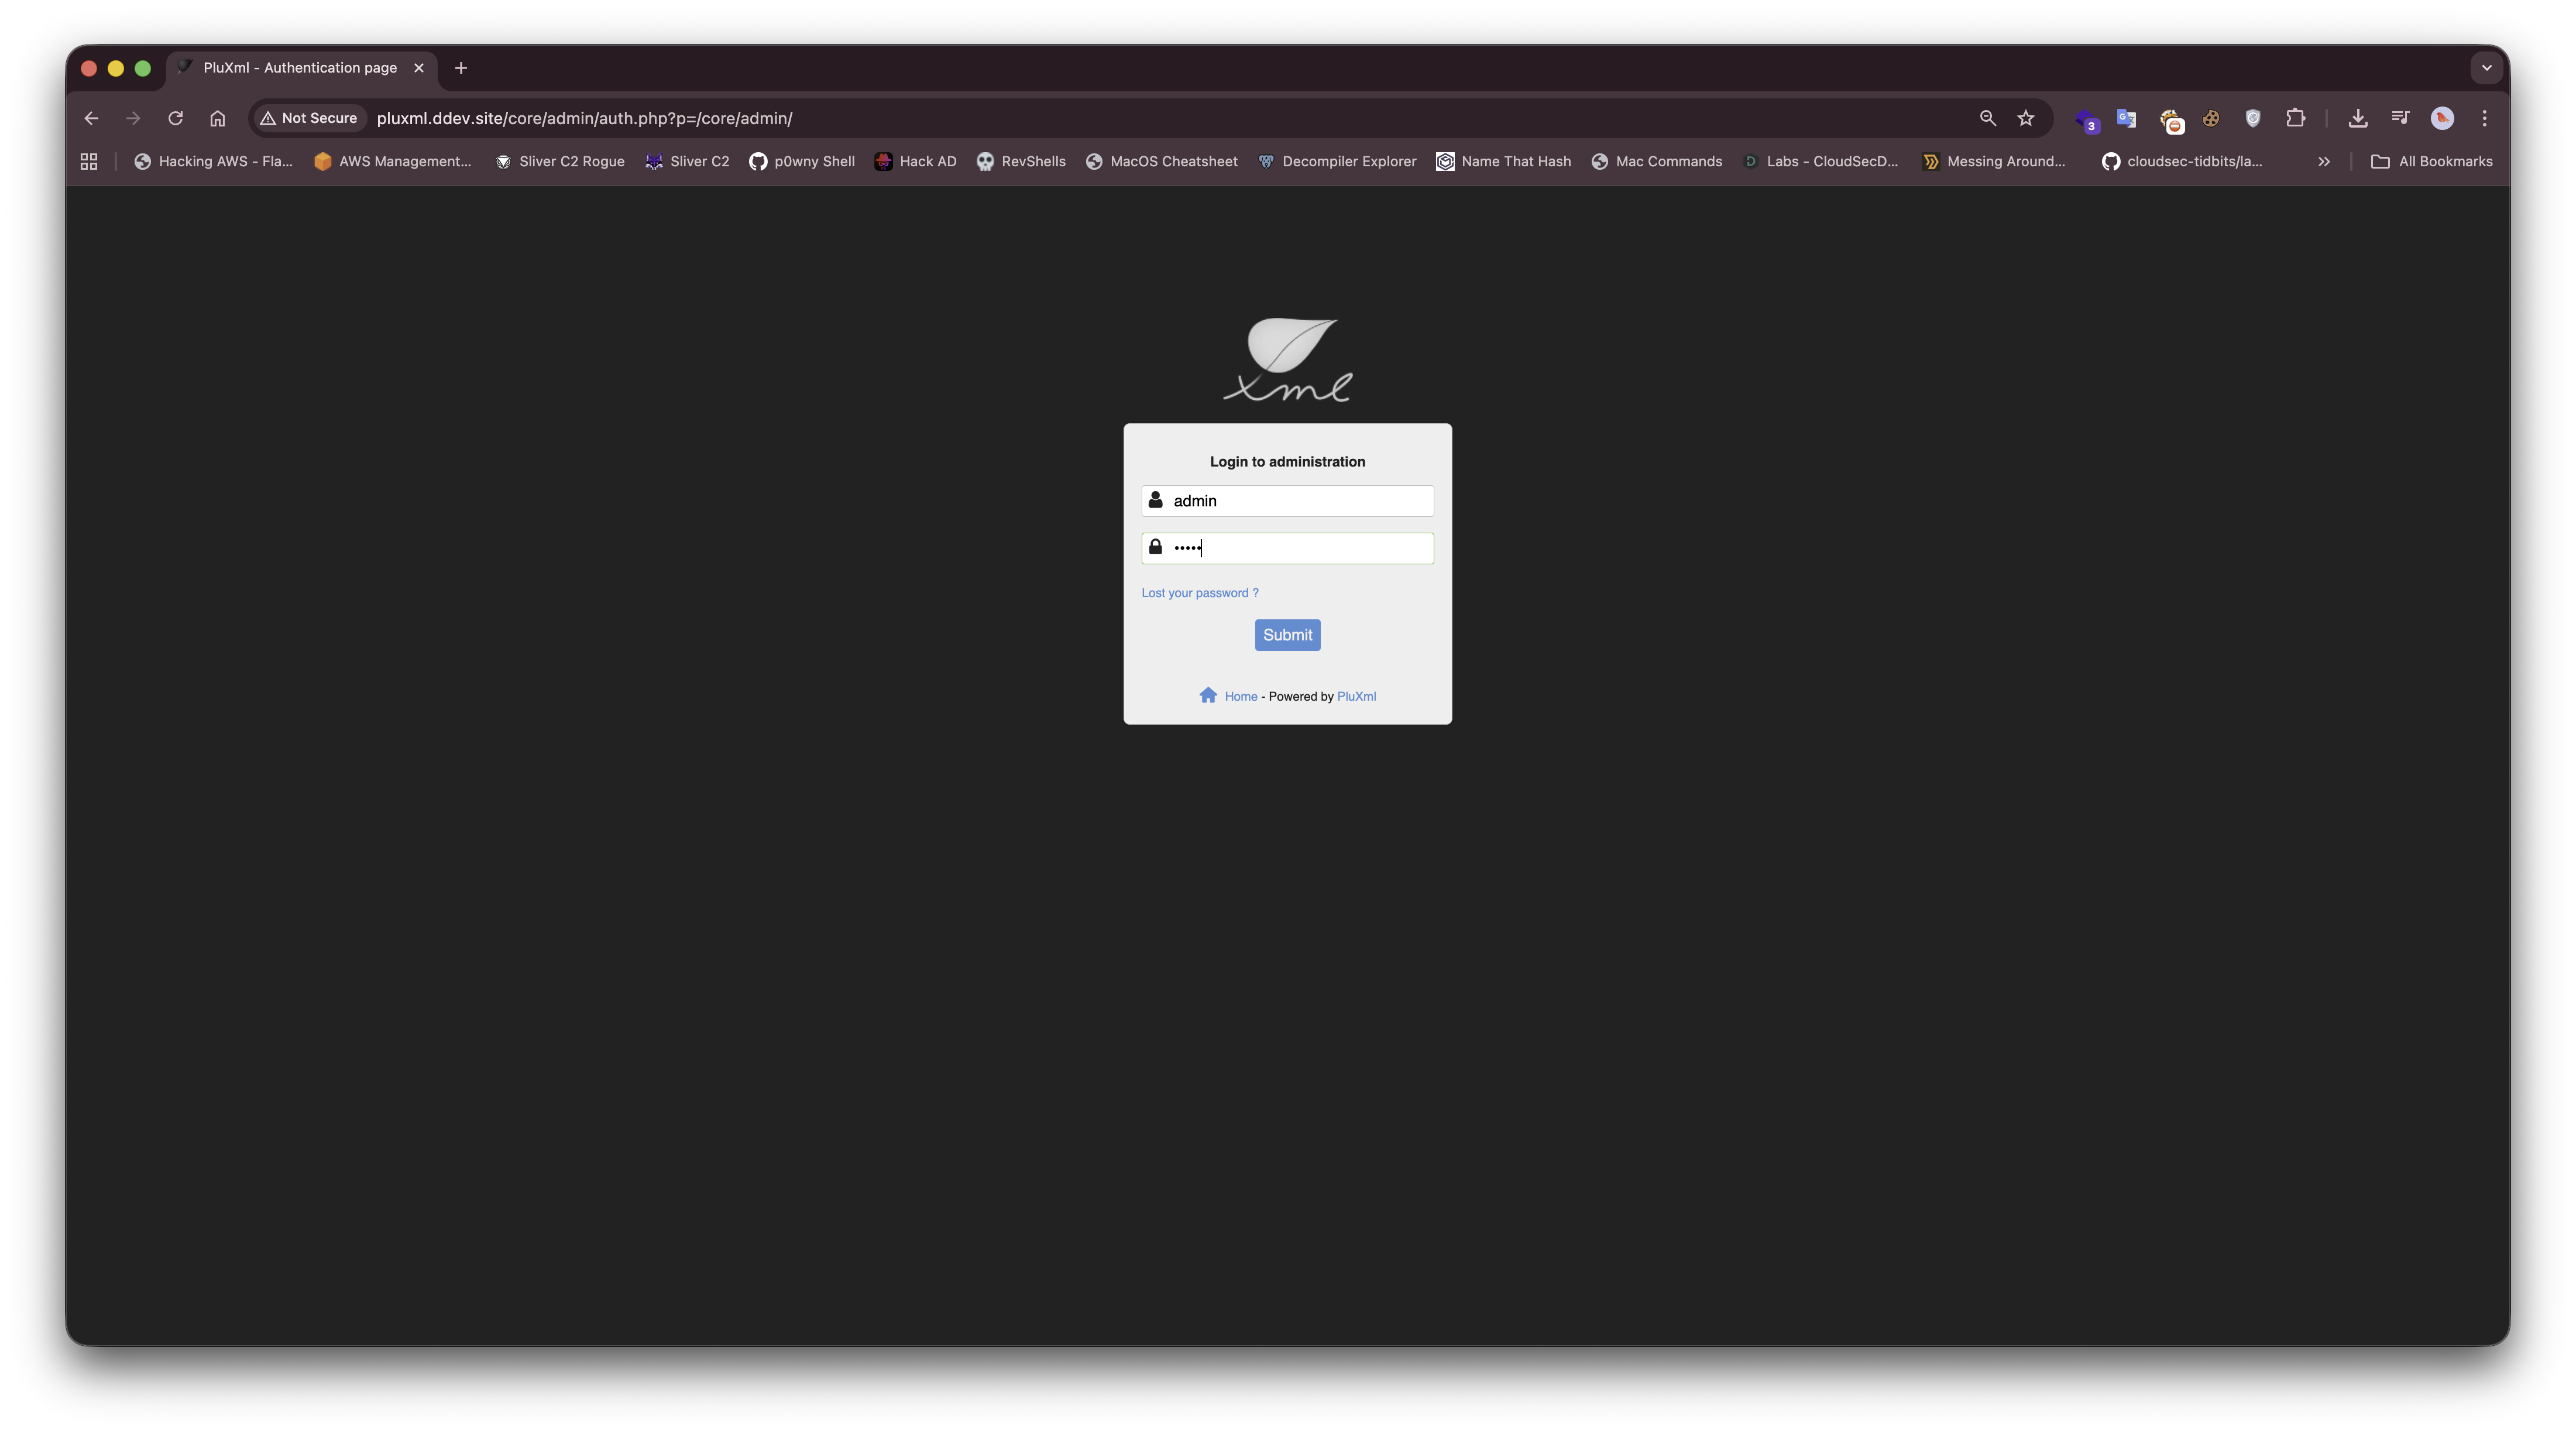 rajchowdhury240/cve-2025-67435
A critical Remote Code Execution (RCE) vulnerability has been identified in PluXML CMS version 5.8.22. This vulnerability allows authenticated…
 mehdiboukhobza/sandbox_cve-2021-23358
 at190510-cuong/cve-2025-64087-ssti-
CVE-2025-64087 (SSTI)
 ronf98/cve-2024-11972-poc
CVE-2024-11972 in Hunk Companion <1.9.0 allows unauthenticated attackers to exploit insecure REST API endpoints and install vulnerable plugins,…
 randomrobbiebf/cve-2024-56058
VRPConnector <= 2.0.1 - Unauthenticated PHP Object Injection
 jvr2022/cve-2026-29786
Proof-of-concept demonstrating a hardlink path traversal in the tar npm package, allowing overwrite of files outside the extraction directory via…
 fatkz/cve-2025-24813
Proof-of-concept exploit for CVE-2025-24813, achieving remote code execution on Apache Tomcat via session deserialization and partial PUT requests.
 halcy0nic/cve-2023-40296
Proof of Concept for CVE-2023-40296
 randomrobbiebf/cve-2024-3553
CVE-2024-3553: Tutor LMS <= 2.6.2 - Missing Authorization vulnerability allowing authenticated attackers to enable user registration








