
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended
 roninforge/roninforge-hono
Cursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…
 roninforge/roninforge-angularjs-migration
AngularJS 1.x -> Angular 18 migration guidance for GitHub Copilot. Source-of-truth repo for…
 neimar47574/cve-2022-24087
Proof-of-concept exploit for CVE-2022-24086 and CVE-2022-24087, demonstrating pre-authentication remote code execution in Magento/Adobe Commerce via…
 bohemianhacks/cve-2024-21534-poc
Proof-of-concept exploit for CVE-2024-21534, a critical RCE in jsonpath-plus, demonstrating arbitrary code execution via the VM module and providing…
 cn016/dedecms-getshell-cve-2023-2928-
DedeCMS文件包含漏洞导致后台getshell(CVE-2023-2928)复现
 trinadh465/openssl-1_0_1g_cve-2015-3194
OpenSSL 1.0.1g source code snapshot, providing SSL/TLS and general-purpose cryptographic library with ciphers, digests, and X.509 certificate…
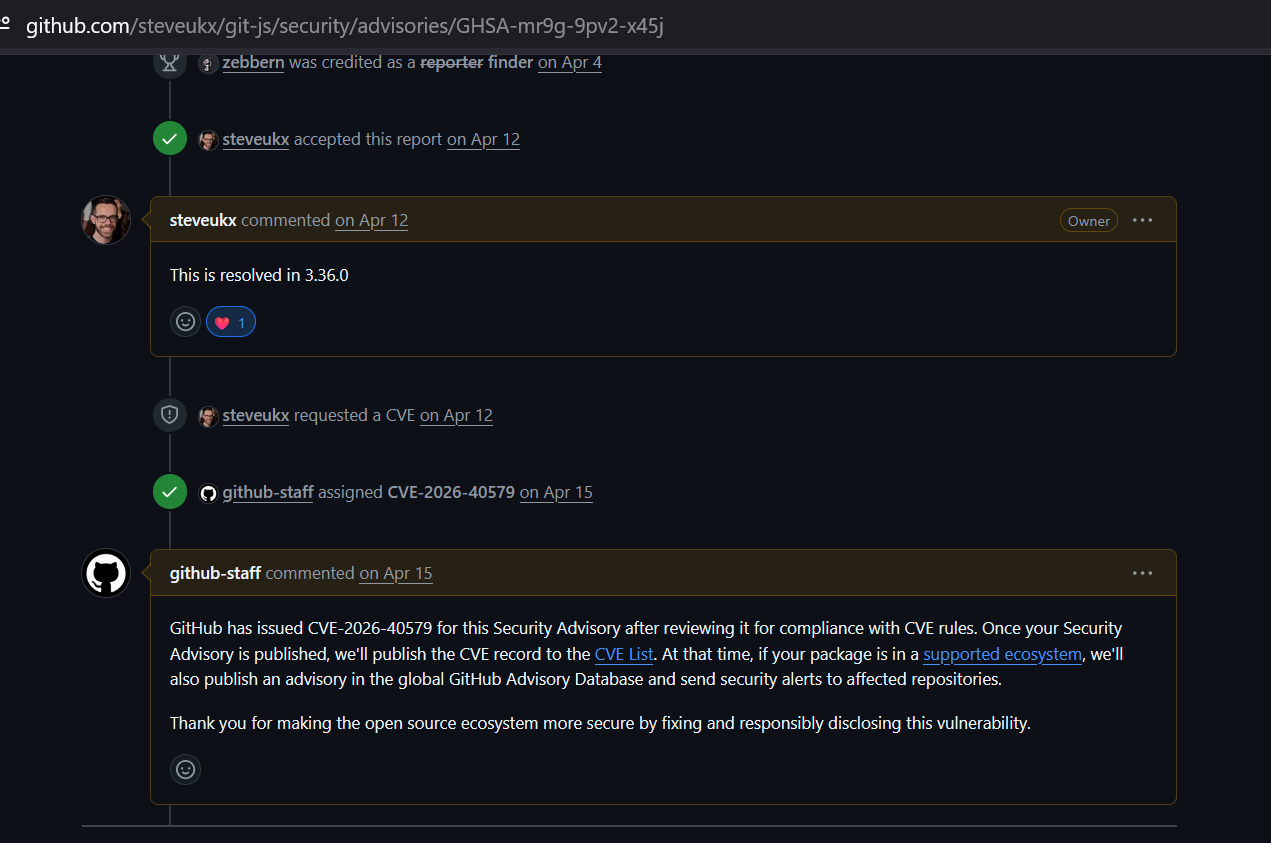 zebberncve/cve-2026-40579
Advisory for git-js ⌯⌲ 11 mill weekly downloads
 meslimohamedm22005188/path-traversal-cve-2026-14628
Educational reproduction of CVE-2026-14628 path traversal vulnerability with vulnerable and secure code examples, fix explanation, and runnable demos…
 az9713/cve-lite-on-pi
Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).
 trinadh465/frameworks_minikin_aosp10_r33-cve-2022-20473
Repository dedicated to CVE-2022-20473, a vulnerability in Android's Minikin library, providing patched source code for AOSP 10.
 hiteshgorana/susvibes-jupyter-server-cve-2026-35397
Benchmark task for reimplementing a masked path-resolution fix in Jupyter Server, with functional and hidden security tests to evaluate…
 danieltangnes/cve-2026-3888
Proof-of-concept exploit for CVE-2026-3888, written in C. Demonstrates vulnerability exploitation and binary-level attack techniques for security…
 dannyendortest/node-vulnerable
Synthetic demo target for EXPOSURE — CVE-2018-21268 (traceroute) + CVE-2018-3757 (pdf-image)
 quyt0/cve-2019-18935-exploit-study
In-depth study of CVE-2019-18935 affecting Telerik UI for ASP.NET AJAX. Covers .NET deserialization vulnerability, RadAsyncUpload handler, gadget…
 azilrababe/cve-2025-68613
Technical analysis of CVE-2025-68613, a critical Expression Injection vulnerability in n8n that allows authenticated attackers to achieve Remote Code…
 gogooma125732/cve-2016-5195
Non-weaponized CVE-2016-5195 (Dirty COW) analysis and validation harness with root-cause research, upstream patch review, and safe lab-only PoC for…
 r00tpgp/cve-2018-6574
Proof-of-concept exploit for CVE-2018-6574, demonstrating exploitation of a remote code execution vulnerability in Go-based applications.
 cyberdefenseinstitute/poc_cve-2016-2098_rails42
A PoC of CVE-2016-2098 (rails4.2.5.1 / view render)








