
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended

 randomrobbiebf/cve-2024-3553
CVE-2024-3553: Tutor LMS <= 2.6.2 - Missing Authorization vulnerability allowing authenticated attackers to enable user registration
 pa2sw0rd/exploit-cve-2025-55182-poc
This POC demonstrates CVE-2025-55182 using actual `[email protected]` vulnerable code.
 rickidevs/cve-2026-35570
Detailed write-up and proof-of-concept for CVE-2026-35570, a sandbox bypass in openclaude v0.1.7 allowing path traversal to read and write arbitrary…
 jun-5heng/cve-2022-22947
SpringCloudGatewayRCE / Code By:Jun_sheng
 edgarloyola/cve-2021-40904
Proof-of-concept for remote code execution in CheckMK Raw Edition 1.5.0–1.5.0p25 via misconfigured Dokuwiki embedded application allowing PHP code…
 quandqn/cve-2018-14667
Proof-of-concept exploit for CVE-2018-14667, demonstrating Java deserialization combined with EL injection to achieve remote code execution in…
 randomrobbiebf/cve-2024-7135
Tainacan <= 0.21.7 - Missing Authorization to Authenticated (Subscriber+) Arbitrary File Read
 mbadanoiu/cve-2021-46364
CVE-2021-46364: YAML Deserialization in Magnolia CMS
 randomrobbiebf/cve-2025-22777
GiveWP – Donation Plugin and Fundraising Platform <= 3.19.3 - Unauthenticated PHP Object Injection
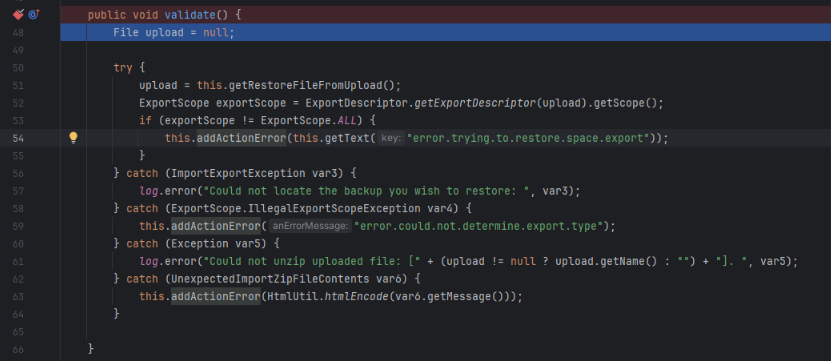 d3ckkno0b/analyze-exploit-cve-2023-22518-confluence
CVE-2023-22518 exploit analysis for Atlassian Confluence Server covering setup, JAR diffing, root cause, and unauthorized restore to regain admin…
 halcy0nic/cve-2022-44318
Proof of concept for CVE-2022-44318
 uniontech-software/libtheora-cve-2024-56431-poc
Proof-of-concept exploit for CVE-2024-56431 in libtheora, demonstrating a memory corruption vulnerability via fuzzing with AddressSanitizer and…
 mbanyamer/cve-2026-26030-microsoft-semantic-kernel-1.39.4-rce
Proof-of-concept exploit for CVE-2026-26030, demonstrating remote code execution via unsafe filter expressions in Microsoft Semantic Kernel's…
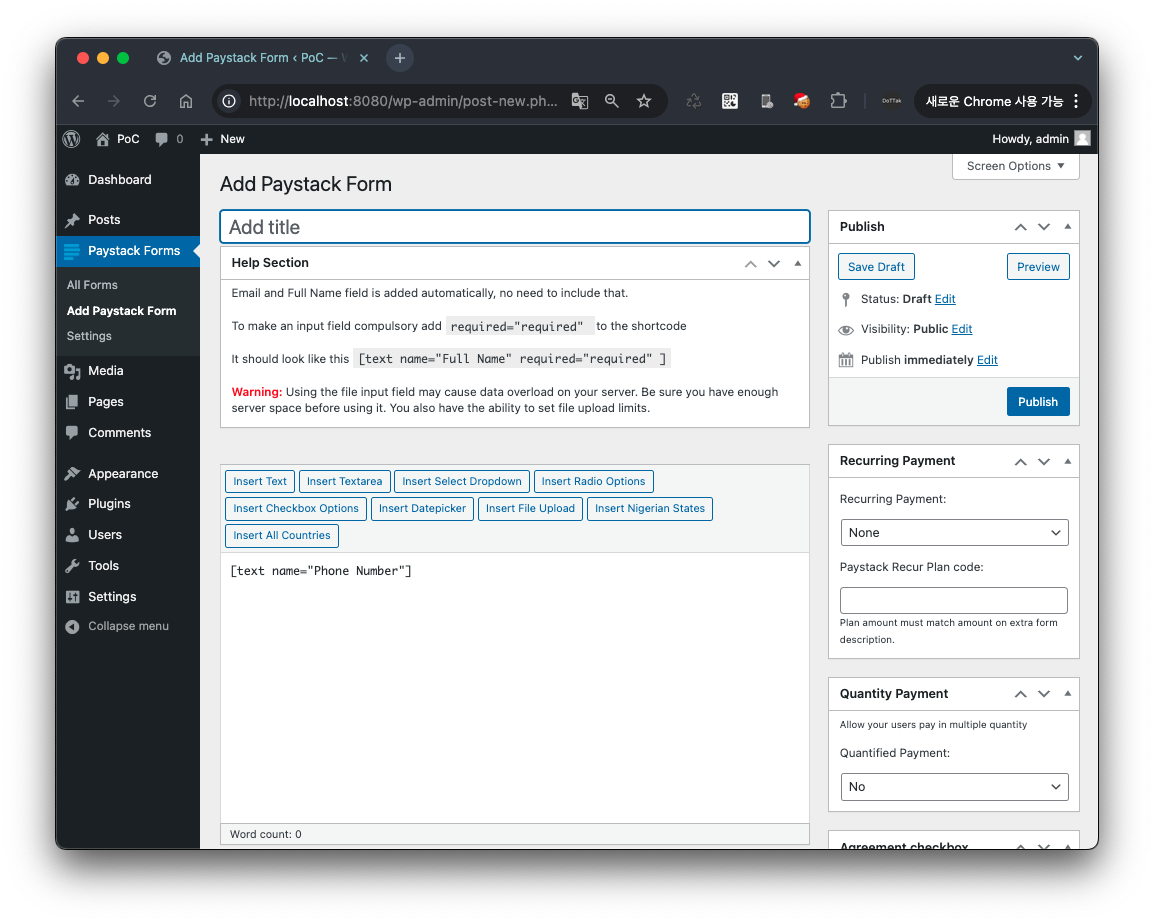 dottak/cve-2025-22652
PoC of CVE-2025-22652
 g4nkd/cve-2023-30253-poc
I couldn’t find a PoC for CVE-2023-30253, so I developed an effective one
 andhrimnirr/mintinstall-object-injection
CVE-2019-17080
 d3sca/cve-2024-52302
PoC exploit for CVE-2024-52302: unrestricted file upload in common-user-management Spring Boot app leading to remote code execution via…
 pastea/cve-2018-12533
Java-based proof-of-concept exploit for CVE-2018-12533 (RF-14310) targeting RichFaces deserialization vulnerability, with analysis reference and…








