
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended
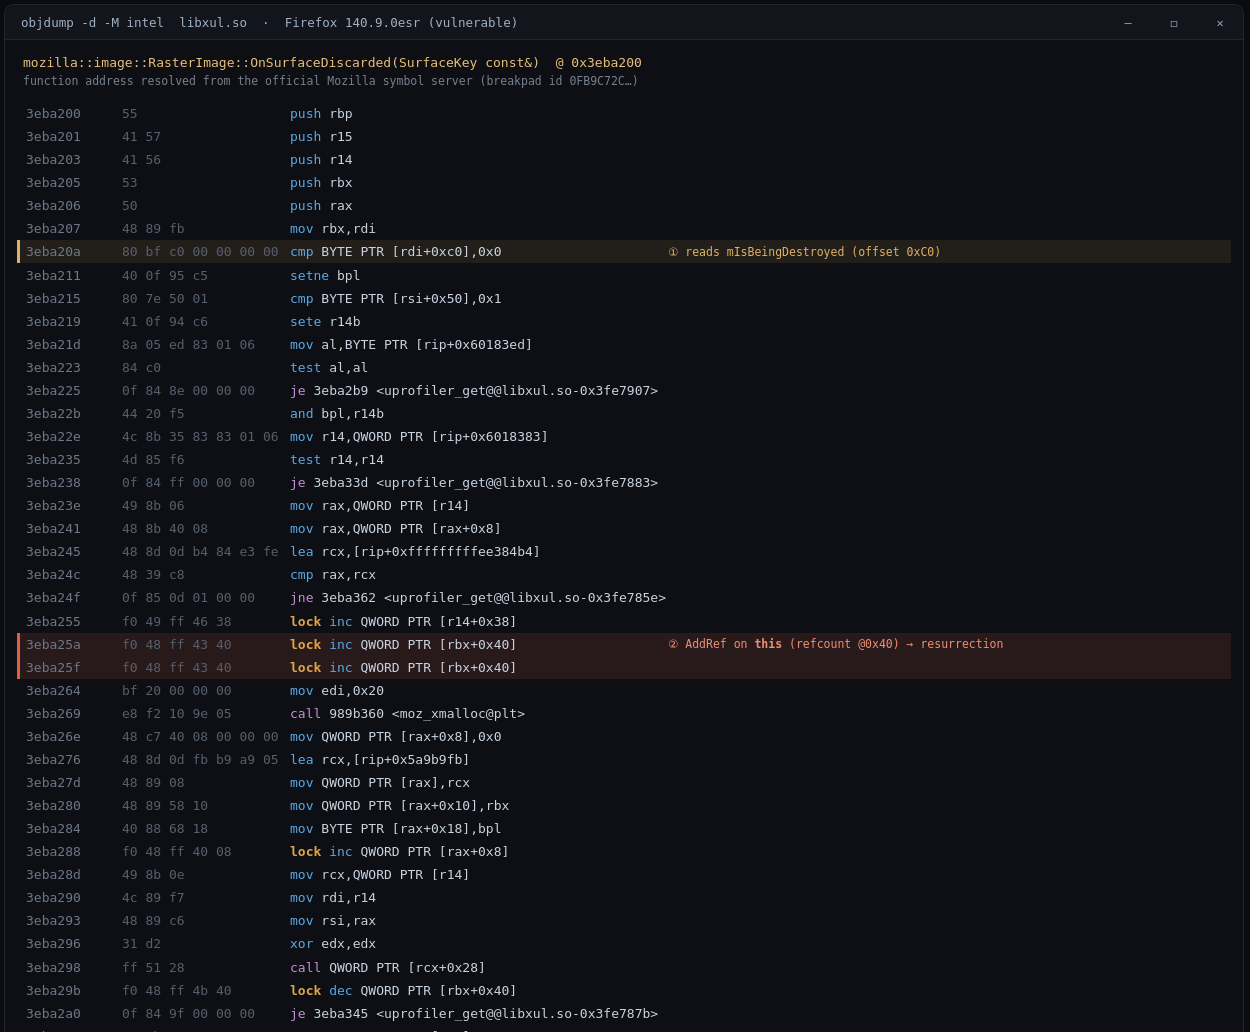
 defineid/revenant
CVE-2026-74943, Use after free in Firefox RasterImage (sec-high)
 oscerd/cve-2026-49098
PoC reproducer for CVE-2026-49098 (Apache Camel camel-kafka): the non-Camel-prefixed kafka.OVERRIDE_TOPIC header escapes the upstream HTTP header…
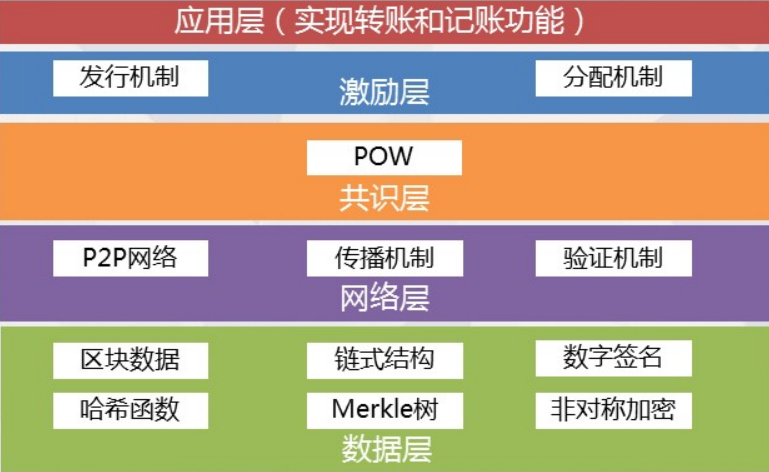 al1ex/blockchainconstruction
BlockChain Security Construction
 trachinus/cve-2026-4813
Proof-of-concept exploit for authenticated remote code execution via XSLT injection in Lutece Core, demonstrating command execution through crafted…
 razureink/cve-2026-63030_60137-wordpress_rce_reproduction
CVE Reproduction: cve-2026-63030_60137-wordpress_rce_reproduction
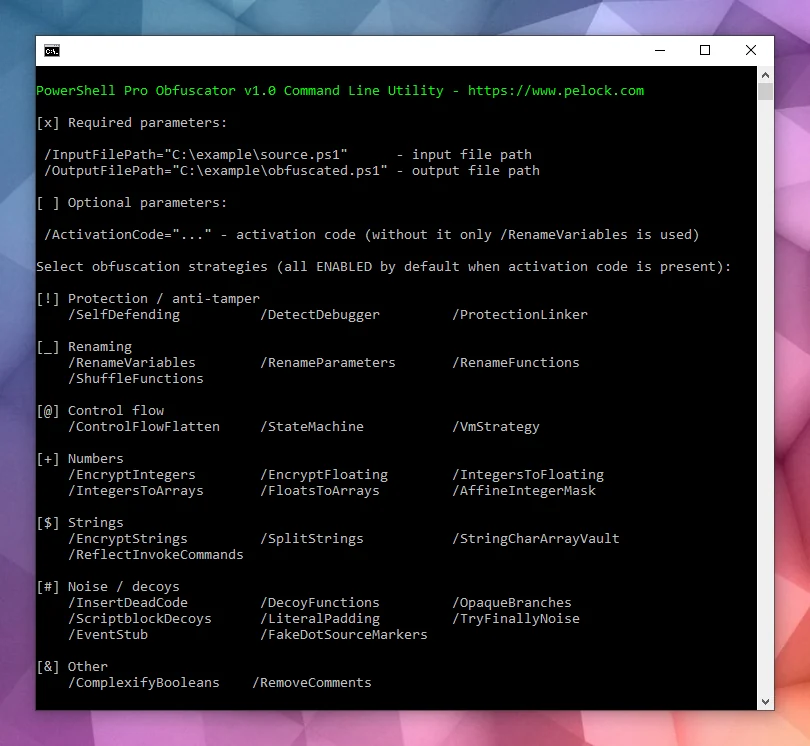 pelock/powershell-pro-obfuscator-python
Automate PowerShell script source code obfuscation & virtualization with a flexible Web API for Python (pip package).
 romain-deperne/cve-2026-77262
Proof-of-concept exploit for arbitrary file read in mcp-atlassian via path traversal in confluence_upload_attachment, with analysis and reproduction…
 ilhomjonr/cve-2026-67598
CVE-2026-67598 — Emlog Pro: disabled TLS certificate validation in AI assistant (MITM → API-key theft). CWE-295, CVSS 9.1. Reported by @IlhomjonR.
 theopaid/cve-2026-66730-infinite-loop-dos-in-facil.io-mime-parser
Security Advisory: Infinite Loop DoS in facil.io MIME Parser (Partial Boundary)
 biitts/cve-2026-52887-nocobase-sqli-rce
CVE-2026-52887 — NocoBase SQL injection -> PostgreSQL-superuser RCE (myInAppChannels:list filter, CVSS 10.0). Author PoC + source analysis + docker…
 oscerd/cve-2026-46455
Reproducer for CVE-2026-46455 — Apache Camel camel-keycloak missing TokenVerifier.IS_ACTIVE check (expired access tokens accepted)
 toanln-cov/cve-2026-66917
IDOR + Stored XSS via Broken Object-Level Authorization in JoomGallery
 romain-deperne/cve-2026-48017
Remote Code Execution in DbGate via functionName injection in the loadReader endpoint — CVSS 8.8
 20000419/cve-2026-39113
Advisory and AddressSanitizer reproducer for a SQLite SQLAR heap-buffer-overflow triggered by a crafted SZ value causing truncated allocation and…
 kx00007/cve-2026-39902
Proof-of-concept exploit for authenticated OS command injection (CWE-78) in Cacti ≤1.2.30, achieving remote code execution with CVSS 7.2.
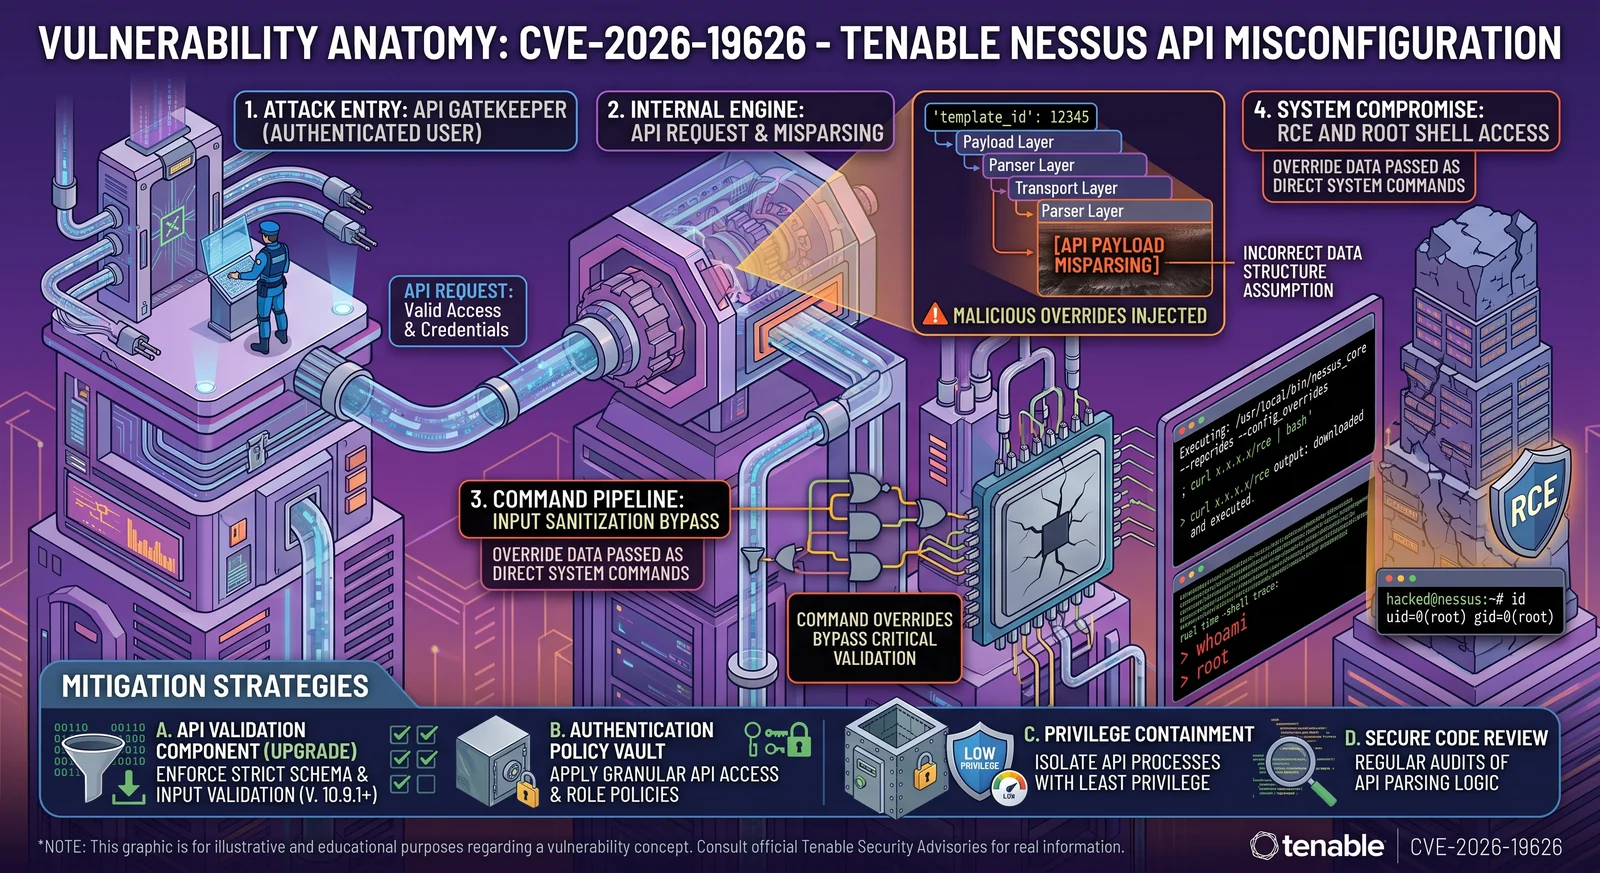 h00die/poc-cve-2026-19626
Proof-of-concept exploit for CVE-2026-19626, an authenticated remote code execution in SecurityCenter report generation, demonstrating a non-admin…
 george0papasotiriou/cve-2026-1337-ai-coding-assistant-prompt-injection-to-sandbox-escape
A prompt injection in a code‑review bot that executes AI‑generated fixes in a sandbox. The sandbox uses a blacklist to prevent dangerous commands,…
 theopaid/cve-2026-66731-negative-chunk-size-parsing-causes-memory-corruption-leading-to-server-crash
Security advisory for CVE-2026-66731 with root cause analysis, PoC exploit, and fix suggestions for facil.io HTTP/1.1 chunked encoding parser bug.








