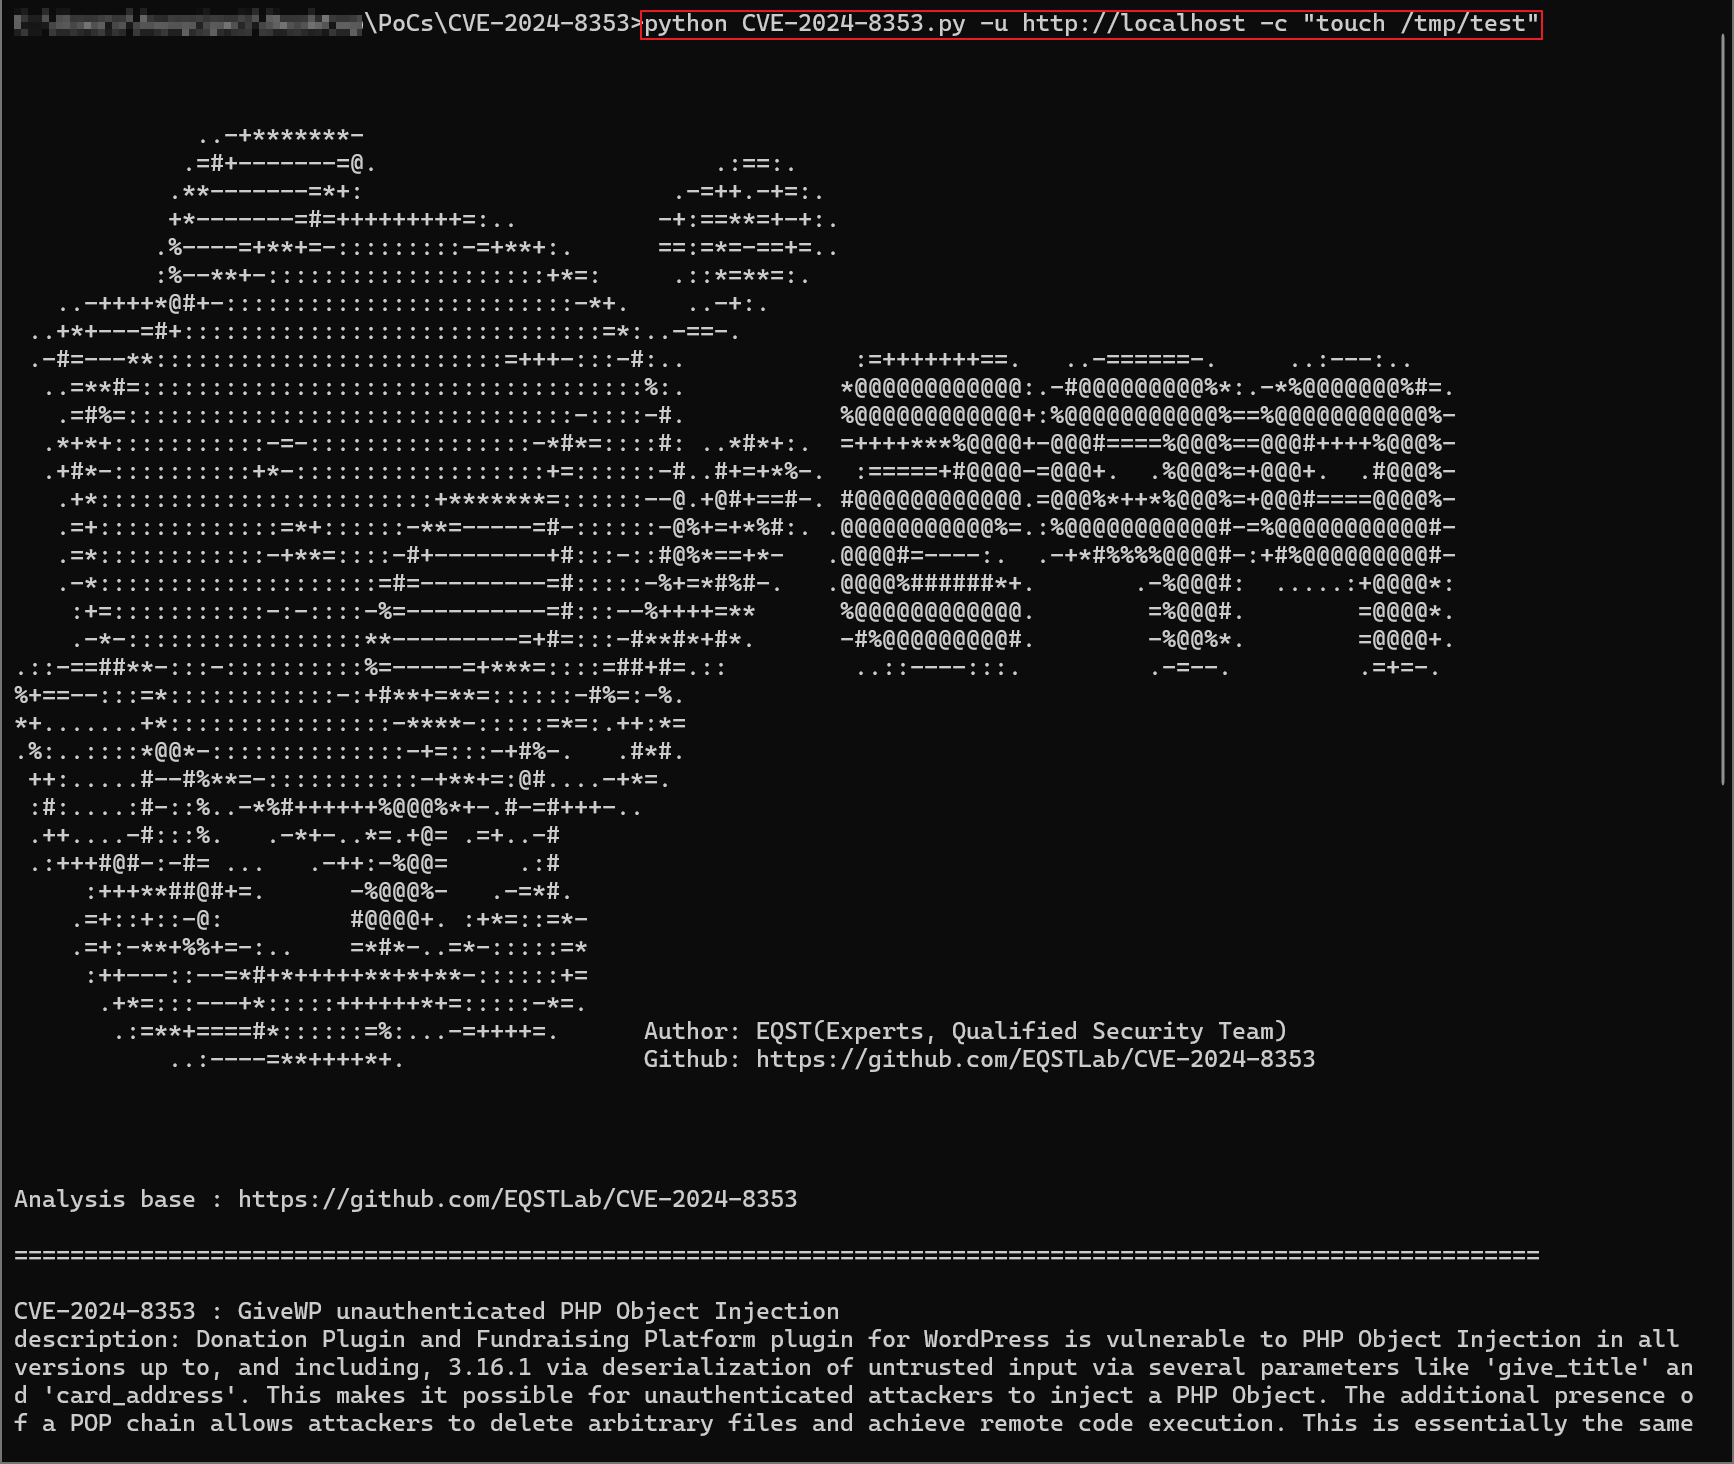
#1

 nanitor/log4fix
Detect and fix log4j log4shell vulnerability (CVE-2021-44228)
 al1ex/cve-2020-36188
CVE-2020-36188 &&Jackson-databind RCE
 randomrobbiebf/cve-2024-9593
Time Clock <= 1.2.2 & Time Clock Pro <= 1.1.4 - Unauthenticated (Limited) Remote Code Execution
 whenx/cve-2026-0776
Security research and proof-of-concept for CVE-2026-0776 affecting Discord Desktop Client.
 dump-guy/powershell-tools
Collection of some easy of use tools - in powershell.
 themalwareguardian/cve-2026-33439
First publicly shared exploit implementation for CVE-2026-33439 (OpenAM pre-auth RCE via jato.clientSession deserialization).
 luftwaffe66/gobfuscator
Obfuscates Go source code via AES-256 string encryption with runtime decryption, identifier renaming, and comment removal to hinder reverse…
 chenaotian/cve-2021-3156
CVE-2021-3156 POC and Docker and Analysis write up
 corelight/quipu
A desktop workbench for writing, validating, compiling, and testing YARA rules.
 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
 mf-labs/witcher
Managing GitHub Advanced Security (GHAS) Controls at Scale
 fairyming/cve-2019-17564
CVE-2019-17564:Apache Dubbo反序列化漏洞
 li8u99/spring-data-mongodb-demo
Demo environment for CVE-2022-22980 (Spring Data MongoDB SpEL injection RCE) with vulnerable application code for security testing and education.
 benedridge/cve-2023-30533
There were no proper POCs for CVE-2023-30533 so I made one. (Reported by Vsevolod Kokorin)
 owasp/benchmark
The OWASP Benchmark GitHub repo has moved to: https://github.com/OWASP-Benchmark/BenchmarkJava
 auditinfra-io/o1js-scan
Dependency-free static analyzer for zk circuit soundness bugs in o1js/Mina zkApps and Noir circuits
 jordan922/cve-2025-8088
Python tool for safe archive handling, path traversal awareness, and secure extraction. Inspired by CVE-2025-8088.