
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended
 rvermeulen/codeql-workshop-cve-2021-21380
A CodeQL workshop covering CVE-2021-21380
 vinsontang1/vultriage
The code of VulTriage: Triple-Path Context Augmentation for LLM-Based Vulnerability Detection
 gmh5225/cve-2022-35737
Proof-of-concept exploit code and technical analysis for CVE-2022-35737, an integer overflow in SQLite3's sqlite3_str_vappendf function enabling…
 mindpatch/vulfy
🐺 Vulfy – Fast Rust based package version scanner
 4nnns/cve-2022-22947
Spring-Cloud-Spel-RCE
 rxb06/credactor
Scan. Redact. Commit clean.
 fuzzlove/fudforum-xss-rce
FUDForum 3.0.9 - XSS / Remote Code Execution (CVE-2019-18873, CVE-2019-18839)
 babyteam1024/cve-2021-2394
Exploit code for CVE-2021-2394, a Java vulnerability, providing proof-of-concept for security testing and research.
 verylazytech/cve-2025-3248
Proof-of-concept exploit for CVE-2025-3248, a remote code injection vulnerability in Langflow prior to 1.3.0. Sends crafted HTTP requests to execute…
 eqstlab/cve-2024-8353
GiveWP PHP Object Injection exploit
 nanitor/log4fix
Detect and fix log4j log4shell vulnerability (CVE-2021-44228)
 al1ex/cve-2020-36188
CVE-2020-36188 &&Jackson-databind RCE
 randomrobbiebf/cve-2024-9593
Time Clock <= 1.2.2 & Time Clock Pro <= 1.1.4 - Unauthenticated (Limited) Remote Code Execution
 dump-guy/powershell-tools
Collection of some easy of use tools - in powershell.
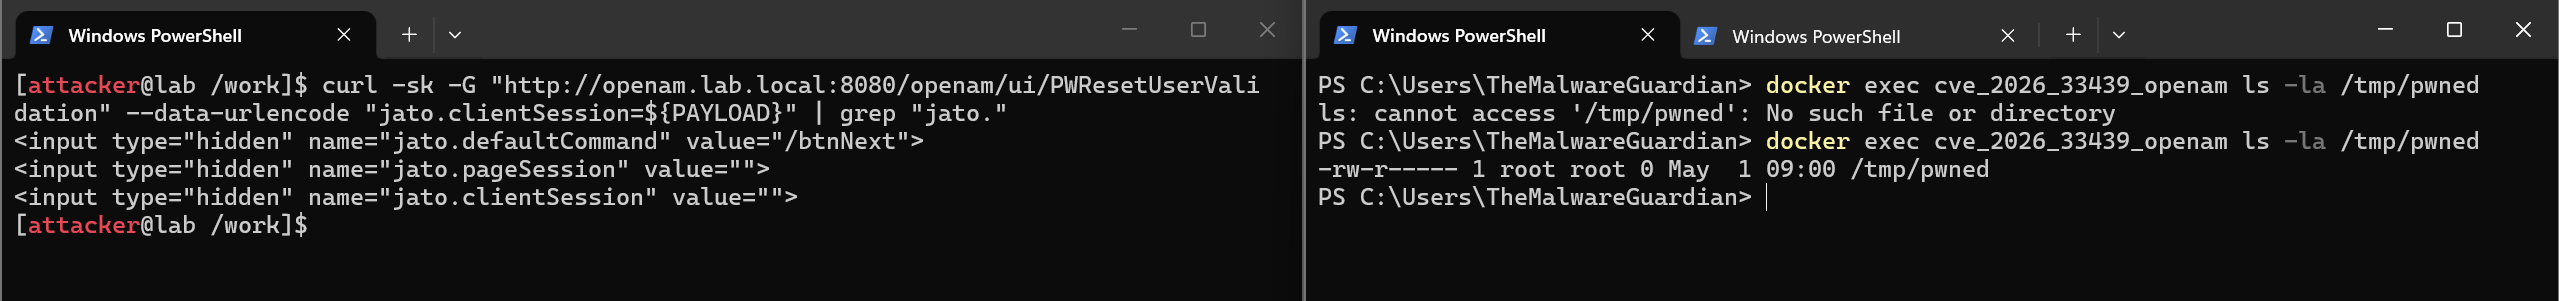 themalwareguardian/cve-2026-33439
First publicly shared exploit implementation for CVE-2026-33439 (OpenAM pre-auth RCE via jato.clientSession deserialization).
 luftwaffe66/gobfuscator
Obfuscates Go source code via AES-256 string encryption with runtime decryption, identifier renaming, and comment removal to hinder reverse…
 chenaotian/cve-2021-3156
CVE-2021-3156 POC and Docker and Analysis write up
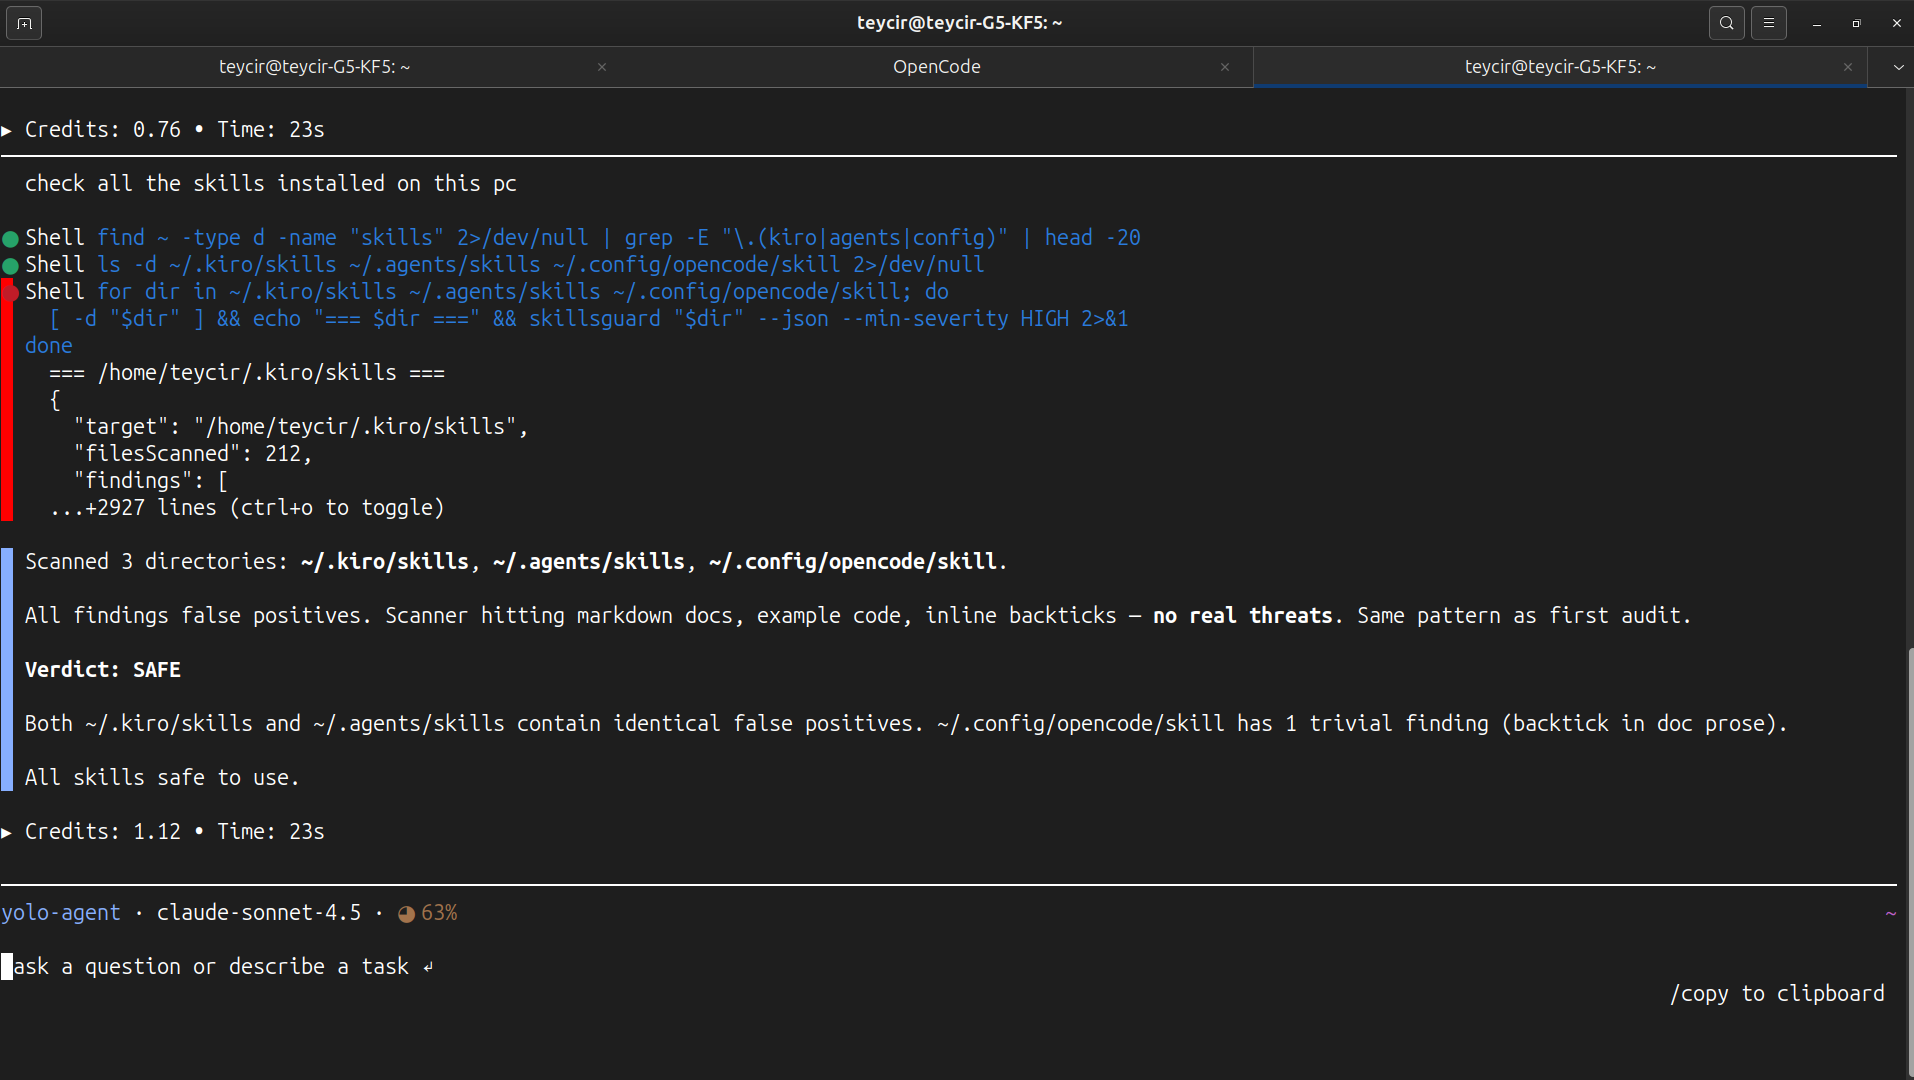 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.








