
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended
 nzkoz/bigdecimal-segfault-fix
Provides a quick workaround for the segfault bug in Ruby (CVE-2009-1904)
 sudistark/vscode-rce-electrovolt
Trying to reproduce CVE-2021-43908
 simplylu/cve-2021-42574
Generate malicious files using recently published bidi-attack (CVE-2021-42574)
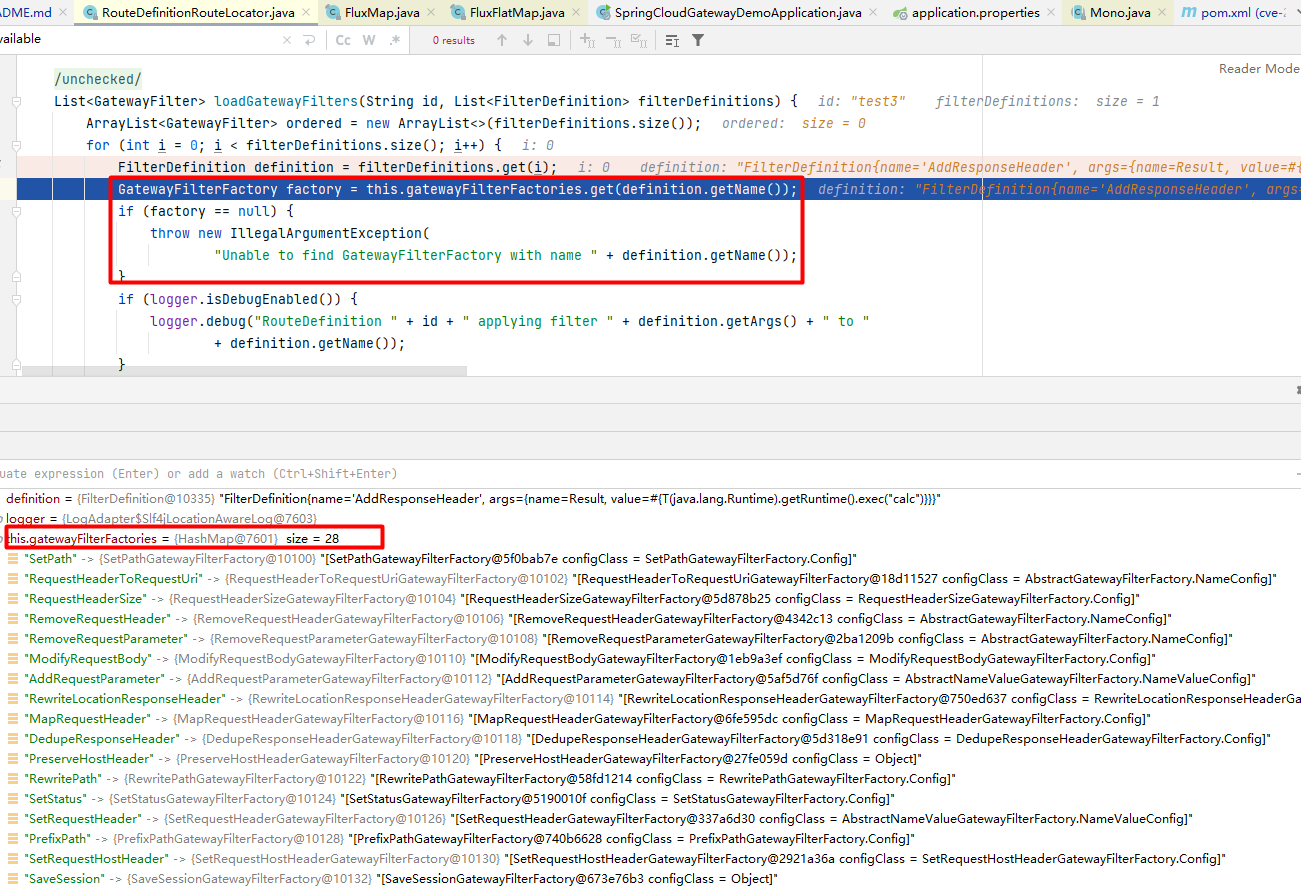 enokiy/cve-2022-22947-spring-cloud-gateway
Detailed analysis and exploit for CVE-2022-22947, a remote code execution vulnerability in Spring Cloud Gateway via SpEL injection in the Actuator…
 neurosaki987/qvm-tool
Static analysis and structure recovery toolkit for ACE .qvm0-protected PE images
 hunntr/cve-2023-46818
An issue was discovered in ISPConfig before 3.2.11p1. PHP code injection can be achieved in the language file editor by an admin if…
 elpe-pinillo/cve-2023-6246
C-based proof-of-concept exploit for CVE-2023-6246, targeting a privilege escalation vulnerability in the Linux kernel's syscalls. Tested on Fedora…
 rgielen/struts1filter
A request parameter filter solution for Struts 1 CVE-2014-0114 based on the work of Alvaro Munoz and the HP Fortify team
 ztcoalson/if-guide
[NeurIPS '25] Code for Paper "IF-Guide: Influence Function-Guided Suppression of Harmful Training Data for Reducing LLM Toxicity"
 elevenpaths/atomshields
Security testing framework for repositories and source code
 werew/qsynth-artifacts
Benchmark datasets and synthesis artifacts for QSynth, containing Tigress-obfuscated C functions, x86_64 binaries, execution traces, ground truth,…
 csenox/cve-2021-21425
GravCMS Unauthenticated Arbitrary YAML Write/Update leads to Code Execution (CVE-2021-21425)
 dollarboysushil/dolibarr-17.0.0-exploit-cve-2023-30253
In Dolibarr 17.0.0 with the CMS Website plugin (core) enabled, an authenticated attacker can obtain remote command execution via php code injection…
 chybeta/cve-2018-11235-demo
Demonstrates exploitation of CVE-2018-11235, a Git submodule RCE vulnerability, with build script and analysis for educational purposes.

 bytehackr/cve-2022-0853
Demonstrates a memory leak in JBoss client when using UserTransaction repeatedly, with a PoC and analysis for CVE-2022-0853.
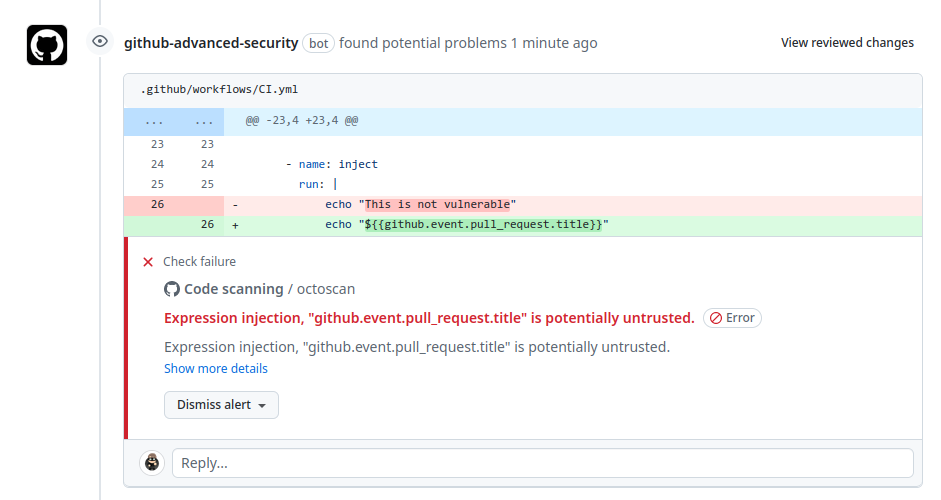 synacktiv/action-octoscan
📦 :octocat: A GitHub Action that performs a security scan of your GitHub Actions.








