
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended
 nollium/cve-2024-9264
Exploit for Grafana arbitrary file-read and RCE (CVE-2024-9264)
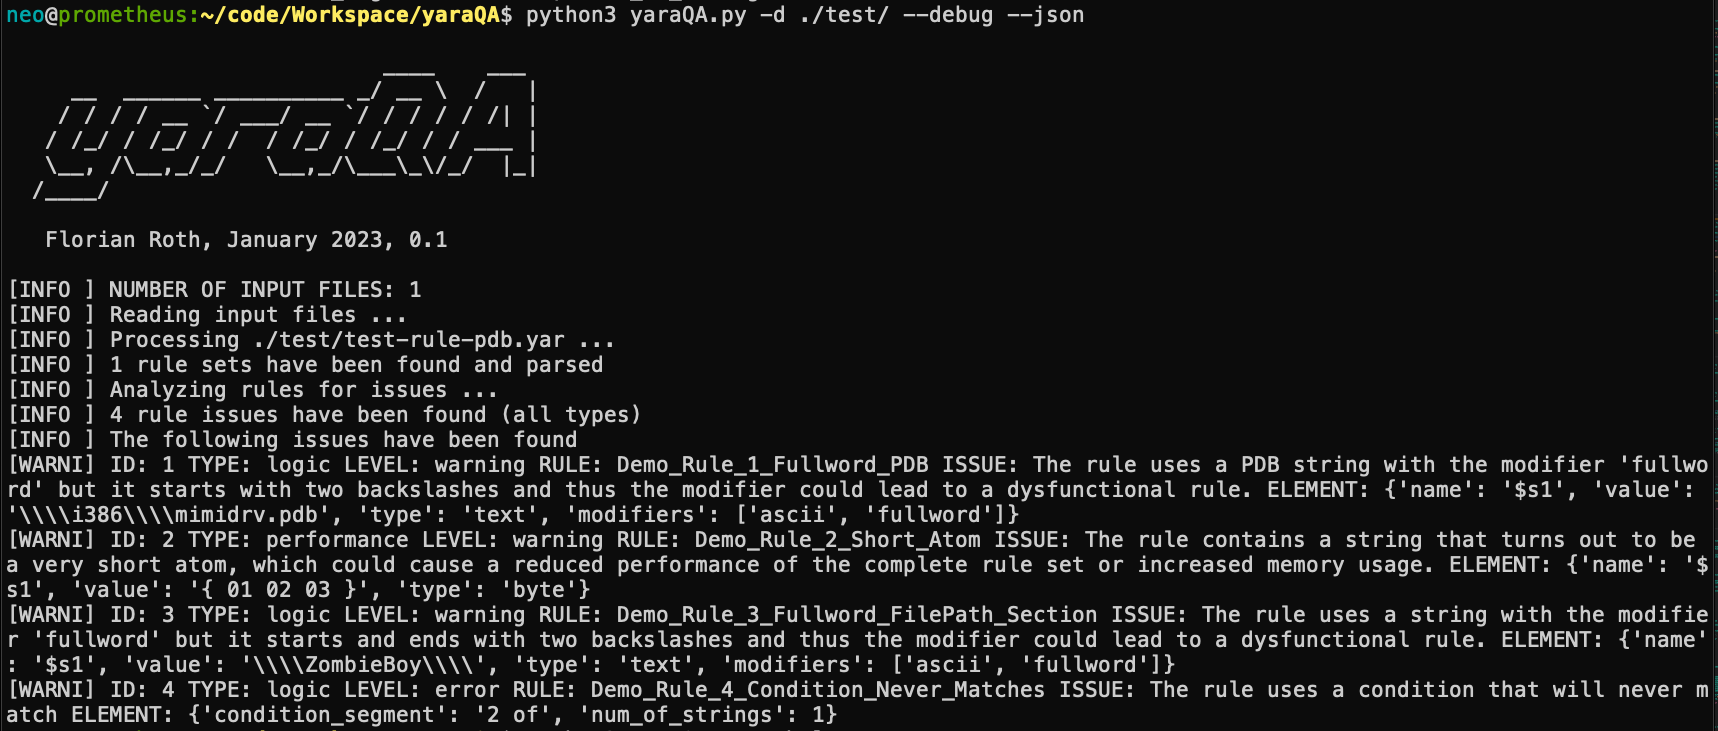 neo23x0/yaraqa
YARA rule analyzer to improve rule quality and performance
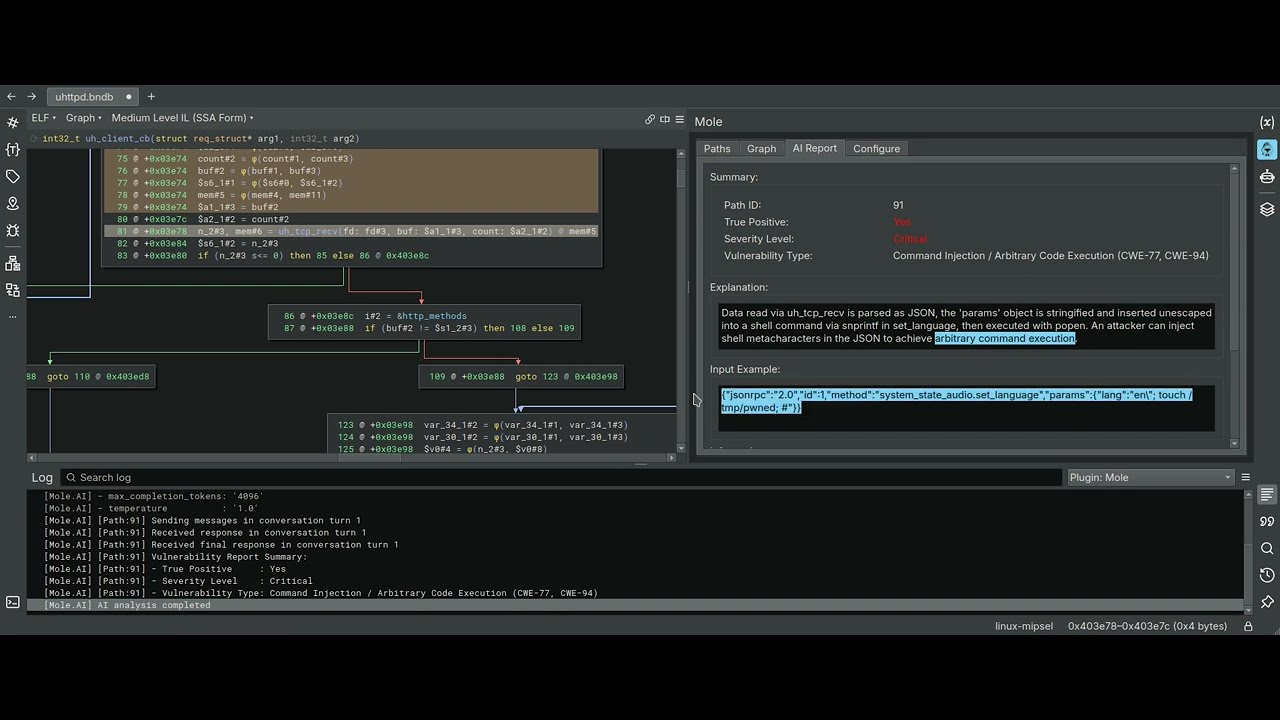 cyber-defence-campus/mole
A Binary Ninja plugin using backward slicing of variables as a driver for static taint analysis
 shubhamshubhankar/autosource
Automated static code analysis framework integrated with SonarQube for early vulnerability detection in source code by scanning Git repositories…
 codewhitesec/httpremotingobjrefleak
Additional resources for leaking and exploiting ObjRefs via HTTP .NET Remoting (CVE-2024-29059)
 wolfssl/wolfcose
A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.
 samsung/utopia
UT based automated fuzz driver generation
 irsdl/burpsuitejsbeautifier
Burp Suite JS Beautifier
 quarkslab/qsynthesis
Greybox Synthesizer geared for deobfuscation of assembly instructions.
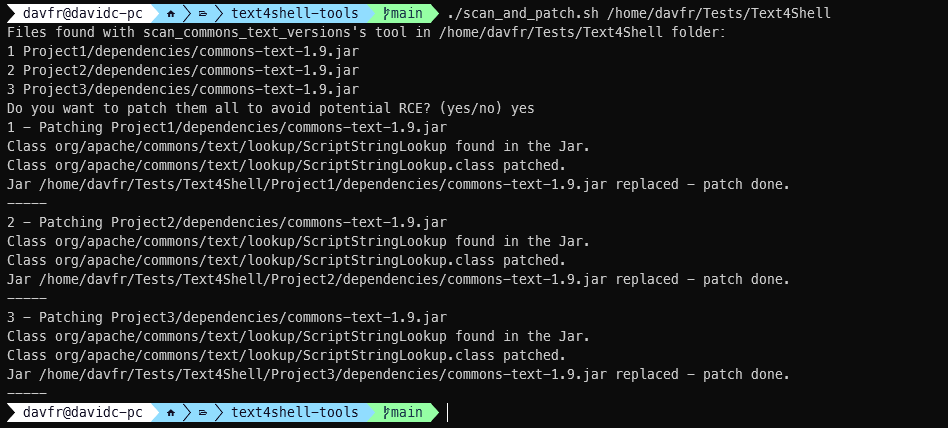 jfrog/text4shell-tools
Detect and patch vulnerable Apache Commons Text in Java JAR/WAR artifacts; fingerprint classes and scan bytecode for CVE-2022-42889 (Text4Shell) call…
 hosch3n/fastjsonvulns
Exploit for Fastjson 1.2.80 CVE-2022-25845 enabling AspectJ file read and Groovy remote class loading for RCE.
 disruptops/cred_scanner
A simple file-based scanner to look for potential AWS access and secret keys in files
 rbmm/ntdetours
Detours implementation (x64/x86) which used only ntdll import
 owasp/sedated
SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)
 jas502n/cve-2019-12384
Jackson Rce For CVE-2019-12384
 gach0ng/agentstalker
End-to-end security audit framework for LLM agents: static AST and taint modeling, attack synthesis, Docker sandbox replay, and deterministic verdict…
 owasp/ocsd
OWASP Certified Secure-Software Developer
 codewhitesec/unmarshalpwn
POC for CVE-2018-0824








