
 #1
Tools for assessing, testing, and securing cloud environments (AWS, Azure, GCP) and their services.
Kitploit recommended

 mnk-works/portainer-cve-2026-44848-checker
Non-destructive checker for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints
 rui0828/cve-2026-21440-adonisjs-bodyparser
Docker-based reproduction lab for CVE-2026-21440. A path traversal / arbitrary file write vulnerability in @adonisjs/bodyparser ≤10.1.1.
 oscerd/cve-2026-79986
Reproducer and analysis for CVE-2026-79986, a path traversal in Apache Camel camel-azure-files where share listing names escape the polled directory.
 abraxas/spark-proxyuser-classpath
Apache Spark 4.2.0 - High - Remote - Privilege leftover - proxy-user defaultExtraClassPath
 abraxas/spark-connect-copy-local
Apache Spark 4.2.0 - High - Remote - File write - Connect session SET copyFromLocalToFs.allowDestLocal
 nvansluis/test_cve-2023-46747
Python script to test F5 BIG-IP for CVE-2023-46747 and add an administrator account if vulnerable.
 apaonum/brotli-cve-check
Agent skill + script to scan projects for CVE-2026-111497 (Brotli), rate criticality and suggest fixes
 nsk-394/kavach-loop
Closed-loop vulnerability remediation: detect -> reproduce exploit -> generate patch -> verify with a proof harness. Worked example: Langflow…

 schroeder-sys/pantheon-souverainete
Infrastructure cloud modulaire, redondante et 100% souveraine pour s'affranchir des GAFAM. Guides techniques, architecture Zero-Trust et chiffrement…
 q0524/cve-2026-44825_ctf
Dockerized Apache Solr CTF challenge reproducing CVE-2026-44825 default-credential authentication bypass, with GZCTF deployment config, exploit…
 onapsis/onapsis-mandiant-cve-2025-31324-vuln-compromise-assessment
CVE-2025-31324 & CVE-2025-42999 vulnerability and compromise assessment tool
 mc493/linux-kernel-zero-day-mitigation-zero-downtime-kernel-defense-
Zero-downtime Linux kernel zero-day defense case study. For the automated CLI and dual-witness notary framework, see mc493/kshield.
 the-infra-company/kcatcher
Catch what's lurking in your Kafka clusters.
 suriyaboon/hackthebox-facts
HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…
 ejfkdev/oss
Cross-cloud S3-compatible object storage CLI to list, export, and download buckets across AWS, Aliyun, Tencent, Huawei and more, with anonymous…
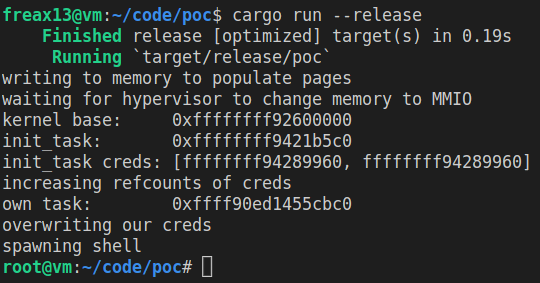 freax13/cve-2023-46813-poc
Proof-of-concept exploit for CVE-2023-46813 targeting AMD SEV-SNP. Escalates privileges by manipulating hypervisor memory type changes to swap task…
 chef-cft/salt-vulnerabilities
Checks for CVE-2020-11651 and CVE-2020-11652
 kavryxdev-group/sandboxed-untrusted-code-execution-runner
Executes untrusted Python, JavaScript, and Bash in a hardened jail with 5-second, 128 MB, 0.5-core, PID and output limits.








