
 #1
Tools for auditing configurations, permissions, and services in cloud platforms (IaaS, PaaS).
Kitploit recommended
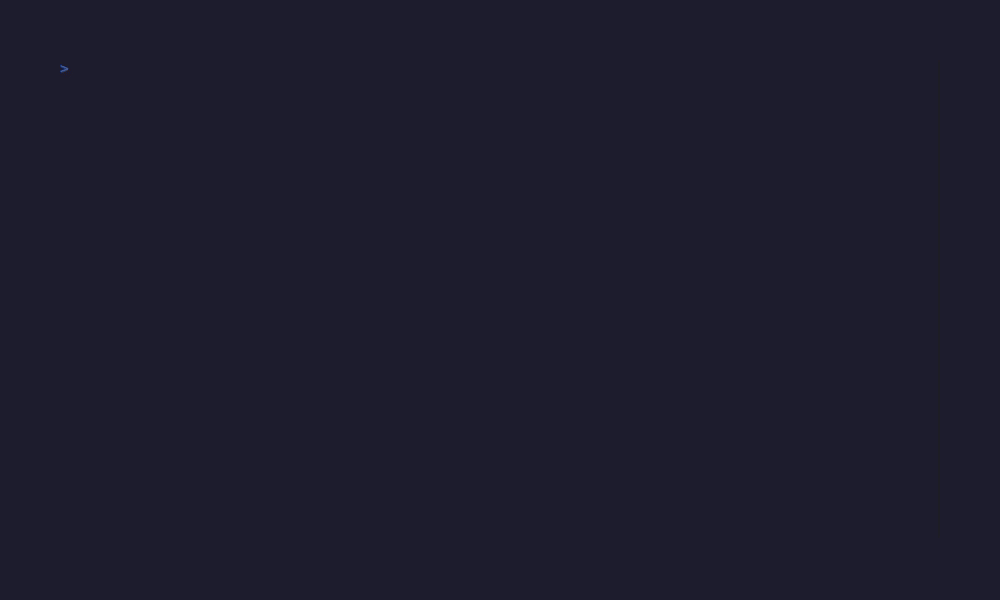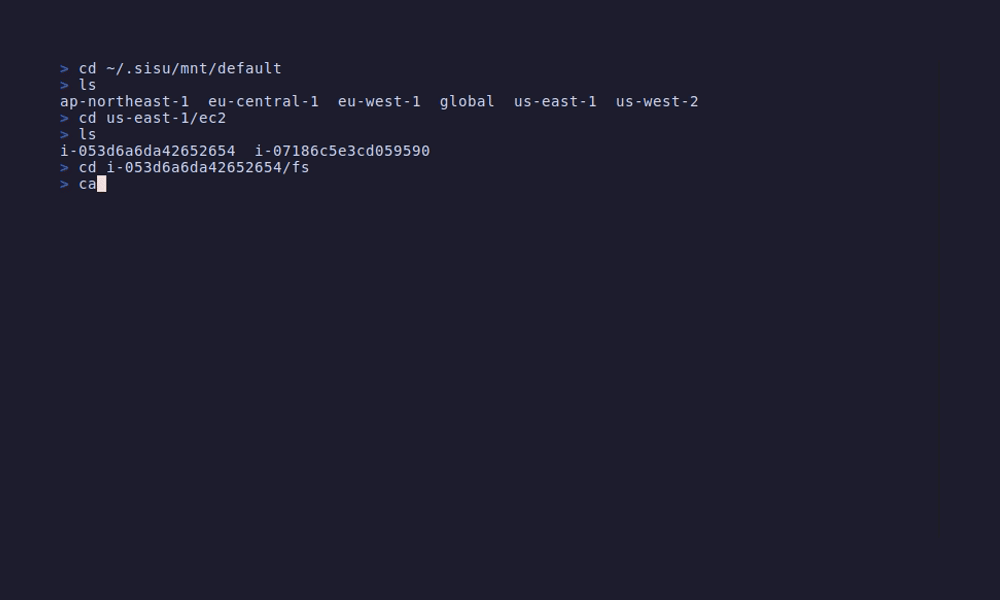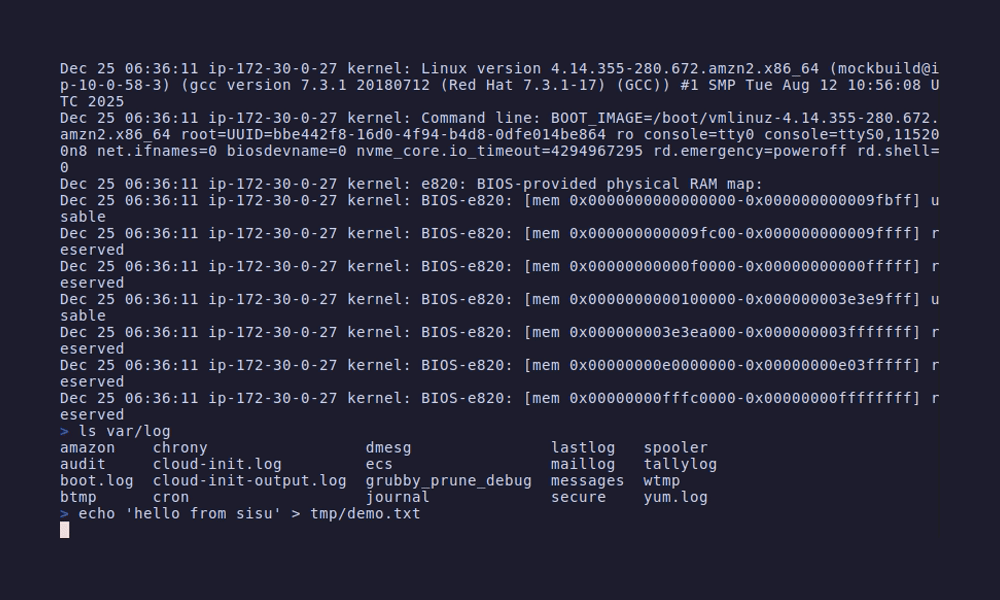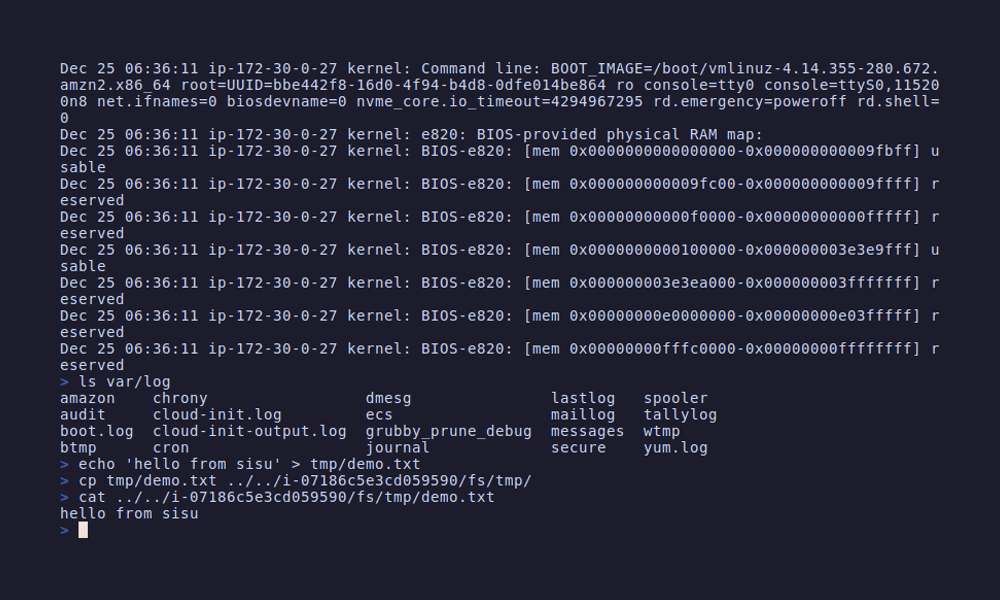
 semonte/sisu
Mounts AWS resources as a local filesystem for infrastructure exploration, security auditing, and configuration analysis using standard Unix tools…
 owasp/awscanner
Finds internet-exposed resources in an AWS account
 jdauphant/patch-openssl-cve-2014-0160
Patch openssl #heartbleed with ansible
 jas502n/cve-2019-5736
Exploit for CVE-2019-5736: runc container escape that overwrites host docker-runc binary with a payload, triggered via docker exec.
 blake-fm/vcenter-log4j
Script to apply official workaround for VMware vCenter log4j vulnerability CVE-2021-44228
 contrastsecurity/contrast
SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…
 seanrickerd/cve-2026-31431
Exploit for Linux kernel CVE-2026-31431 causing page cache corruption via authencesn AEAD manipulation, targeting privilege escalation in containers…
 jq6l43d1/proxmox-lxc-docker-fix
Workaround for CVE-2025-52881: Fixes Docker/Podman breakage in Proxmox LXC containers caused by AppArmor incompatibility with runc 1.2.7+. Universal…
 eduardolat/authkeysync
🔐 Lightweight CLI utility designed to synchronize SSH public keys from remote URLs into local authorized_keys files
 anee769/conduit
On-prem API gateway for AI coding agents with per-engineer cost attribution, hard budgets, egress governance (secrets/entity scanning), context-rot…
 ooafa/bucketbuster
Scans public cloud object-storage endpoints across Yandex, VK, Selectel, Sber, Alibaba, Tencent, Huawei, and Baidu to find listable buckets and…
 mitiga/log4shell-cloud-scanner
we are providing DevOps and security teams script to identify cloud workloads that may be vulnerable to the Log4j vulnerability(CVE-2021-44228) in…
 akhld/spark-exploit
Arbitary Code Execution in Unsecured Apache Spark Cluster
 d3vzer0/cnc-relay
Docker projects to retain beacon source IPs using C2 relaying infra
 mandiant/vcsa-hardening-tool
Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)
 atiilla/cve-2026-42897
CVE-2026-42897 - Exchange Health Checker blind spot: outbound IIS URL Rewrite rules silently ignored, making EOMT mitigations invisible in diagnostic…
 tapanmeena/azpim
A command-line interface tool for managing Azure Privileged Identity Management (PIM) role activations directly from your terminal.
 aoripus-ltd/januscape-hotfix
Complete fix collection for the CVE-2026-53359 guest-to-host escape vulnerability in the KVM/x86 shadow MMU. From zero-downtime livepatch to kernel…








