
 #1
Tools for auditing configurations, permissions, and services in cloud platforms (IaaS, PaaS).
Kitploit recommended

 vighnesh91/cloudgarrison
Offline browser-based multi-cloud posture workbench that simulates attack paths, audits IaC compliance, analyzes identity graphs, and maps audit logs…

 nihal799/zttp
Zero-trust SSH bastion proxy with Vault-backed key management, RBAC policy enforcement, full session recording, and admin TUI for auditable access to…
 schroeder-sys/pantheon-souverainete
Infrastructure cloud modulaire, redondante et 100% souveraine pour s'affranchir des GAFAM. Guides techniques, architecture Zero-Trust et chiffrement…
 ejfkdev/oss
Cross-cloud S3-compatible object storage CLI to list, export, and download buckets across AWS, Aliyun, Tencent, Huawei and more, with anonymous…
 bishopfox/cirro-azcli-ext
Azure CLI extension for Cirro collection
 leitwacht/leitwacht
Leitwacht control plane — runtime security for GitLab Runner CI/CD: policy authoring, multi-tenancy, audit, GitLab integration
 infiniroot/ansible-mitigate-copyfail-dirtyfrag
Simple Ansible Playbook to mitigate against CopyFail (CVE-2026-31431) and DirtyFrag (CVE-2026-43284) vulnerabilities.
 imlzw/kubernetes-1.12.3-all-auto-install
个人整理的Centos7.x + Kubernetes-1.12.3 + Dashboard-1.8.3 无 CVE-2018-1002105 漏洞的master节点全自动快速一键安装部署文件,适用于测试环境,生产环境的快速安装部署
 oriolrius/kafka-keycloak-oauth
Apache Kafka 4.1.0 (KRaft) with Keycloak OAuth2 authentication using Strimzi - bypasses CVE-2025-27817 URL allowlist restriction
 vvpoglazov/cve-2024-41110-checker
Parallel SSH-based scanner that detects CVE-2024-41110 in Docker installations, identifies vulnerable versions and AuthZ plugins, and generates a…
 h4wkst3r/dop2mop
OpenGraph collector for BloodHound that maps attack paths from DevOps to MLOps infrastructure, collecting CI/CD pipeline, service principal, and ML…
 shahidmallaofficial/cpanel-cve-2026-41940-fix
One-shot detection and remediation for cPanel/WHM servers compromised via CVE-2026-41940, including IOC checks, malware cleanup, C2 blocking, and…
 dmcdtc/openvz-cve-patch-2026
GhostLock - CVE-2026-43499 backport patch for openVZ 7
 placeos/auth
PlaceOS authentication service and API gatekeeper.
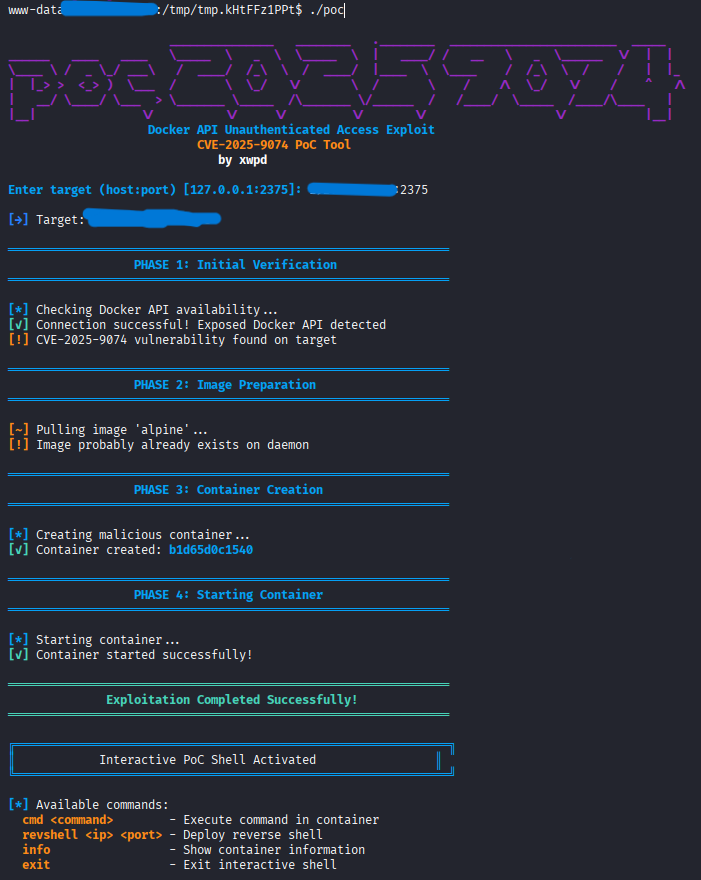 xwpdx0/poc-2025-9074
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…
 oseguera12/cowrie-honeypot-digitalocean
Medium-interaction SSH/Telnet honeypot built with Cowrie, Loki, Promtail, and Grafana - provisioned on DigitalOcean via Terraform with a GitLab CI…
 mahdi13830510/cve-2026-31431-mitigation-suite
Kernel-runtime defense framework for AF_ALG vulnerabilities, featuring eBPF socket tracing, Ansible hardening, and a crypto auditor for drift…
 george0papasotiriou/cve-2026-9999-serverless-event-injection-to-code-overwrite
Proof-of-concept exploit for CVE-2026-9999, demonstrating path traversal in serverless object storage events that overwrites function source code to…








