
 #1
Tools for auditing configurations, permissions, and services in cloud platforms (IaaS, PaaS).
Kitploit recommended

 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
 radkawar/aws-firmware-dump
Acquires the EBS disks of an AWS AMI you can launch, streaming snapshots via EBS direct APIs to a private S3 bucket with sha256 manifests and…
 qmadev/tf-mythic-azure
Automatically deploying Mythic C2 in Azure using Terraform
 xlab-si/iac-scan-runner
Service that scans your Infrastructure as Code for common vulnerabilities
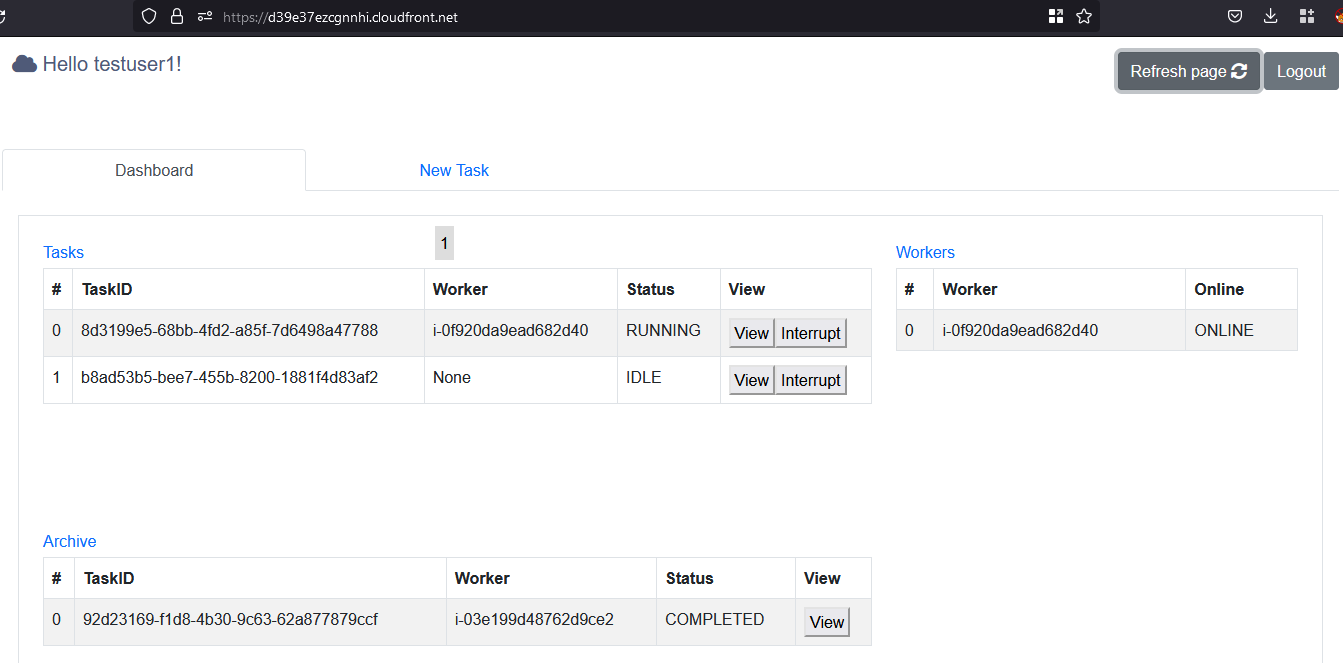 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
 wearecloudar/s3-account-search
S3 Account Search
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…
 aquasecurity/trivy-plugin-aqua
Plugin for integrating Trivy with Aqua Security platform to scan IaC, pipelines, and dependencies for vulnerabilities and misconfigurations.
 capture0x/aws-pentest
Automated AWS security assessment CLI with 30 modules covering IAM privilege escalation, S3 exposure, compute, network, logging and misconfiguration…
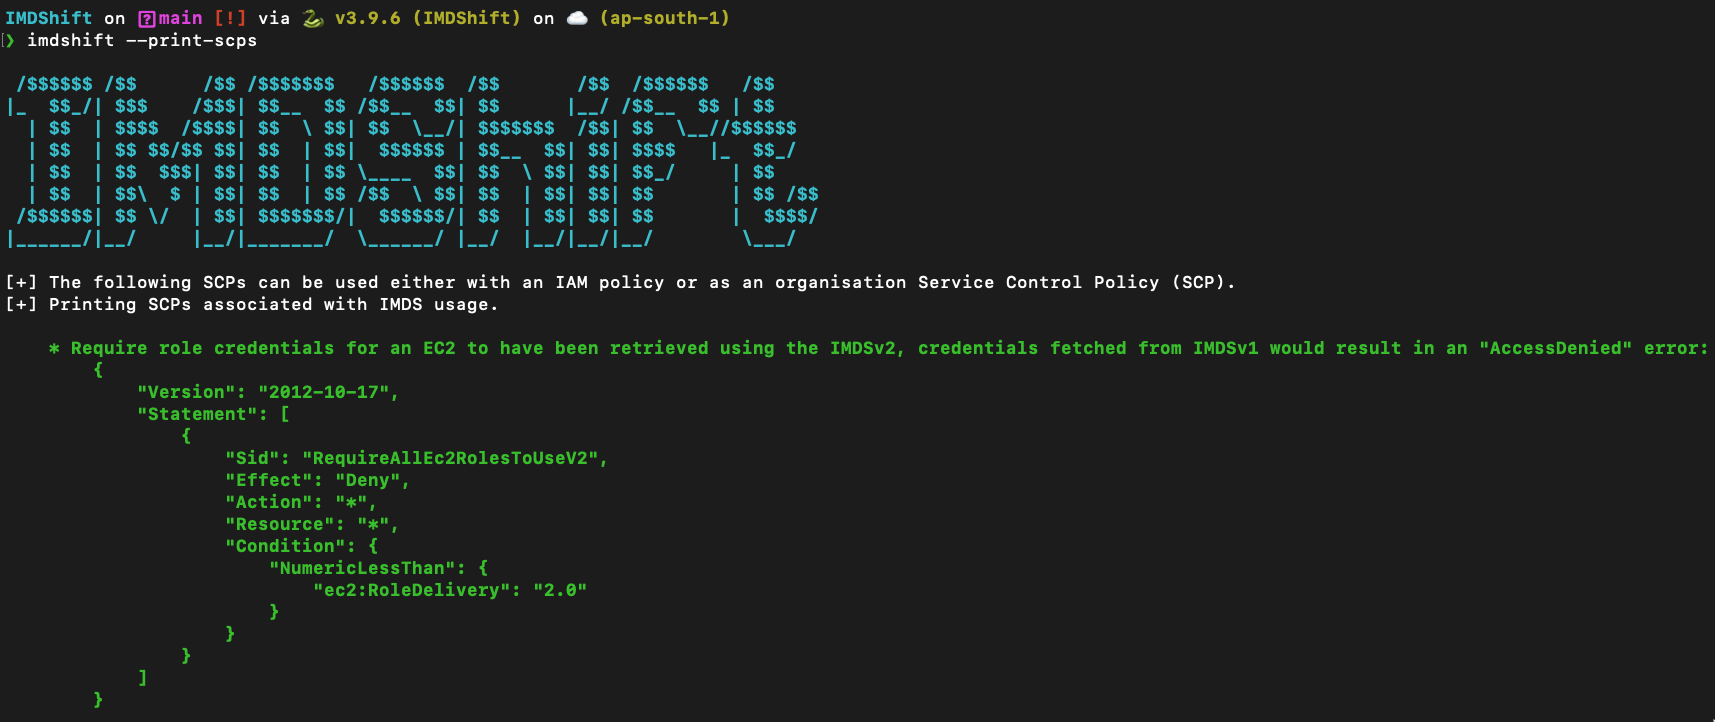 ayushpriya10/imdshift
Automates migration of AWS workloads from IMDSv1 to IMDSv2 to mitigate SSRF attacks. Detects IMDSv1 usage across EC2, ECS, EKS, Lightsail, and more,…
 andresriancho/nimbostratus-target
This repository holds a target infrastructure you can use for running the nimbostratus tools.
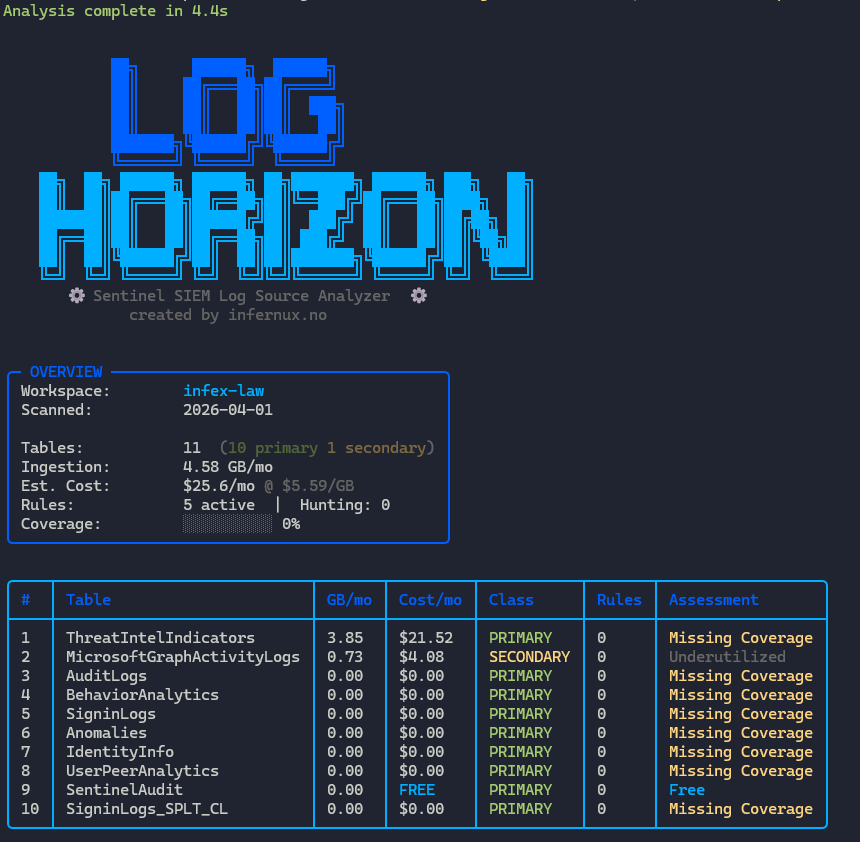 lnfernux/log-horizon
Microsoft Sentinel SIEM Log Source Analyzer
 pyperanger/dockerevil
WorldFirst (Public) Docker API Exploit - My security researches involving Docker and Openshift
 tevora-threat/rt_redirectors
Ansible role to configure redirectors for red team C2
 qarait/ephemera
Zero-Trust SSH CA
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
 ustayready/outpost
AWS Testing and Reporting Management Tool
 nccgroup/sfpoldevchk
Salesforce Policy Deviation Checker








