
 #1
Binary reverse engineering, disassembly, decompilation, and patching tools.
Kitploit recommended
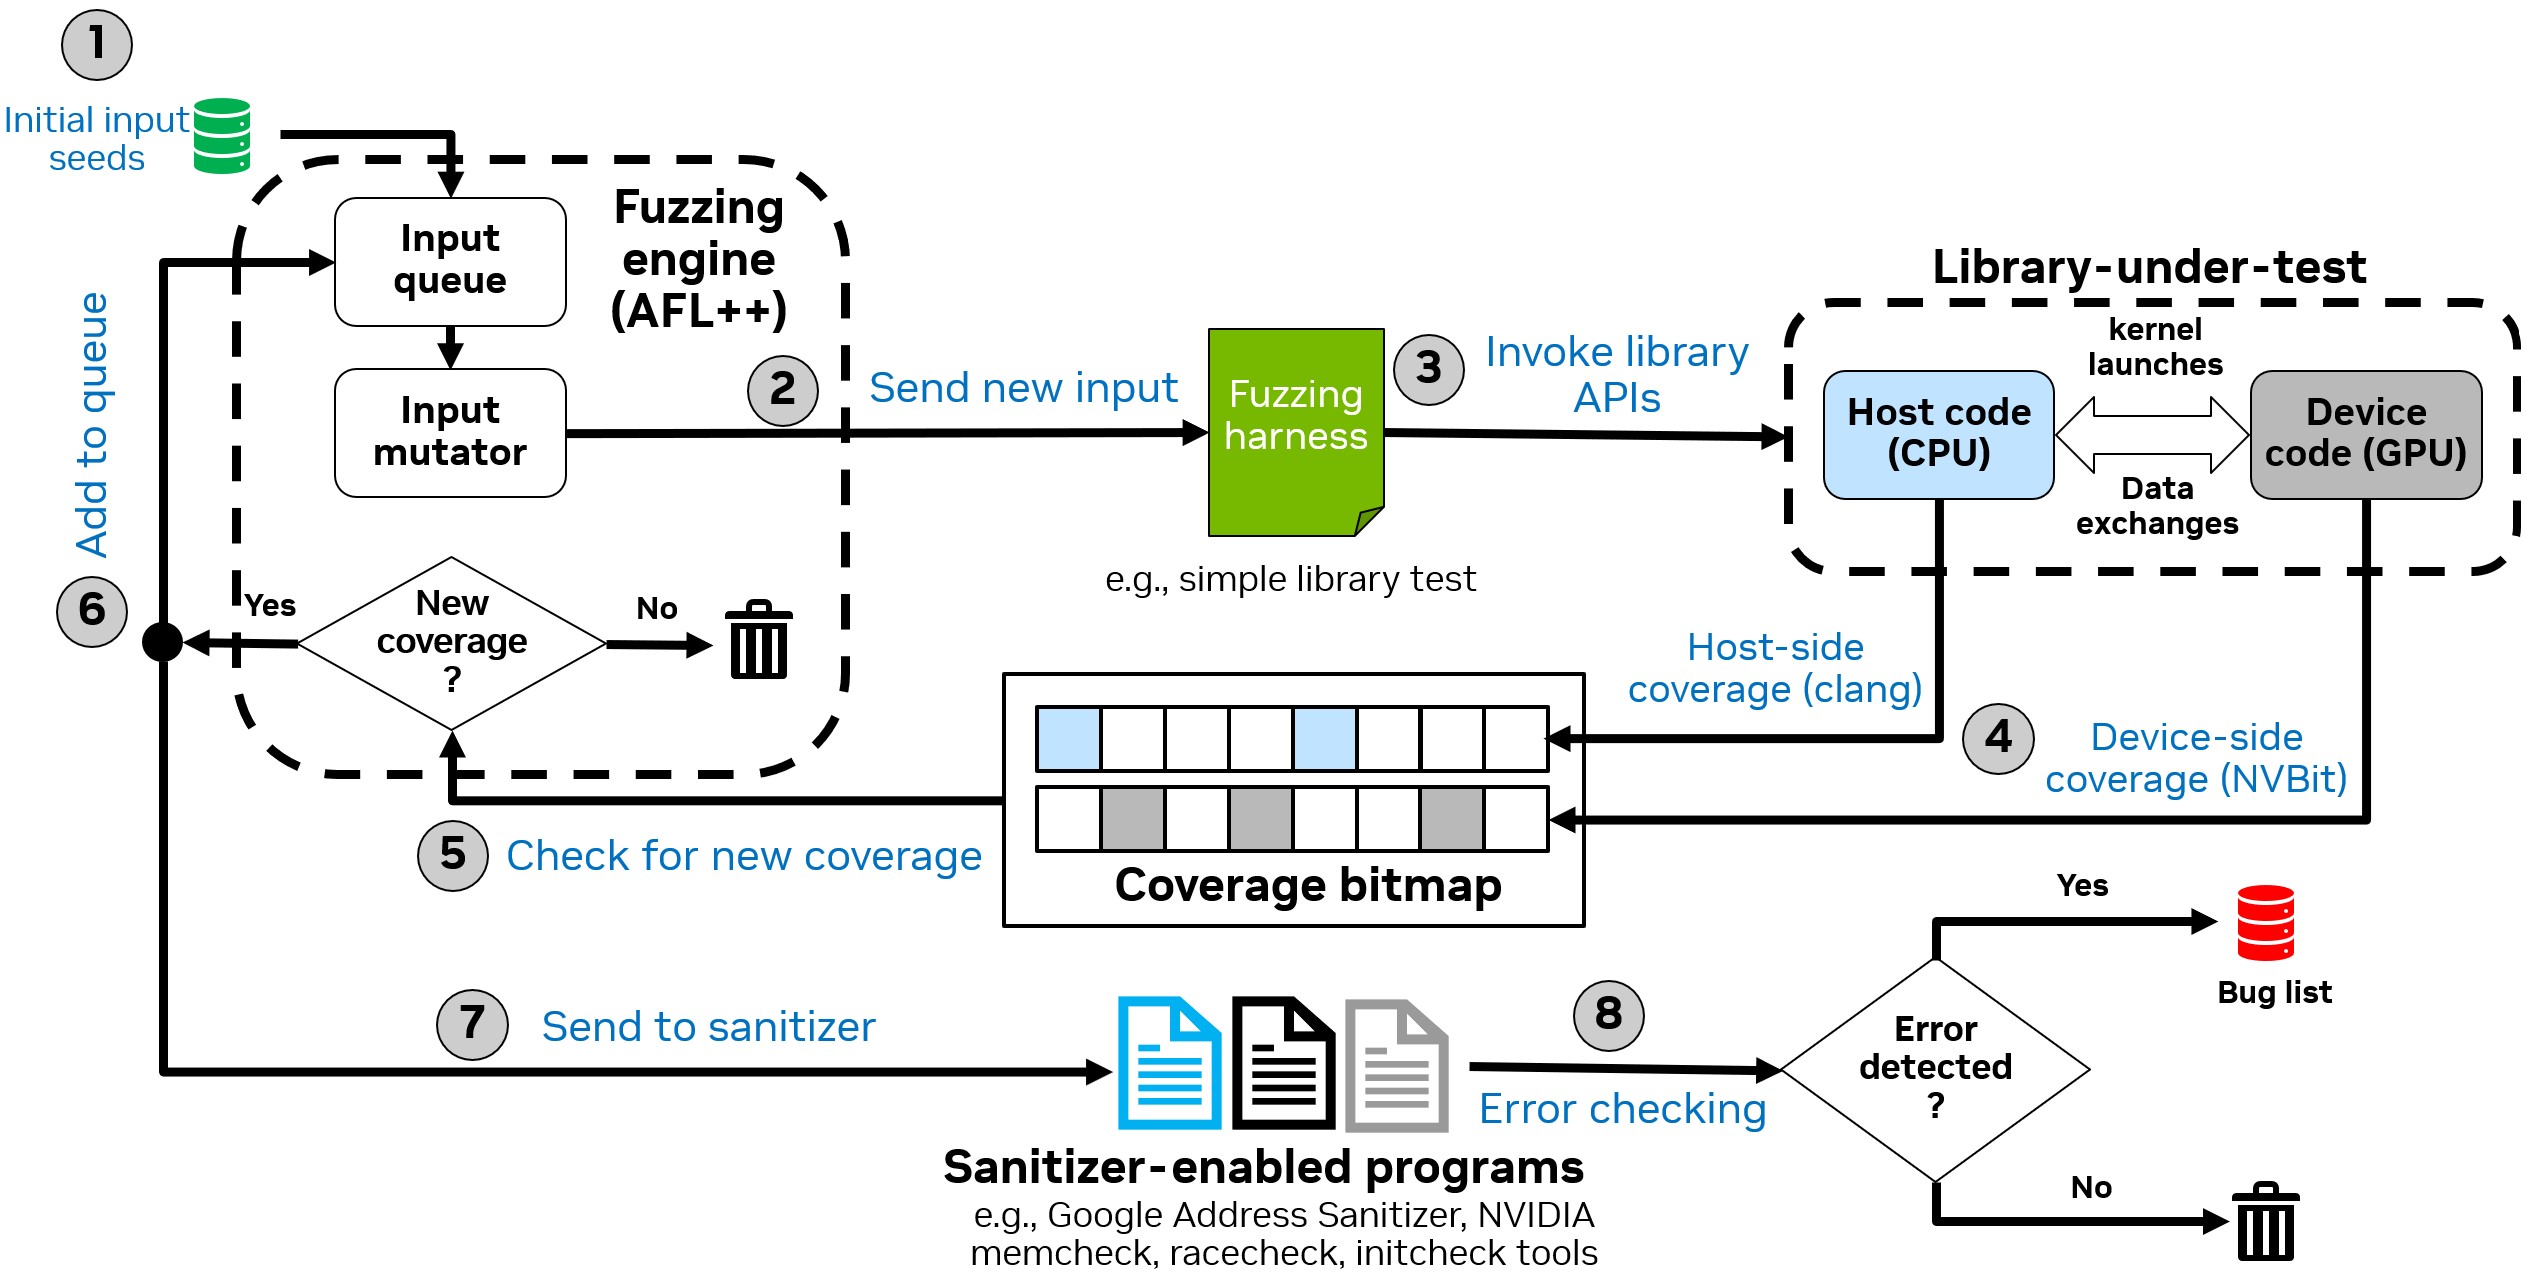
 nvlabs/cufuzz
A GPU-oriented coverage-guided fuzzer for userland CUDA applications
 trailofbits/ruzzy
A coverage-guided fuzzer for pure Ruby code and Ruby C extensions
 zx0cf1/shredder-rs
A high-fidelity x86_64 polymorphic mutation engine focused on instruction-level fragmentation and context preservation.
 trustedsec/lnkmemaybe
Lnk crafting and research tools
 metaredteam/rtx-cve-2023-45779
Proof-of-concept code for Android APEX key reuse vulnerability
 siemens/fluffi
FLUFFI (Fully Localized Utility For Fuzzing Instantaneously) - A distributed evolutionary binary fuzzer for pentesters
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
 synacktiv/dotniet
IDA Pro plugin that imports runtime-resolved symbols in .NET Native binaries, parsing SharedLibrary.dll and its PDB to restore missing imports for…

 hiddenillusion/nomorexor
Tool to help guess a files 256 byte XOR key by using frequency analysis
 altumptic/paranoia
Open reverse engineering — PE/ELF/Mach-O, x86/x64/AArch64, graphs, pseudocode. Rust engine, no network. Desktop · CLI · browser.
 macmade/unicorn-bios
Basic BIOS emulator for Unicorn Engine.
 zznop/bn-uefi-helper
Helper plugin for analyzing UEFI firmware
 peterhackz/zyrox
Zyrox: LLVM based, compile-time obfuscator plugin.

 warpedatom/offsetinspect
PowerShell toolkit for AMSI/Defender detection-boundary analysis and static malware triage maps byte offsets to detection triggers, plus YARA,…
 idiom/pftriage
Python tool and library to help analyze files during malware triage and analysis.
 owl4444/jsdeob-workbench
Reverse engineer obfuscated JavaScript visually. Chain transforms, inspect AST changes, write reusable deobfuscation plugins.








