
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Binary Analysis — Page 33 | Kitploit
Categories

Binary Analysis

Binary reverse engineering, disassembly, decompilation, and patching tools.

Kitploit recommended
Top tools

10 selected
ghidra preview#1

ghidra

GitHubnationalsecurityagency/ghidra
71.1k1 day ago
radare2 preview#2

radare2

GitHubradareorg/radare2
24.5k14h 1m ago
cutter preview#3

cutter

GitHubrizinorg/cutter
19.4k1 day ago
rizin preview#4

rizin

GitHubrizinorg/rizin
4.1k1 day ago
x64dbg preview#5

x64dbg

GitHubx64dbg/x64dbg
49.1k6 days ago
angr preview#6

angr

GitHubangr/angr
9.0k18h 24m ago
capa preview#7

capa

GitHubmandiant/capa
6.1k1 day ago
Detect-It-Easy preview#8

Detect-It-Easy

GitHubhorsicq/detect-it-easy
11.3k1 day ago
LIEF preview#9

LIEF

GitHublief-project/lief
5.5k12h 58m ago
ImHex preview#10

ImHex

GitHubwerwolv/imhex
54.4k27 days ago
NewestRelevanceMost popularRecently updated
1671 results
autoharness preview

autoharness

GitHubparikhakshat/autoharness

A tool that automatically creates fuzzing harnesses based on a library
vulnerability-analysiscode-analysisfuzzing+1
2934 years ago
IDA2Obj preview

IDA2Obj

GitHubjhftss/ida2obj

Static binary instrumentation tool that dumps COFF object files from executables, enabling code/data insertion at any location for black-box fuzzing…
static-analysisreverse-engineeringdebuggers+2
1215 years ago
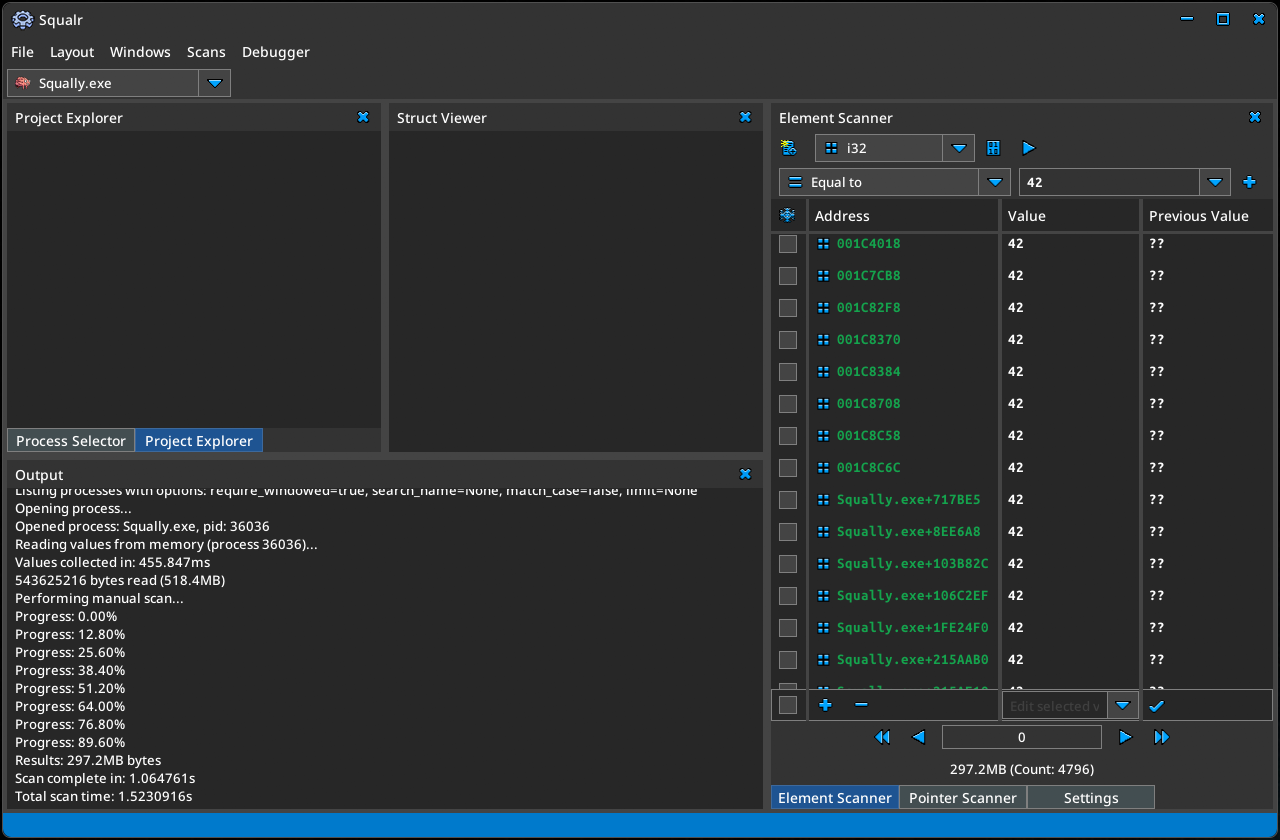
Squalr preview

Squalr

GitHubsqualr/squalr

A generic game/software hacking tool written from the ground up in Rust.
dynamic-analysis-sandboxingmemory-forensicsexploitation+5
1514 months ago
nuitka-static-unpacker preview

nuitka-static-unpacker

GitHubdimareverse/nuitka-static-unpacker

Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.

static-analysisreverse-engineeringforensics+3
1282 months ago
dezlock-dump preview

dezlock-dump

GitHubdougwithseismic/dezlock-dump

Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
reconnaissancememory-forensicsdynamic-code-analysis+6
8217 days ago
EFISwissKnife preview

EFISwissKnife

GitHubgdbinit/efiswissknife

IDA plugin to enhance (U)EFI binary reversing with batch analysis, GUID database, and service usage statistics for firmware security research.
embedded-systems-securityreverse-engineeringhardware-iot-security+2
1599 years ago
krie preview

krie

GitHubgui774ume/krie

Linux Kernel Runtime Integrity with eBPF
defensive-toolsbinary-analysisintrusion-detection
1862 years ago
IoT-Implant-Toolkit preview

IoT-Implant-Toolkit

GitHubarthastang/iot-implant-toolkit

Toolkit for implant attack of IoT devices

embedded-systems-securityiot-securityexploitation+8
1368 years ago
EVENSTAR preview

EVENSTAR

GitHubwinterknife/evenstar

Intel 64/Windows low-level experiments
memory-forensicsexploitationreverse-engineering+5
1081 month ago
CVE-2022-3602 preview

CVE-2022-3602

GitHubcolmmacc/cve-2022-3602

Technical deep-dive and anti-POC for CVE-2022-3602, a punycode buffer overflow in OpenSSL 3.0.x, with reproduction scripts, stack analysis, and…

vulnerability-analysisexploitationcryptography+3
1694 years ago
decomp.anything preview

decomp.anything

GitHubgiveen/decomp.anything

decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge

android-securitystatic-analysisdynamic-code-analysis+7
801 day ago
reverse-engineering-workshop preview

reverse-engineering-workshop

GitHubromainthomas/reverse-engineering-workshop

Slides & Hands-on for the reverse engineering workshop

reverse-engineeringbinary-analysiseducation+1
1813 years ago
IDARustDemangler preview

IDARustDemangler

GitHubtimetravelthree/idarustdemangler

Rust Demangler & Normalizer plugin for IDA
code-analysisreverse-engineeringbinary-analysis
3563 years ago
ghidra-evm preview

ghidra-evm

GitHubadelapie/ghidra-evm

Ghidra module for disassembling, decompiling, and analyzing Ethereum smart contract bytecode. Detects insecure instructions, extracts hidden methods,…
static-analysisvulnerability-analysisreverse-engineering+1
1495 years ago
dd preview

dd

GitHubricccrd/dd

JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…
container-securitydynamic-analysis-sandboxingreverse-engineering+3
2581 month ago
rematch preview

rematch

GitHubnirizr/rematch

REmatch, a complete binary diffing framework that is free and strives to be open source and community driven.

reverse-engineeringutilities-frameworksbinary-analysis
1557 years ago
rasputin preview

rasputin

GitHubfrenchyeti/rasputin

Ressources and papers related to my conferences and work on (un)RASPs. These work is in progress, please be patient :) Don't hesitate to contribute /…
android-securityreverse-engineeringmalware-analysis+4
621 month ago
shellex preview

shellex

GitHubtherealdreg/shellex

C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…


exploitationreverse-engineeringshellcode+5
1123 years ago
Previous1…323334…93Next







