
 #1
Tools for testing and implementing authentication mechanisms (e.g., MFA, SSO) and authorization policies.
Kitploit recommended

 0xblackash/cve-2025-31161
CVE-2025-31161
 kc57/jitbit_helpdesk_auth_bypass
Utility to derive the shared secret on a JitBit Helpdesk install which can be used for authentication bypass (CVE-2017-18486)
 philippeabraxas-jpg/tbp-network
Theory and implemantation of the TBP protocol to secure networked AI in small to open web networks
 berraesen/nextjs-middleware-auth-bypass-lab
Bu laboratuvar ortamını sıfırdan kendim oluşturdum. Next.js uygulaması içerisinde giriş, ana sayfa ve admin sayfalarını hazırladım. Middleware ile…
 mr-zapi/cve-2024-54085
Just poc for CVE 2024-54085
 arvion-agent/next-cve-2025-29927
CVE-2025-29927 Authorization Bypass in Next.js Middleware
 digicred-oss/caos-os
Customer Assurance Operating System. Answer the security questionnaires your customers send you, once.
 realalexandergeorgiev/artifactory-cve-2026-82329-poc.py
CVE-2026-82329 — JFrog Artifactory unauthenticated authentication bypass ("phantom join key" -> forged service admin token)
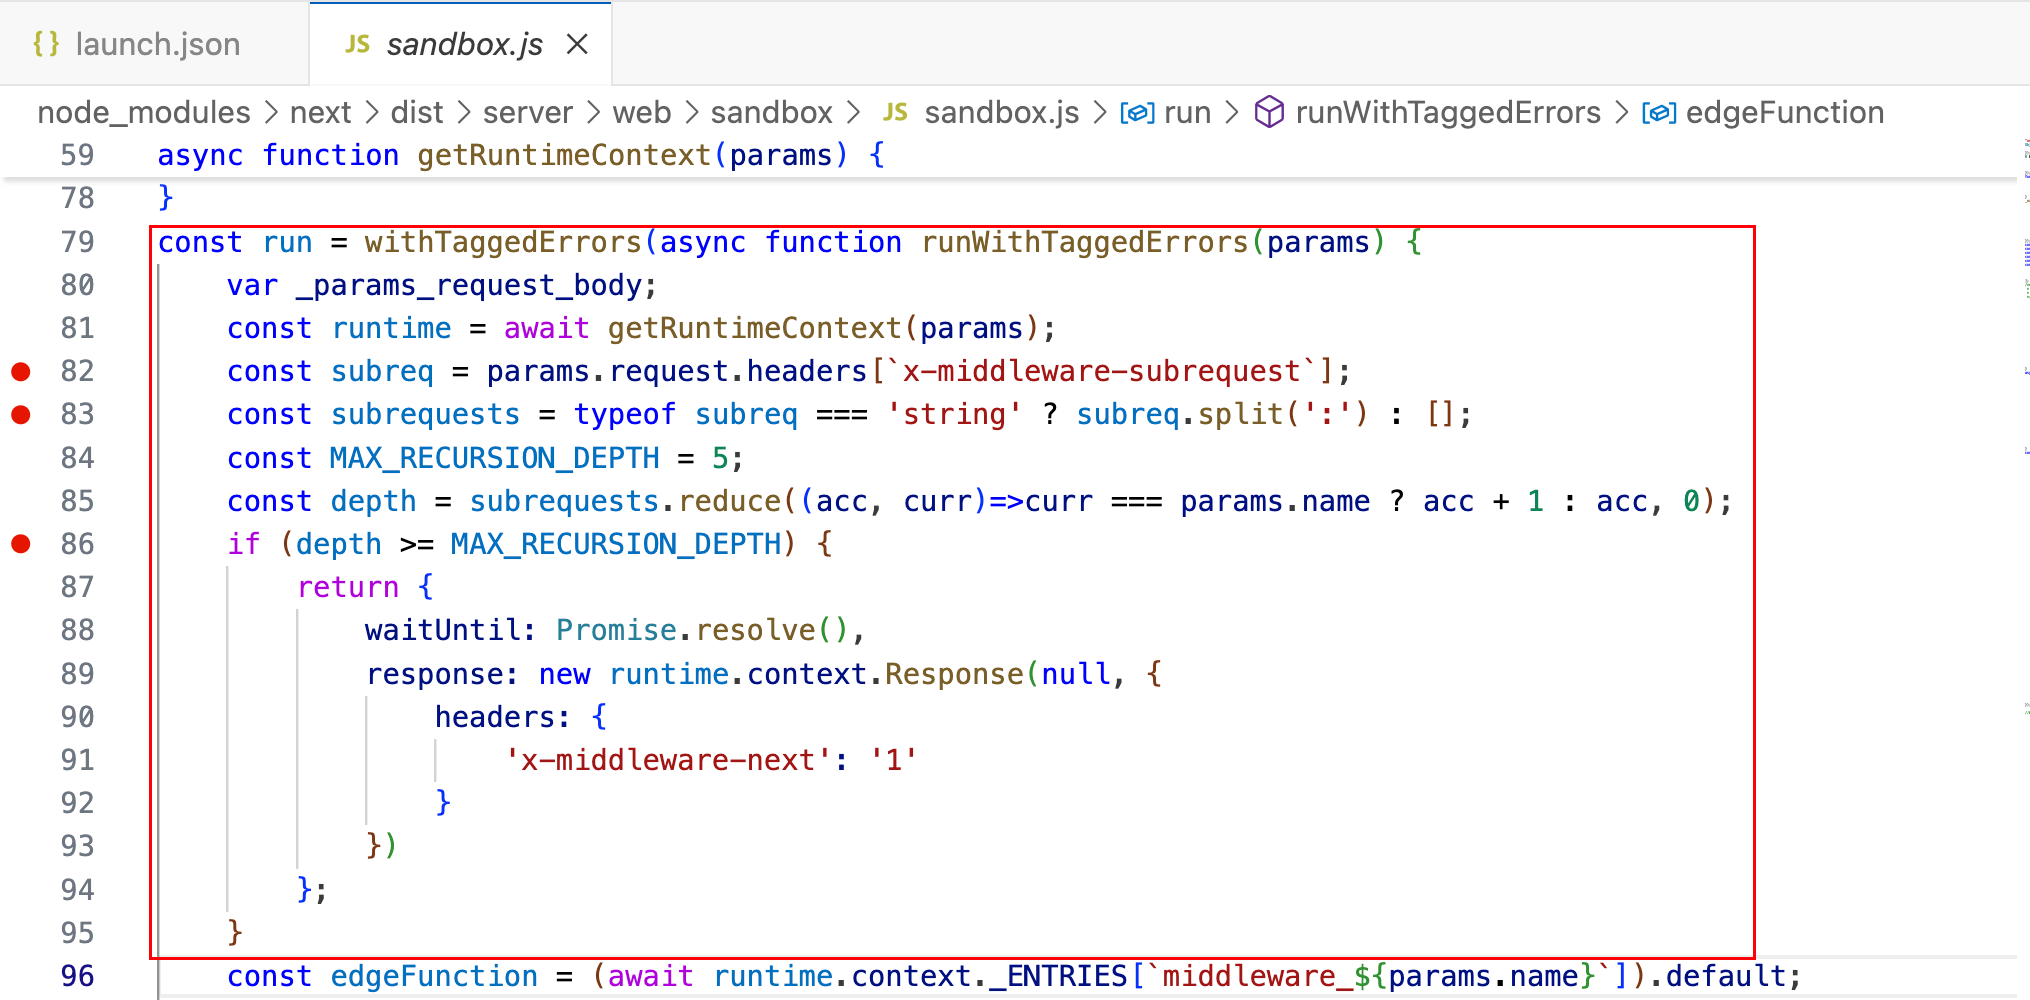 oyst3r1ng/cve-2025-29927
Next.js Middleware Auth Bypass
 kmaruthisrikar/cve-2026-41940-cpanel-auth-bypass-exploit
Exploit for CVE-2026-41940, an authentication bypass in cPanel/WHM, allowing unauthenticated attackers to gain root access via session injection and…
 fredevsec/cve-2026-0073
0-Click RCE Android Adb TLS Wireless Debugging
 umakant76705/cve-2022-22978
Step-by-step demonstration of CVE-2022-22978 authorization bypass in Spring Security's RegexRequestMatcher, with vulnerable app setup, payload…
 0xblackash/cve-2026-41940
CVE-2026-41940
 0xabdoulaye/cpanel-cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940, a critical cPanel/WHM authentication bypass via CRLF injection, enabling unauthenticated root access and…
 johanneslks/cve-2026-33186
gRPC-Go RBAC Authorization Policy Bypass via Missing `:path` Slash (Auth Bypass)
 abraxas/pfsense-api-fleet-jwt
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - IDOR - one controller JWT is a fleet token
 rajsidwadkar/uap-protocol
A unified, security-first wire protocol for tool access and agent coordination. UAP eliminates CVE-2025-49596 and MCP tool-poisoning vulnerabilities…
 abraxas/pfsense-api-export-key-get
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - GET export-key private keys








