
 #1
Tools for testing and implementing authentication mechanisms (e.g., MFA, SSO) and authorization policies.
Kitploit recommended

 cerberusmrxi/discuz-x5.0-authentication-bypass-exploit-framework
Discuz! X5.0 Authentication Bypass Exploit Framework (CVE-2026-49952) - Critical vulnerability allowing unauthenticated database backup access via…
 0xdak/cve-2026-59243_exploit
Exploit for Apache Airflow FAB OAuth authentication bypass (CVE-2026-59243) that achieves admin access and remote code execution by triggering a…
 eqstlab/cve-2026-20896
Gitea Docker Image Authentication Bypass
 0xgh057r3c0n/cve-2026-41940
cPanel & WHM - Authentication Bypass via Session-File CRLF Injection
 zer0dayf/cve-2026-15013
Exploit for CVE-2026-15013: unauthenticated SAML auth bypass via algorithm confusion. Forges SAML responses to gain admin access and deploy…
 george0papasotiriou/cve-2026-22005-oauth-2.0-device-code-phishing-short-interval-
Proof-of-concept for CVE-2026-22005 showing OAuth 2.0 device code phishing via too-short polling interval, with vulnerable Flask server and exploit…
 xenom0rph97/cve-2024-30896
Proof-of-concept exploit for CVE-2024-30896, a privilege escalation vulnerability in InfluxDB allowing allAccess token holders to gain operator-level…
 ilhomjonr/cve-2026-71518
Advisory and PoC for an unauthenticated authorization bypass in Typemill media downloads, using path-equivalent URL variants to access…
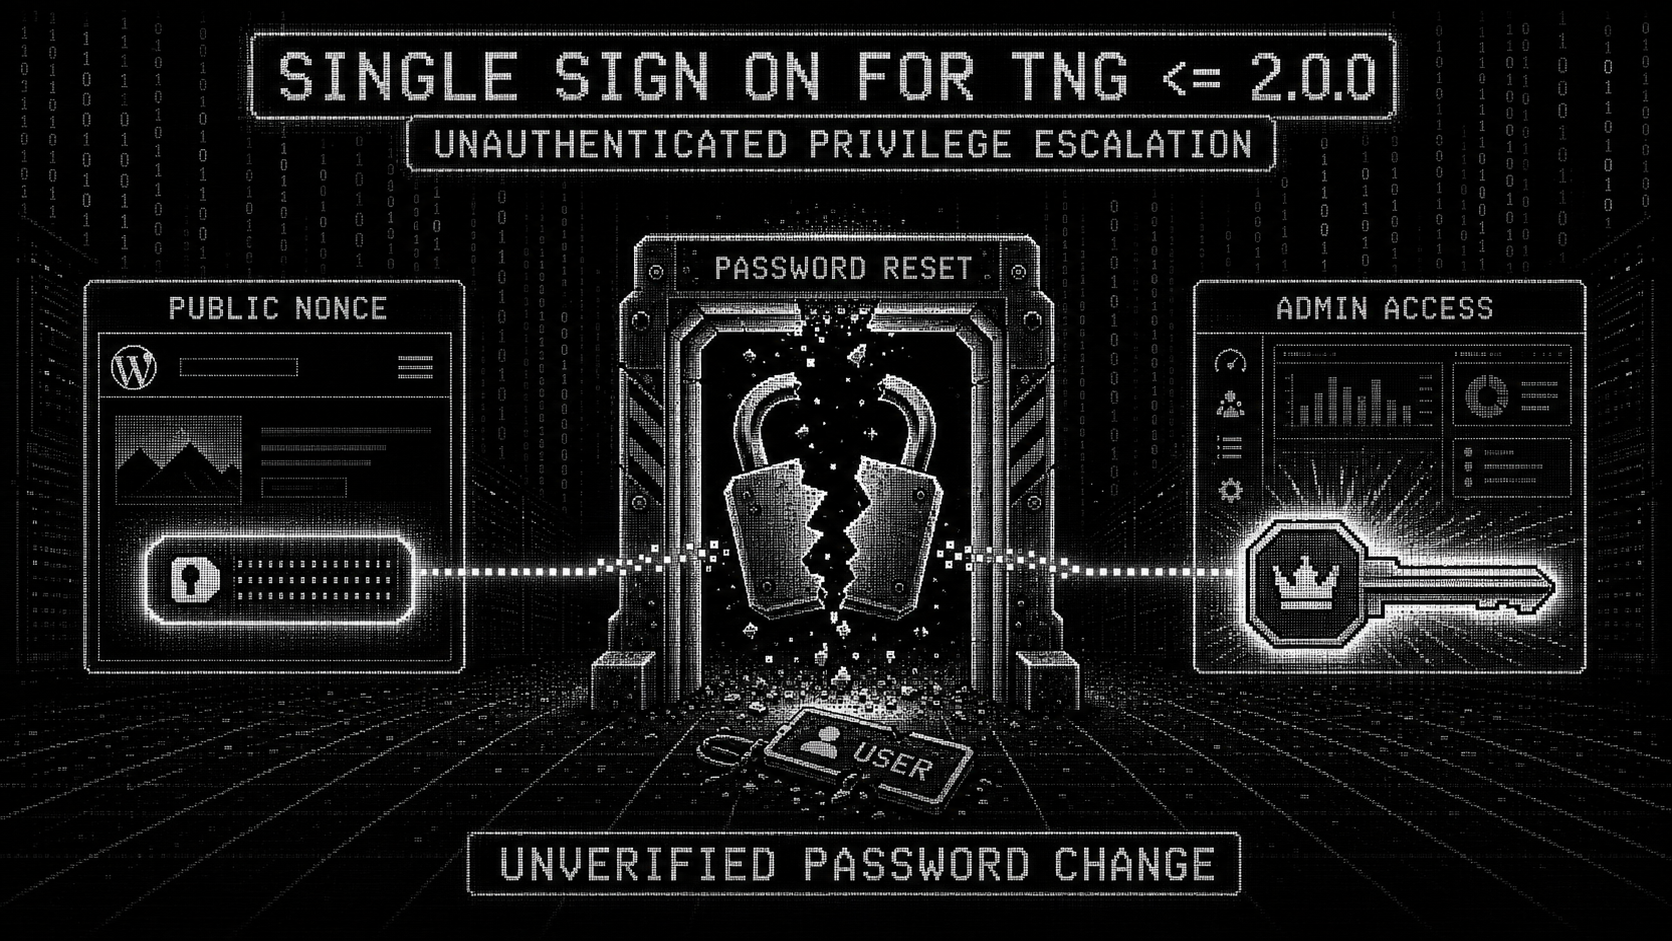 instructor-admin/cve-2026-15964-poc
PoC & checker for CVE-2026-15964 - unauthenticated password change in the WordPress plugin Single Sign On For TNG <= 2.0.0 (CVSS 9.8)
 mrcord77/rust_citadel
Post-quantum hybrid encryption library combining X25519 + ML-KEM-768 with AES-256-GCM
 sag-asab/cve-2026-19598
Custom Content Types and Fields plugin for WordPress
 krakeneu/cve-2026-54121-certighost
CVE-2026-54121(CertiGhost) without MachineAccountQuota POC
 0xgh057r3c0n/cve-2025-34077
Poc for Unauthenticated Admin Session Hijack - Pie Register Plugin (≤ 3.7.1.4)
 0xterror/cve-2026-8181
Exploit PoC for WordPress Burst Statistics authentication bypass allowing unauthenticated admin impersonation via crafted Authorization header.
 synacktiv/sap_logon_ticket
General toolkit related to SAP's SSO mechanism : the Logon Tickets
 bombobombone/cve-2026-73309
Proof-of-concept and technical write-up for CVE-2026-73309, an OAuth2 authentication bypass in XenForo before 2.3.13. Demonstrates empty…
 bombobombone/cve-2026-73317
Proof-of-concept exploit and technical write-up for CVE-2026-73317, an authorization bypass in XenForo allowing limited admins to approve content as…
 george0papasotiriou/cve-2026-21017-ldap-anonymous-bind-privilege-escalation
Python proof-of-concept for LDAP anonymous bind privilege escalation, simulating insecure ACLs to create admin users via unauthenticated LDAP binds.








