
 #1
Tools for testing and implementing authentication mechanisms (e.g., MFA, SSO) and authorization policies.
Kitploit recommended

 philippeabraxas-jpg/tbp-network
Theory and implemantation of the TBP protocol to secure networked AI in small to open web networks
 0xblackash/cve-2025-31161
CVE-2025-31161
 berraesen/nextjs-middleware-auth-bypass-lab
Bu laboratuvar ortamını sıfırdan kendim oluşturdum. Next.js uygulaması içerisinde giriş, ana sayfa ve admin sayfalarını hazırladım. Middleware ile…
 mr-zapi/cve-2024-54085
Just poc for CVE 2024-54085
 arvion-agent/next-cve-2025-29927
CVE-2025-29927 Authorization Bypass in Next.js Middleware
 digicred-oss/caos-os
Customer Assurance Operating System. Answer the security questionnaires your customers send you, once.
 realalexandergeorgiev/artifactory-cve-2026-82329-poc.py
CVE-2026-82329 — JFrog Artifactory unauthenticated authentication bypass ("phantom join key" -> forged service admin token)
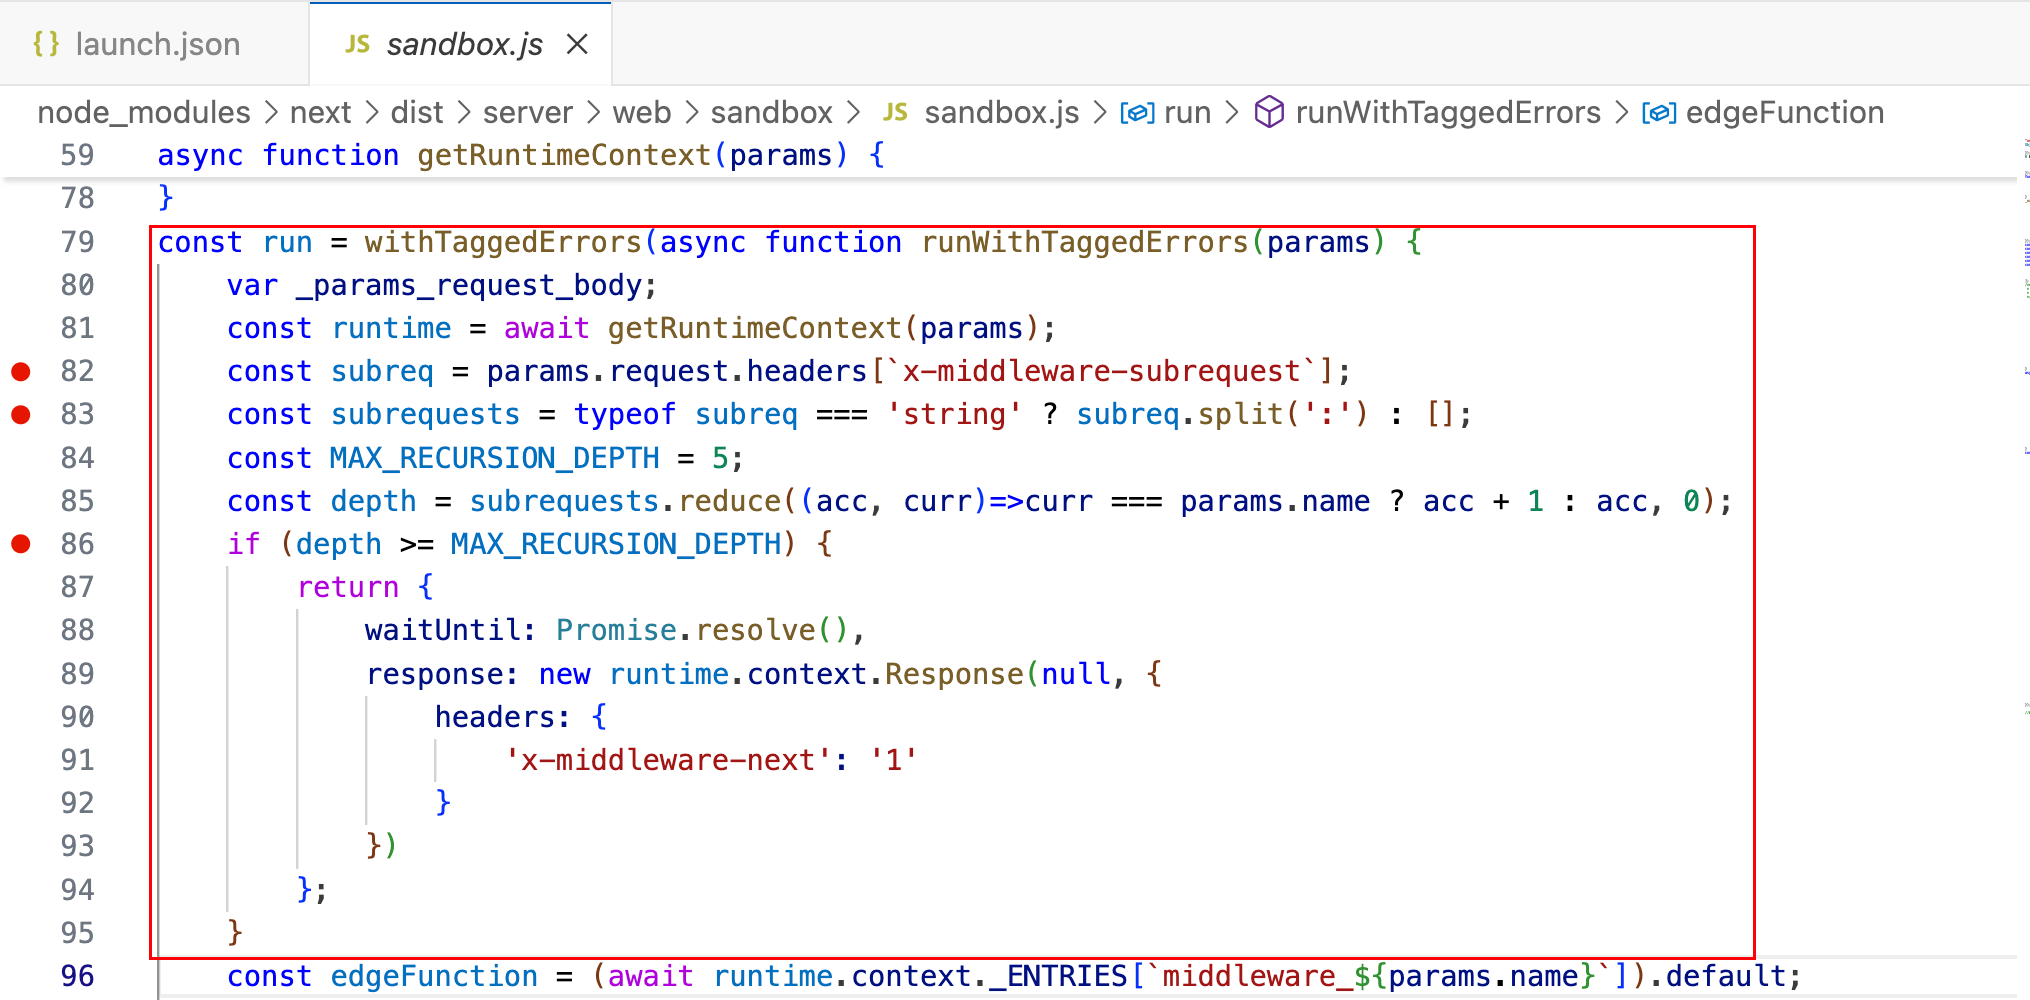 oyst3r1ng/cve-2025-29927
Next.js Middleware Auth Bypass
 kmaruthisrikar/cve-2026-41940-cpanel-auth-bypass-exploit
Exploit for CVE-2026-41940, an authentication bypass in cPanel/WHM, allowing unauthenticated attackers to gain root access via session injection and…
 fredevsec/cve-2026-0073
0-Click RCE Android Adb TLS Wireless Debugging
 umakant76705/cve-2022-22978
Step-by-step demonstration of CVE-2022-22978 authorization bypass in Spring Security's RegexRequestMatcher, with vulnerable app setup, payload…
 0xabdoulaye/cpanel-cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940, a critical cPanel/WHM authentication bypass via CRLF injection, enabling unauthenticated root access and…
 abraxas/pfsense-api-fleet-jwt
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - IDOR - one controller JWT is a fleet token
 rajsidwadkar/uap-protocol
A unified, security-first wire protocol for tool access and agent coordination. UAP eliminates CVE-2025-49596 and MCP tool-poisoning vulnerabilities…
 abraxas/pfsense-api-export-key-get
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - GET export-key private keys
 galaxy-sc/cve-2026-0920-wordpress-la-studio-exploit
Proof-of-concept exploit for CVE-2026-0920 in LA-Studio Element Kit, enabling unauthenticated privilege escalation to administrator via crafted AJAX…
 edtrackai/nextjs-supabase-stripe-security-checker
Local static security scanner for Next.js, Supabase and Stripe apps: 24 AST-based checks for leaked keys, missing RLS and grants, unsafe webhooks.…
 nxploited/cve-2025-14440
JAY Login & Register <= 2.4.01 - Authentication Bypass via Cookie








