
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-34077 — Poc for Unauthenticated Admin Session Hijack - Pie Register Plugin (≤ 3.7.1.4) | Kitploit

Tools/GitHubGitHub/0xgh057r3c0n/cve-2025-34077
Authentication & AuthorizationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & Education
GitHub0xgh057r3c0n/cve-2025-34077

CVE-2025-34077

Poc for Unauthenticated Admin Session Hijack - Pie Register Plugin (≤ 3.7.1.4)

View Repository
3331 year agoNot yet reviewed
Share

WordPress Logo

CVE-2025-34077

Unauthenticated Admin Session Hijack - Pie Register Plugin (≤ 3.7.1.4)


📌 Description

This exploit targets a vulnerability in the Pie Register WordPress plugin (versions ≤ 3.7.1.4), allowing unauthenticated session hijacking of admin accounts.

🛡️ This tool is for authorized testing and research only. Do not use it on systems you do not own or have explicit permission to test.
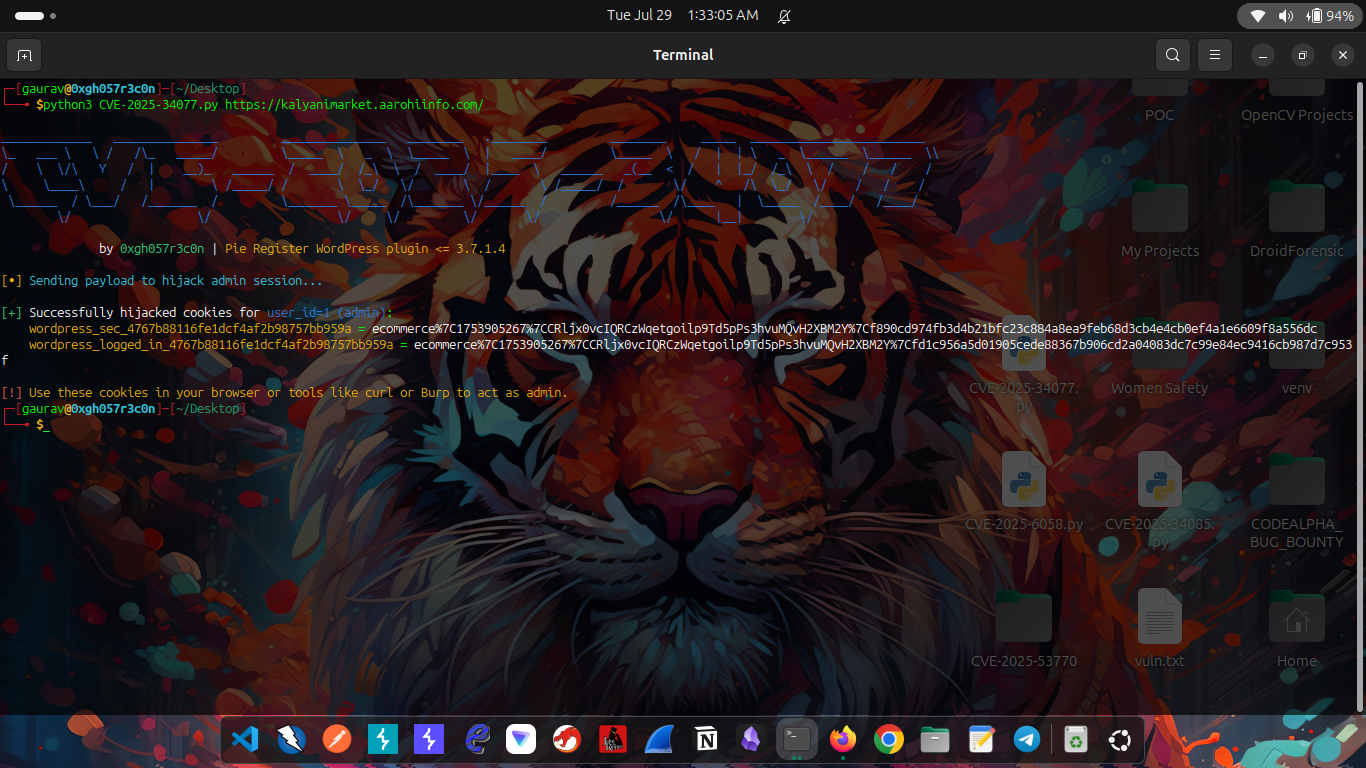

🧪 Proof of Concept

PoC Screenshot

---

🚀 Usage

python3 CVE-2025-34077.py http://target.site

Example:

python3 CVE-2025-34077.py http://example.com

✅ Features

  • Sends crafted POST payload to target site
  • Extracts valid Set-Cookie values from unauthenticated response
  • Confirms exploit success with cookie details
  • Works with tools like Burp Suite or browser dev tools

🧠 Technical Details

  • Vulnerability Type: Auth Bypass / Session Hijack
  • Plugin: Pie Register for WordPress
  • Affected Versions: ≤ 3.7.1.4
  • Vector: Crafted POST request to login endpoint
  • Impact: Attacker gains administrator-level access via hijacked cookies

⚠️ Disclaimer

This script is provided for:

  • Educational purposes
  • Authorized penetration testing
  • Security research

You are fully responsible for any misuse. Unauthorized use of this tool may violate laws.


👤 Author

  • Handle: 0xgh057r3c0n
  • GitHub: github.com/0xgh057r3c0n/CVE-2025-34077

📄 License

This project is licensed under the MIT License.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    668
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    496
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    394
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    339
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    254

Explore all tools

Browse our collection of tools

View all tools →





