
 #1
AI-powered decompilation, binary analysis, code summarization, and malware analysis tools.
Kitploit recommended

 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 inokinoki/attesor
AI-powered reverse-engineering of Rosetta (2 for Linux). Disclaimer: due to the user agreement, I will not touch the code. All is done by AI, so…
 fadi002/de4py
The ultimate AI-powered toolkit for python reverse engineering
 neuromancer/rats-re
Reconstructs legacy Windows binaries into C source by pairing Ghidra decompiler exports with local LLMs, producing compile-checked candidates and…
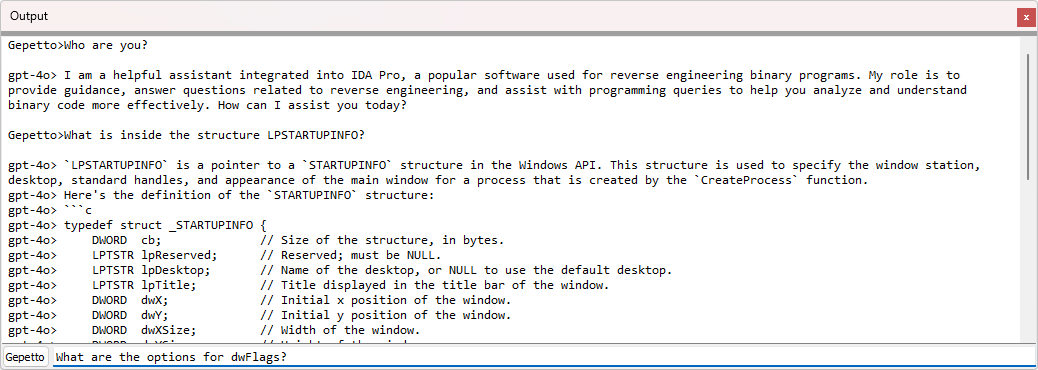 justicerage/gepetto
IDA plugin which queries language models to speed up reverse-engineering
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
 euva-project/euva
A lightweight hex editor and decompiler to solve your binary file analysis problems.
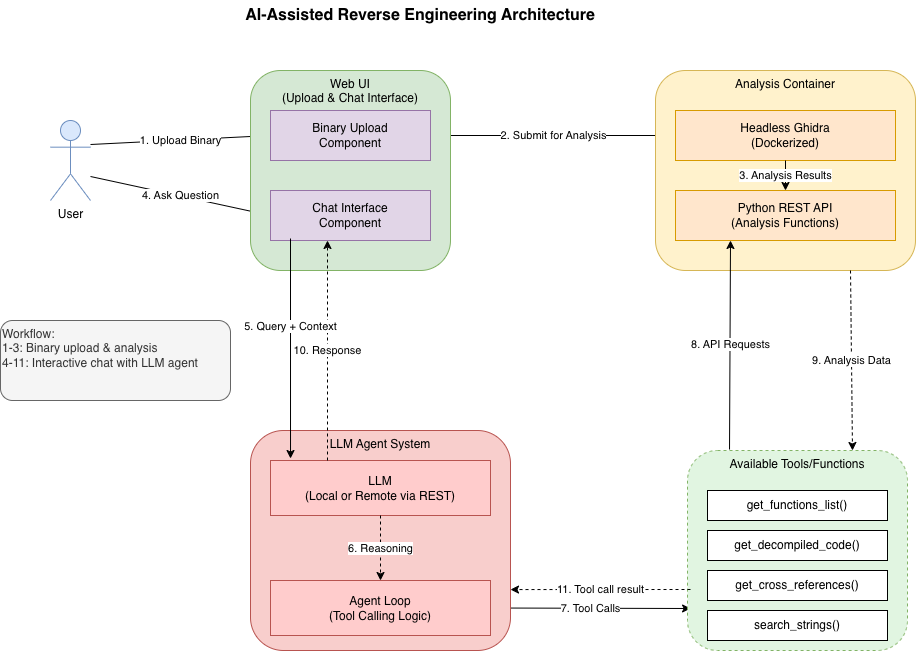 biniamf/ai-reverse-engineering
AI-Assisted Reverse Engineering with Ghidra
 allthingsida/allthingsida
Repository for the code snippets from the AllThingsIDA video channel
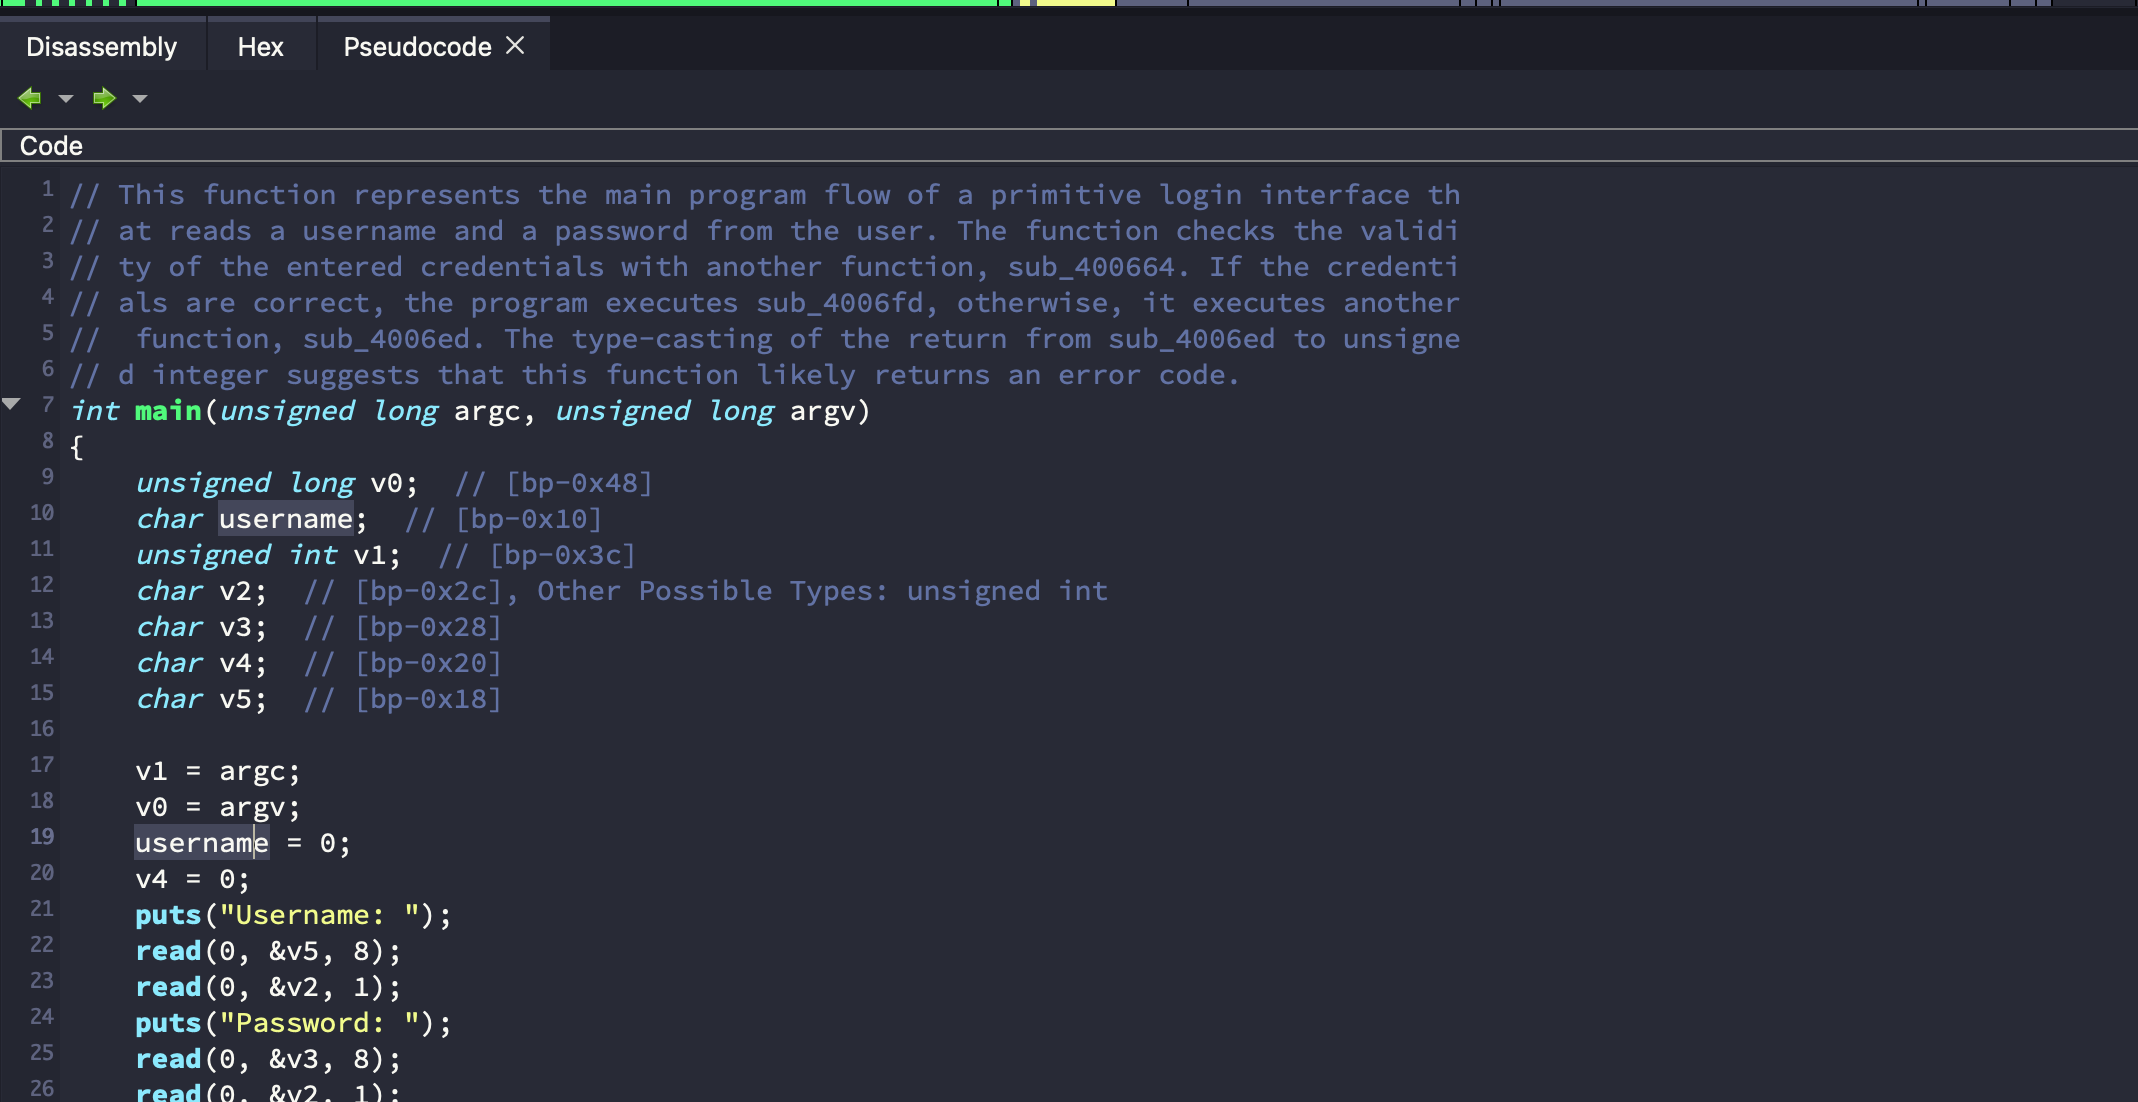 mahaloz/daila
A decompiler-agnostic plugin for interacting with AI in your decompiler. GPT, Claude, and local models supported!
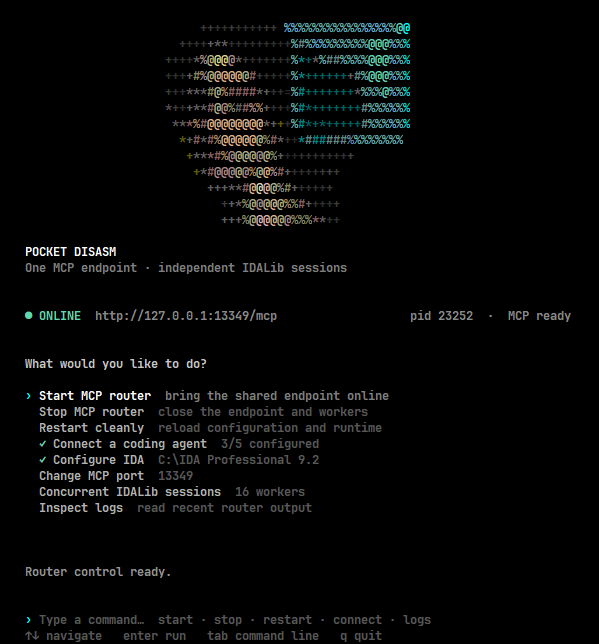 whoisqwerz/pocket_disasm
Multi-session IDALib MCP router for coding agents. Analyze multiple binaries in parallel with IDA-compatible reverse engineering tools.
 ggfuchsi-oss/spectrida-reverse_engineering_stack
Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…
 llvmparty/striga
Experimental x86-64 to LLVM IR lifter in Python that translates machine code into analyzable IR for reverse engineering, optimization, and VM handler…
 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
 martyx00/vulnfanatic-ng
BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.
 gmh5225/enigma-
C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 infobyte/isa_recovery
ISA Recovery








