
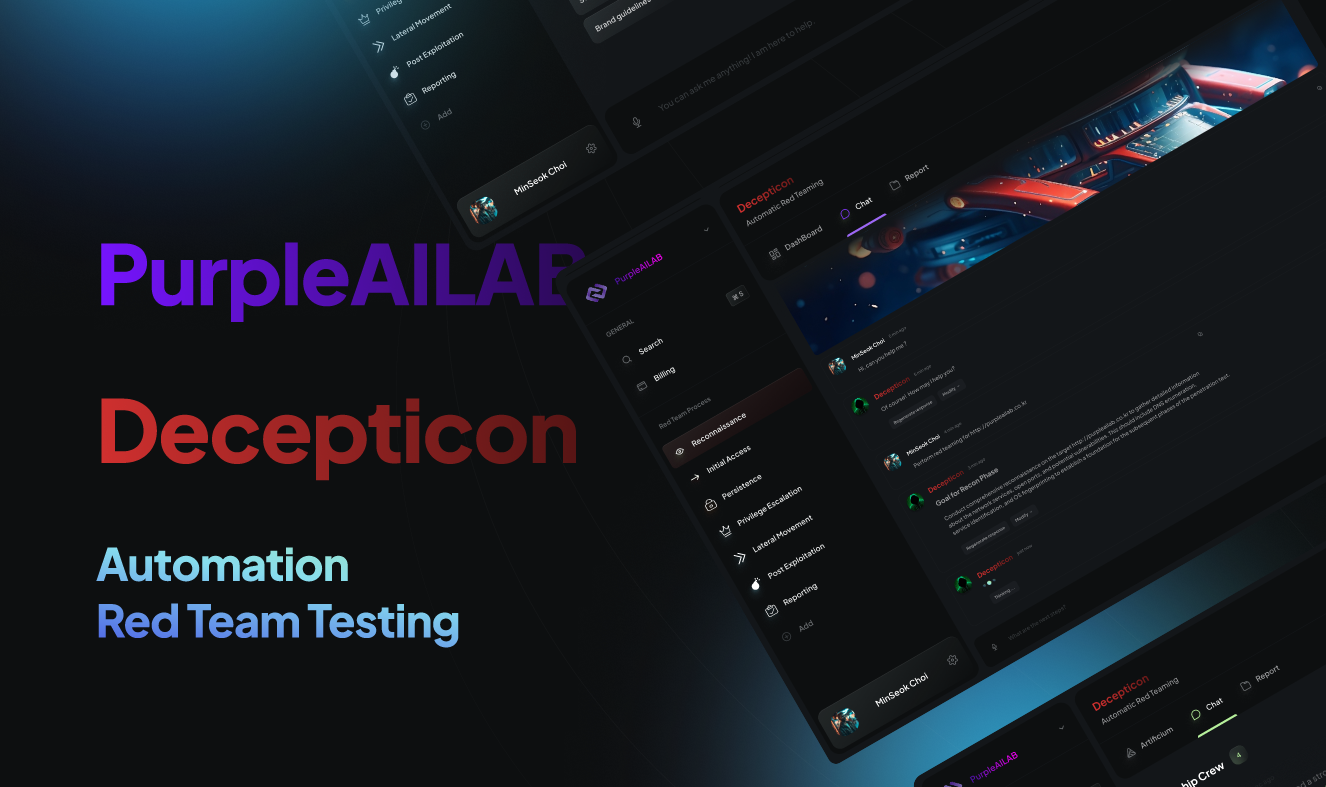
Decepticon
 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
penetration-testing-frameworksprivilege-escalationreconnaissance+9
5.0kvor 8h 15m
purpleailab/decepticonAutonomous Hacking Agent for Red Team
 bigbodycobain/shadowbroker
Real-time geospatial OSINT platform aggregating 60+ public telemetry feeds (ADS-B, AIS, satellites, CCTV) into a unified map with server-side recon…
 vulncheck-oss/go-exploit
Go-basiertes Exploit-Entwicklungsframework mit integrierten Phasen für Zielverifikation, Versionsscan, Exploitation und C2. Unterstützt mehrere…
 node9-ai/node9-proxy
Zugriffskontrolle für KI-Agenten. Legen Sie fest, was Claude Code, Codex, Gemini, Cursor und jeder MCP-Server tun dürfen, prüfen Sie riskante…
 capesandbox/cape-parsers
CAPE-Kern- und Community-Parser
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 manuelschipper/nah
a guard that blocks catastrophic agent actions
 pennyw0rth/netexec
Post-Exploitation-Framework für automatisierte Netzwerk-Authentifizierungstests, Credential-Harvesting und laterale Bewegung in Windows/AD-Umgebungen…
 beefproject/beef
Das Browser-Exploitation-Framework-Projekt
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
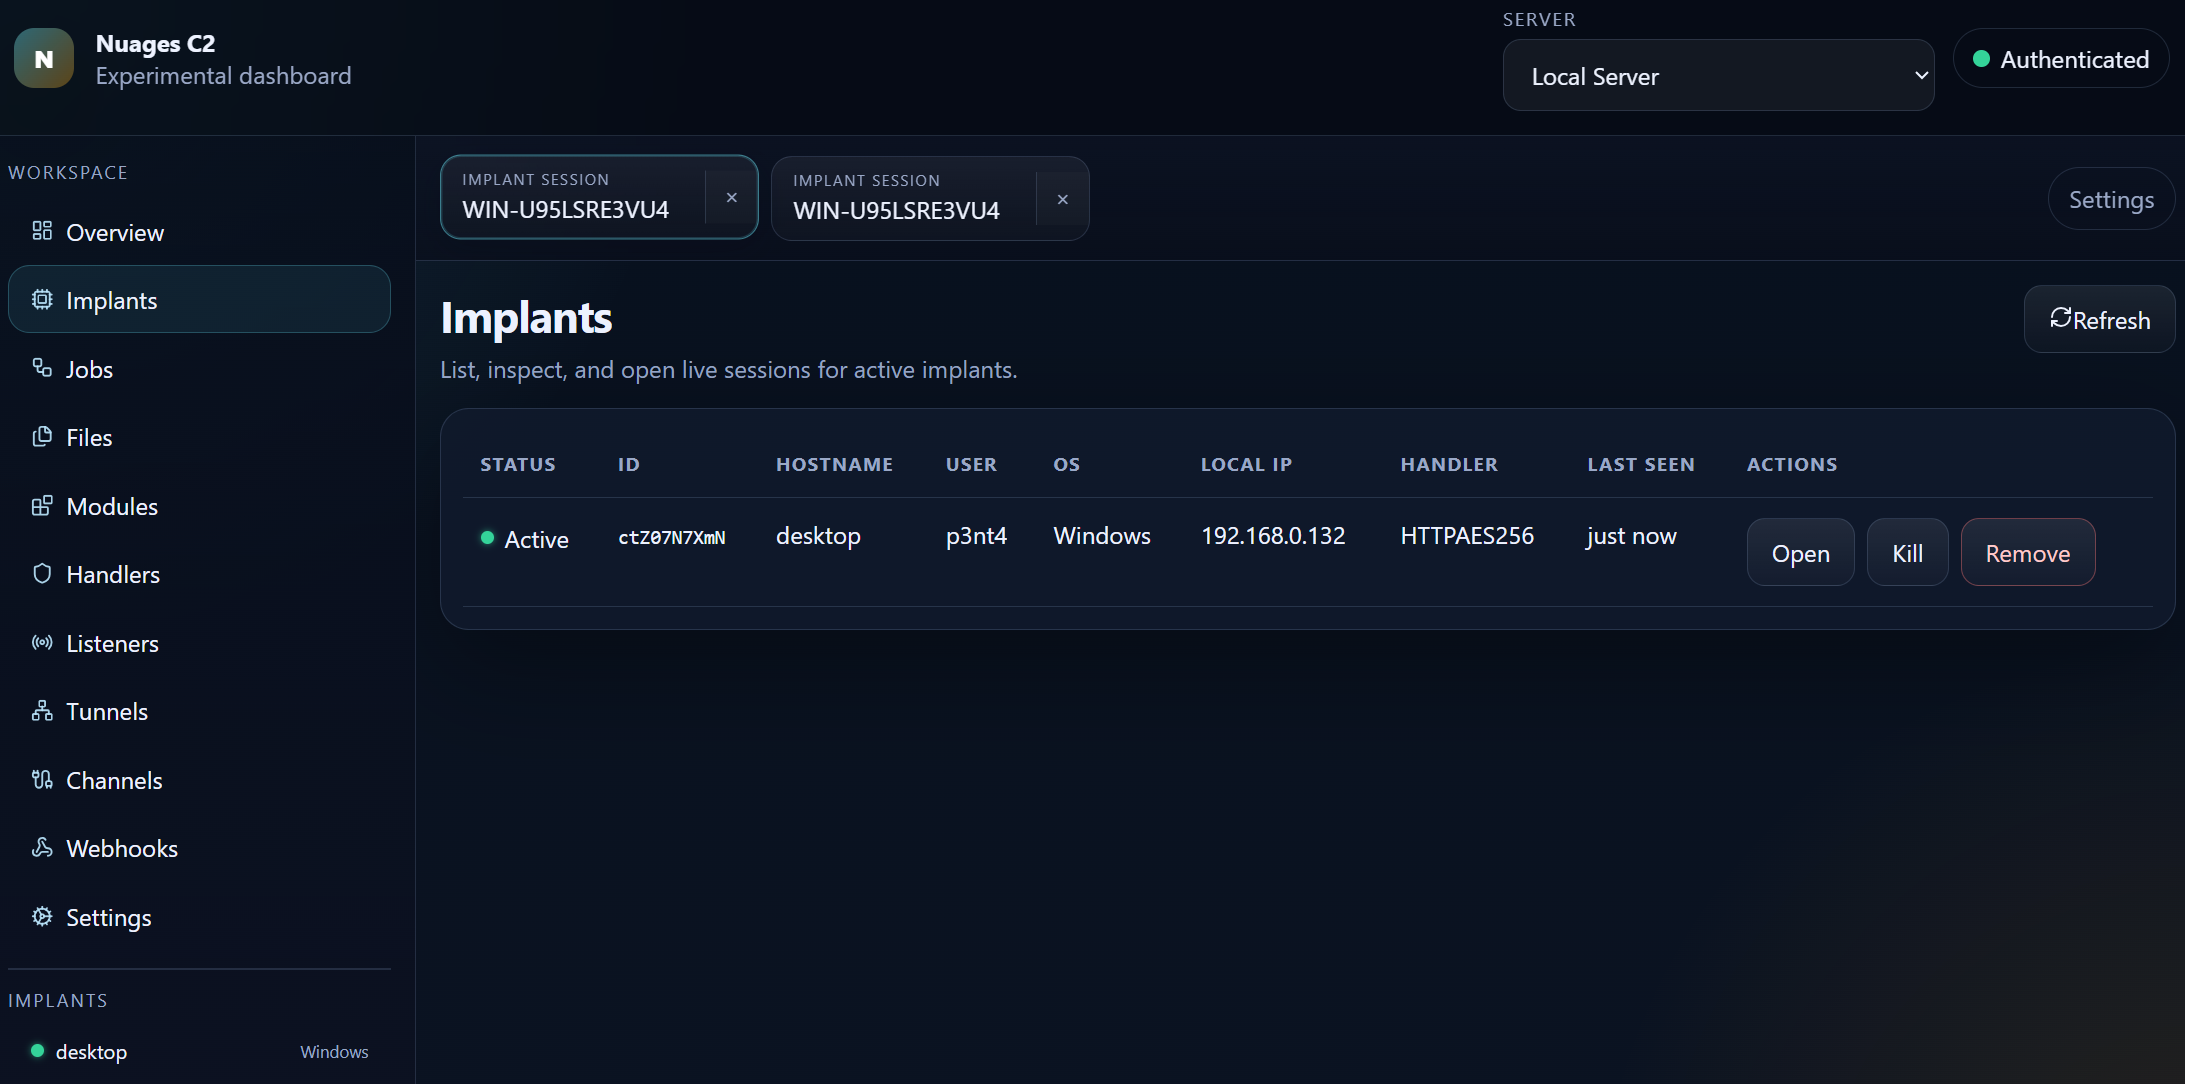 p3nt4/nuages
Ein modulares C2-Framework
 rapid7/metasploit-framework
Open-Source-Exploitation-Framework mit modularem Payload-, Encoder- und Hilfssystem für Penetrationstests, Schwachstellenvalidierung und…
 goshs-labs/goshs
Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…
 oyesanyf/oshoosiclaw
Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
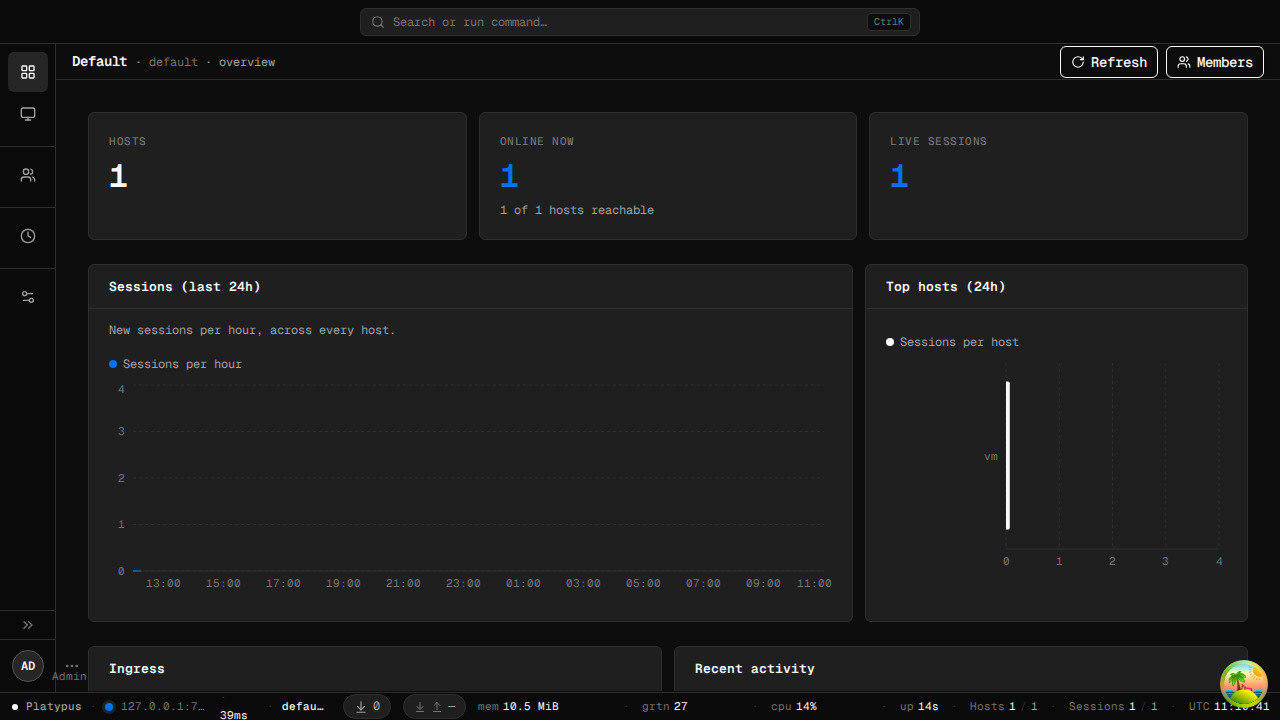 wangyihang/platypus
:hammer: Ein moderner, plattformübergreifender Maschinenmanager
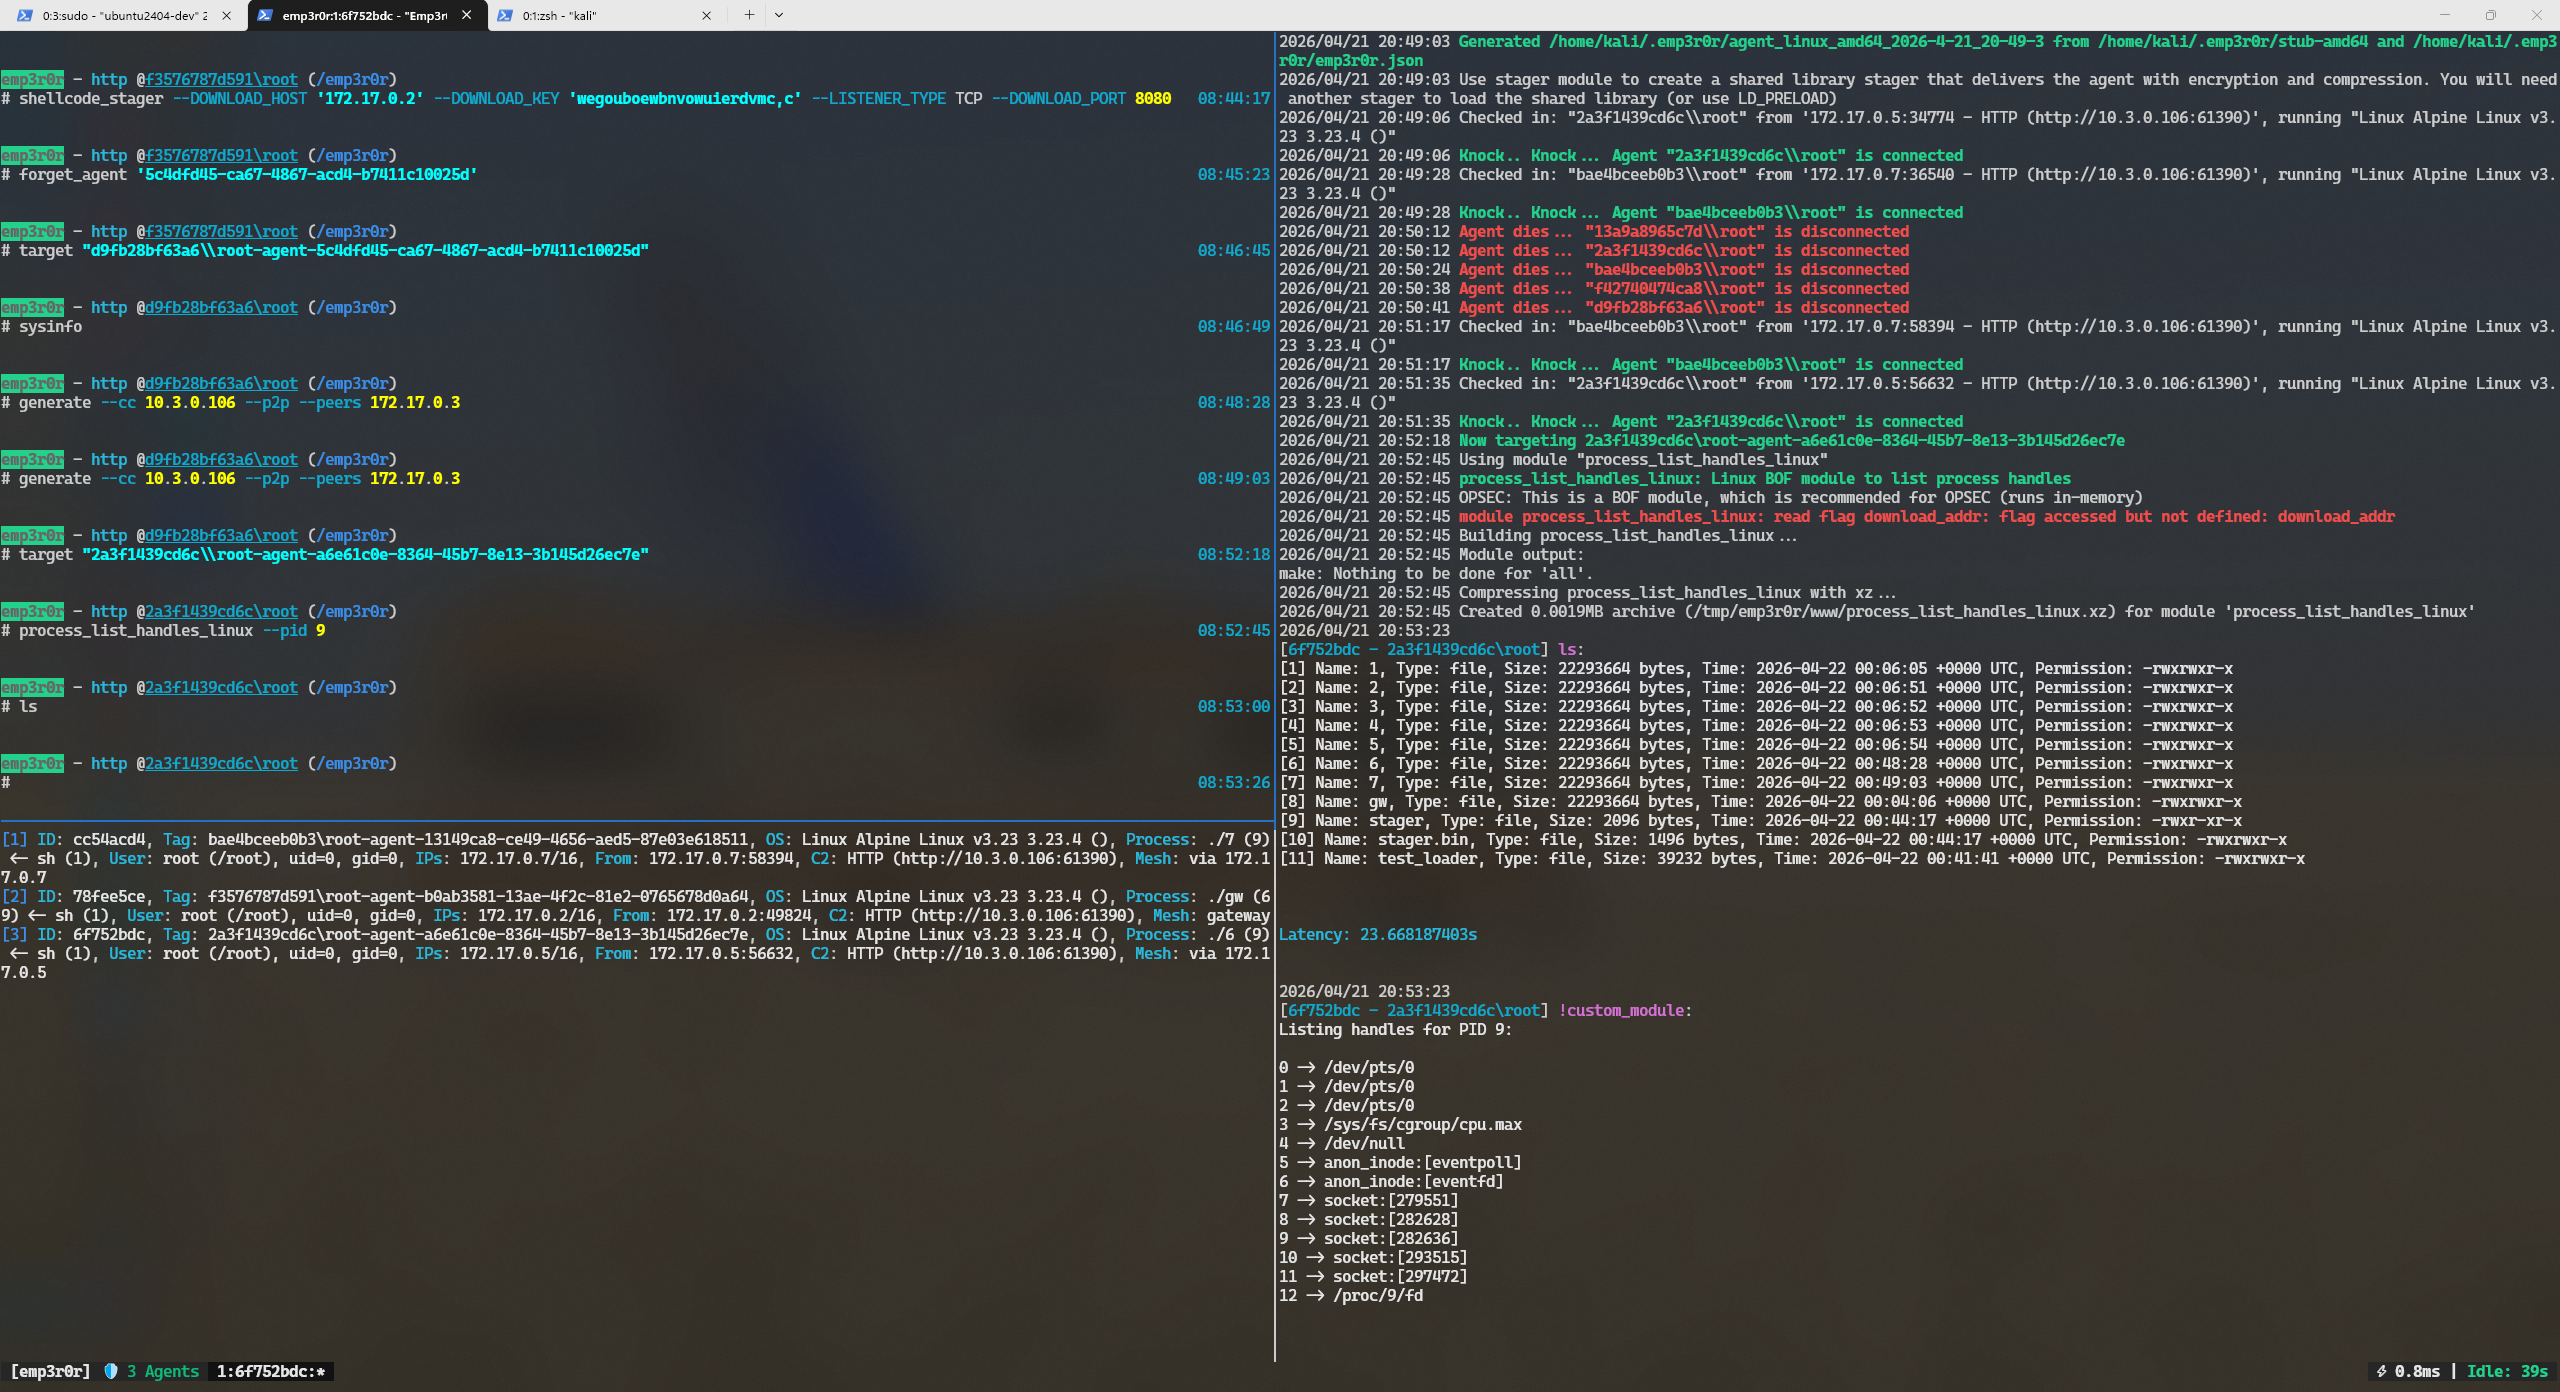 jm33-m0/emp3r0r
Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
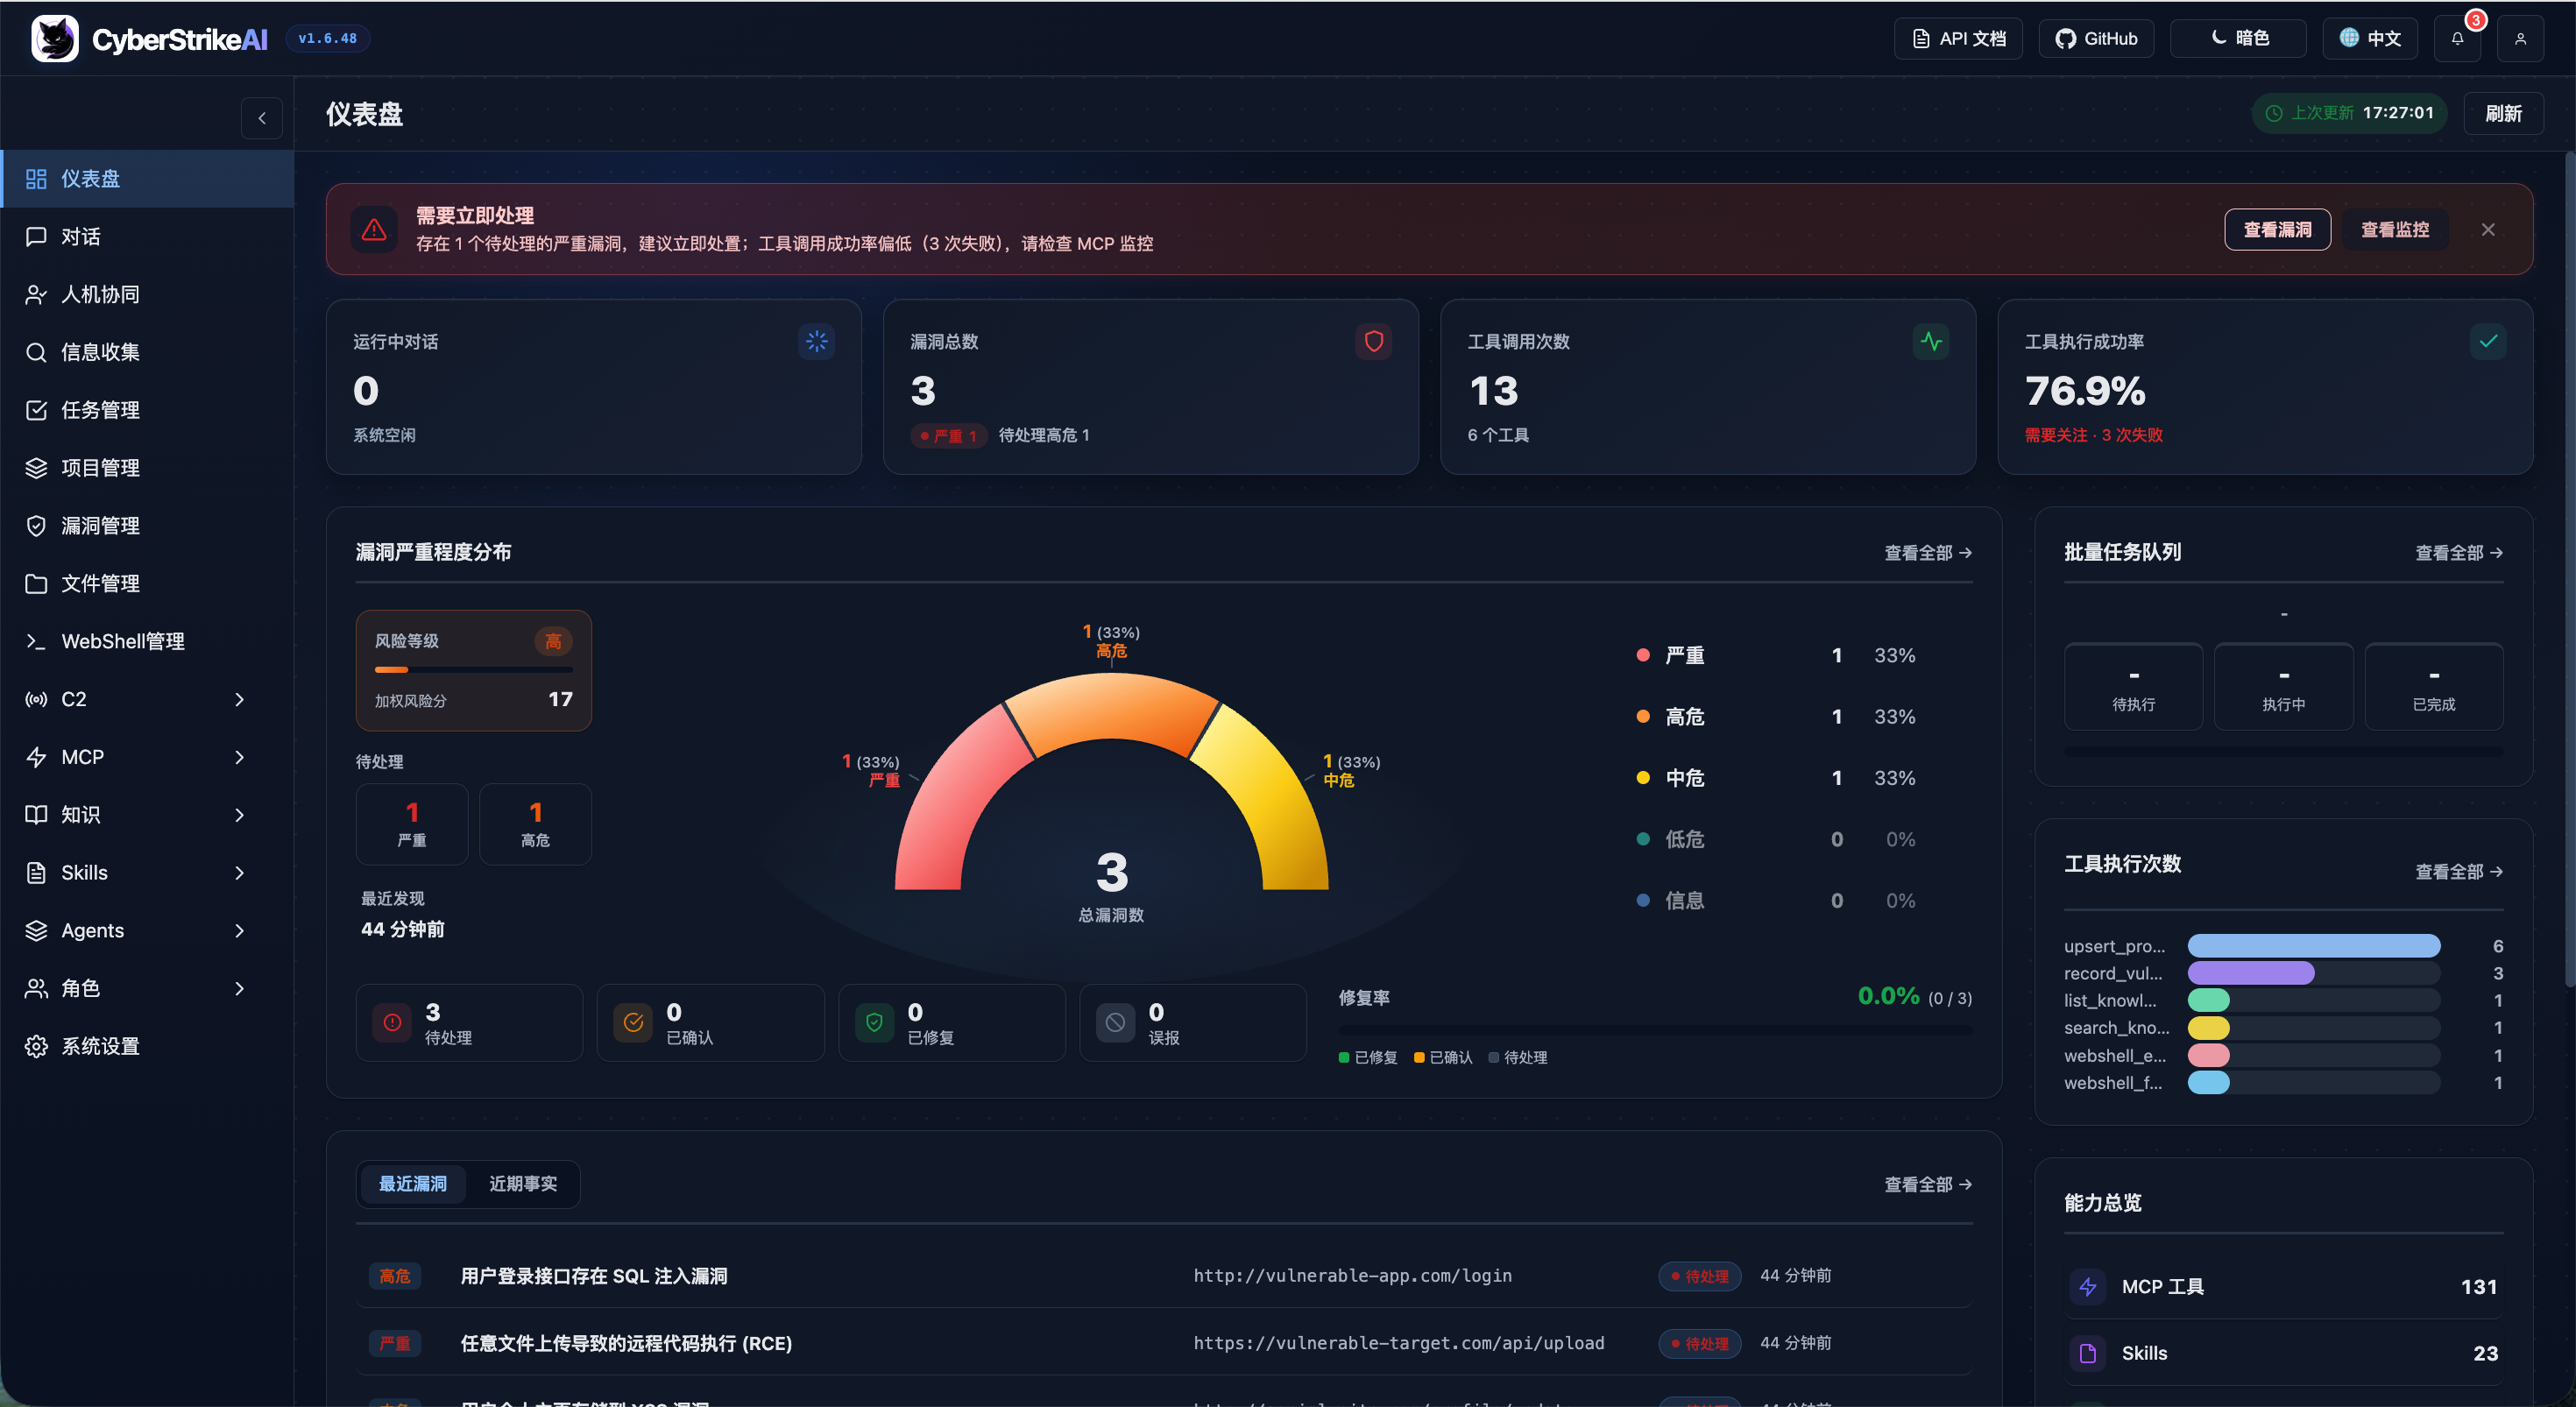 ed1s0nz/cyberstrikeai
Das System der Handlung für KI-native Cybersicherheit – wo Absicht zu gesteuerter Ausführung wird, Beweise zu operativem Gedächtnis werden und jeder…
 yaklang/yakit
All-in-one-Plattform für Penetrationstests mit MITM-Proxy, Web-Fuzzer, Reverse-Connection-Handler und Plugin-System für automatisierte…